
JarHunter
 prophetcraft/jarhunter
JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…
binary-analysiscode-analysisdigital-forensics+5
8
prophetcraft/jarhunterJAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…
 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
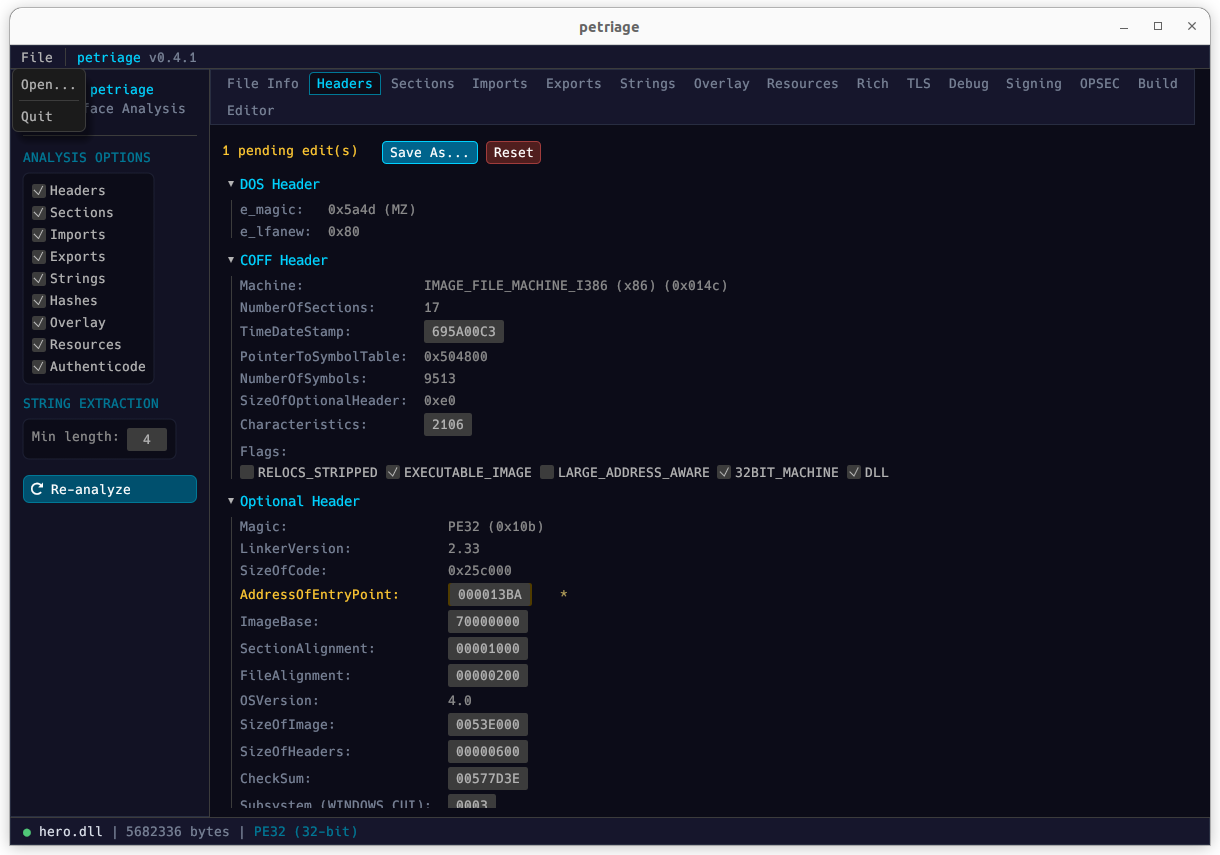 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 elevenpaths/iphonerestrictionspasscodebf
Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.
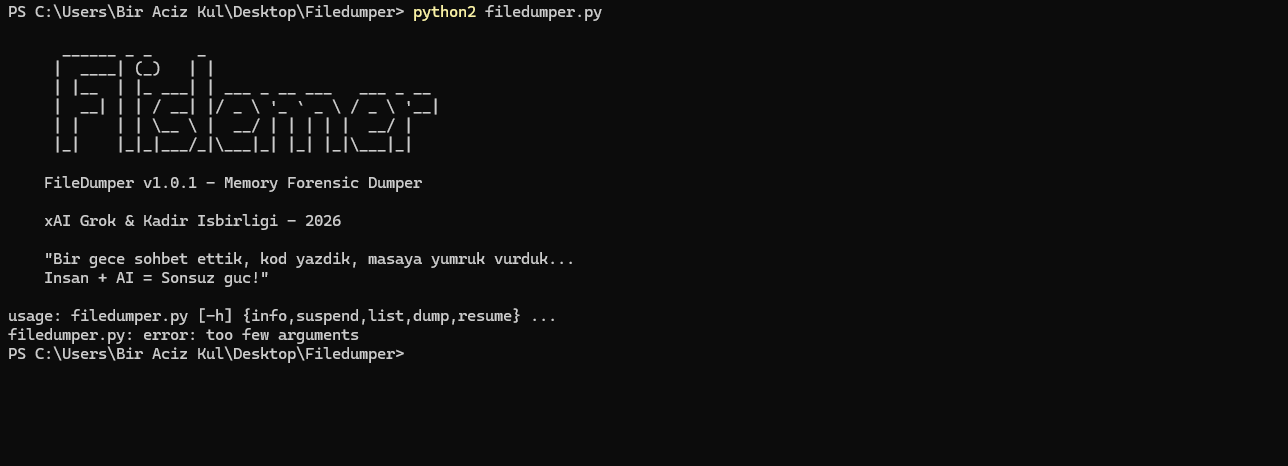 seyyidkadir/filedumper
Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…
 volatilityfoundation/dwarf2json
convert ELF/DWARF symbol and type information into vol3's intermediate JSON
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
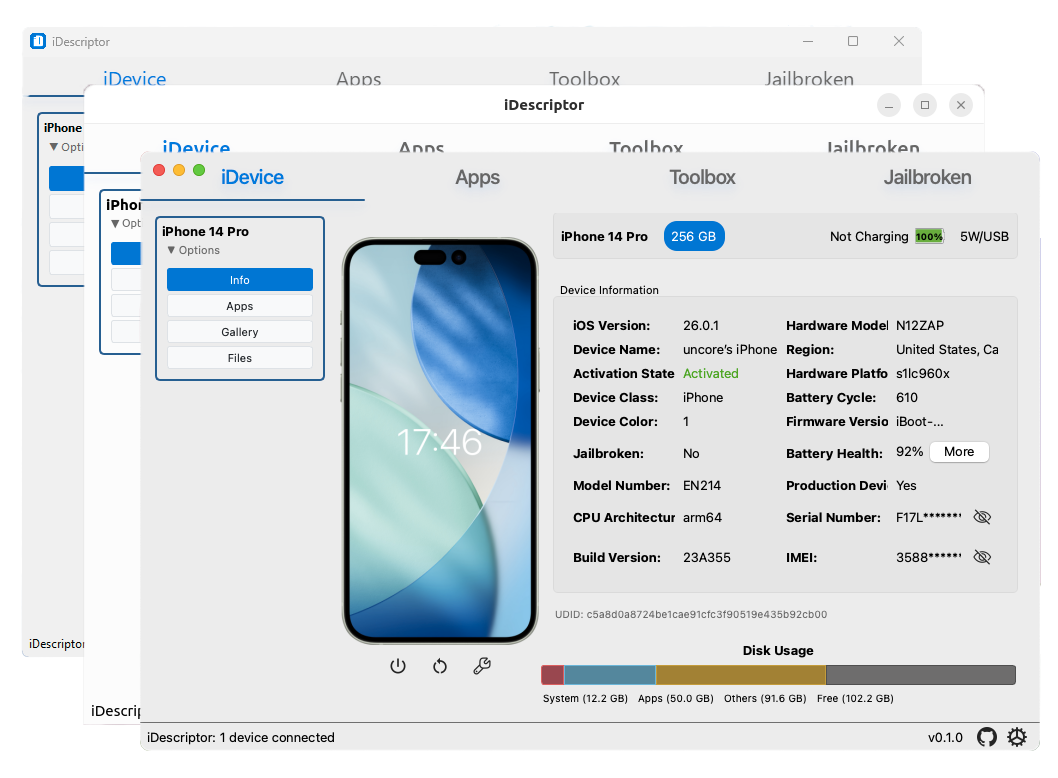 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
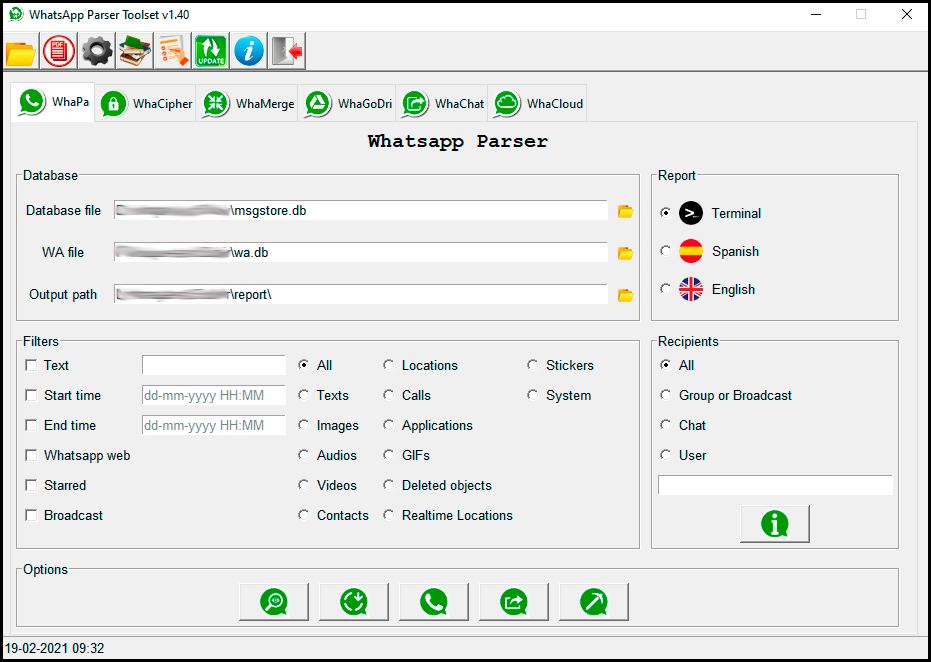 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
 perkins-fund/malware-bible
Free educational courses in cybersecurity, reverse engineering, malware analysis, and programming designed to expand access, build practical skills,…