Detecting-and-Analyzing-CVE-2024-24919-Exploitation

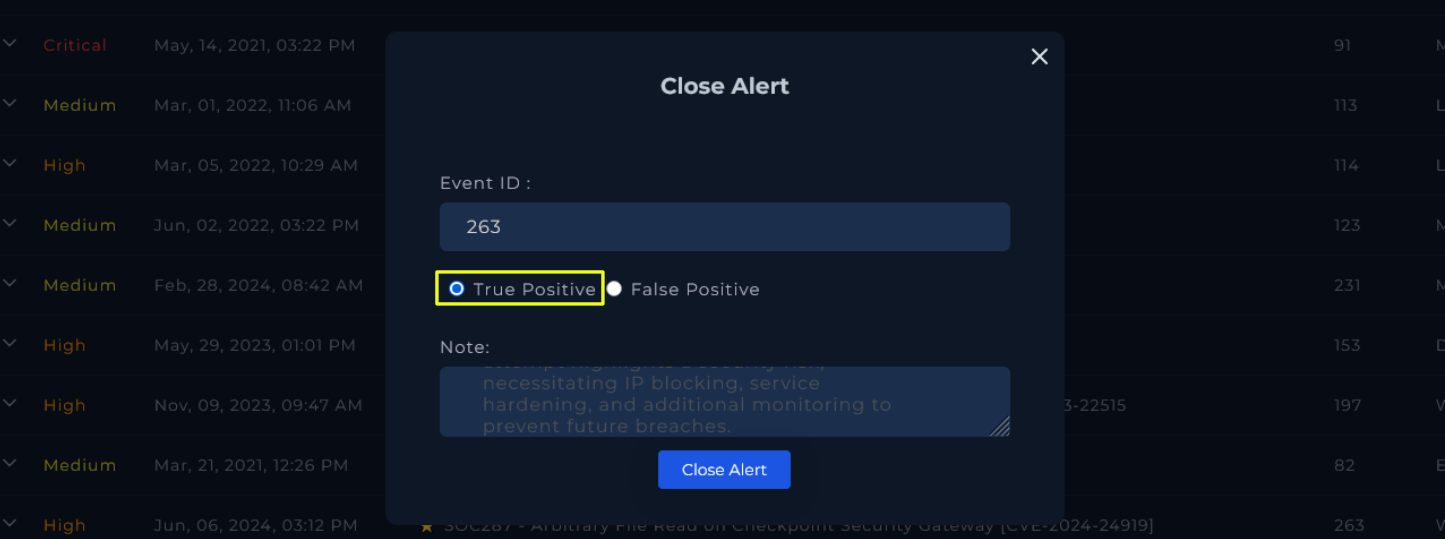
Step-by-step walkthrough of detecting and analyzing CVE-2024-24919 exploitation using a SIEM platform, including traffic analysis, IOC documentation,…

Step-by-step walkthrough of detecting and analyzing CVE-2024-24919 exploitation using a SIEM platform, including traffic analysis, IOC documentation,…

A comprehensive collection of penetration testing cheatsheets, guides, and tools.

Self-hosted multi-engine Sigma detection for event logs

Free hands-on digital forensics labs for students and faculty

Tools and Techniques for Blue Team / Incident Response


A list of cyber-chef recipes and curated links

Records calls from a Trunked Radio System (P25 & SmartNet)

Visibility into AI agent activity on endpoints, with on-device detection, optional pre-action blocking, and forensic reconstruction.

ThePhish: an automated phishing email analysis tool

TCP/IP packet demultiplexer. Download from:

Code written as part of our various malware investigations

PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

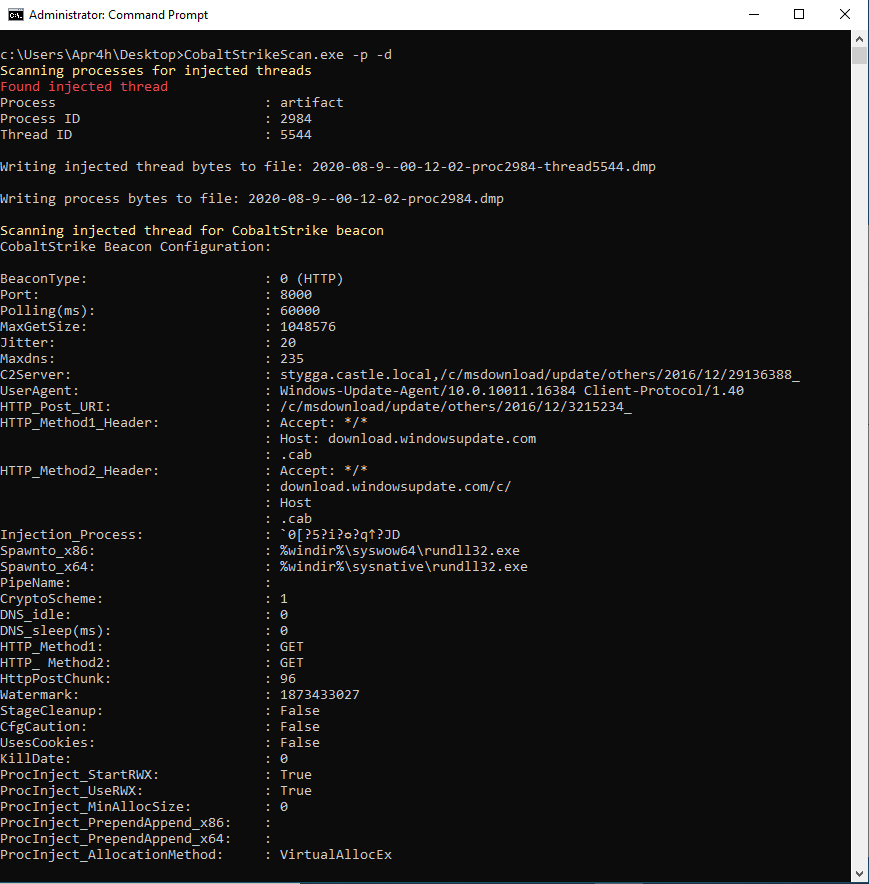
Scan files or process memory for CobaltStrike beacons and parse their configuration

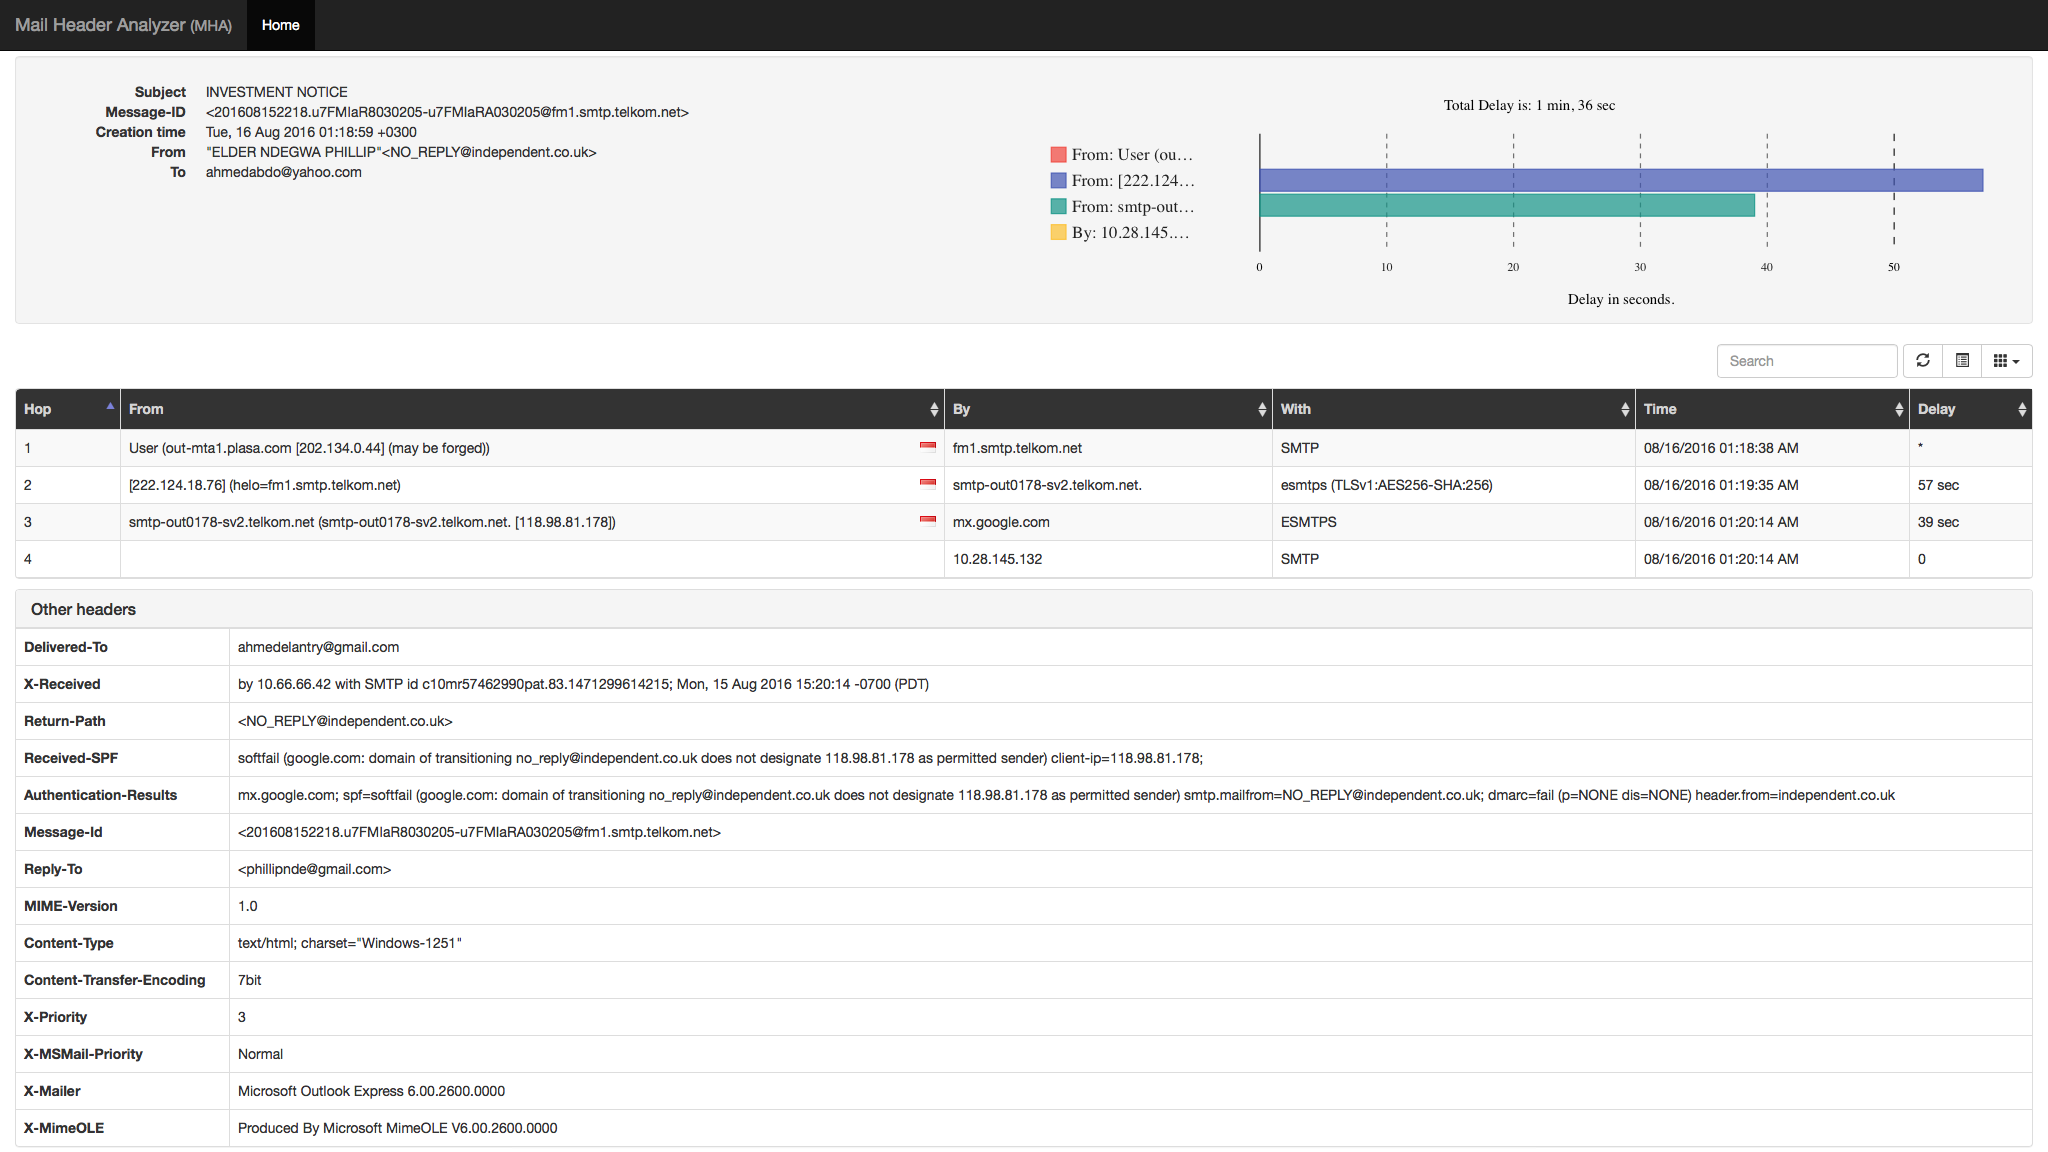
E-Mail Header Analyzer