

MCPTrace
 kowntaewook/mcptrace
Volatility 3 plugin that carves MCP/JSON-RPC message candidates from Windows and Linux memory dumps, preserving raw bytes, addresses, and SHA-256 for…
ai-securitydigital-forensicsforensics+5
7
kowntaewook/mcptraceVolatility 3 plugin that carves MCP/JSON-RPC message candidates from Windows and Linux memory dumps, preserving raw bytes, addresses, and SHA-256 for…
 evyatarmeged/stegextract
Bash script that extracts trailing data, embedded files, and hidden strings from PNG, JPG, and GIF images using magic numbers and hexdump analysis.
 habanada/nativemirror
Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
 nanashili/rea-rust
Rust port of REA, a local-only reverse-engineering tool with CLI/MCP workflows and a native Ghidra worker
 brentmartinmiller/php2shell-check
Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…
 kaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis
Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…
 kaandemir993/overlord-rat-reverse-engineering-a-go-based-rat-injection-keylogging-c2-exfiltration-analysis
Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…
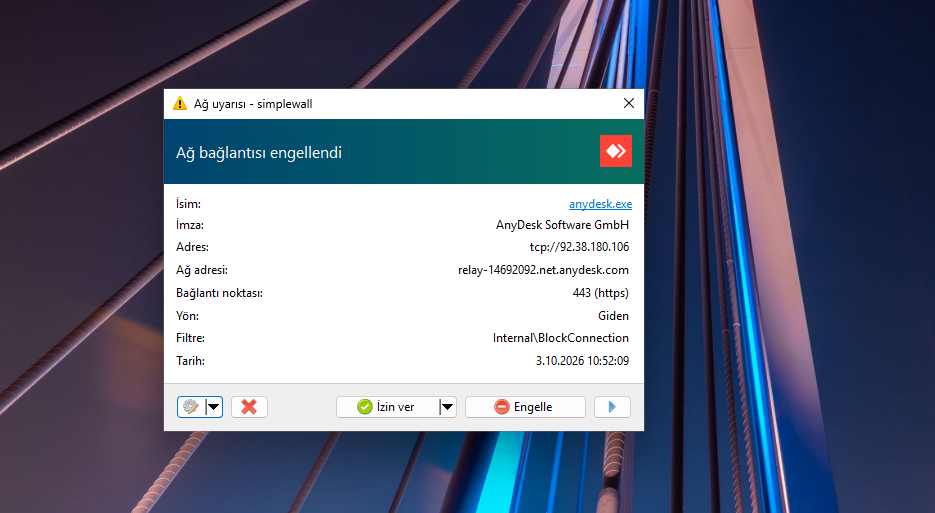 kaandemir993/python-shellcode-anydesk-apc-injection-remote-ip-address-analysis
Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…
 volexity/donut-decryptor
Extracts and decrypts inner payloads from Donut obfuscator samples by detecting loader shellcode signatures, parsing the DONUT_INSTANCE structure,…
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
 trustedsec/lazzzy_dump
Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
 ivancabrera02/srhollow
Extracts LSA secrets and DPAPI keys from Windows registry hives via existing or newly created VSS shadow copies, with an inline regf parser and…
 wrongbaud/spidump
Tool for reconstructing SPI flash images via logic analyzer captures
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 florentineprinzessinzusachsen/badbox-h713-projector
Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
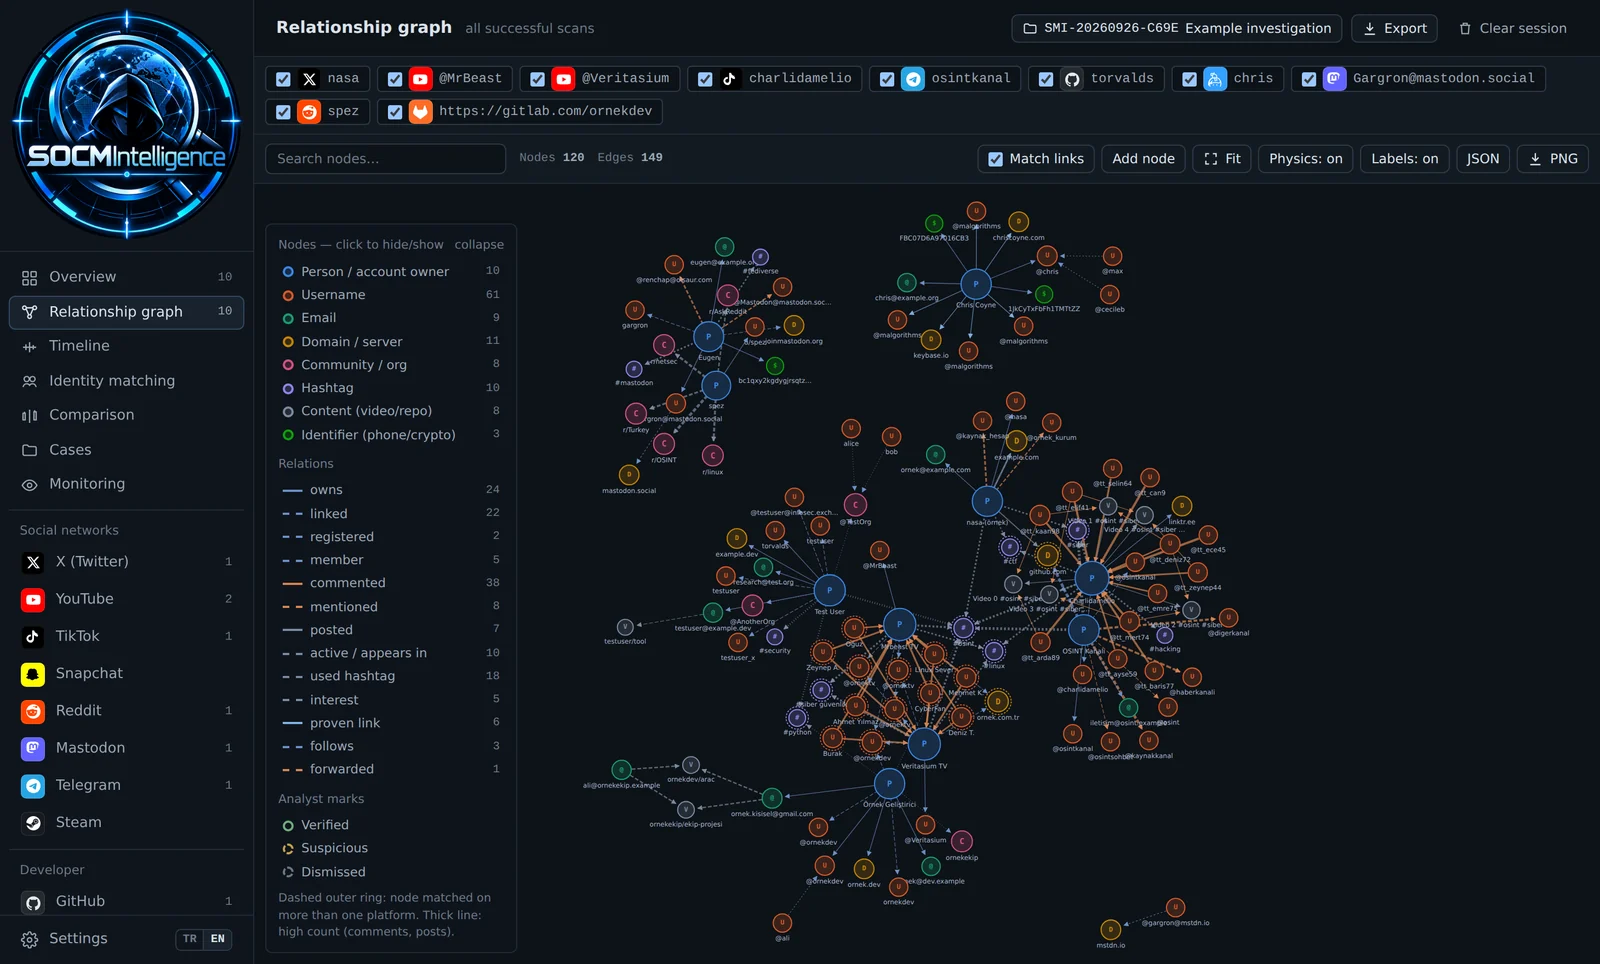 emrekybs/socmintelligence
A modular OSINT & SOCMINT framework for social media intelligence, investigation, and public data analysis.
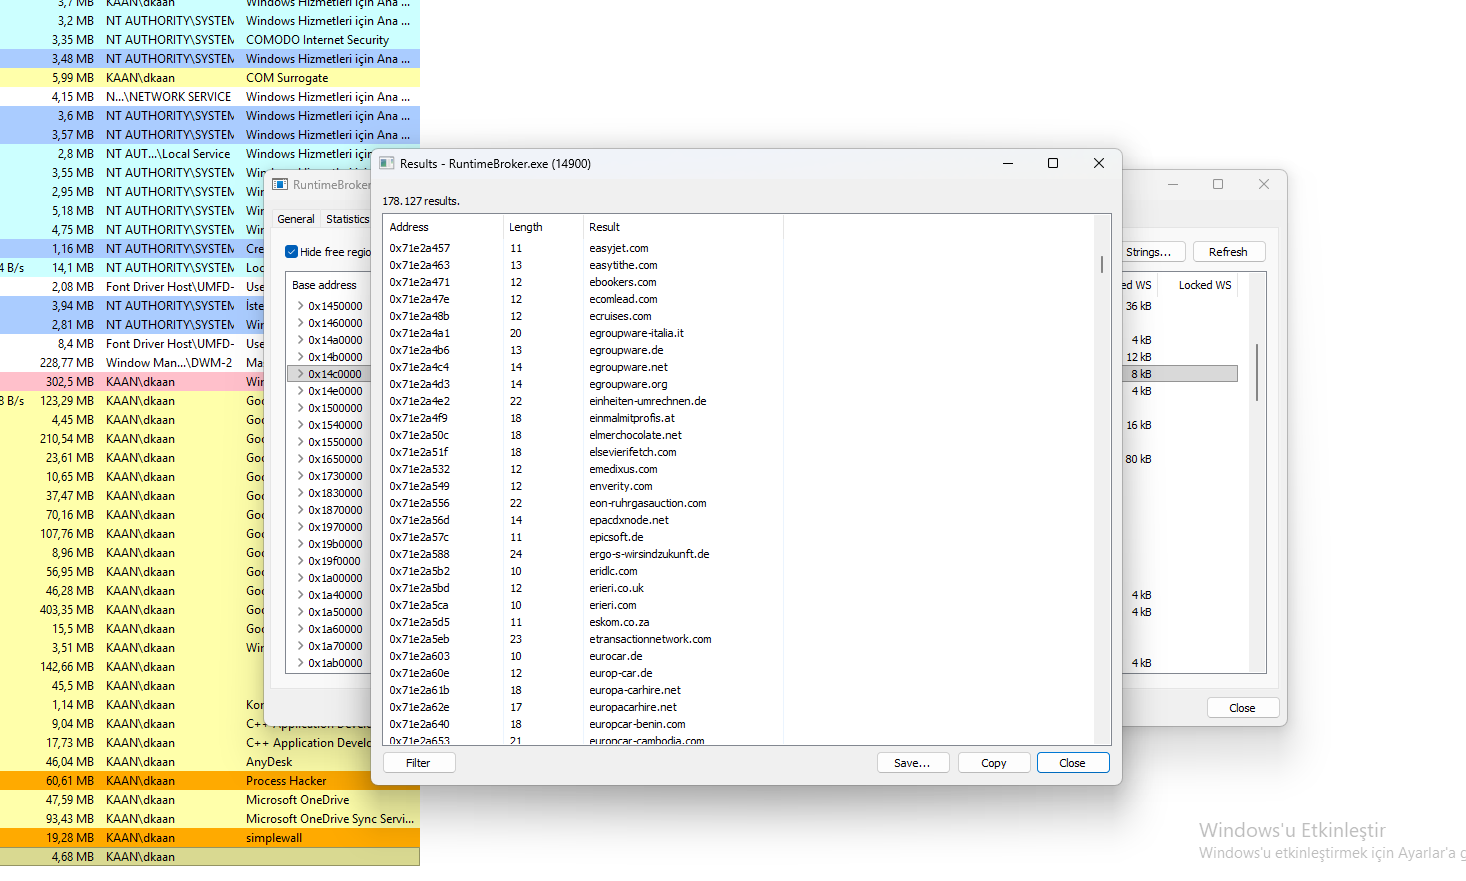 kaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…