
naabu-action
 projectdiscovery/naabu-action
A fast port scanner written in go with a focus on reliability and simplicity.
devsecopsinformation-gatheringnetwork-mapping+3
21
projectdiscovery/naabu-actionA fast port scanner written in go with a focus on reliability and simplicity.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
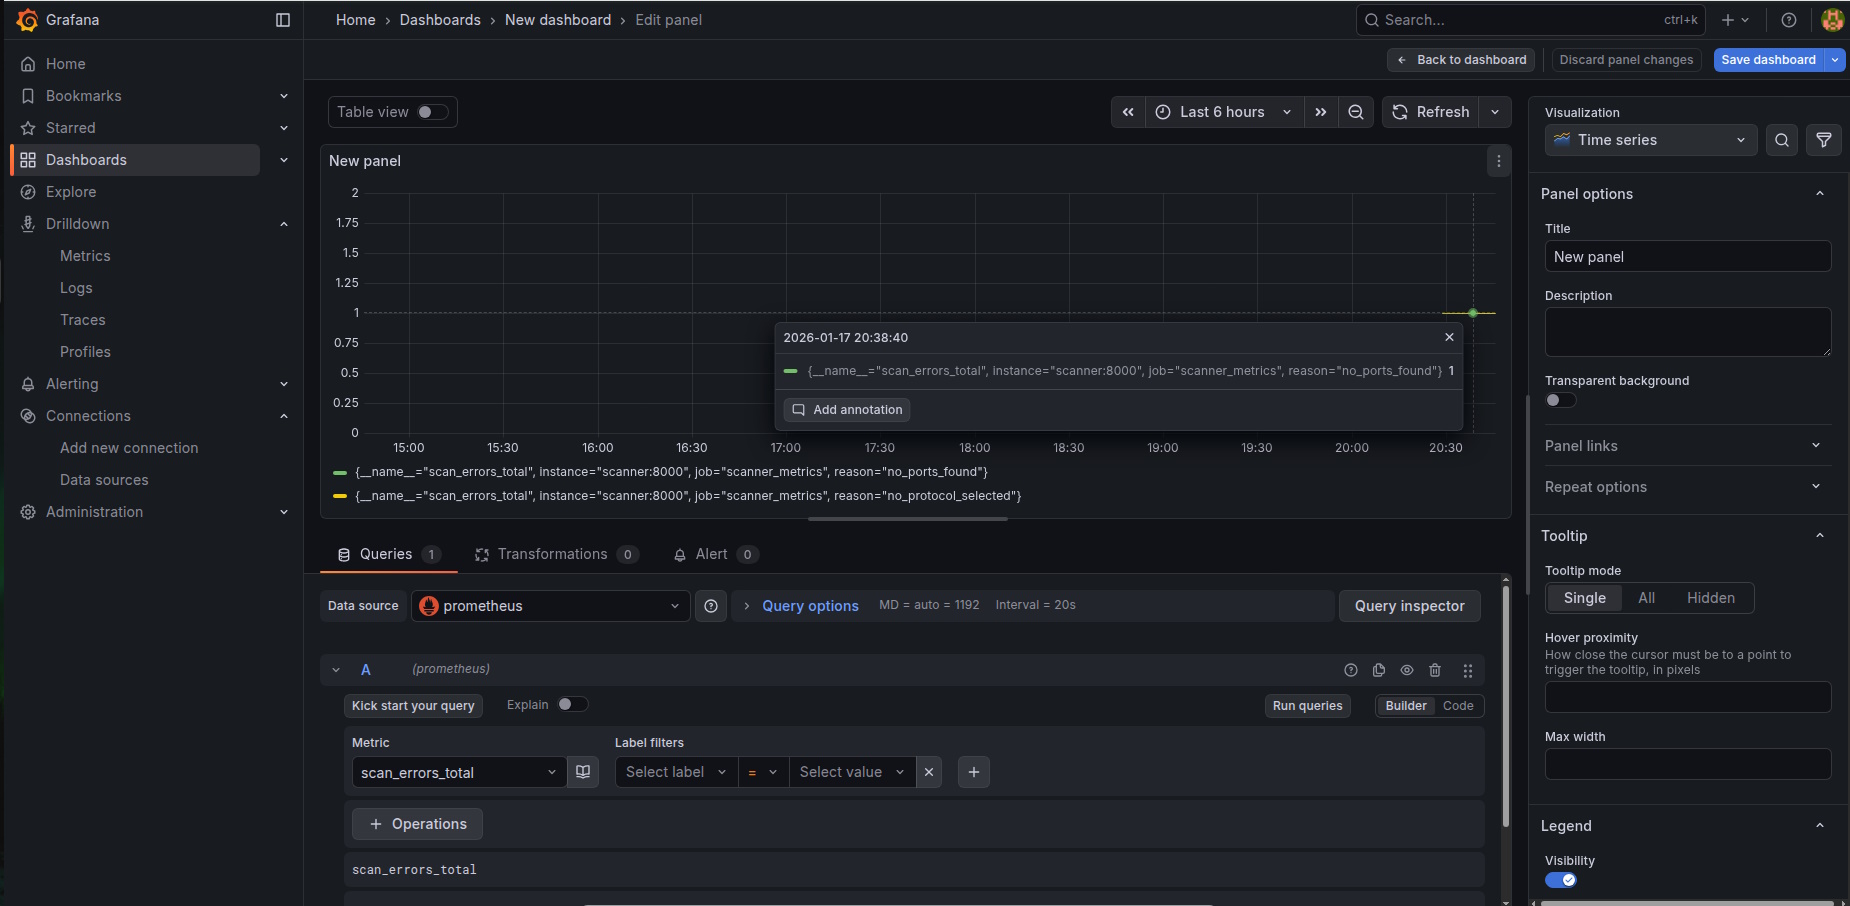 znakar/sharktooth
Port Scanner with Docker & Prometheus + Grafana integration. A tool for network auditing with multithreading support and real-time monitoring.
 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
 raskrebs/sonar
CLI tool for inspecting and managing services listening on localhost ports
 mhaggis/package-inferno
A Public Package Scanner for The Community
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
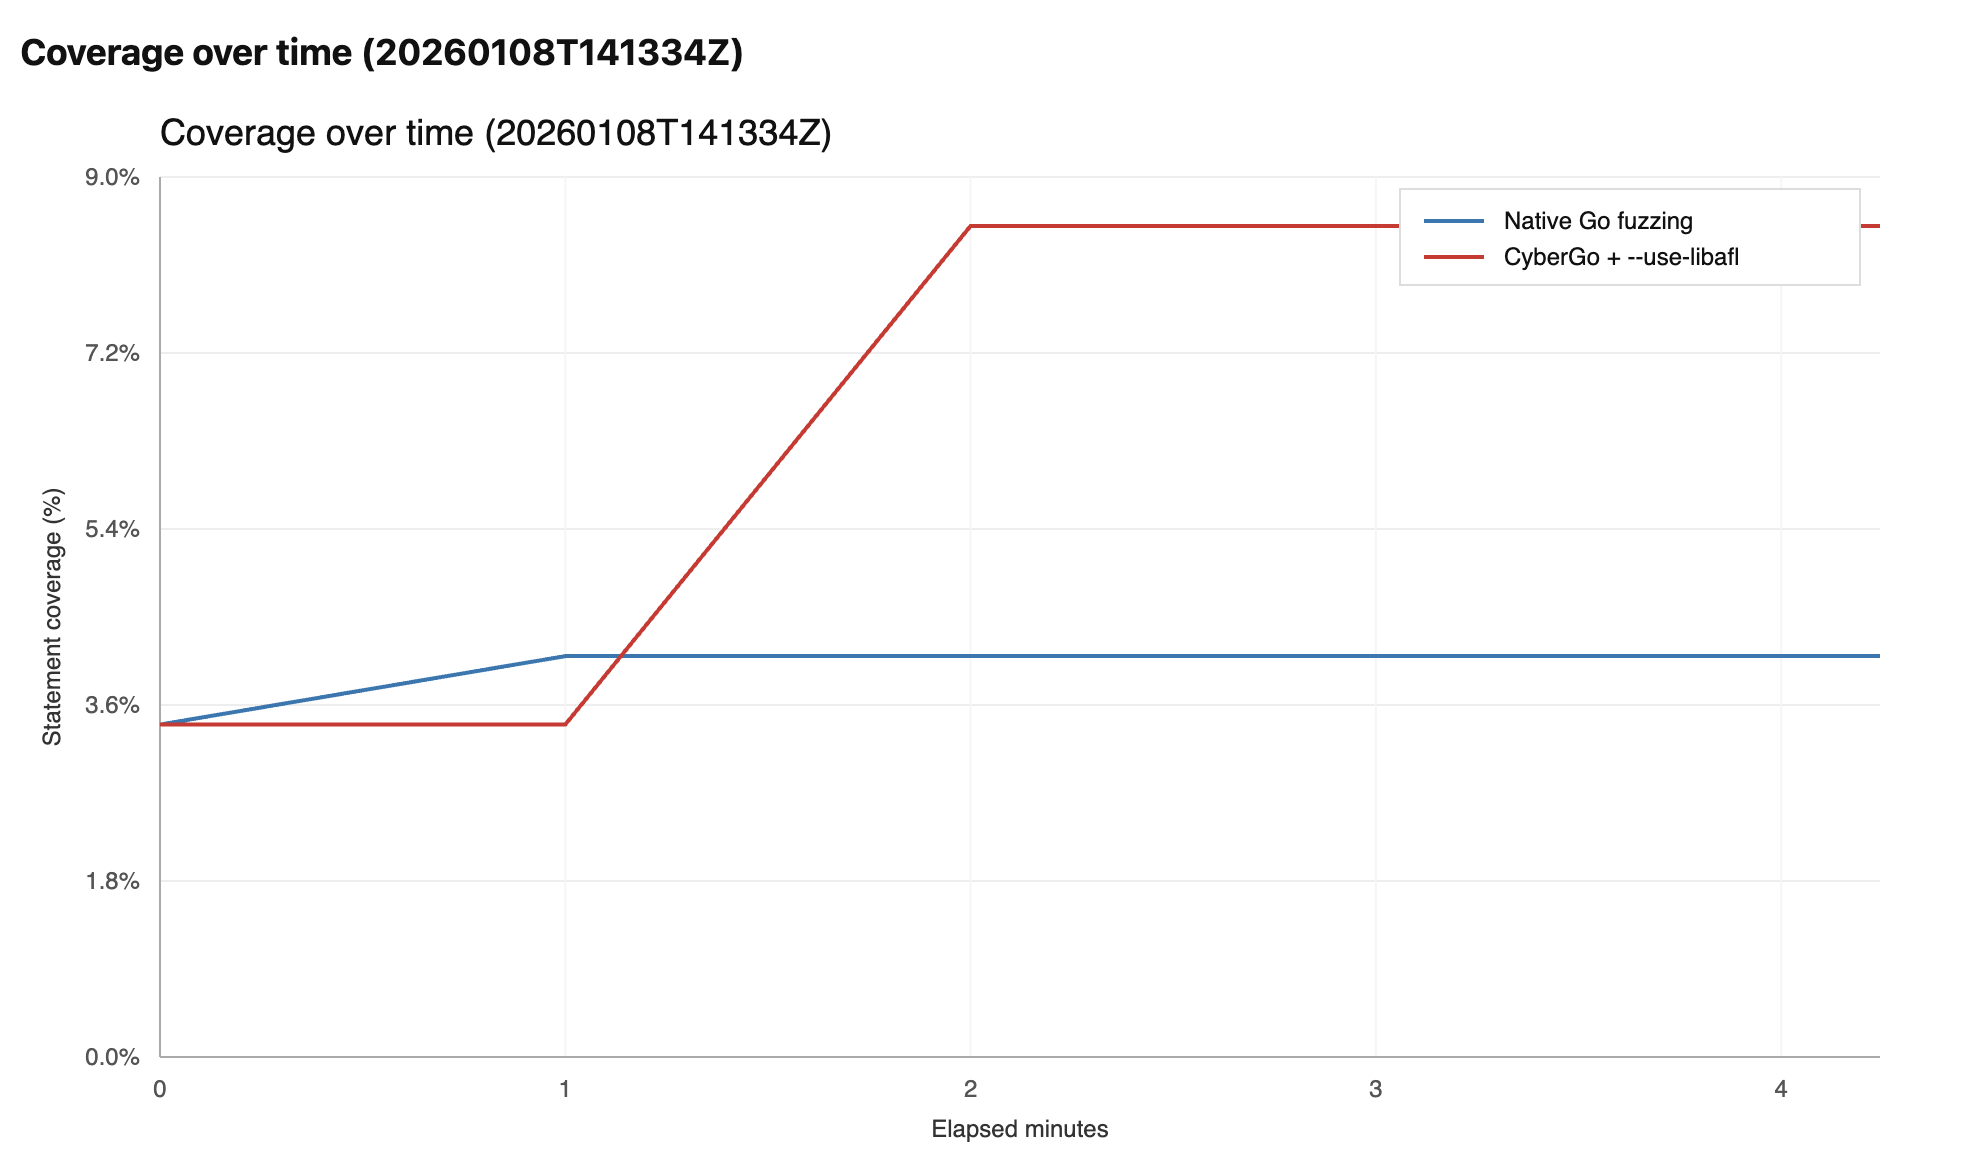 trailofbits/gosentry
Security-oriented Go toolchain, focused on state-of-the-art fuzzing capabilities.
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems

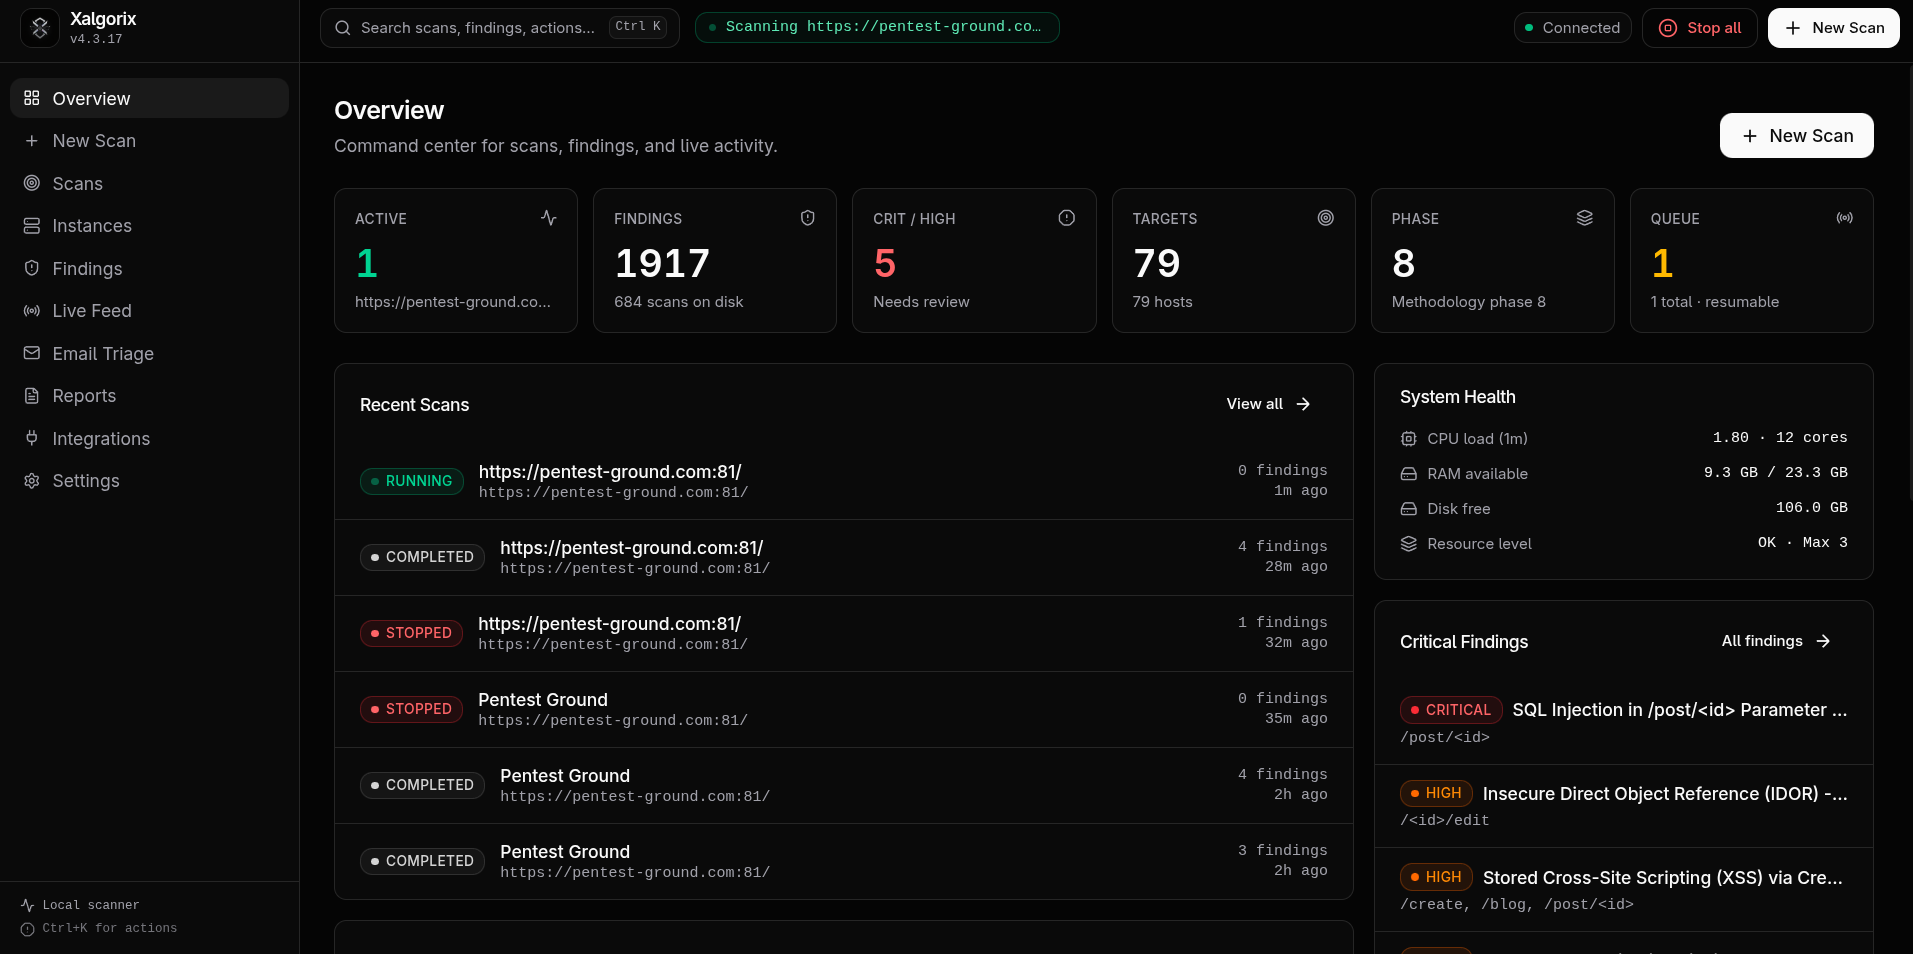 xalgord/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 google/capslock
CLI tool for analyzing Go package capabilities by tracing transitive calls to privileged standard library operations, enabling supply chain risk…
 finbarr/yolobox
Let your AI go full send. Your home directory stays home.
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…