
appsec-forge
 appsec-forge/appsec-forge
Structured security knowledge base with production-inspired cases: vulnerability analysis, exploit explanation, remediation, and DevSecOps for…
ai-securitycloud-securitycontainer-security+7
appsec-forge/appsec-forgeStructured security knowledge base with production-inspired cases: vulnerability analysis, exploit explanation, remediation, and DevSecOps for…
 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…
 shoucheng3/jenkinsci__workflow-cps-global-lib-plugin_cve-2022-25174_544-vff04fa68714d
Exploit for CVE-2022-25174 in Jenkins Pipeline Shared Libraries plugin, demonstrating code injection via crafted library definitions for security…
 shoucheng3/jenkinsci__workflow-multibranch-plugin_cve-2022-25175_706-vd43c65dec013
Exploit for CVE-2022-25175 targeting Jenkins Pipeline: Multibranch plugin, enabling automated exploitation of a specific vulnerability in CI/CD…
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 moisestapia/http-react2shell
Detection of the React Server Actions Exploit vector – CVE-2025-55182 / CVE-2025-66478
 bgsilvait/win-cve-2021-31166
Proof-of-concept for CVE-2021-31166 (http.sys RCE) with Terraform deployment on AWS, including testing scripts and a WAFv2 rule to block the exploit.
 jblaine/cookbook-bash-cve-2014-6271
Chef cookbook that will fail if bash vulnerability found per CVE-2014-6271
 teedeedubya/bash-fix-exploit
Ansible role to check the CVE-2014-6271 vulnerability
 infobyte/faraday
Open-source and AI-powered cybersecurity tools for offensive security, vulnerability management, and autonomous pentesting. Built by hackers in Latin…
 google/osv.dev
Open source vulnerability DB and triage service.
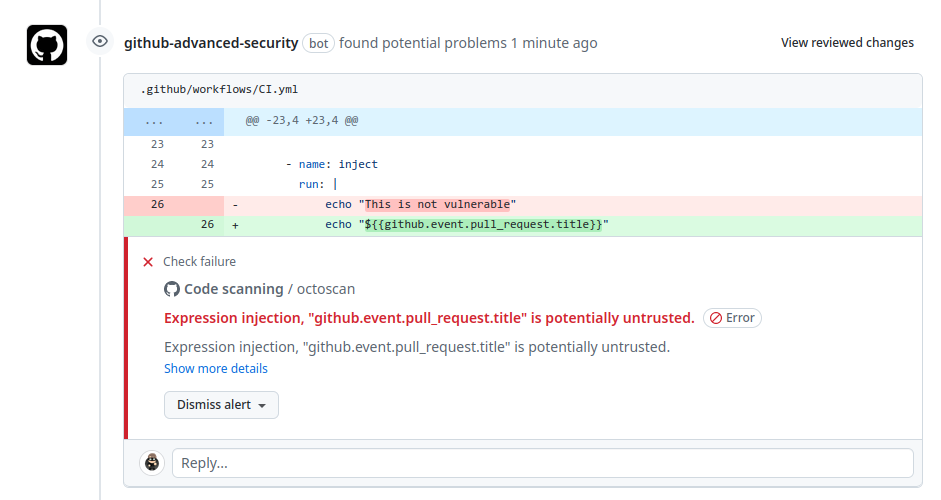 synacktiv/octoscan
Octoscan is a static vulnerability scanner for GitHub action workflows.
 ohaswin/pyscan
python dependency vulnerability scanner, written in Rust.
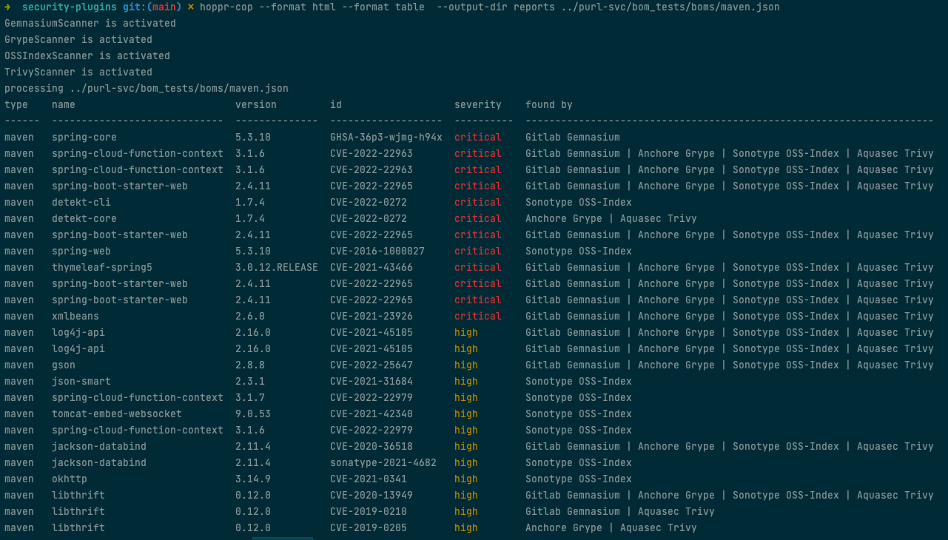 hoppr/hoppr-cop
Aggregates vulnerability data from multiple databases into CycloneDX SBOMs, generating deduplicated VEX, HTML, and GitLab-compatible reports for…
 hasecuritysolutions/vulnwhisperer
Create actionable data from your Vulnerability Scans
 defectdojo/django-defectdojo
Open-Source Unified Vulnerability Management, DevSecOps & ASPM
 projectdiscovery/nuclei-action
Vulnerability Scan with Nuclei
 faloker/purify
All-in-one tool for managing vulnerability reports from AppSec pipelines