
Archived
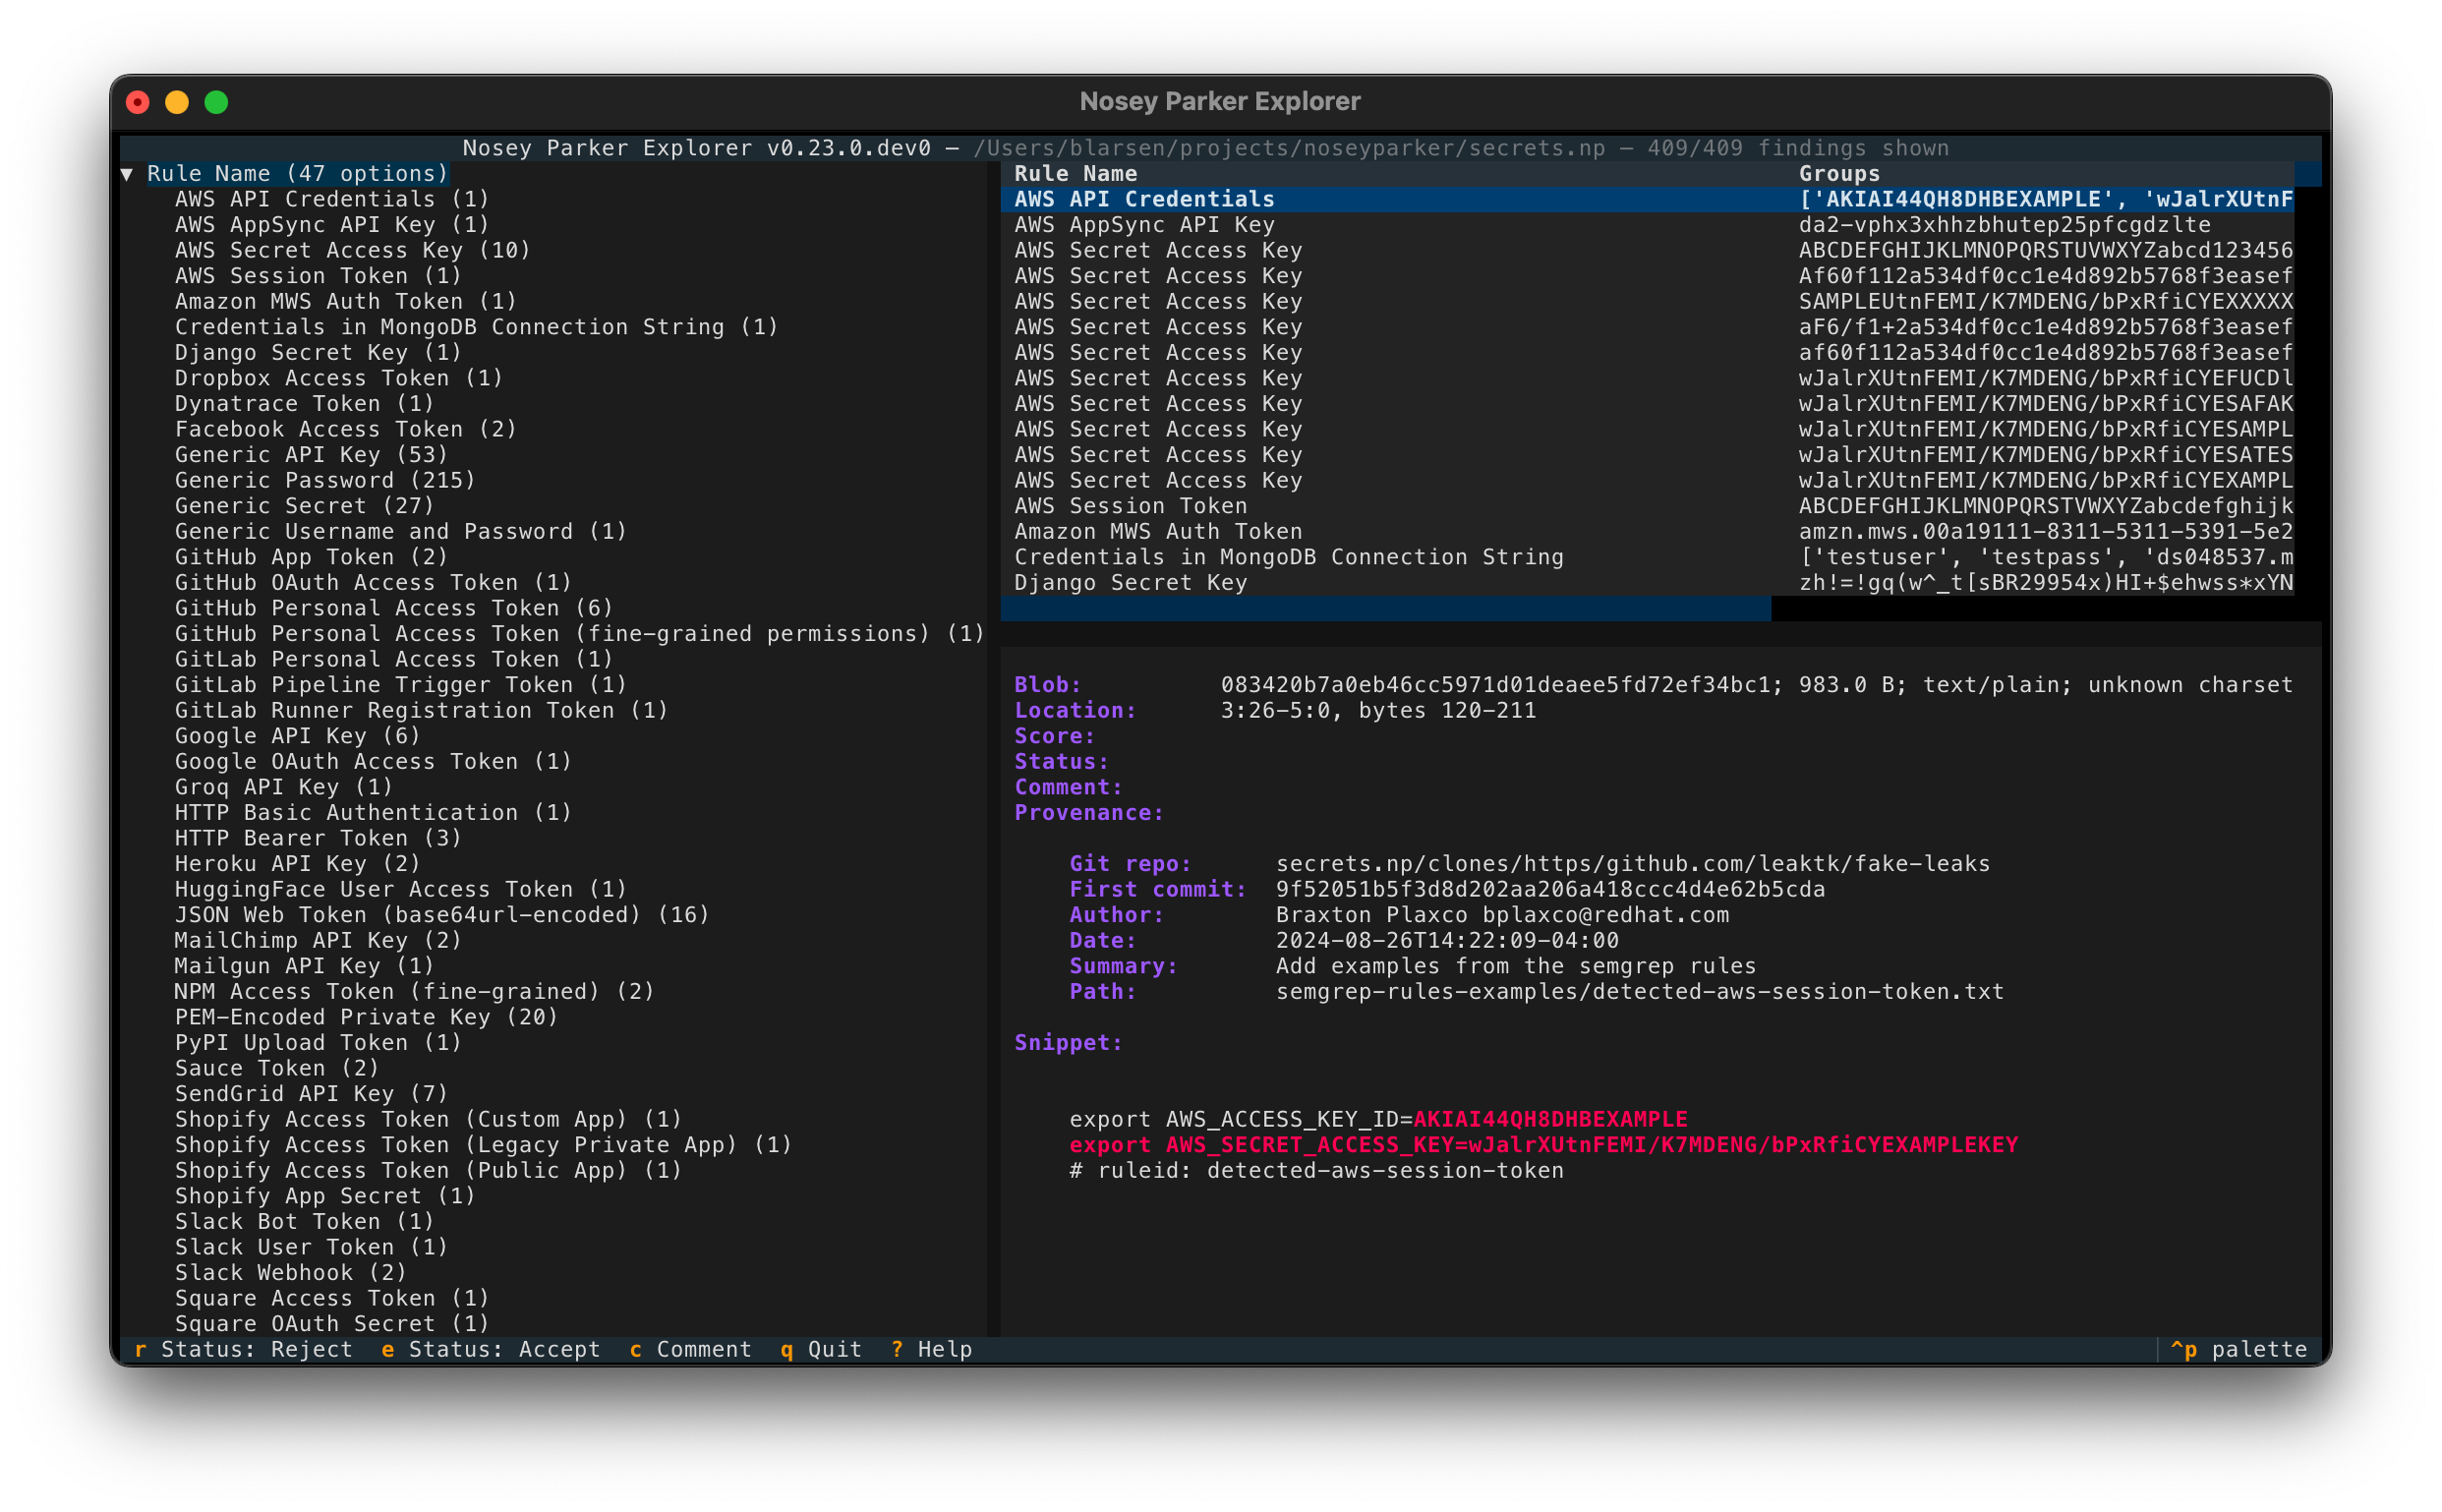
noseyparker
 praetorian-inc/noseyparker
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
code-analysisdevsecopsinformation-gathering+3
praetorian-inc/noseyparkerNosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
 joshlarsen/aws-recon
Multi-threaded AWS inventory collection tool with a focus on security-relevant resources and metadata.
 hawkeyesec/scanner-cli
A project security/vulnerability/risk scanning tool
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 nomograph/kit
Verified tool registry manager. Manages developer toolchains from git-based registries.
 reposaur/reposaur
Open source compliance tool for development platforms.
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…

 nabla-c0d3/sslyze
Fast and powerful SSL/TLS scanning library.
 thoughtworks/talisman
Git hook-based secret scanner that detects tokens, passwords, and private keys in outgoing changesets, preventing sensitive data from being committed…
 punk-security/dnsreaper
Fast subdomain takeover scanner with 50+ signatures, supporting cloud provider integrations (AWS, Azure, Cloudflare) and CI/CD pipeline mode for…
 optiopay/klar
Integration of Clair and Docker Registry
 megamansec/gixy-next
Gixy-Next: NGINX Configuration Security Scanner & Performance Checker
 disruptops/cred_scanner
A simple file-based scanner to look for potential AWS access and secret keys in files
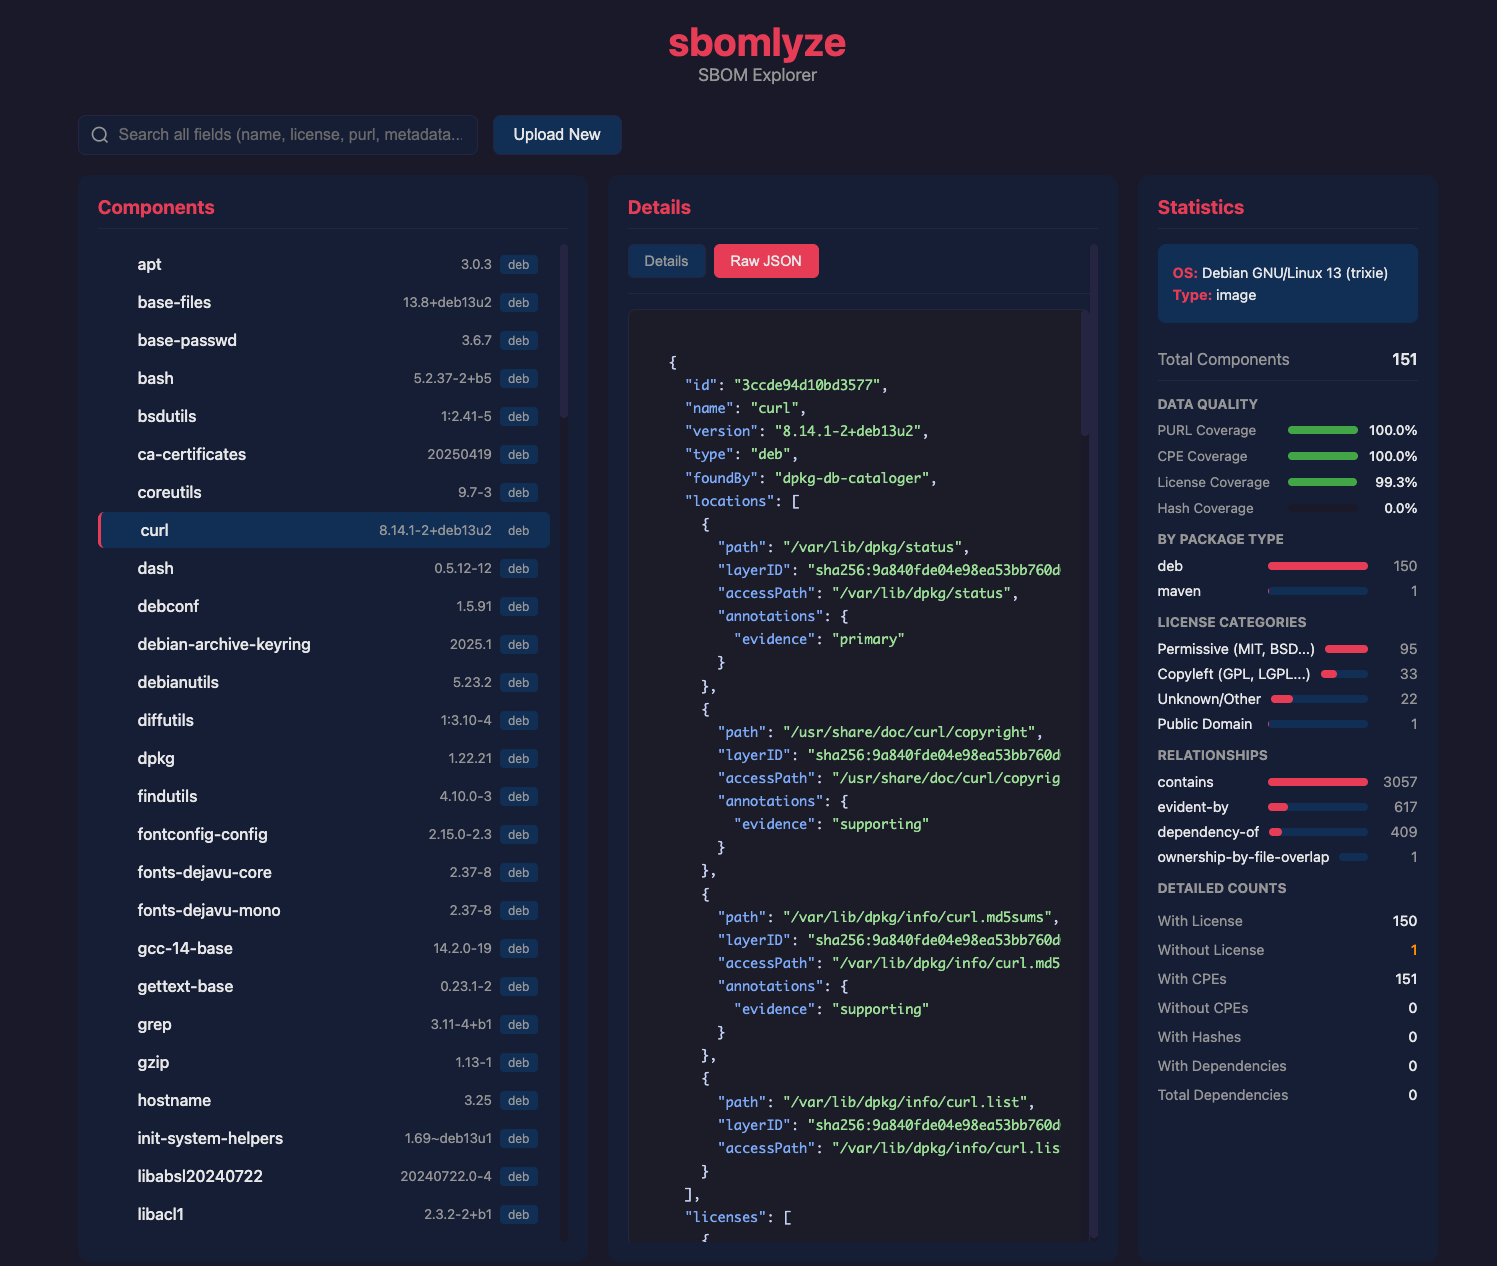 rezmoss/sbomlyze
Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
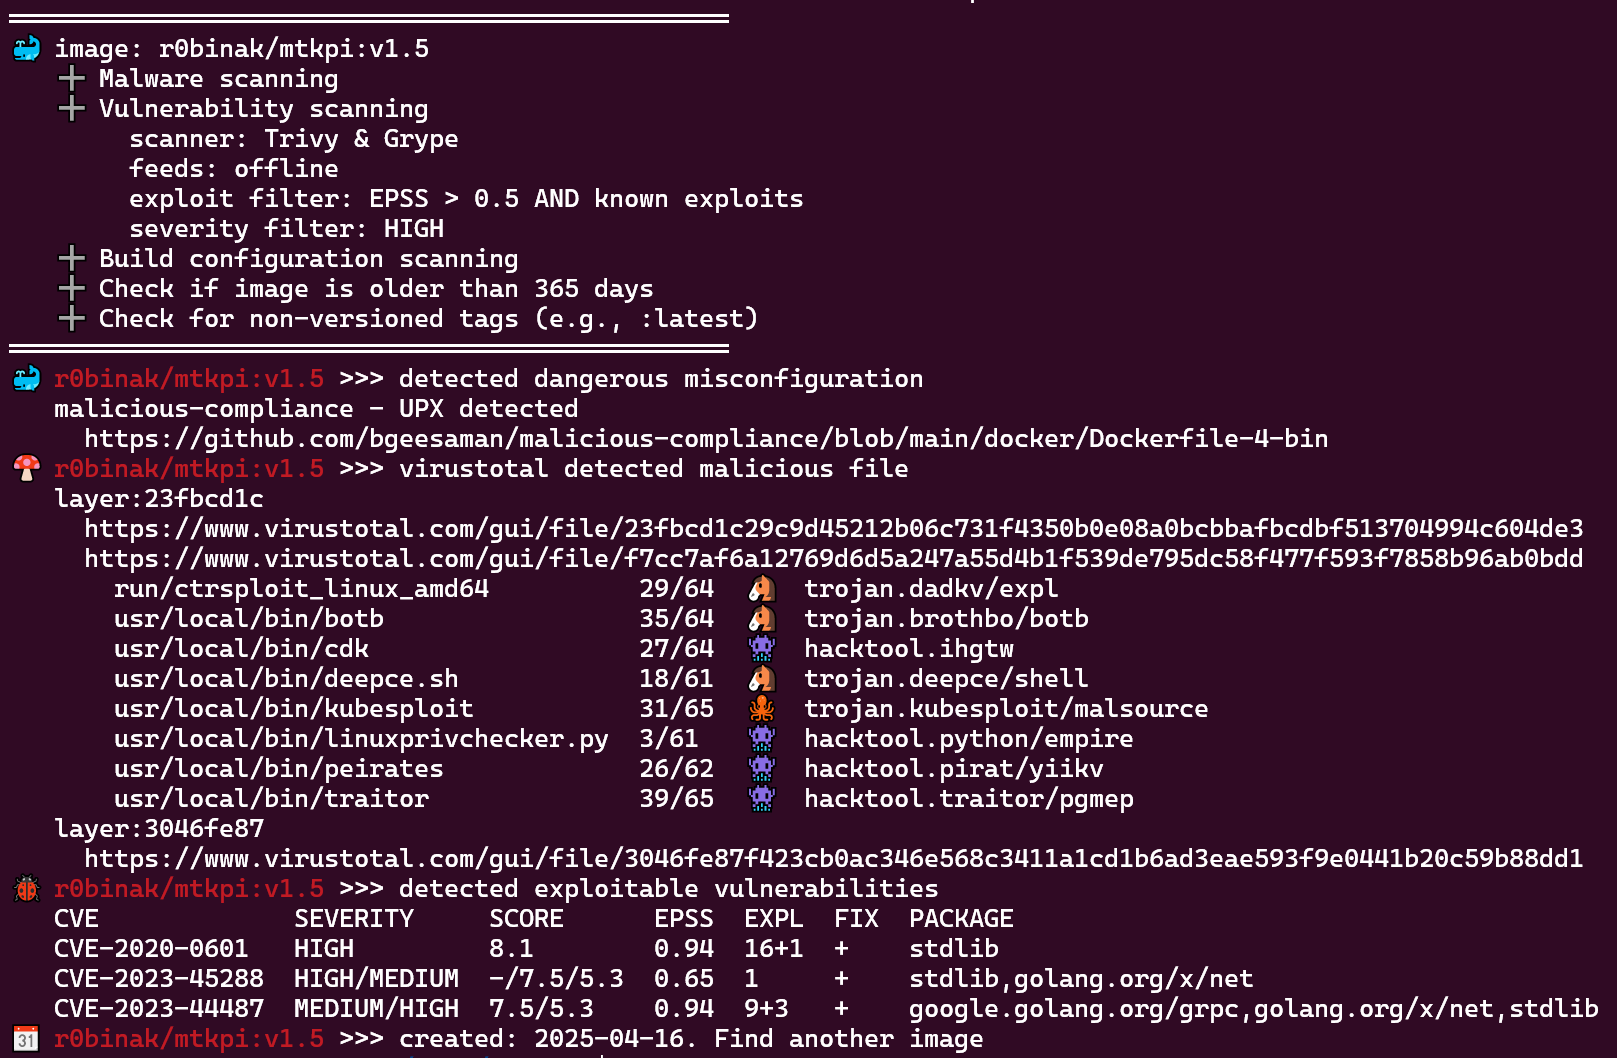 ecomtech-oss/pisc
Public OCI-Image (docker image) Security Checker