NetworkSandboxEngine

A deterministic network sandbox for testing nftables rules. It uses ephemeral Linux network namespaces (netns) and Scapy to validate firewall logic…

A deterministic network sandbox for testing nftables rules. It uses ephemeral Linux network namespaces (netns) and Scapy to validate firewall logic…

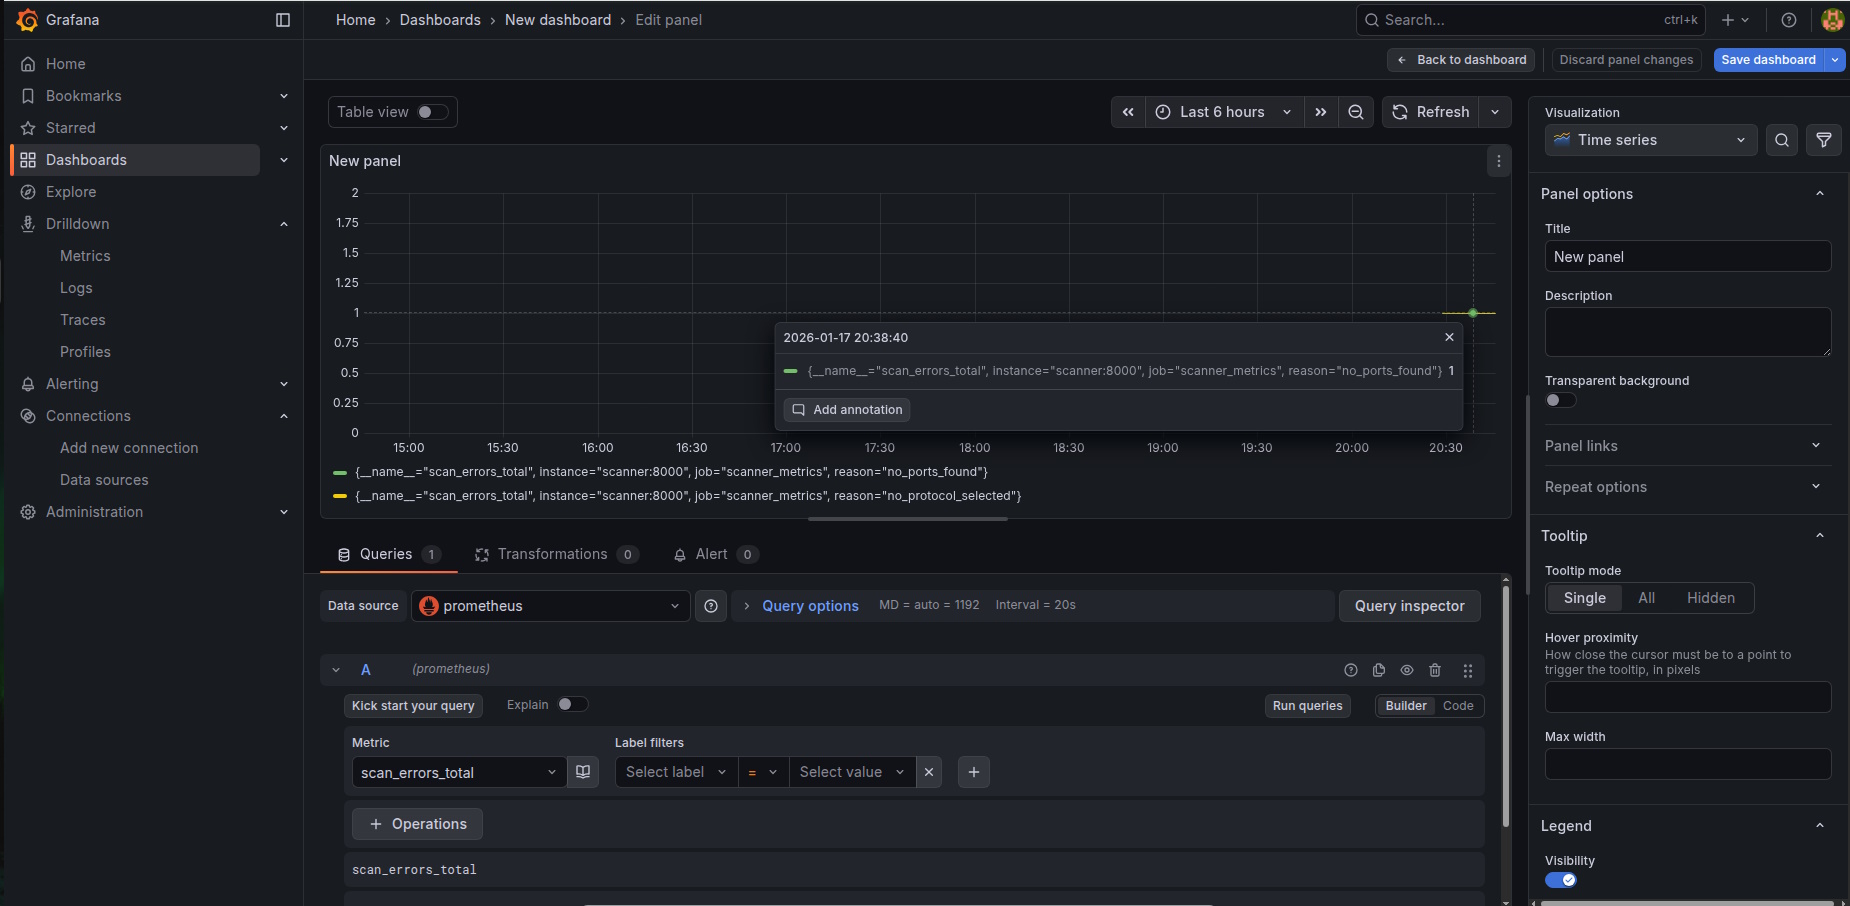
Port Scanner with Docker & Prometheus + Grafana integration. A tool for network auditing with multithreading support and real-time monitoring.

Local CVE scanner for OpenClaw that checks versions against 522+ known vulnerabilities, displays recent HIGH-severity CVEs, and recommends upgrades.…

Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…

Local Git pre-push hook and filesystem scanner that detects likely secret leaks, redacts matched values, and blocks pushes without telemetry or…

Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…

WireGuard-based zero-trust access platform providing secure, peer-to-peer remote access with granular policy controls, SSO authentication, and audit…

API-first identity and user management system for cloud-native applications. Handles login, registration, MFA, recovery, and profile management with…

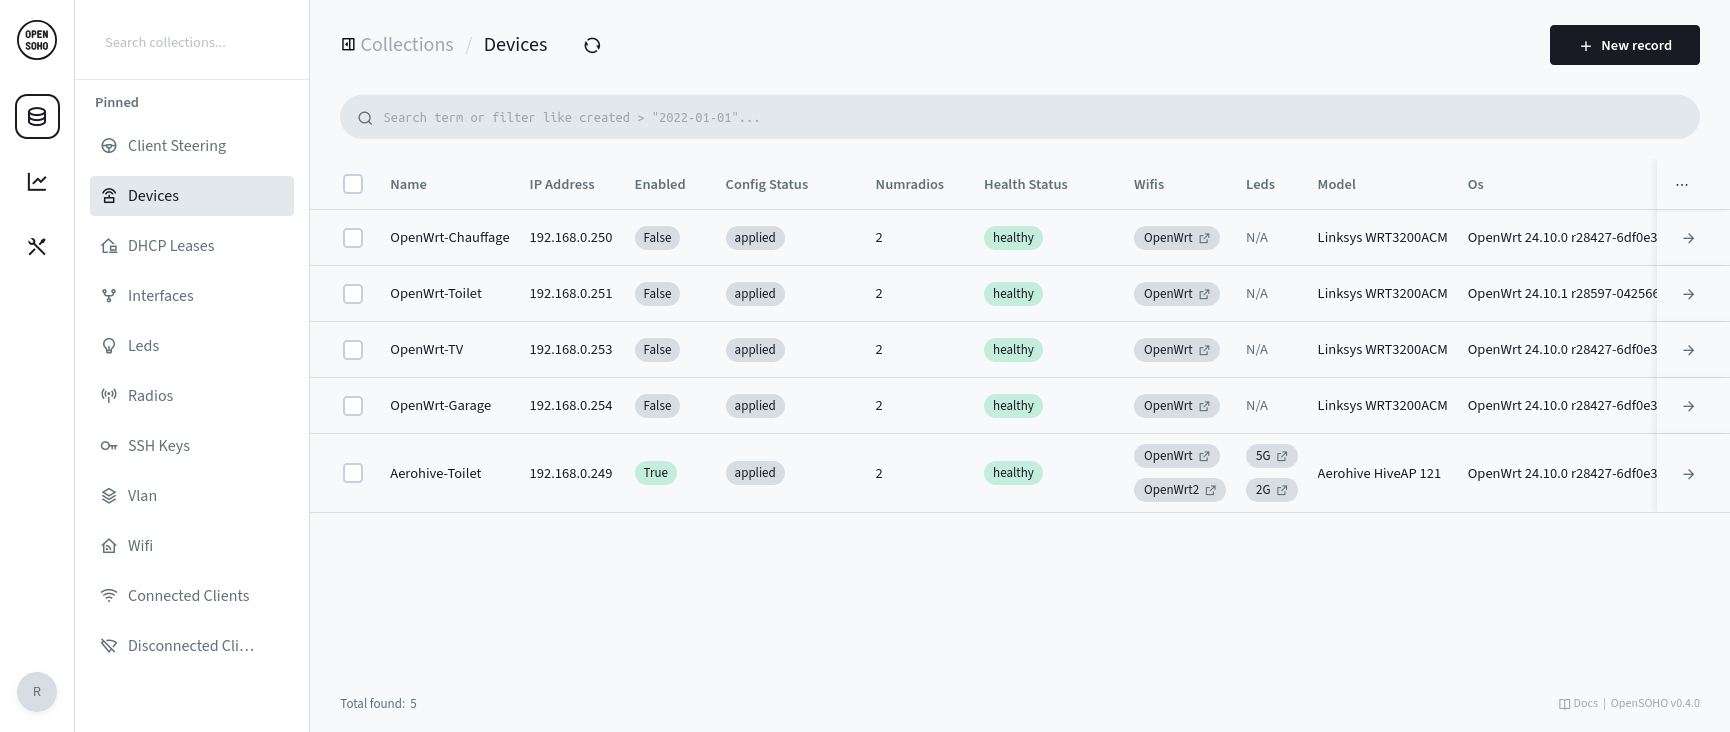
Lightweight OpenWRT device management platform for small networks. Centralized configuration, monitoring, and WiFi management for 2–20 devices with…

A horizontally scalable Direct Server Return layer 4 load balancer for Linux using XDP/eBPF

Scalable API key server for issuing, verifying, and revoking credentials with token derivation for fine-grained capability tokens. Supports…

Like Envoy xDS, but for eBPF filters

An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.

Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration

Terraform module to manage AWS Security Groups. Currently, the ingress and egress rules support IPv4, IPv6, and Security Group ID inputs.

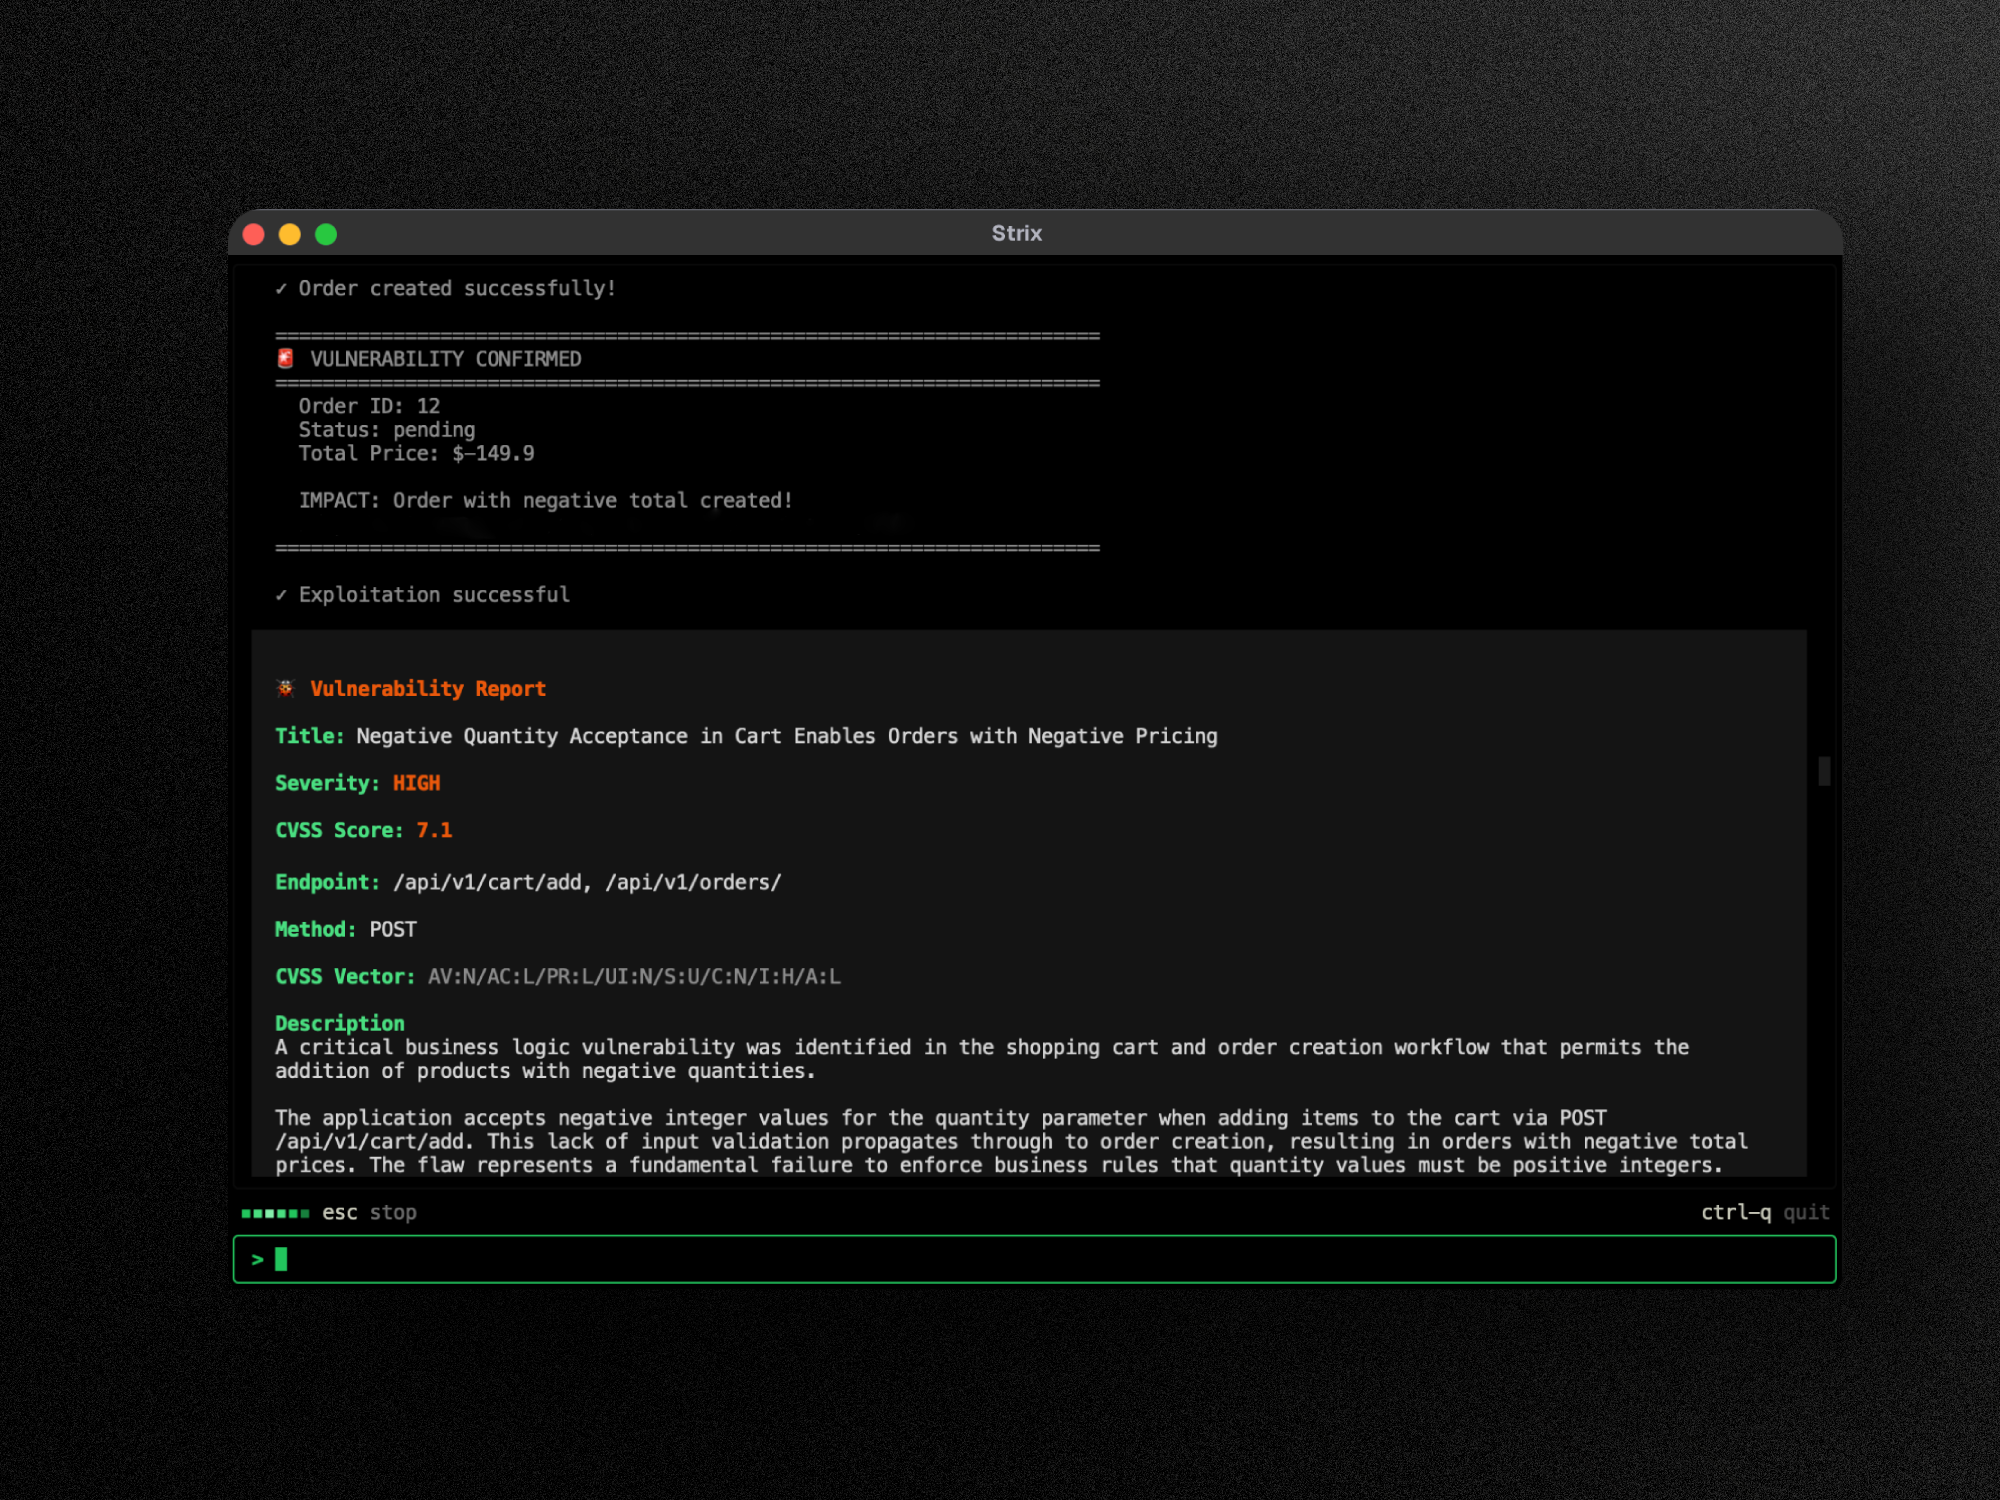
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.

Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…

Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more