
smolvm
 smol-machines/smolvm
An embeddable, portable, branchable virtual machine to safely run Agents locally.
cloud-infrastructure-securitycontainer-securitydevsecops+2
6.6k7h 16m ago
smol-machines/smolvmAn embeddable, portable, branchable virtual machine to safely run Agents locally.
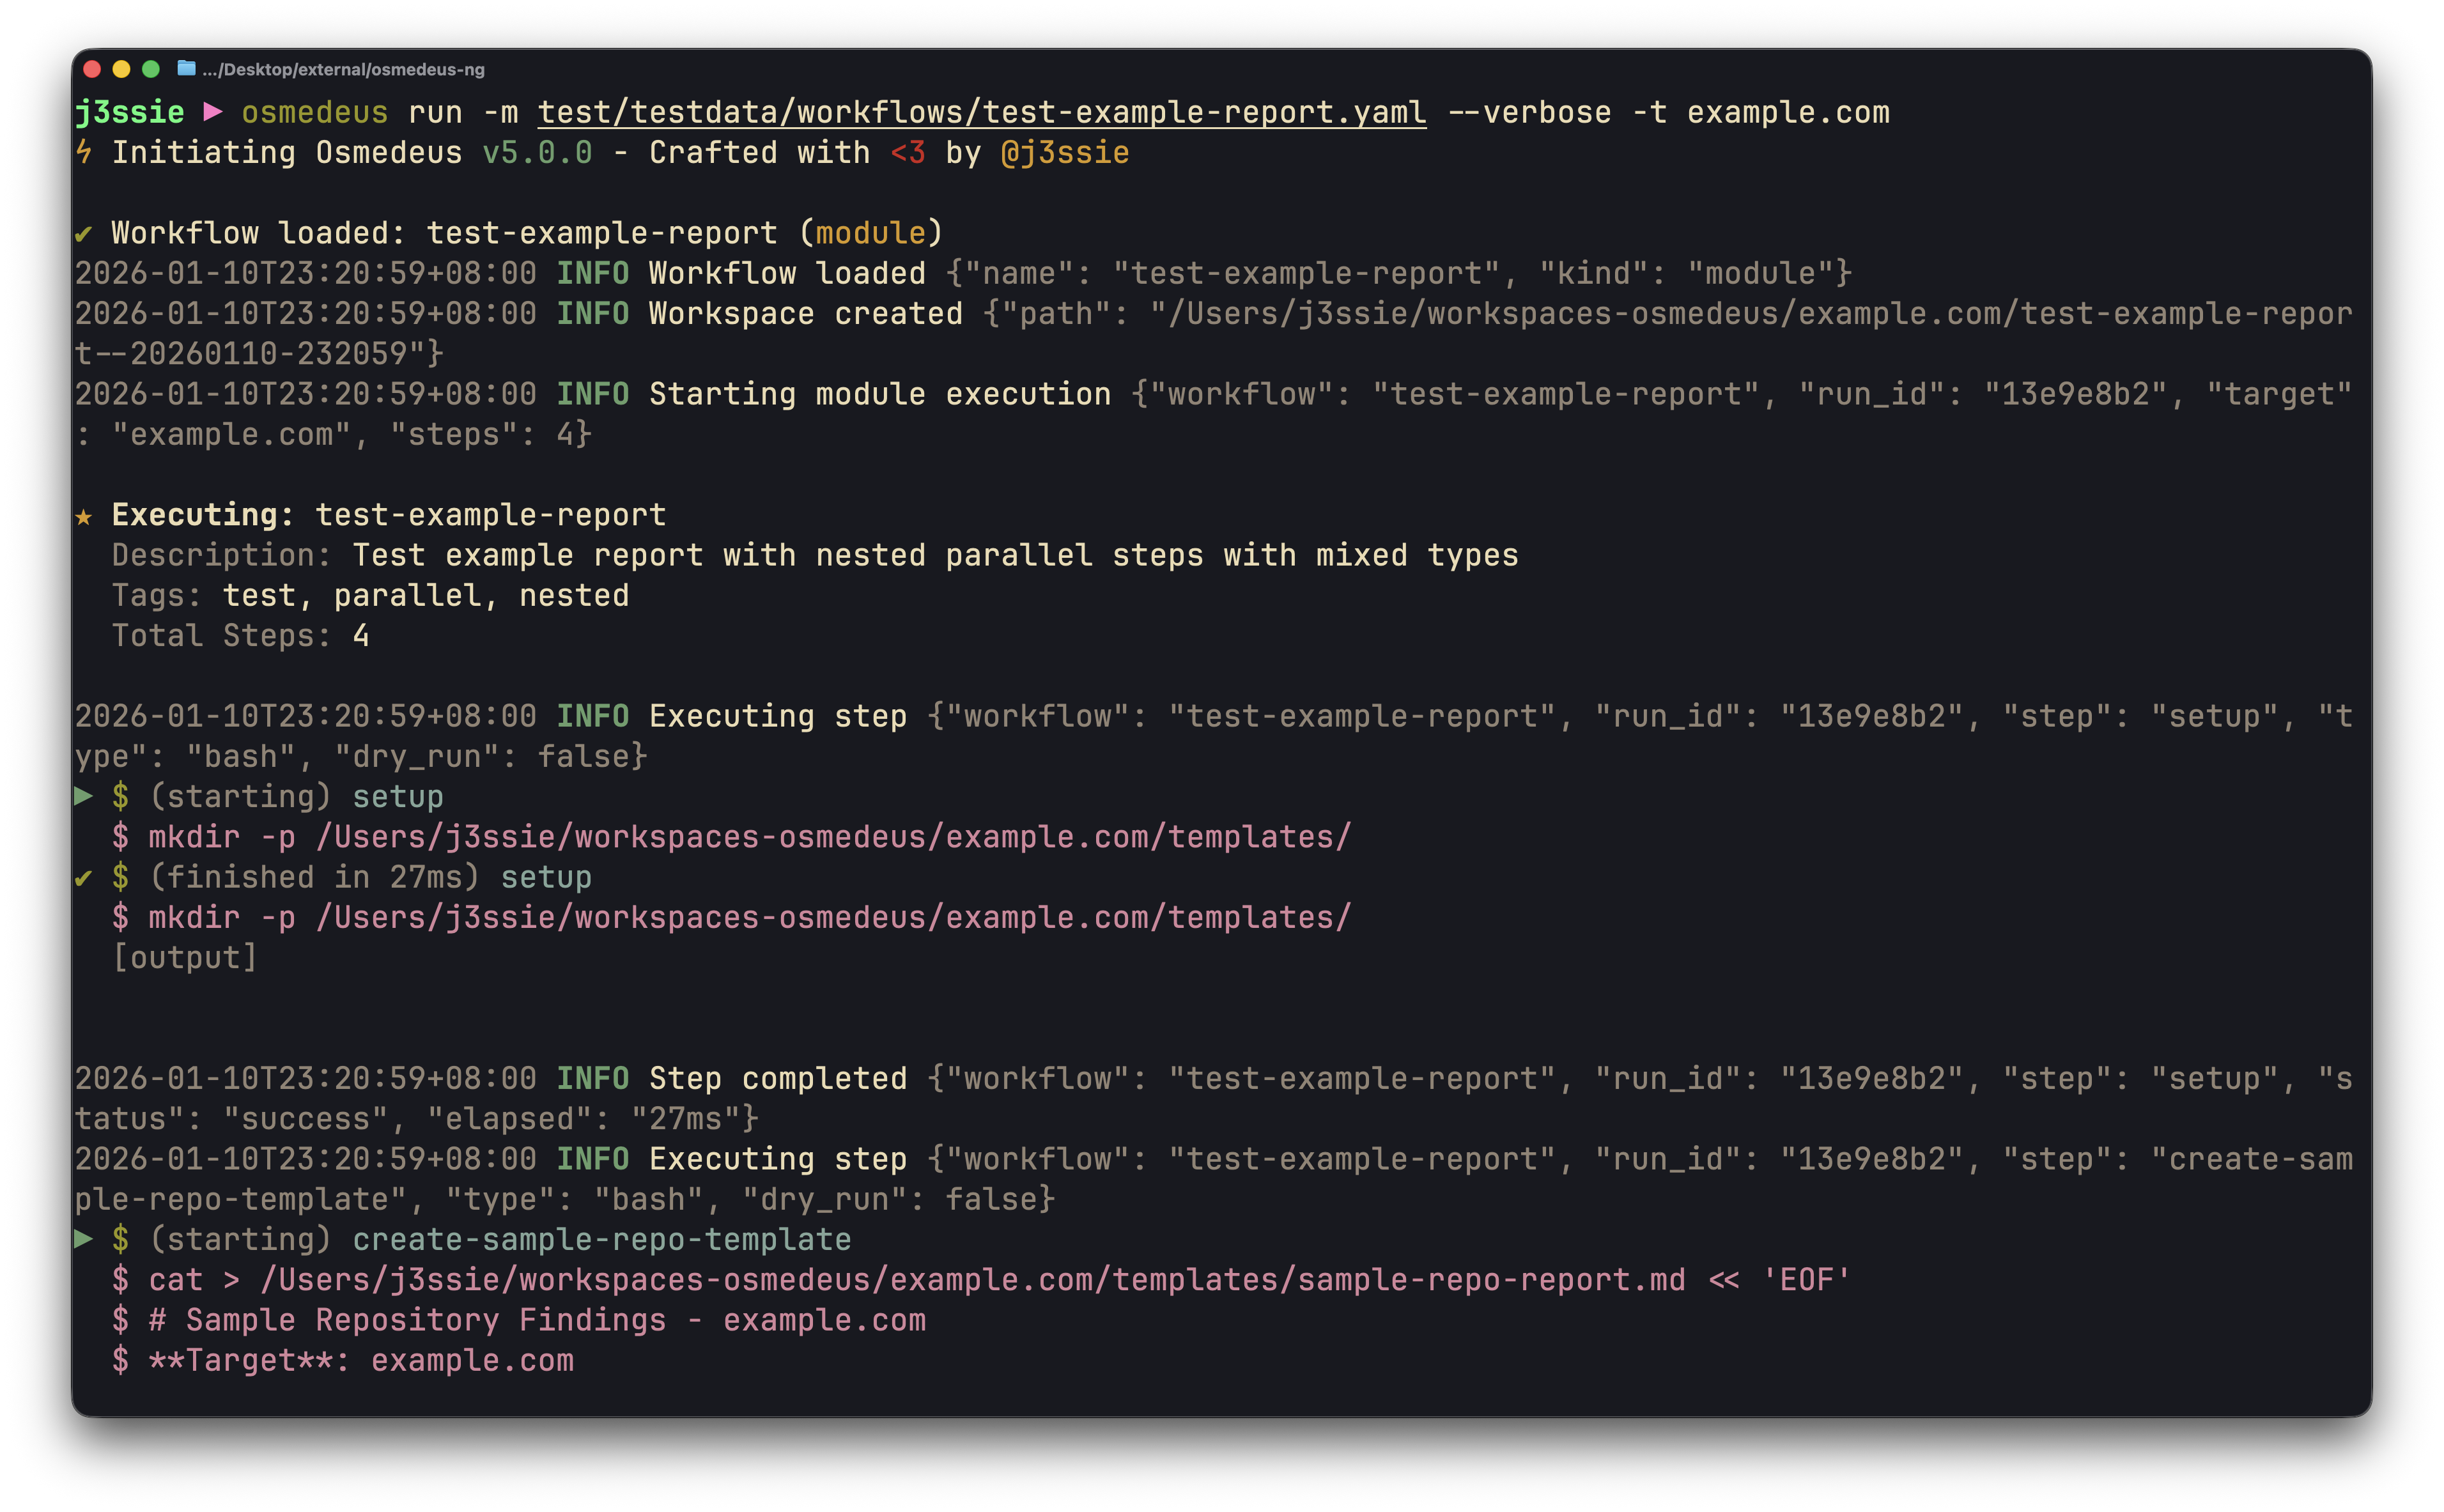 j3ssie/osmedeus
A Modern Orchestration Engine for Security
 chainguard-dev/melange
Compiles source code into auditable, signed APK packages using declarative pipelines for Wolfi/Alpine, with multi-architecture QEMU emulation and…
 aikidosec/safe-chain
Protect against malicious code installed via npm, yarn, pnpm, npx, pnpx, pip, uv and poetry with Aikido Safe Chain. Free to use, no tokens required.
 inceptionstack/lowkey
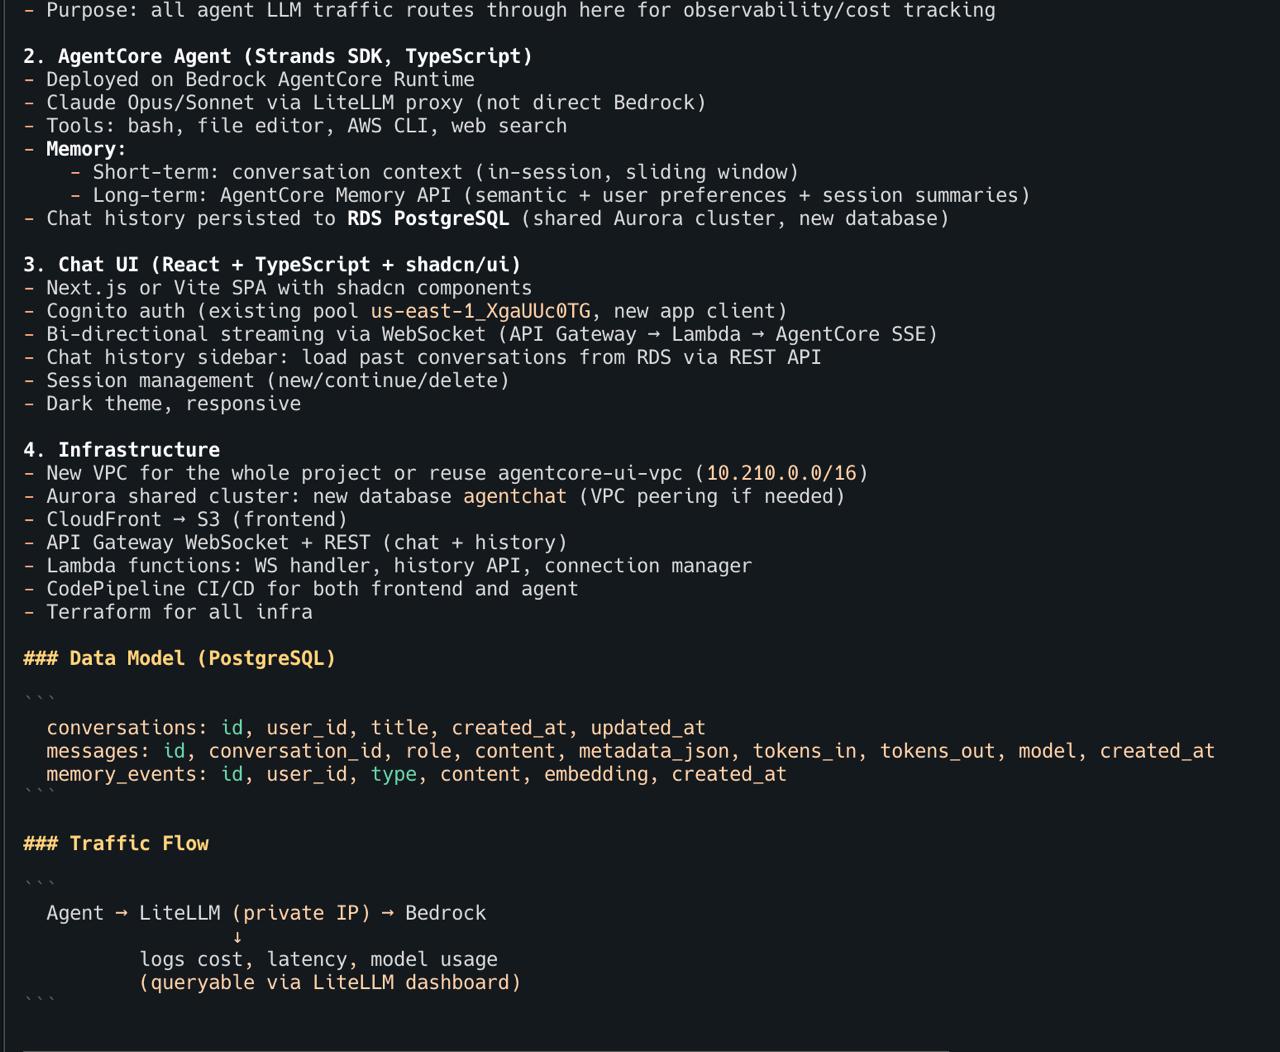
Deploy self-hosted AI coding agents (OpenClaw, Claude Code, Codex) into your AWS account with CloudFormation, IAM profiles, and sandbox isolation for…
 aws/serverless-application-model
Transforms SAM templates into CloudFormation resources, generating Lambda functions, IAM roles, and policies with built-in serverless best practices.
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 aquasecurity/vuln-list-update
Automated vulnerability data aggregator that collects advisories from NVD, OSV, Alpine, Red Hat, and 20+ other sources into a unified parsable format…
 godaddy/tartufo
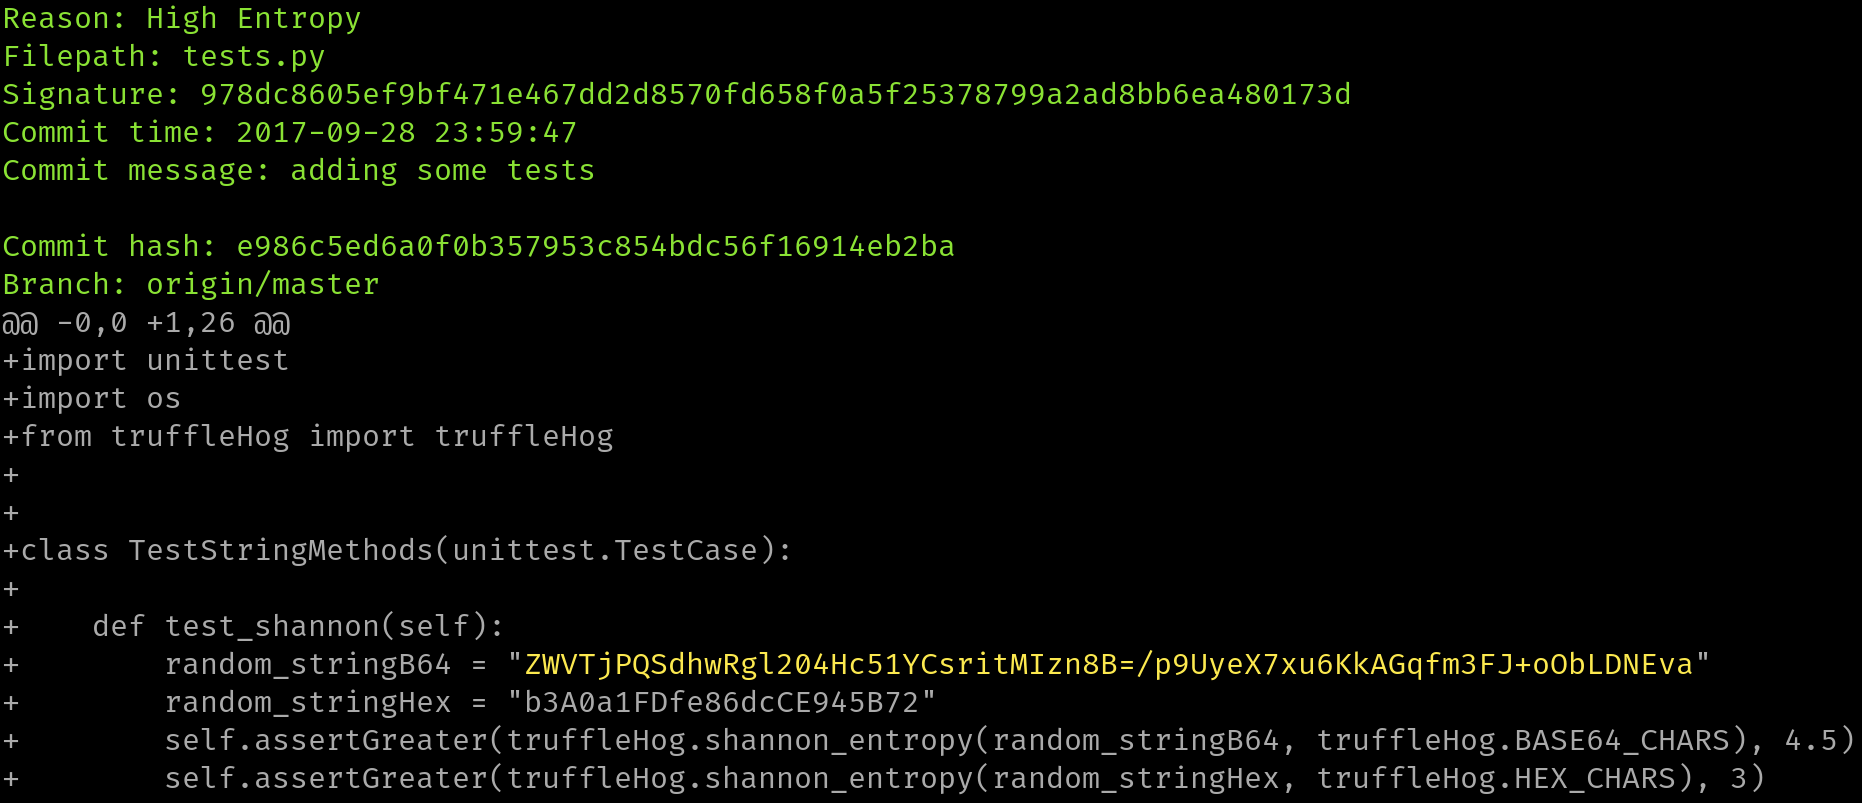
Searches through git repositories for high entropy strings and secrets, digging deep into commit history
 hoppr/hoppr-cop
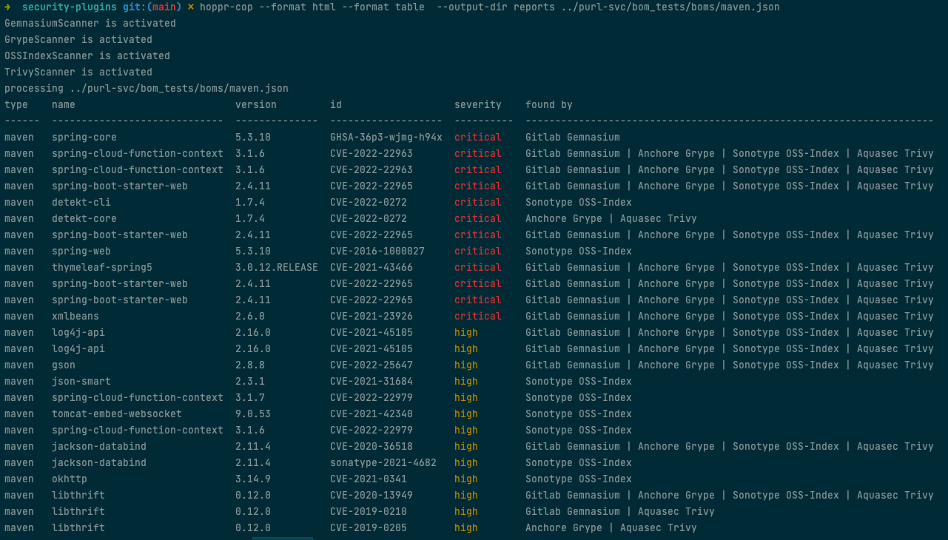
Aggregates vulnerability data from multiple databases into CycloneDX SBOMs, generating deduplicated VEX, HTML, and GitLab-compatible reports for…
 defectdojo/django-defectdojo
Open-Source Unified Vulnerability Management, DevSecOps & ASPM
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 danthegoodman1/netfence
Like Envoy xDS, but for eBPF filters
 tejasprasad2008-afk/tracetree
Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…
 iaga-team/iaga-sentinel
Cryptographically signed, replay-verifiable evidence layer for AI agents. Governs actions in the loop, produces Ed25519-signed receipts linked into a…
 manishrawat21/cisa-kev-threat-intel-orchestrator
Zero-touch pipeline that turns newly weaponized CVEs from the CISA Known Exploited Vulnerabilities (KEV) catalog into production-ready Sigma…
 andreicscs/honeywire
Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…