
siper
 fksvs/siper
XDP Based Lightweight and Fast Firewall
cloud-securityconfiguration-auditingdefensive-tools+3
fksvs/siperXDP Based Lightweight and Fast Firewall
 arisharazakhan-cpu/dod-blue-team-network-lab
High fidelity defensive security lab simulating a DoD aligned enterprise network with Active Directory, VLAN segmentation, STIG based hardening,…
 owasp/intrusion-alert-educational-network-ids
Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
 raniaemran/cve-2024-36401-security-simulator
Educational Python simulator modeling a fictional security incident inspired by CVE-2024-36401 to demonstrate vulnerability management, segmentation,…
 fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 owerdogan/whoami-project
Whoami provides enhanced privacy, anonymity for Debian and Arch based linux distributions
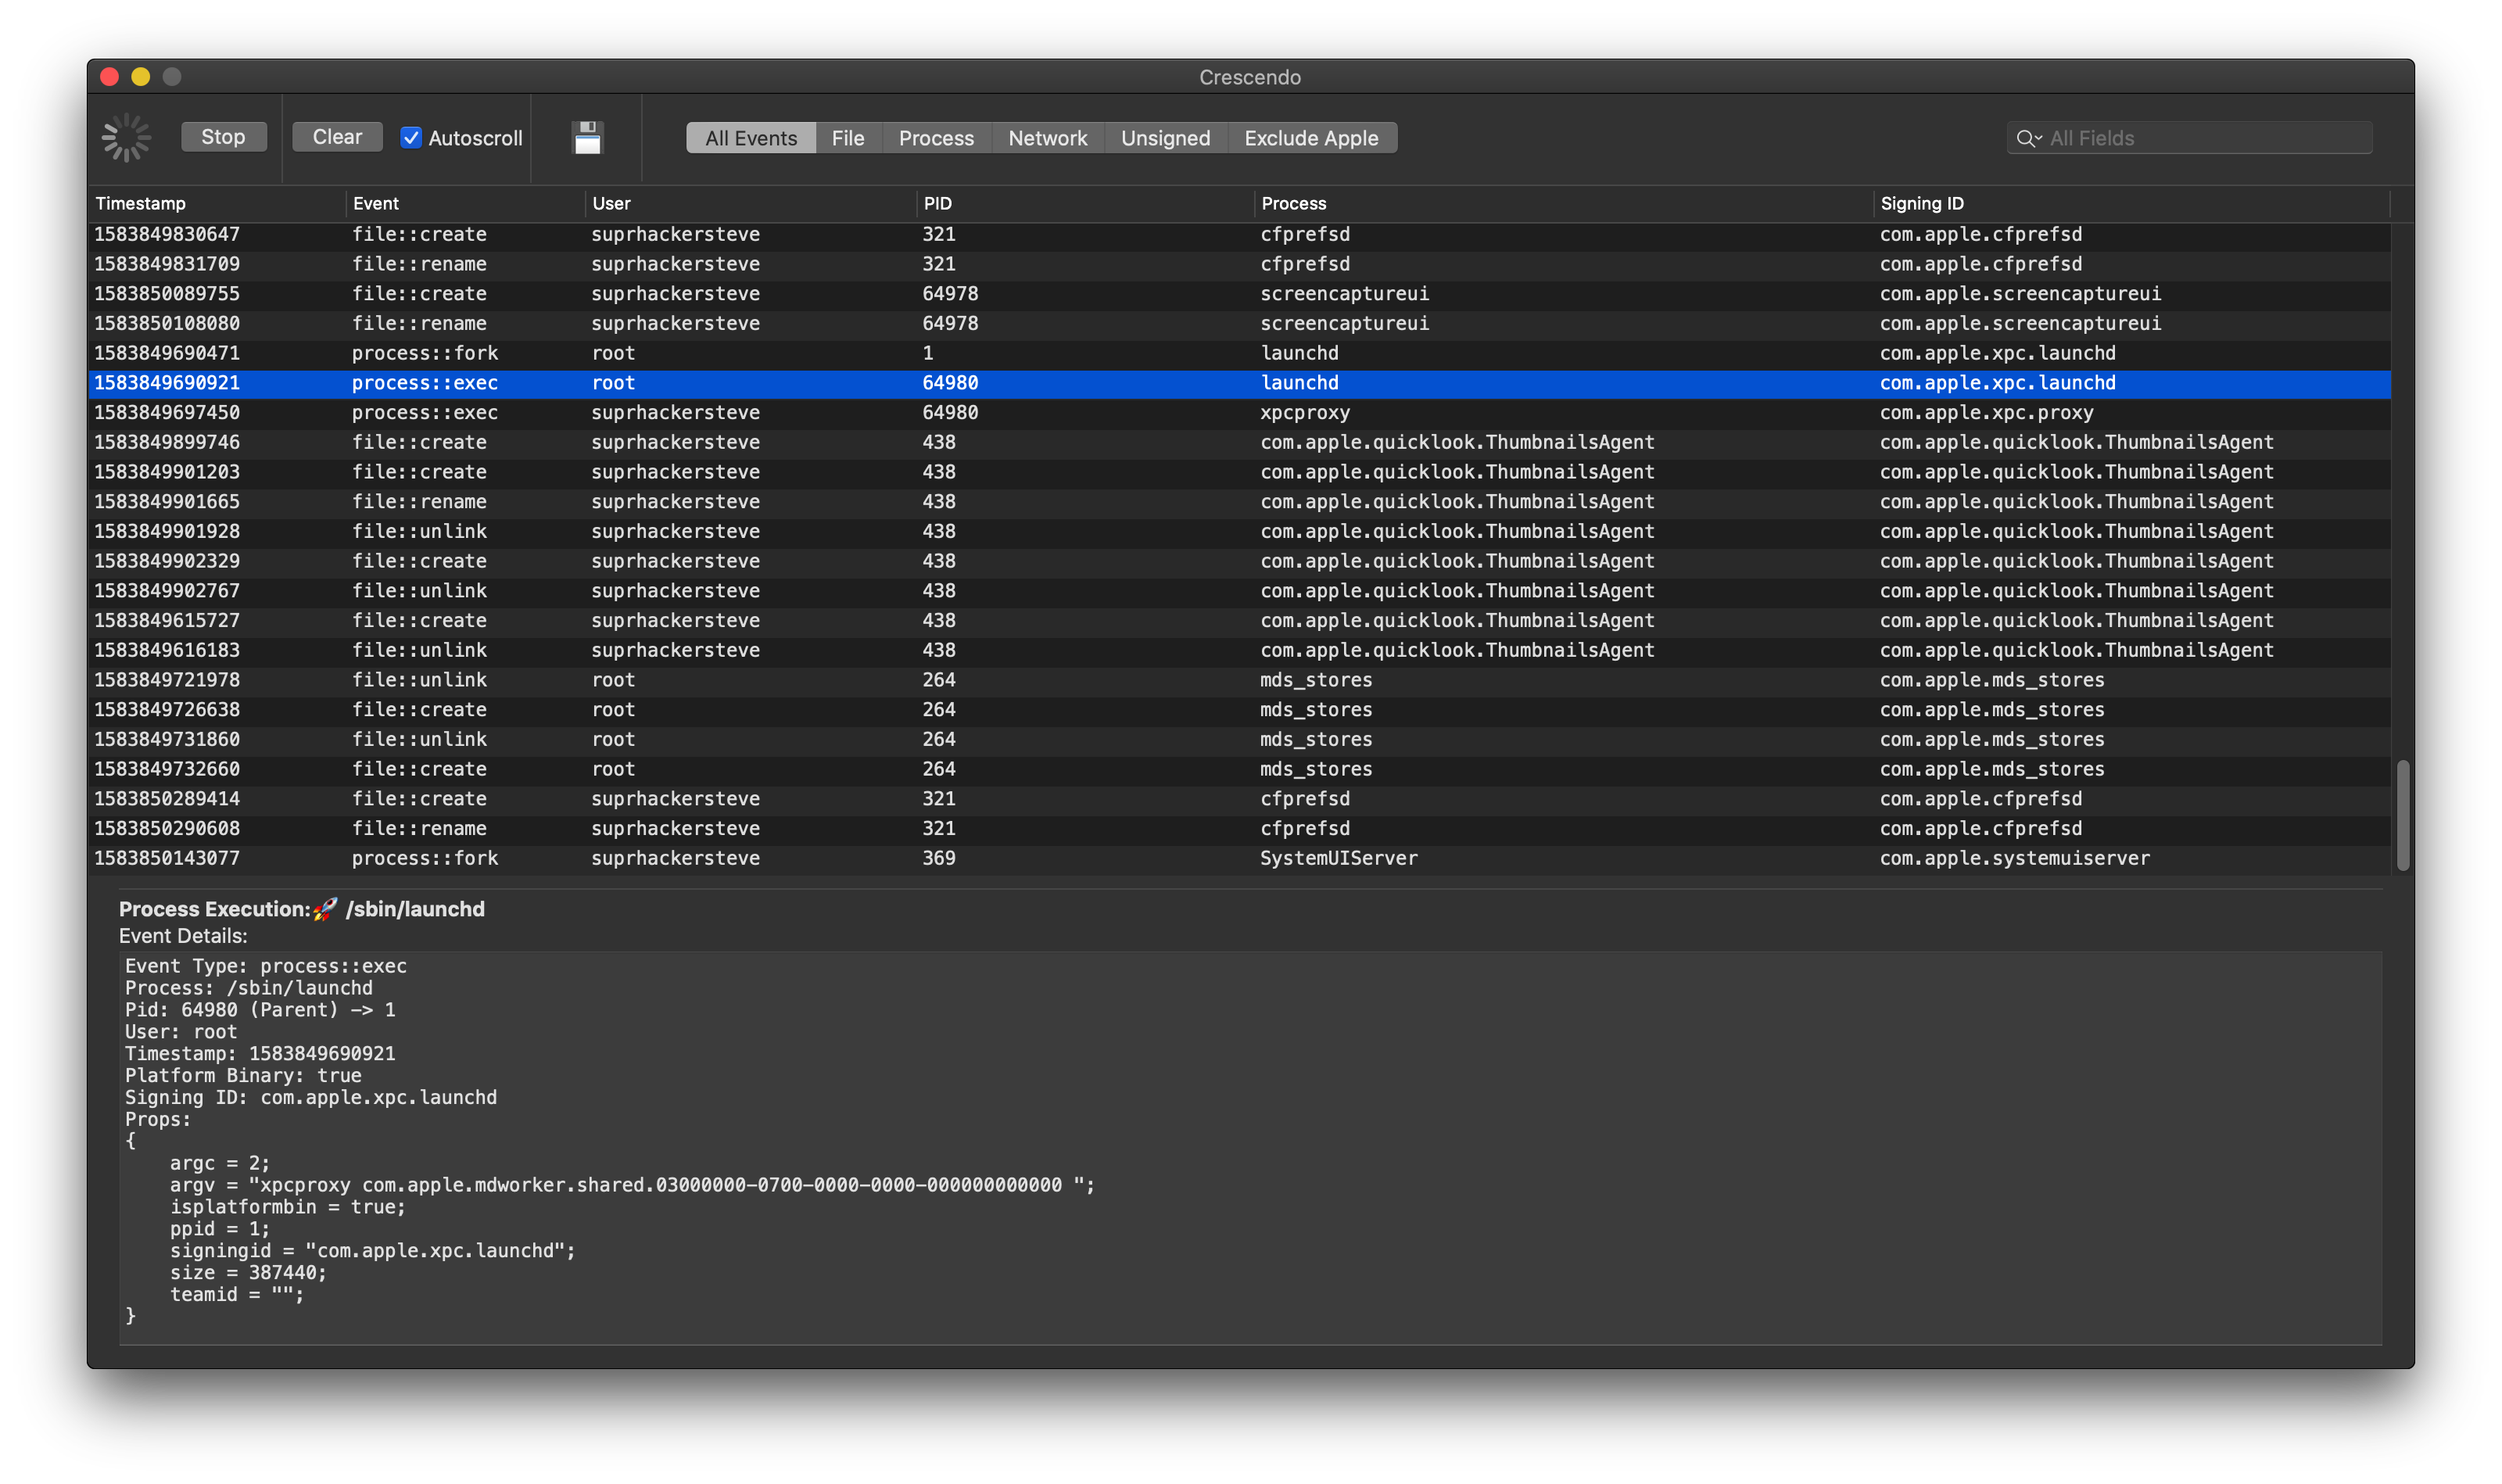 suprhackersteve/crescendo
Crescendo is a swift based, real time event viewer for macOS. It utilizes Apple's Endpoint Security Framework.
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.
 cyberark/ketshash
A little tool for detecting suspicious privileged NTLM connections, in particular Pass-The-Hash attack, based on event viewer logs.
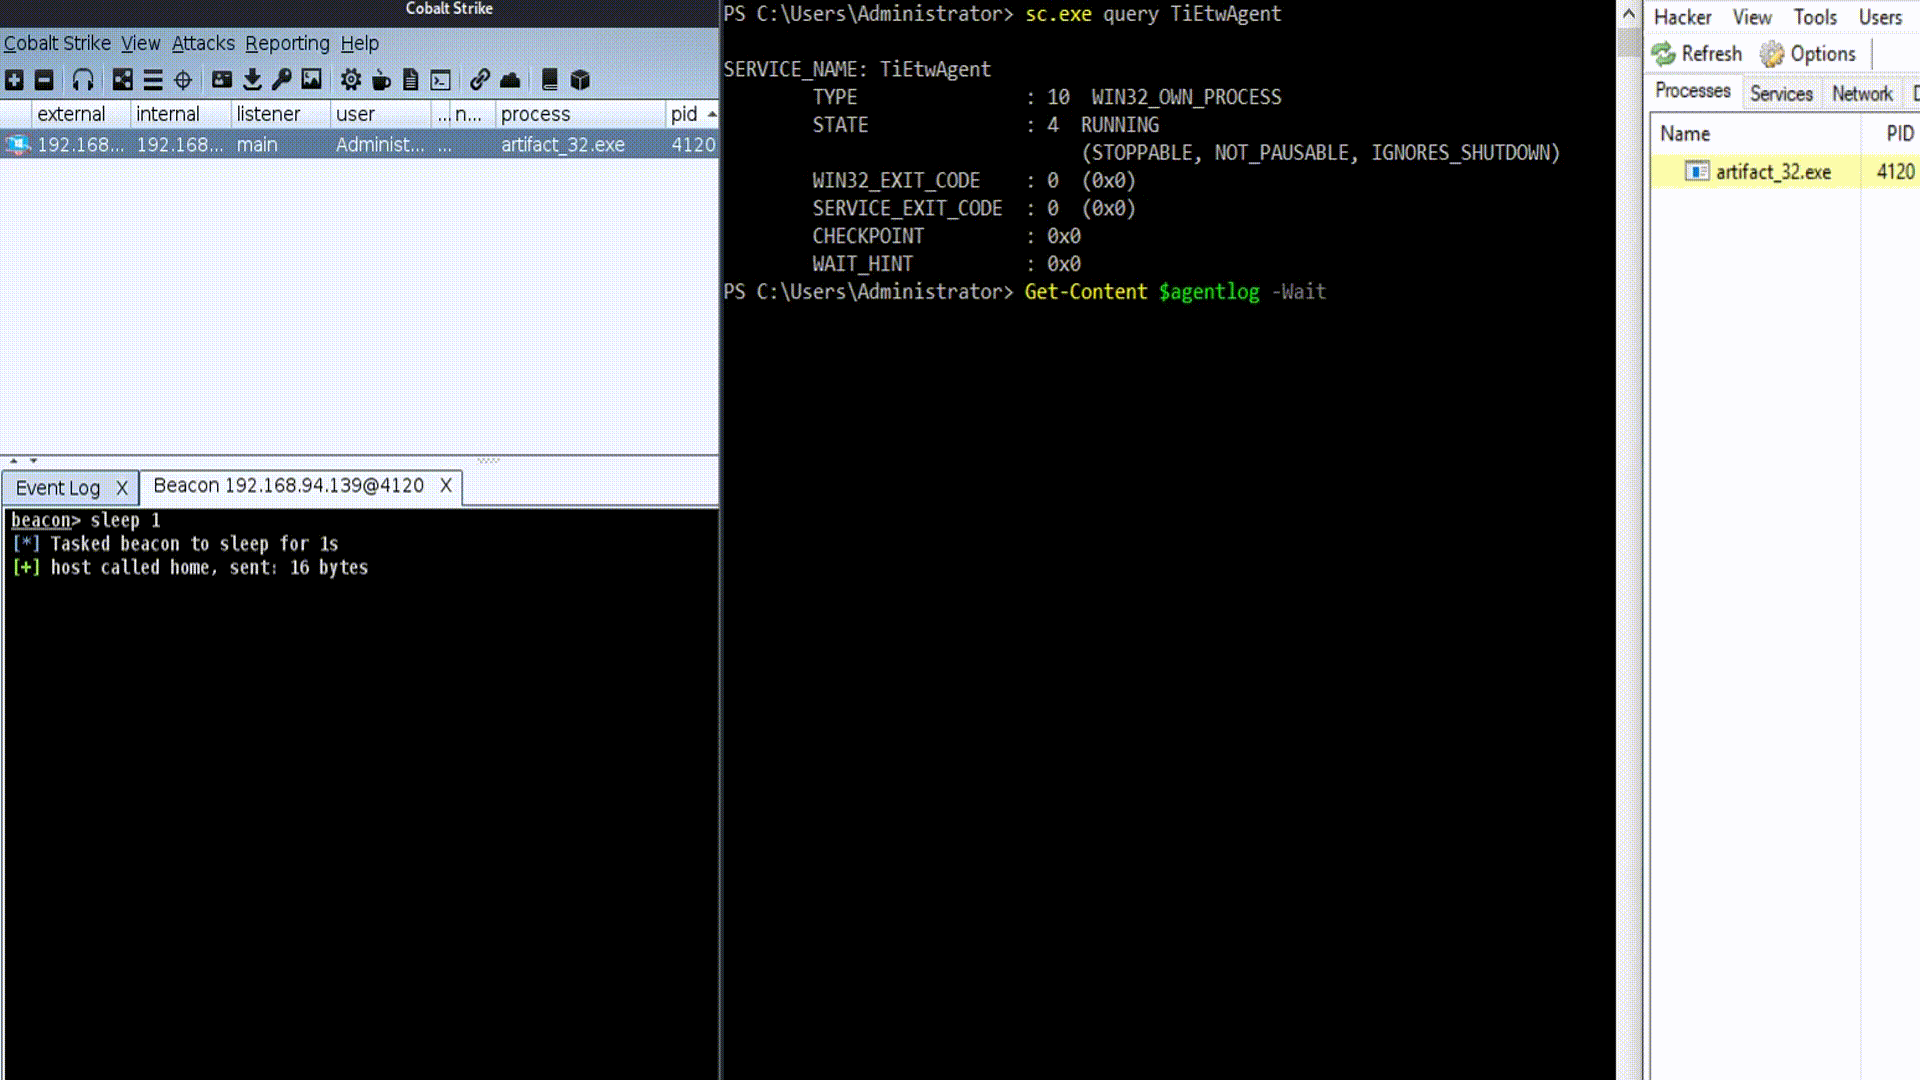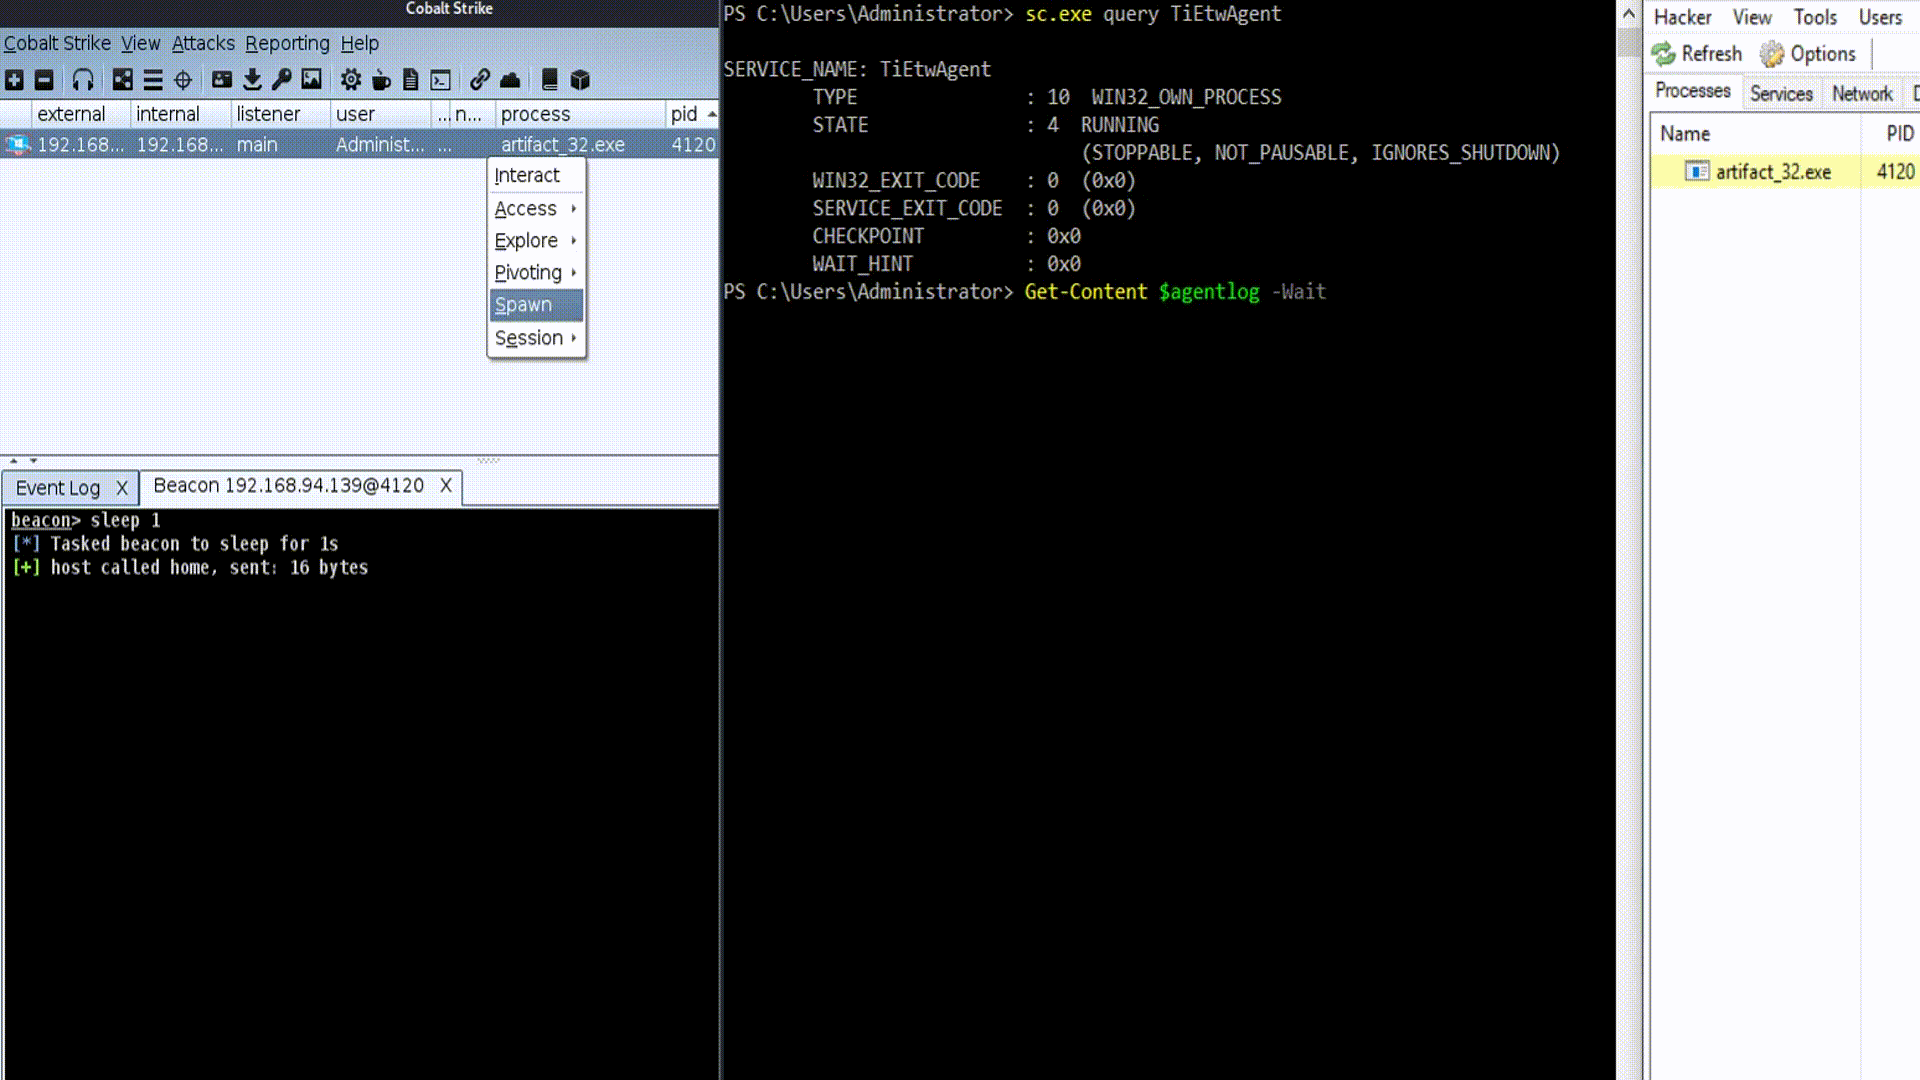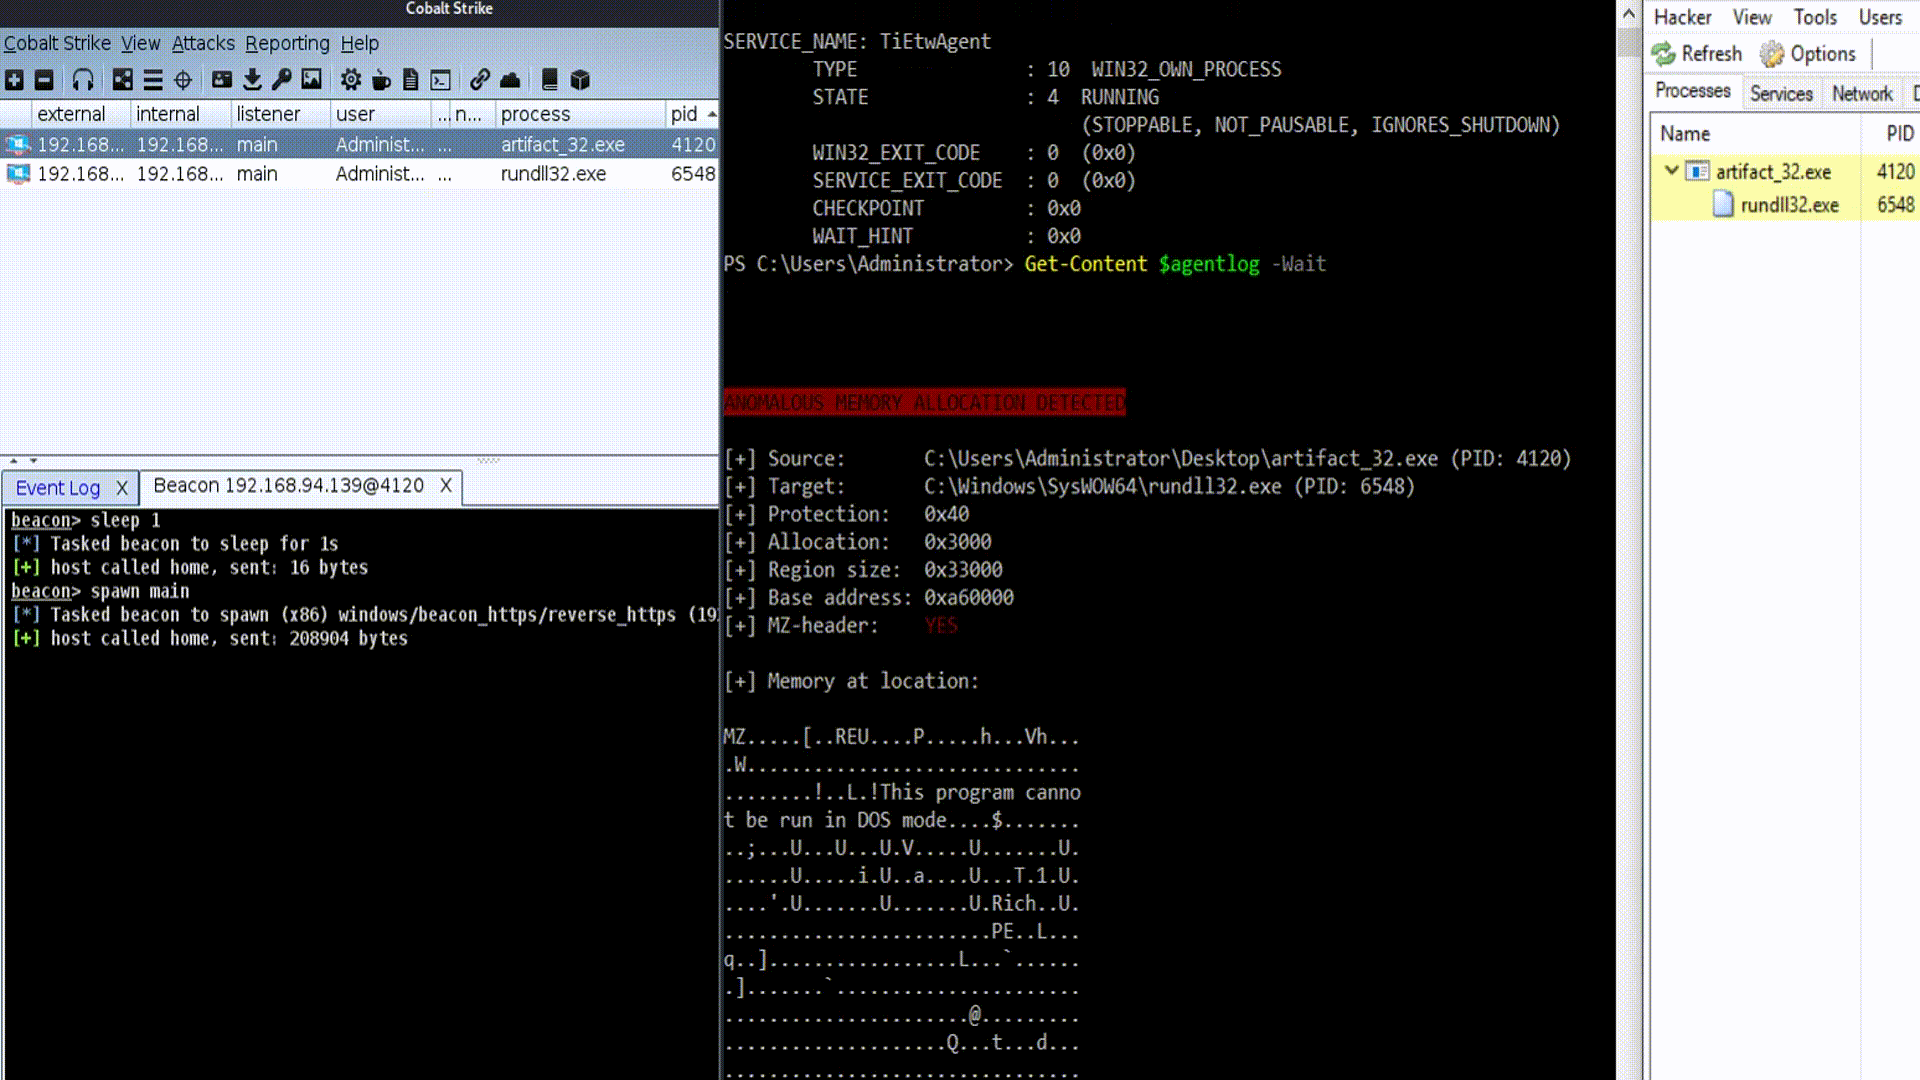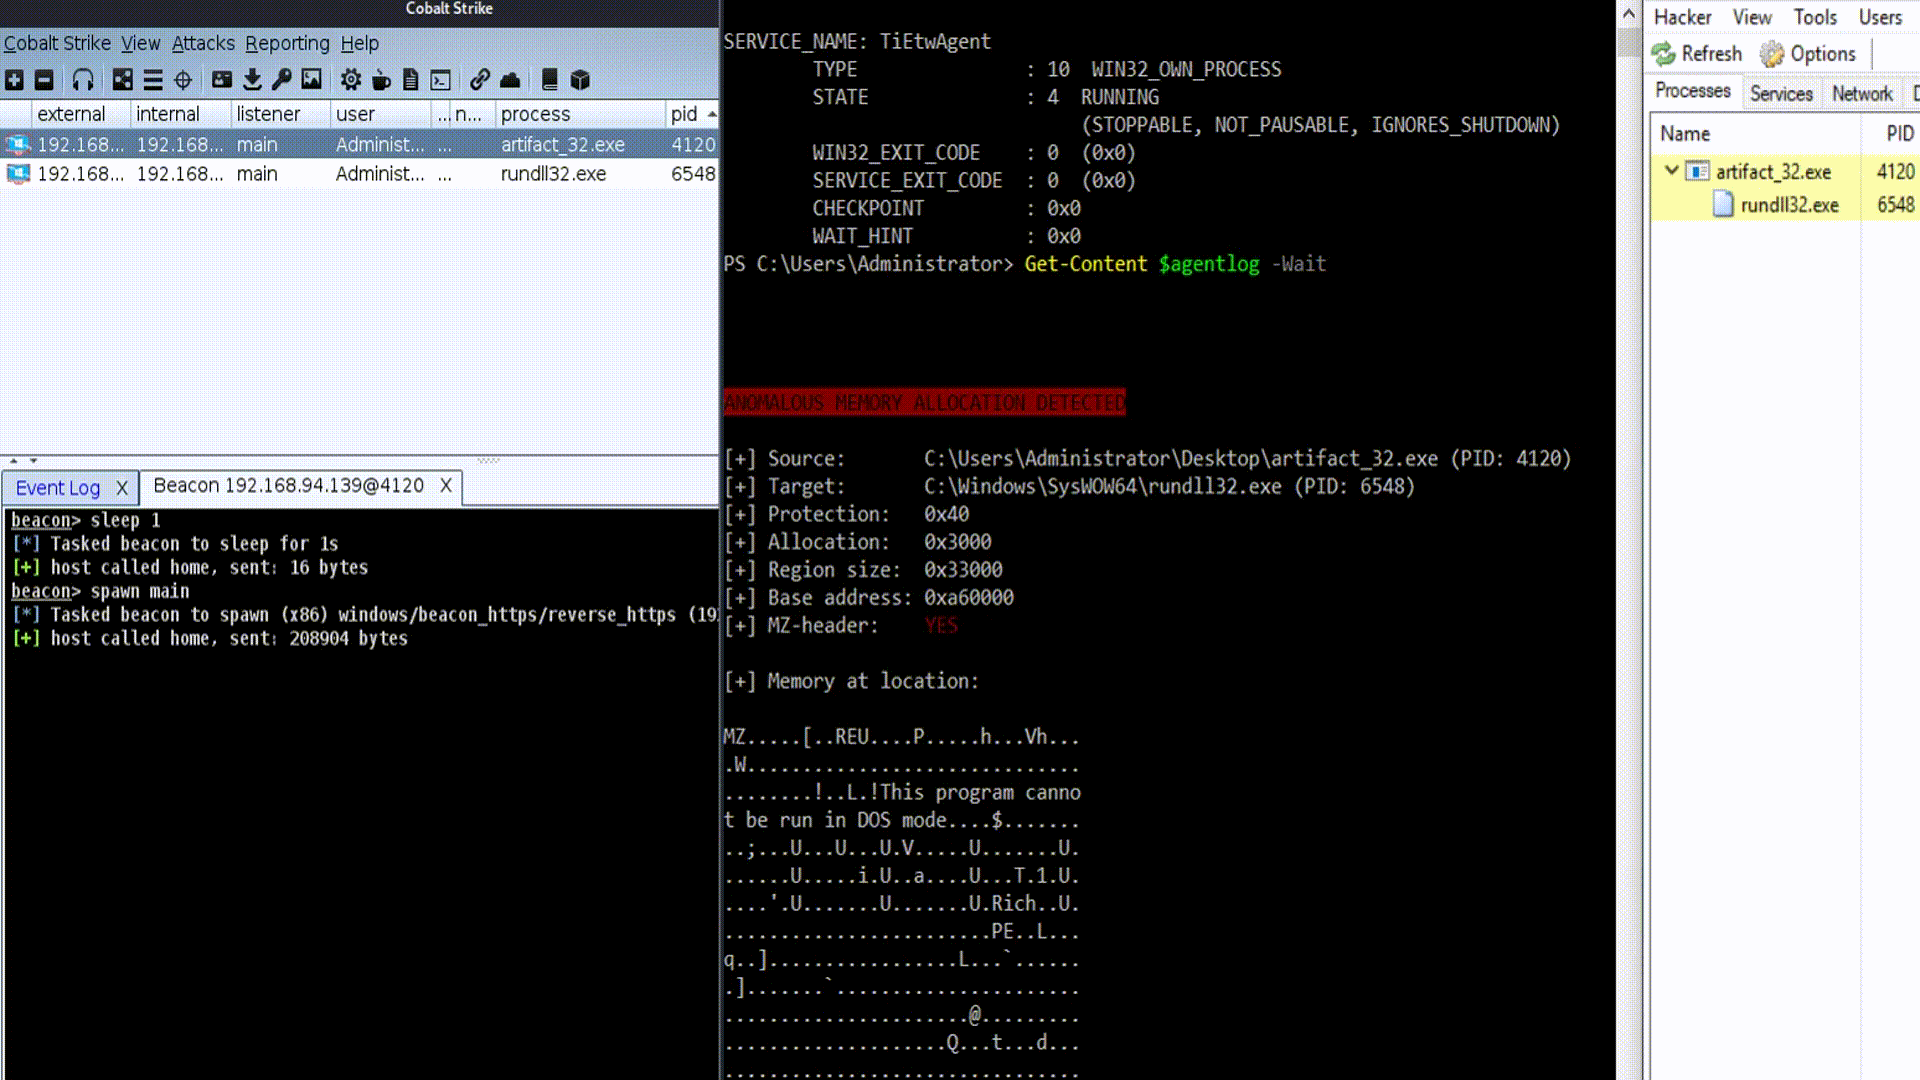 xuanxuan0/tietwagent
PoC memory injection detection agent based on ETW, for offensive and defensive research purposes
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
 theflink/hunt-weird-syscalls
ETW based POC to identify direct and indirect syscalls
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
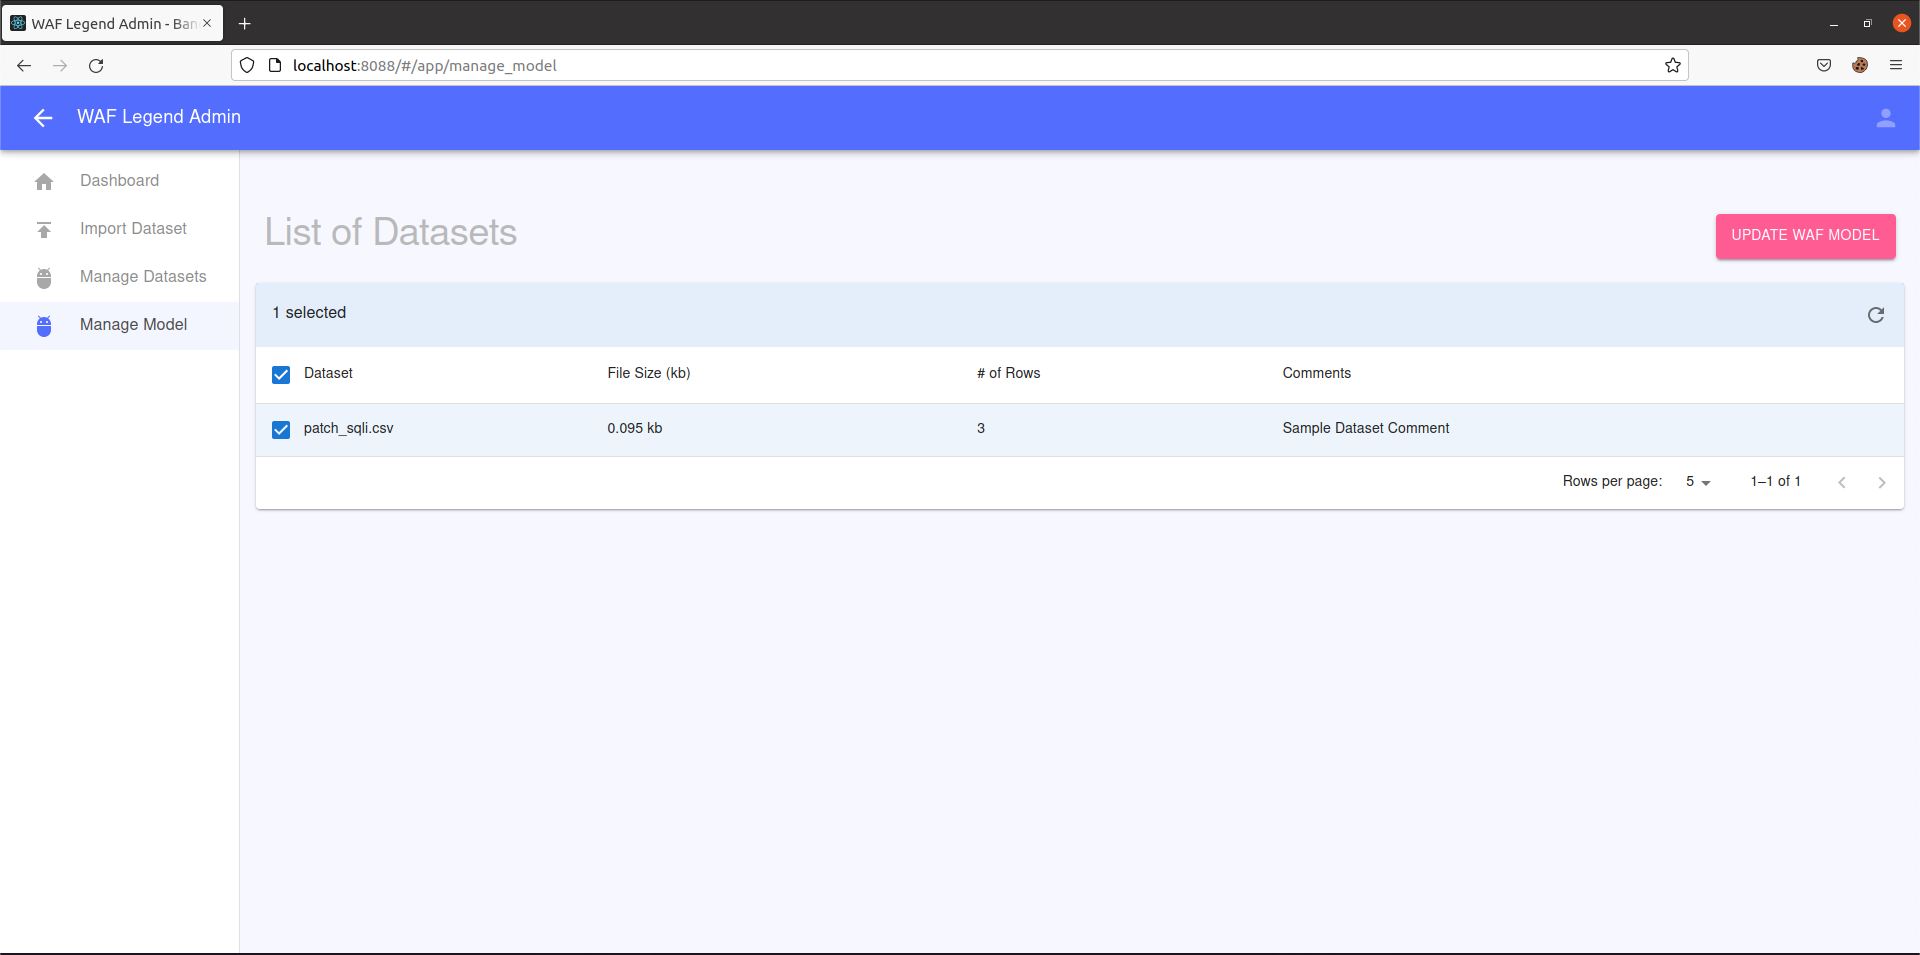 fa-pengfei/ngwaf
First iteration of ML based Feedback WAF
 rvazarkar/antipwny
A host based IDS written in C# Targetted at Metasploit