
Archived
tyton
 nbulischeck/tyton
Kernel-Mode Rootkit Hunter
defensive-toolsincident-responseintrusion-detection+1
371
 oisf/libhtp
Security-aware HTTP protocol parser library used by IDS/IPS engines to inspect and normalize HTTP traffic for threat detection.
 mozilla/bleach
Bleach is an allowed-list-based HTML sanitizing library that escapes or strips markup and attributes
 mozilla/mozdef
DEPRECATED - MozDef: Mozilla Enterprise Defense Platform
 elbraino/awesome-blackhat-arsenal
Curated collection of cybersecurity tools featured in Black Hat Arsenal events.
 aa22396584/synology-nas-cli
nas: a zero-dependency Python CLI + MCP server for Synology DSM 7. One-command audit and fix for the C3RB3R / .L0CK3D ransomware campaign; hand it to…
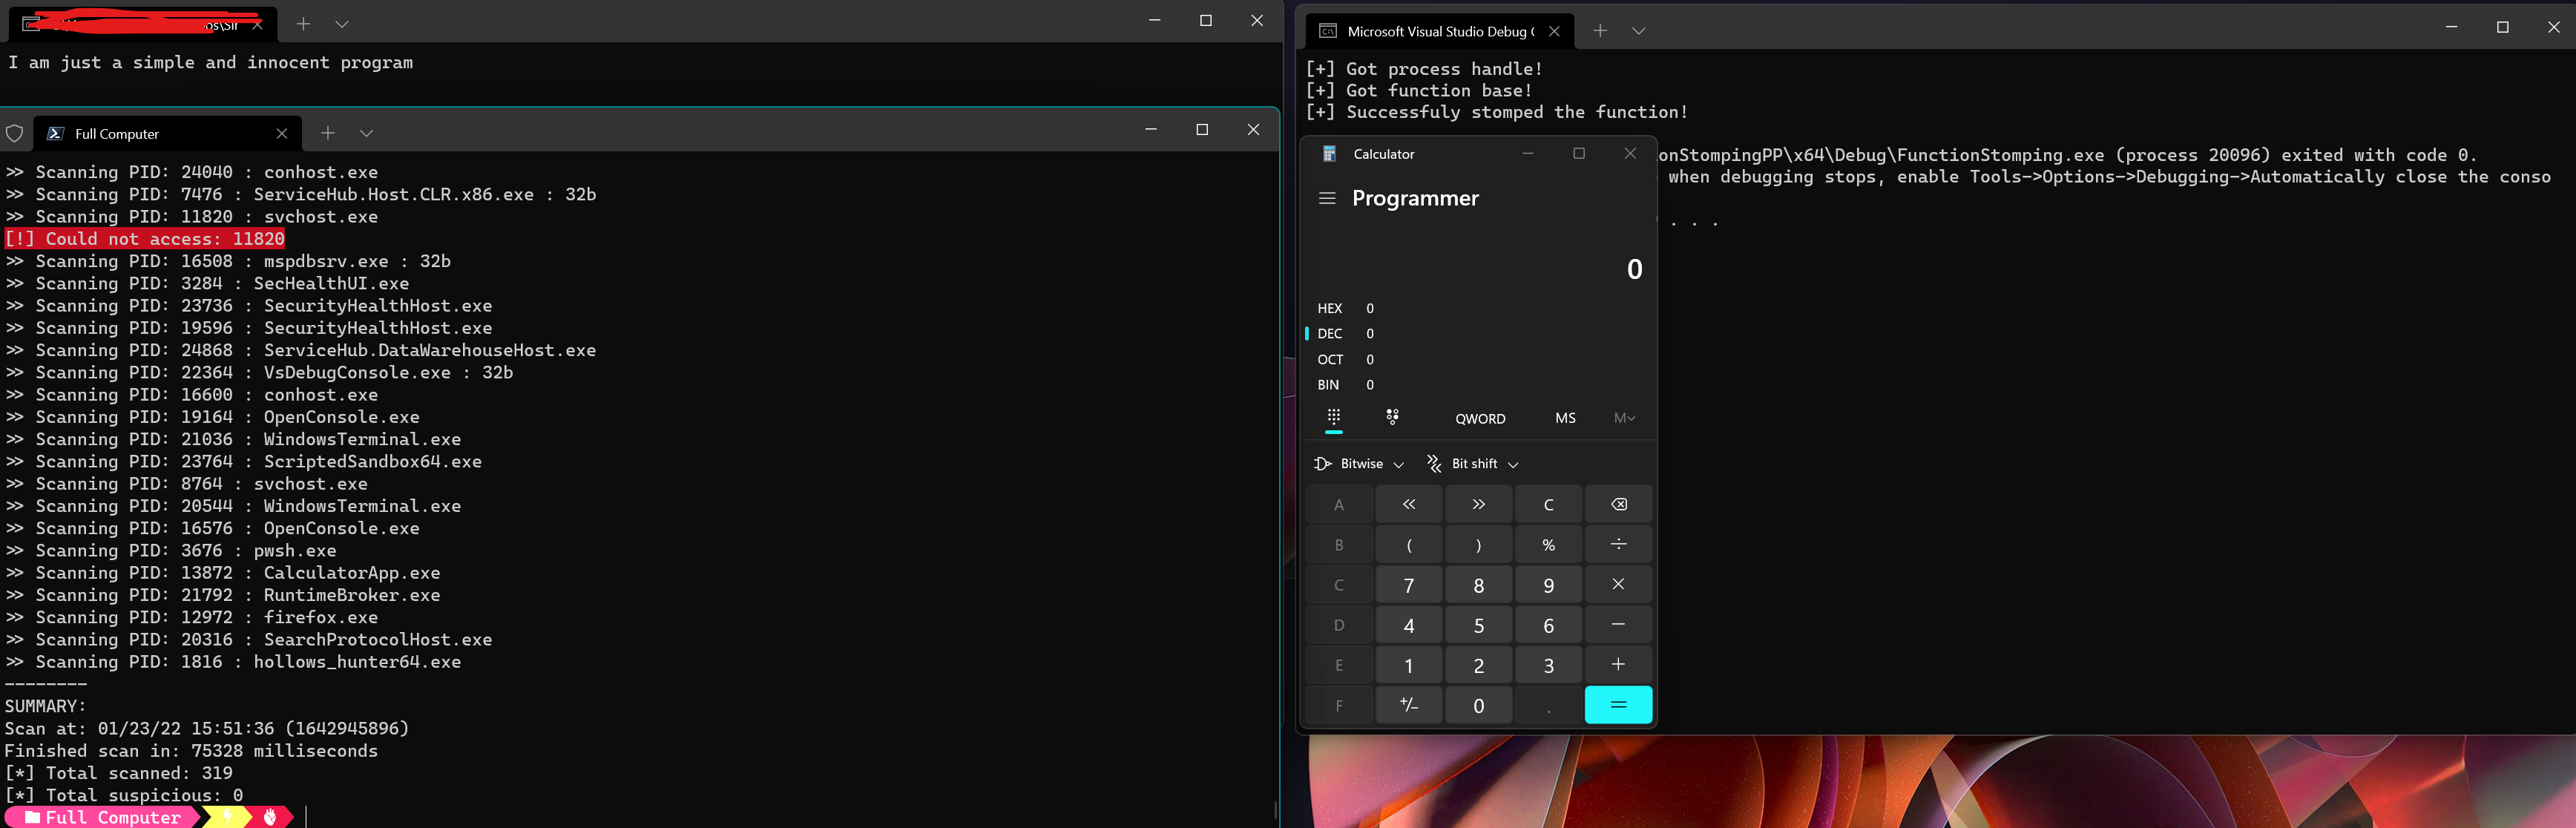 idov31/functionstomping
Shellcode injection technique. Given as C++ header, standalone Rust program or library.
 konstruktoid/prescryb
MCP server for CVE/config remediation orchestration: SSH inventory, OSV/NVD lookups, CIS/DISA STIG-mapped Ansible playbook suggestions.
 google/paranoid_crypto
Paranoid's library contains implementations of checks for well known weaknesses on cryptographic artifacts.
 fusion1110/ebpf-hid_guard
Linux kernel-space HID injection attack detector using eBPF. Monitors USB and Bluetooth HID devices for anomalous keystroke timing and automatically…
 optiv/dent
A framework for creating COM-based bypasses utilizing vulnerabilities in Microsoft's WDAPT sensors.
 chxhana/aligned-rag-eval
Lightweight evaluation harness for RAG poisoning defenses that builds four-condition clean/poisoned records and reports prevented targets, net…
 g0tmi1k/kippo-g0tmi1k
Medium-interaction SSH honeypot that logs brute force attacks and full attacker shell interactions, with customization options to reduce…
 itinerisltd/trellis-cve-2018-6389
Mitigate CVE-2018-6389 WordPress load-scripts / load-styles attacks
 xsanflip/anti-begal.py
Python script that exploits a resource-exhaustion flaw in the B.E.G.A.L C2 collector endpoint, flooding it with spoofed XOR/Base64 payloads to…
 jotaqc/cve-2022-30190_temporary_fix_source_code
These are the source codes of the Python scripts to apply the temporary protection against the CVE-2022-30190 vulnerability (Follina)
 cosmo121/follina-remediation
Removes the ability for MSDT to run, in response to CVE-2022-30190 (Follina)
 chryzsh/darthsidious
Building an Active Directory domain and hacking it