

BloodHound
 specterops/bloodhound
Six Degrees of Domain Admin
defensive-toolsidentity-access-managementinformation-gathering+4
3.5k13h 8m ago
specterops/bloodhoundSix Degrees of Domain Admin
 gorhill/ublock
Wide-spectrum content blocker for browsers that blocks ads, trackers, coin miners, and malicious sites using filter lists and customizable privacy…
 g4bri-3l3/idwolf
Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 mafifrizi/tanuki
Tactical Identity Operator for Linux & Hybrid Active Directory
 getprobo/probo
Open source solutions for SOC2, GDPR, and ISO27001
 ooni/probe-cli
Go measurement engine and CLI for detecting Internet censorship and network interference, running OONI network tests and reporting results to the…
 matijamiki/ranwhat
Flight recorder and secret scanner for AI coding agents. Reads what Claude Code, Codex, Gemini CLI and 17 more ran, and flags risky actions and…
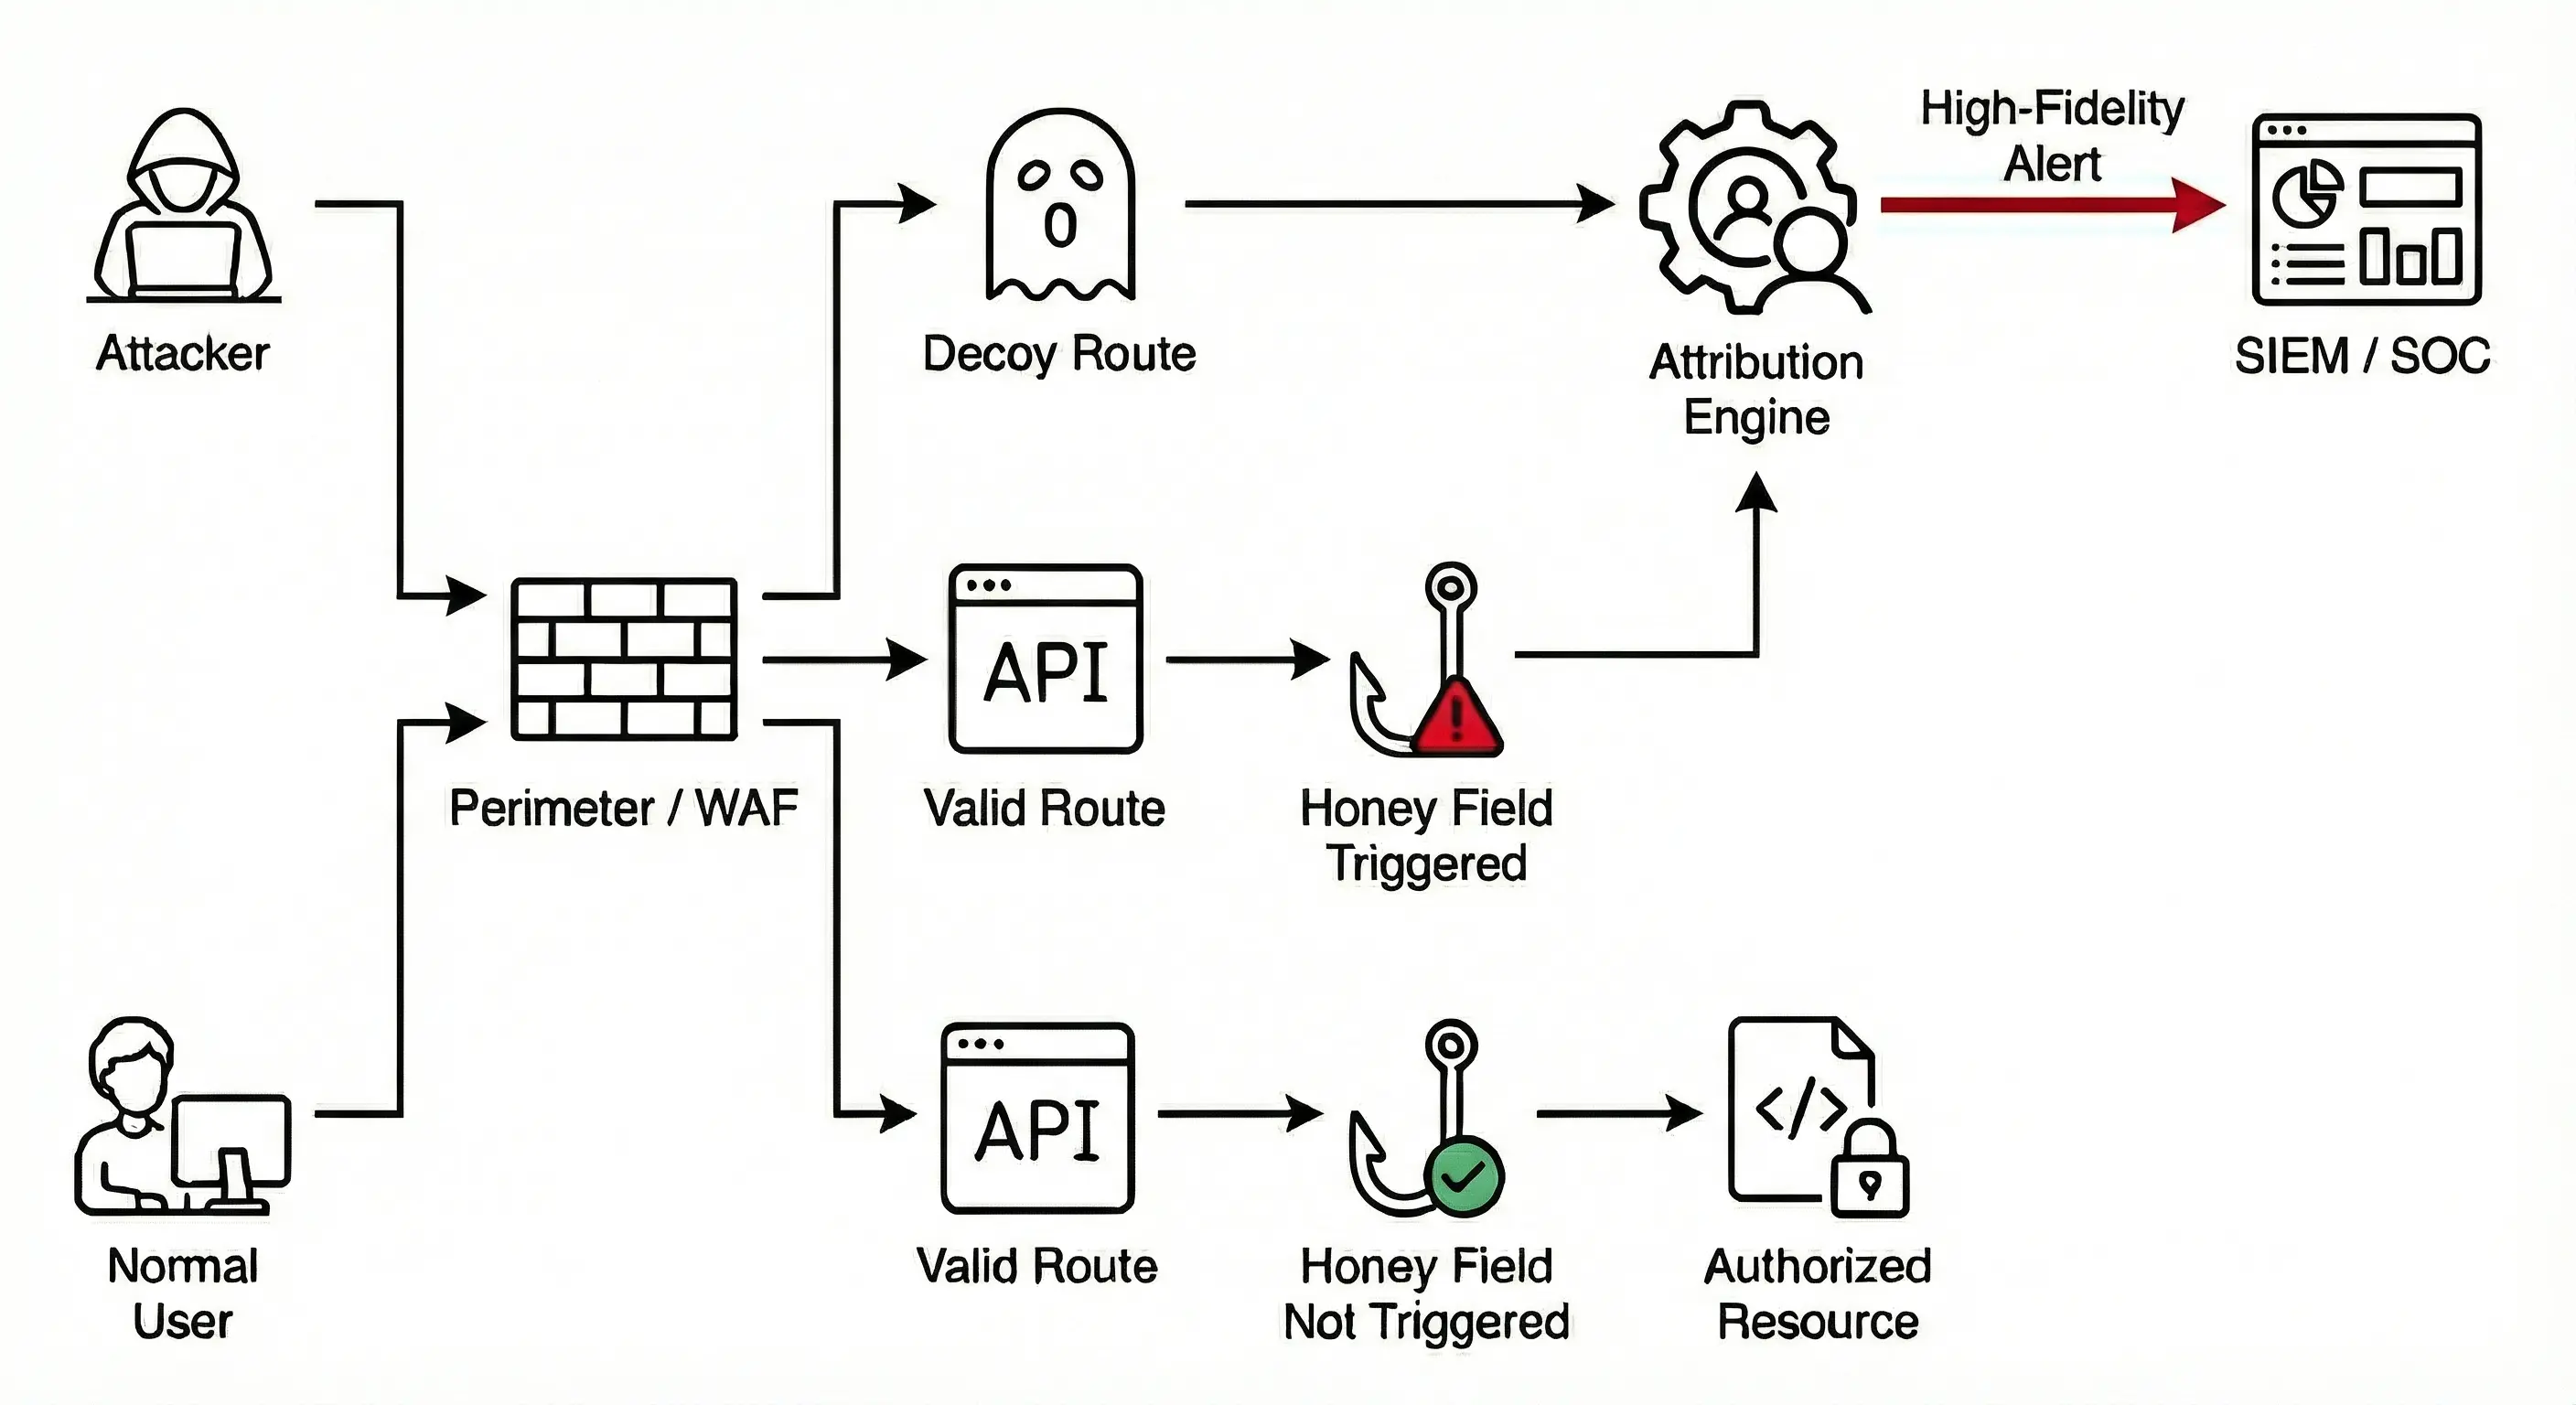 trappsec-dev/trappsec
Open-source framework for embedding realistic decoy routes and honey fields into APIs to detect attackers probing business logic, converting…
 brentmartinmiller/php2shell-check
Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
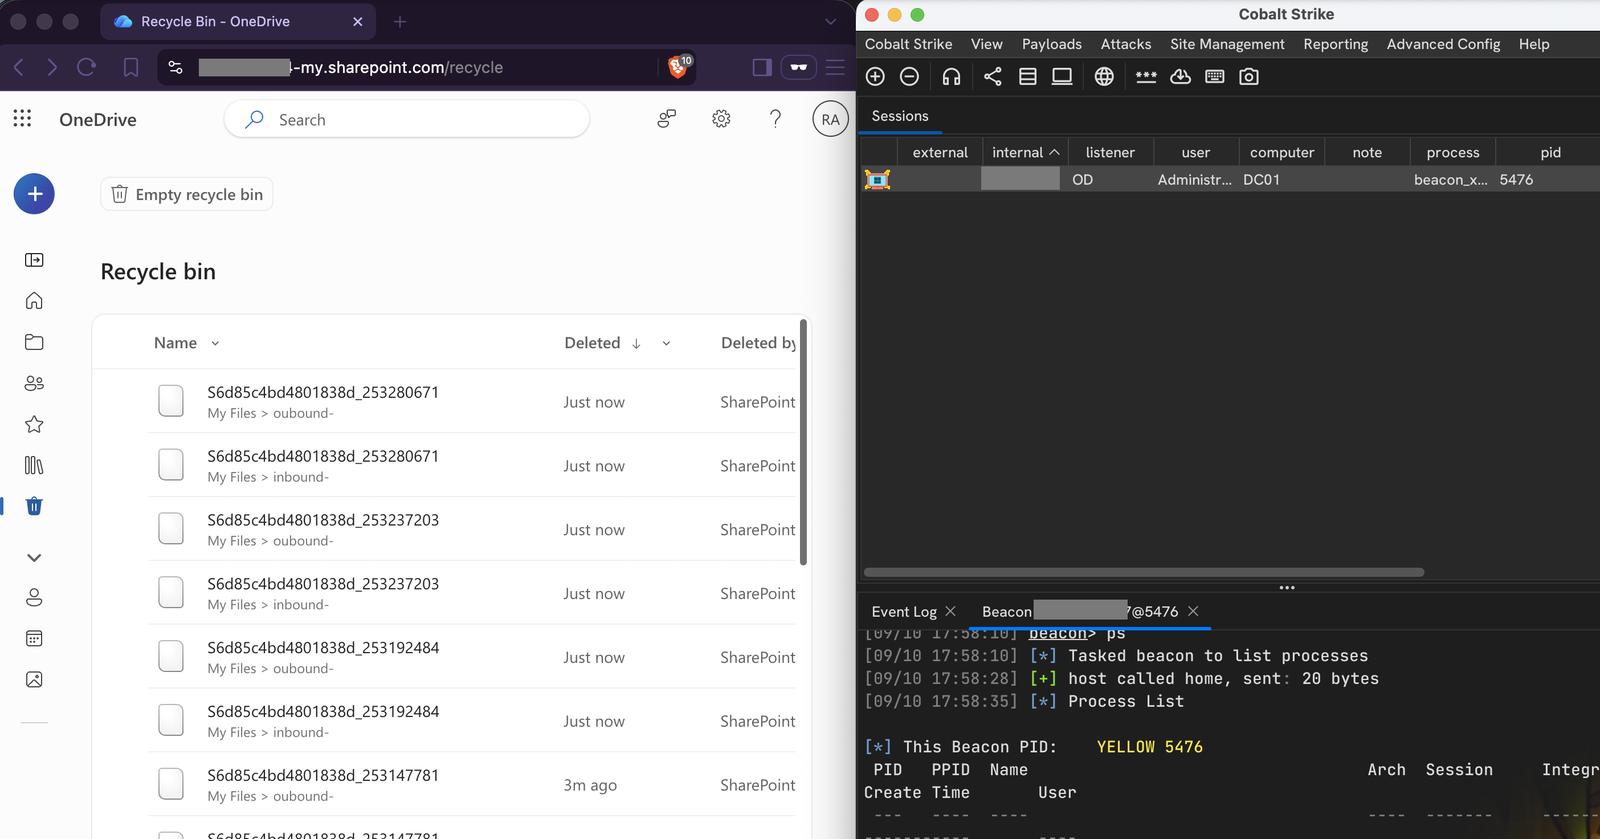 nmht3t/onedrive-udc2
OneDrive as a covert C2 transport for Cobalt Strike
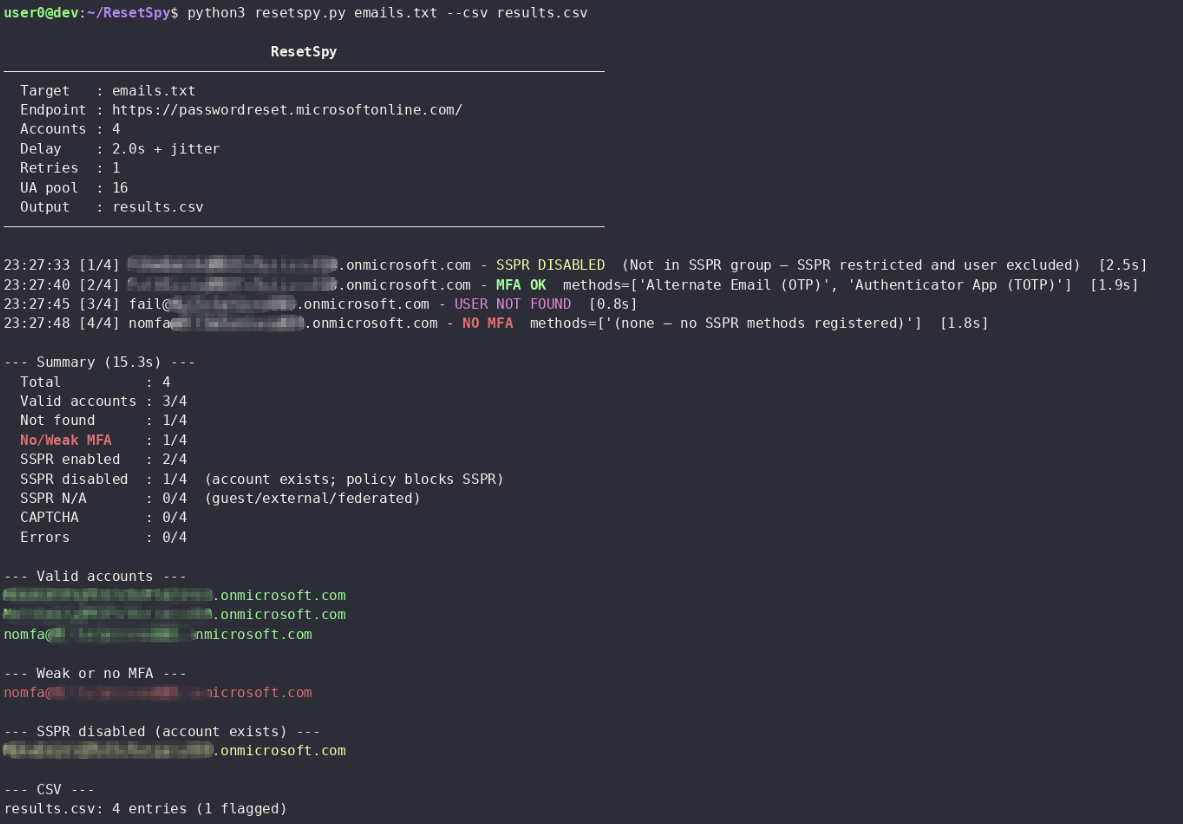 mlcsec/resetspy
Enumerate user accounts and registered authentication methods via the Microsoft Self-Service Password Reset (SSPR) portal
 basitsajidsoc/soc-investigation-cve-2024-49138
Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)
 johnearle/coalmine
Cloud Canary Object Orchestration Management Platform
 azqzazq1/sunnydaybpf
SunnyDayBPF: eBPF-based post-syscall user-buffer telemetry deception research by Azizcan Daştan
 michael-kanda/wp2shell-ioc-scanner
Detects shadow-administrator accounts in WordPress via configurable indicators and heuristics, then removes selected accounts through guarded, logged…