akca
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
api-security-testingdefensive-toolsdynamic-analysis-sandboxing+9
243
akha-security/akcaEvidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 mythicc2profiles/httpx
Configurable, Community driven, HTTP C2 Profile
 owasp/owasp-top-10-neocloud-and-ai-data-center-security-risks
OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…
 albinowax/activescanplusplus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
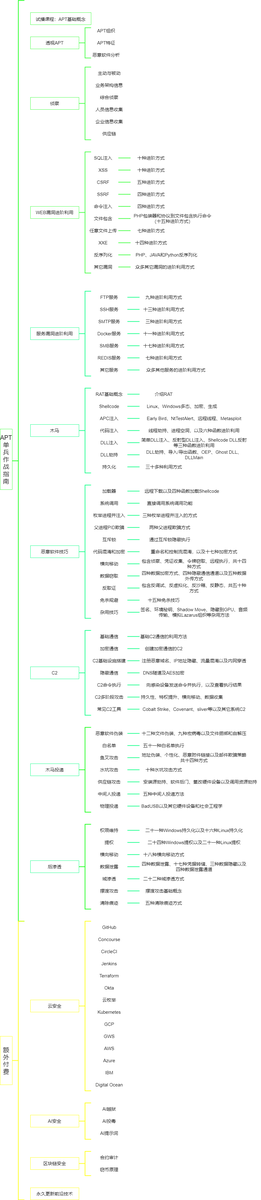 ghostwolflab/ai_security_top
A structured knowledge base covering AI security fundamentals, threat modeling, red team offensive techniques, and blue team defenses, including LLM…
 owasp/secure-headers-project
OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.
 a3sal0n/falcongate
A smart gateway to stop cyber criminals - Sponsored by Falcon Guard
 hashgraph-online/hol-guard
Open-source antivirus for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and skills at…
 asciimoo/morty
Privacy aware web content sanitizer proxy as a service
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 ivancabrera02/hashsiphon
Extracts the current user's NetNTLMv2 hash via HTTP authentication proxying, avoiding direct SSPI calls; v2 delegates auth to the BITS service to…
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 dylan-chainguard/cve-2026-22732-poc
Proof-of-concept demonstrating CVE-2026-22732, a Spring Security flaw where setIntHeader("Content-Length") drops all security headers, with…