
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
538 results
nCPU preview

nCPU

GitHubrobertcprice/ncpu

Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
ai-securitybinary-analysiscryptography+8
660
3 months ago
CustomProcessingUnit preview

CustomProcessingUnit

GitHubpietroborrello/customprocessingunit

The first analysis framework for CPU microcode
debuggersdynamic-code-analysisexploitation+5
4153 years ago
regenerator2000 preview

regenerator2000

GitHubricardoquesada/regenerator2000

An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…
binary-analysisdebuggerseducation+3
1641 month ago
CVE-2025-38352-PoC preview

CVE-2025-38352-PoC

GitHublongwasu/cve-2025-38352-poc

PoC and GDB script assists in triggering CVE-2025-38352

binary-exploitationdebuggerseducation+5
28 days ago
ll-34 preview

ll-34

GitHubdbrll/ll-34

Circuit-level PDP-11/34 emulator

curated-resourcesdebuggerseducation+4
706 days ago
unicorn preview

unicorn

GitHubunicorn-engine/unicorn

Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
ai-assisted-reversingbinary-analysisbinary-exploitation+7
9.4k7 months ago
mora-hwbp preview

mora-hwbp

GitHubdovughs/mora-hwbp

Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).

adversarial-attackdebuggersdefensive-tools+3
1817 days ago
MAccConc preview

MAccConc

GitHubgoogleprojectzero/maccconc

Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…
binary-analysisdebuggersdynamic-analysis-sandboxing+6
501 month ago
strace preview

strace

GitHubstrace/strace

Linux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
debuggersdynamic-analysis-sandboxinggeneral-purpose-utilities
2.7k5 days ago
xnu preview

xnu

GitHubapple-oss-distributions/xnu

Hybrid kernel combining Mach, FreeBSD, and IOKit for macOS and iOS. Provides core OS services, driver framework, and security policy enforcement on…
debuggersembedded-systems-securityfirmware-analysis+2
3.7k1 year ago
xed preview

xed

GitHubintelxed/xed

Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
binary-analysiscode-analysisdebuggers+3
1.6k1 month ago
TangledWinExec preview

TangledWinExec

GitHubdaem0nc0re/tangledwinexec

PoCs and tools for investigation of Windows process execution techniques
adversarial-attackdebuggersids-ips-evasion+6
9588 months ago
idacode preview

idacode

GitHubioncodes/idacode

An integration for IDA and VS Code which connects both to easily execute and debug IDAPython scripts.
binary-analysisdebuggersreverse-engineering+1
9931 year ago
VMDragonSlayer preview

VMDragonSlayer

GitHubpoppopjmp/vmdragonslayer

Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
binary-analysisdebuggersdynamic-analysis-sandboxing+8
4431 year ago
drltrace preview

drltrace

GitHubmxmssh/drltrace

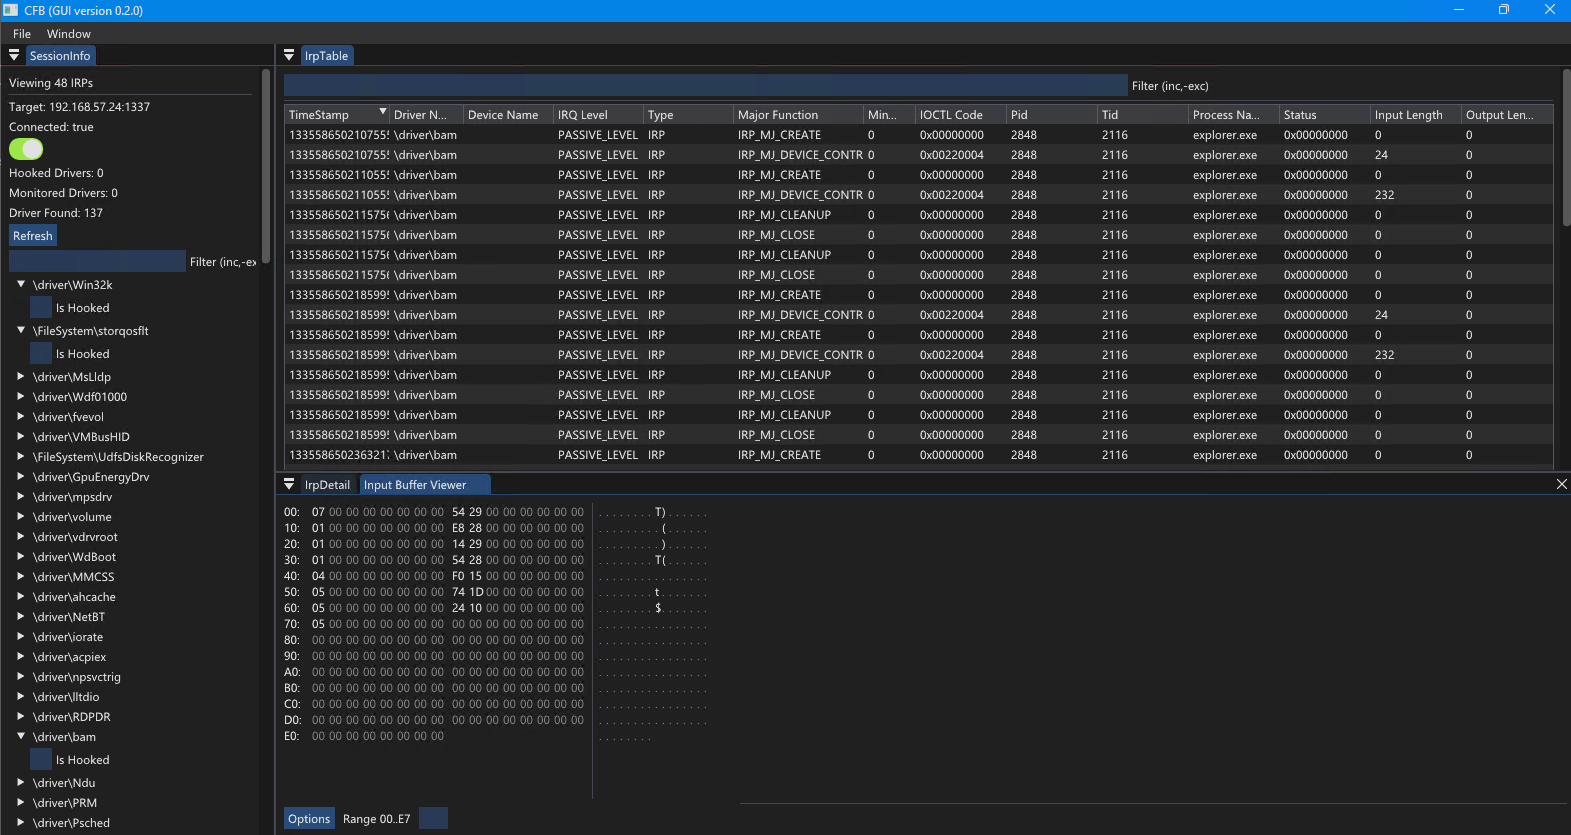
Drltrace is a library calls tracer for Windows and Linux applications.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
4196 years ago
CFB preview

CFB

GitHubhugsy/cfb

ProcMon-style IRP monitor for Windows drivers. Captures and logs I/O Request Packets via a kernel driver and user-land broker, outputting JSON for…

debuggersfuzzingvulnerability-analysis
3392 years ago
scare preview

scare

GitHubnetspooky/scare

A multi-arch assembly REPL and emulator for your command line.
binary-analysisdebuggersdynamic-analysis-sandboxing+4
3121 year ago
oregami preview

oregami

GitHubshemesh999/oregami

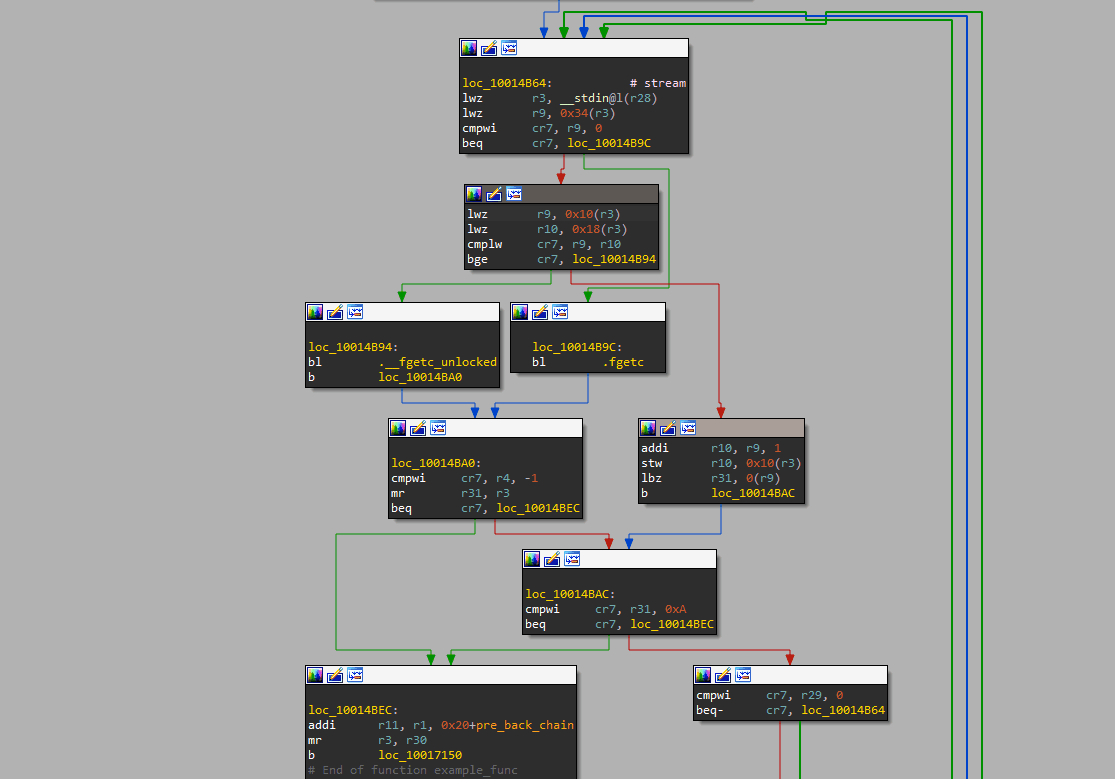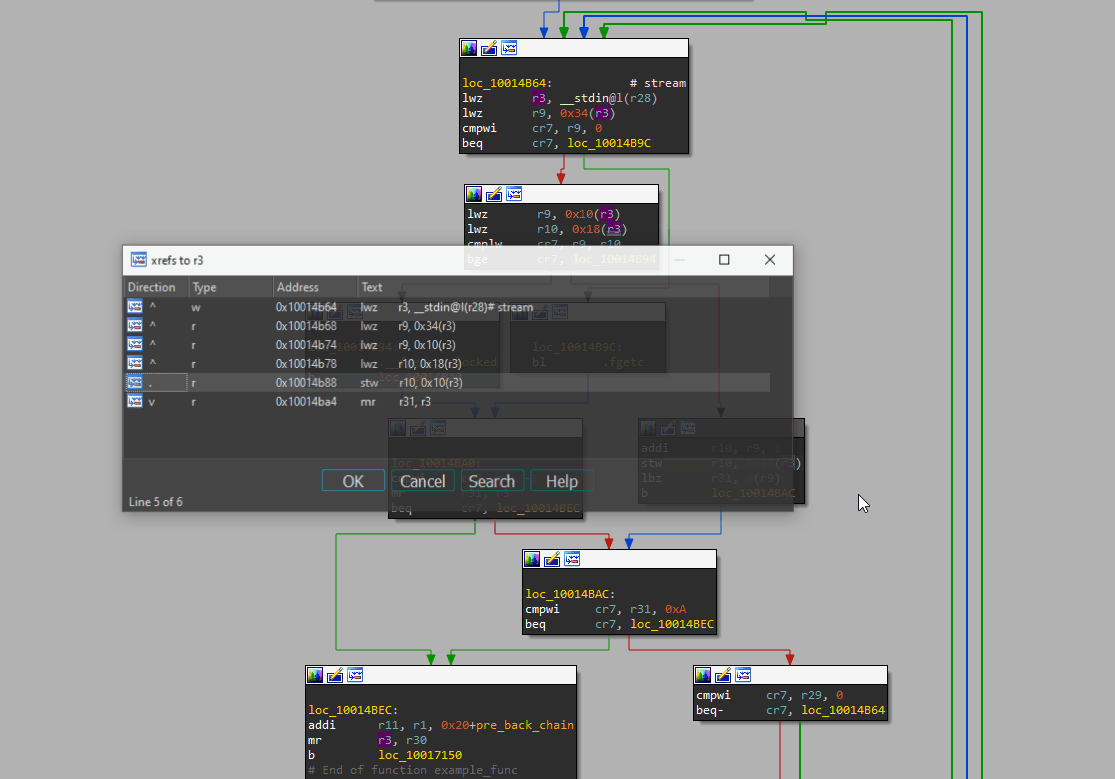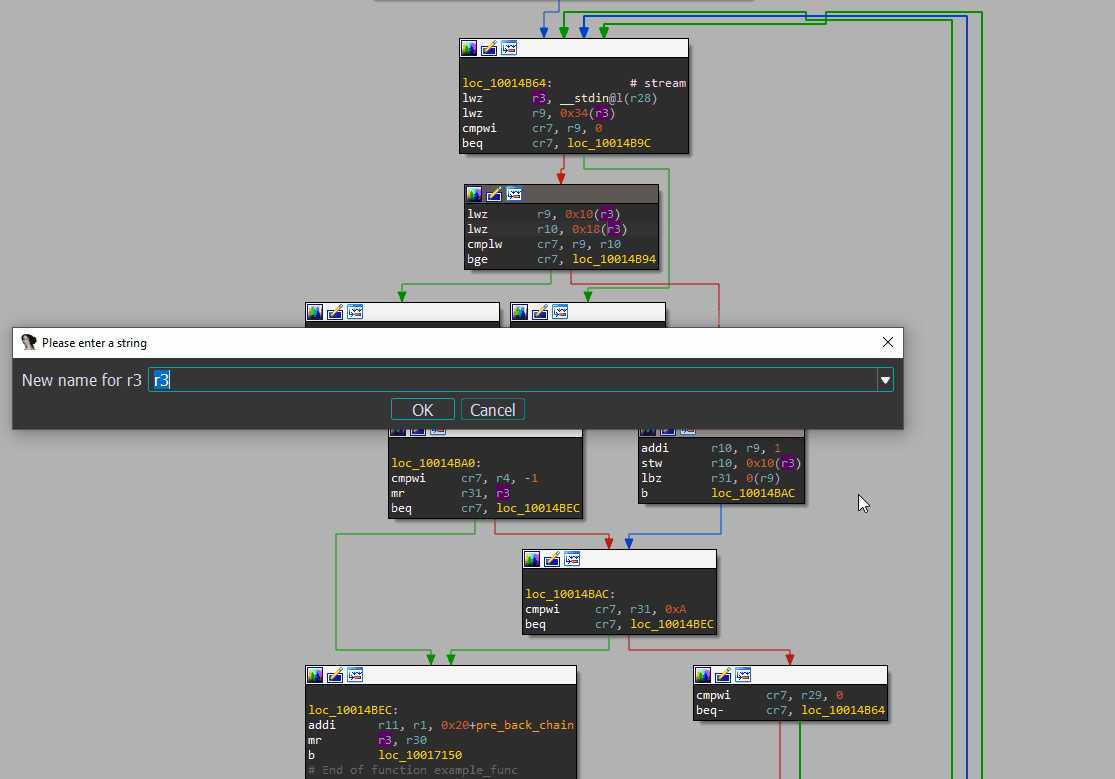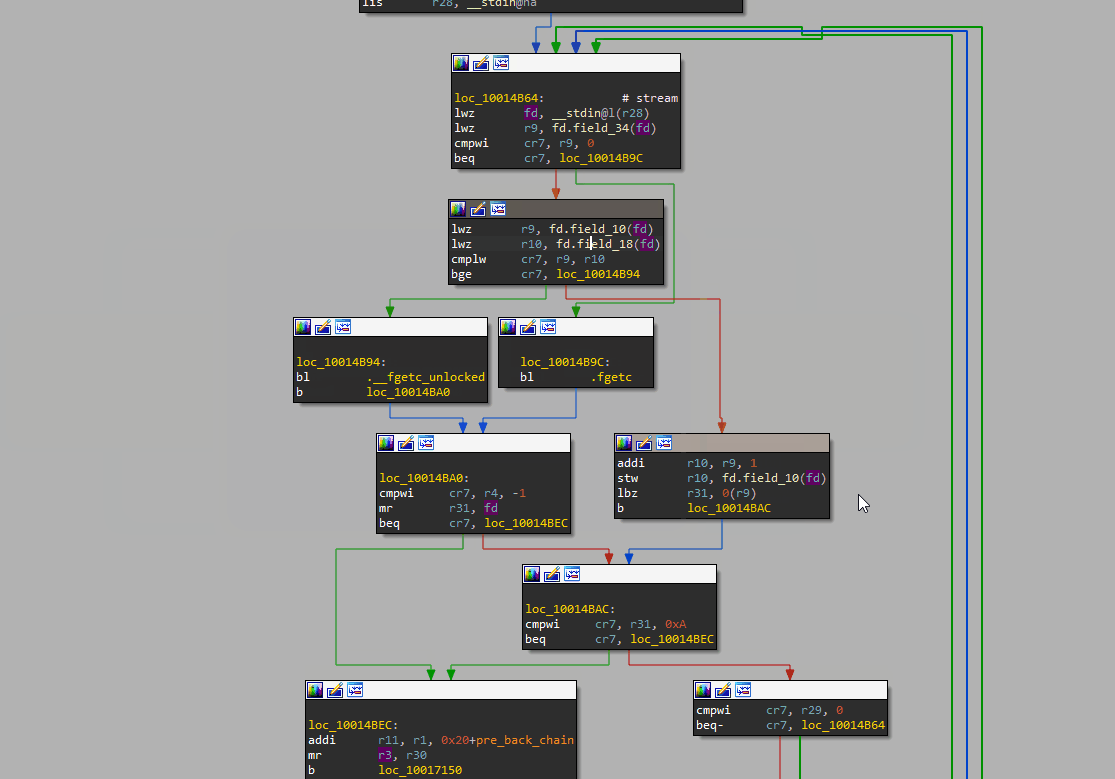
IDA plugins and scripts for analyzing register usage frame

binary-analysisdebuggersreverse-engineering+1
1837 months ago
Previous12…30Next