
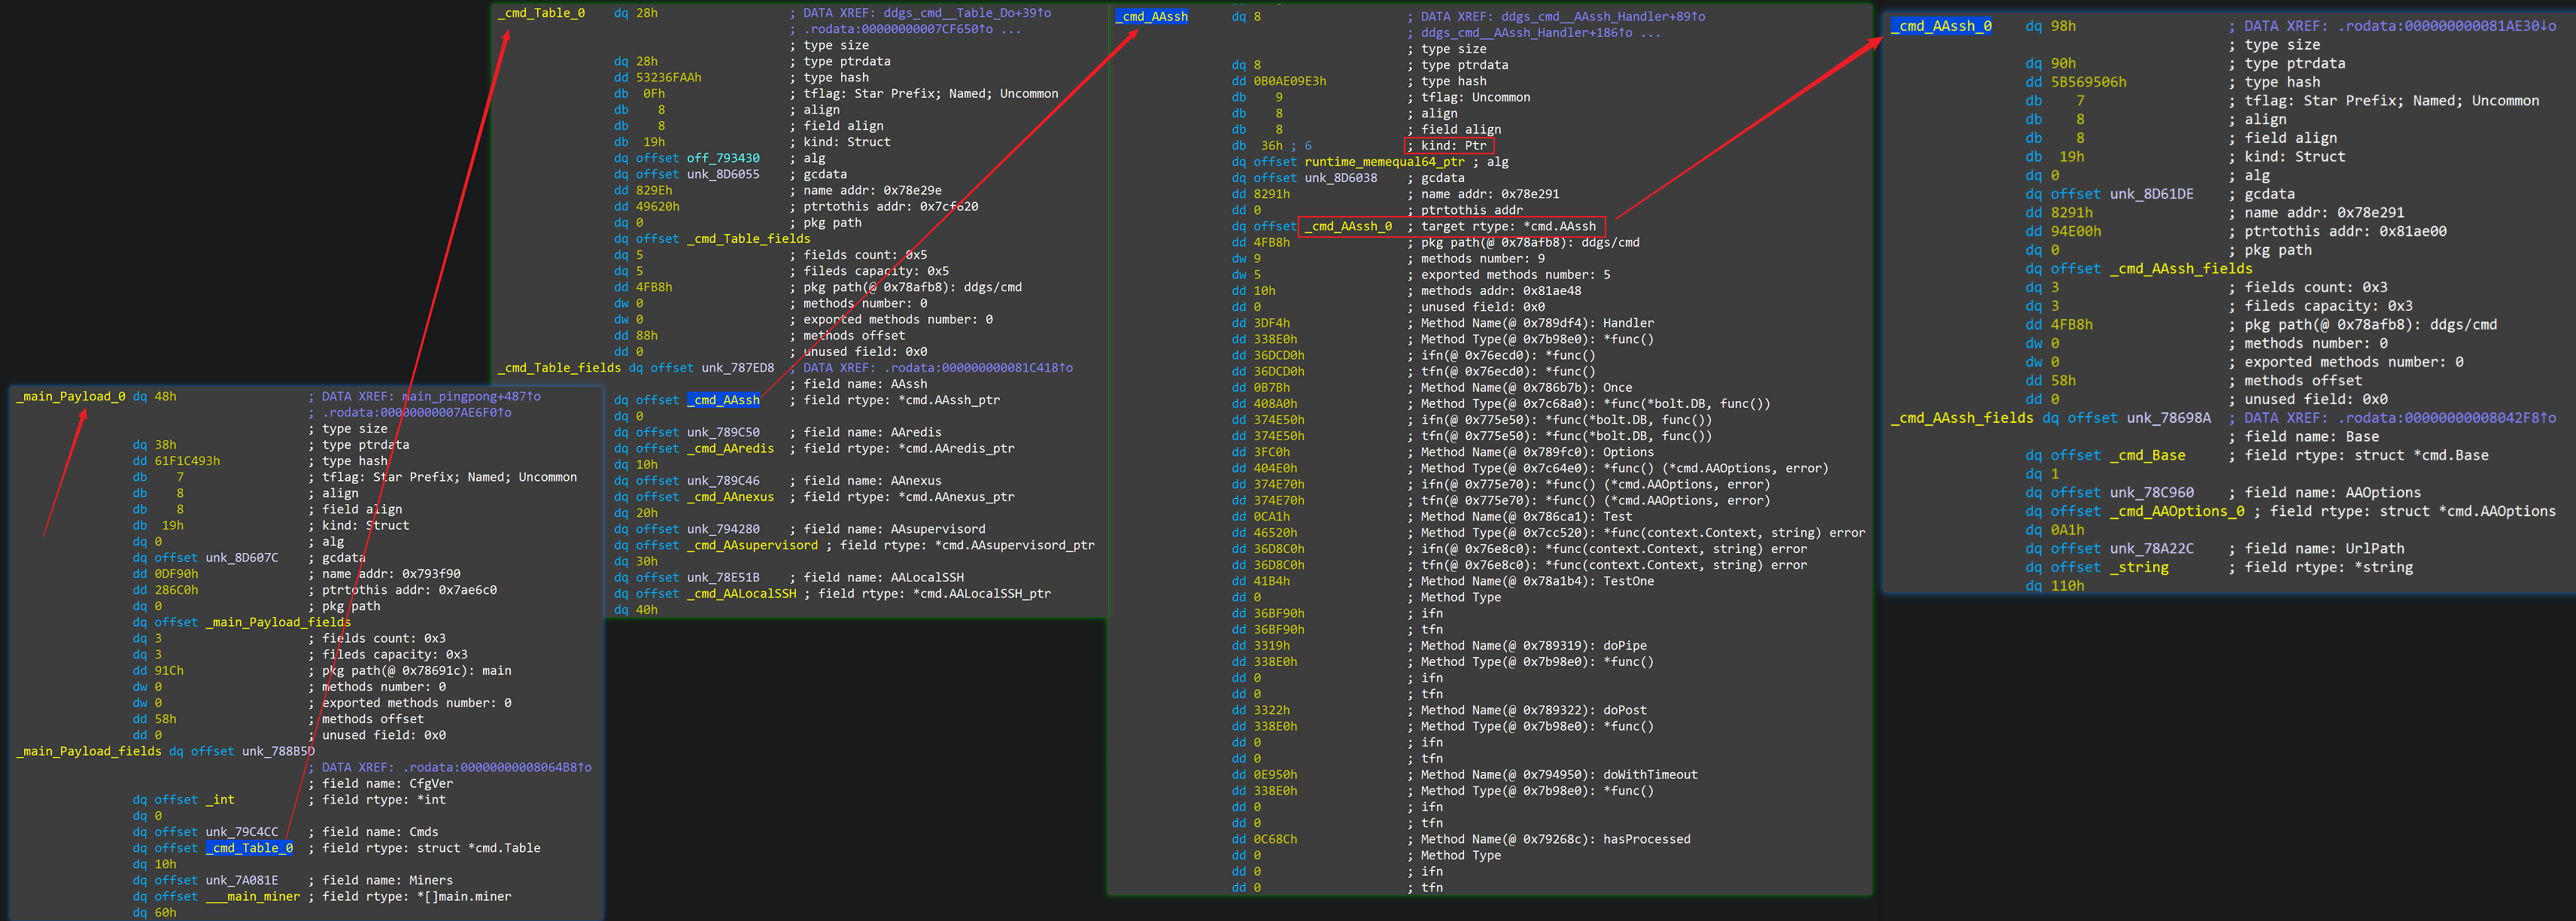
go_parser
 0xjiayu/go_parser
Yet Another Golang binary parser for IDAPro
binary-analysisdebuggersmalware-analysis+1
0xjiayu/go_parserYet Another Golang binary parser for IDAPro
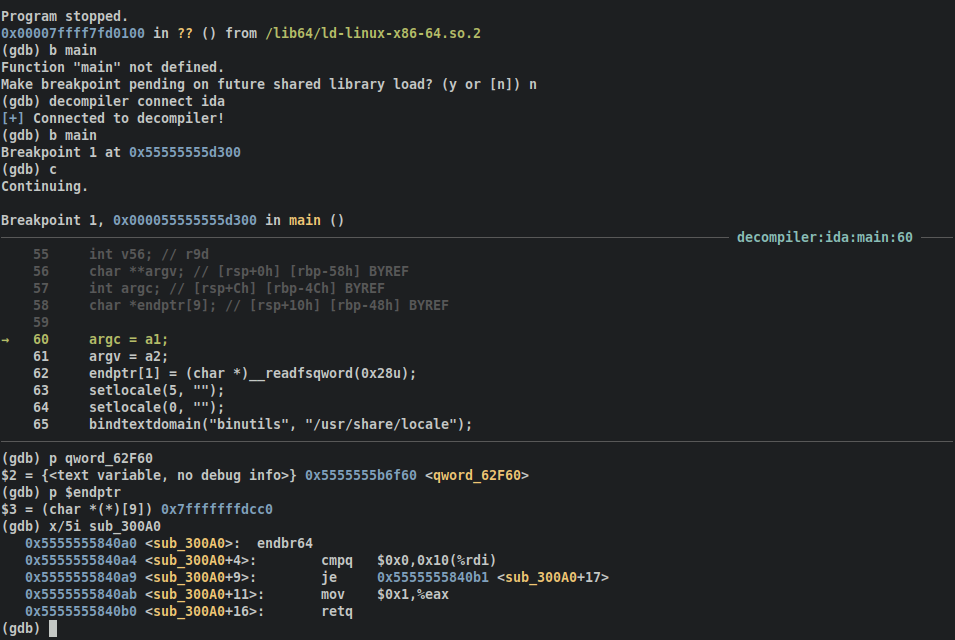 mahaloz/decomp2dbg
A plugin to introduce interactive symbols into your debugger from your decompiler
 sneakynachos/cve-2026-85048-the-gpu-died
Reproducer and technical analysis for CVE-2026-85048, a Chrome viz surface use-after-free in the GPU process, with ASAN unit tests and browser…
 kevoreilly/capev2
Malware Configuration And Payload Extraction
 mandiant/flare-learning-hub
Free educational content on reverse engineering and malware analysis from the FLARE team
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 checkpointsw/showstopper
ShowStopper is a tool for helping malware researchers explore and test anti-debug techniques or verify debugger plugins or other solutions that clash…
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 0xz0f/z0fcourse_reverseengineering
Structured reverse engineering course covering x64 Windows binaries, assembly, debugging, and malware analysis. Designed for beginners to…
 dump-guy/malware-analysis-and-reverse-engineering
Some of my publicly available Malware analysis and Reverse engineering.
 ctxis/cape
Malware Configuration And Payload Extraction
 oalabs/blobrunner
Quickly debug shellcode extracted during malware analysis
 darkcodersc/psylodbg
User-friendly Microsoft Windows Debugger for Malware Analysts.
 enkomio/thematrix
a PE Loader and Windows API tracer. Useful in malware analysis.
 malienist/lupo
WinDbg plugin for automated malware dynamic analysis and IOC extraction. Executes within the debugger to collect predefined indicators and writes…
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…