Yet Another Golang binary parser for IDAPro
English | 中文
NOTE:
Now the latest master branch is the Python3 version. The old master branch has been changed to branch py2, and temporarily not maintained.
Instructions for Python3 branch
This version is developed and tested on macOS/Windows, IDA7.4+ and Python3.8.x,
If there are problems on other platforms and version, you are welcomed to submit issue or Pull Requsts.
In addition, it should be noted that IDA7.4 on macOS uses Python3 installed by default, which may cause the third-party library installed by yourself to fail to load. You need to switch to Python installed by brew. Please refer to this script for specific switching methods.
Inspired by golang_loader_assist and jeb-golang-analyzer, I wrote a more complete Go binaries parsing tool for IDAPro.
Main Features:
- Locate and parse firstmoduledata structure in Go binary file, and make comment for each field;
- Locate pclntab(PC Line Table) according to the firstmoduledata and parse it. Then find and parse and recover function names and source file paths in the pclntab. Source file paths will be printed in the output window of IDAPro;
- Parse strings and string pointers, make comment for each string, and make dref for each string pointer;
- According to firstmoduledata, find each type and parse it, meke comment for each attribute of type, which will be very convenient for malware researcher to analyze a complex type or data structure definition;
- Parse itab(Interface Table).
Helpful information to RE work for Go binaries:
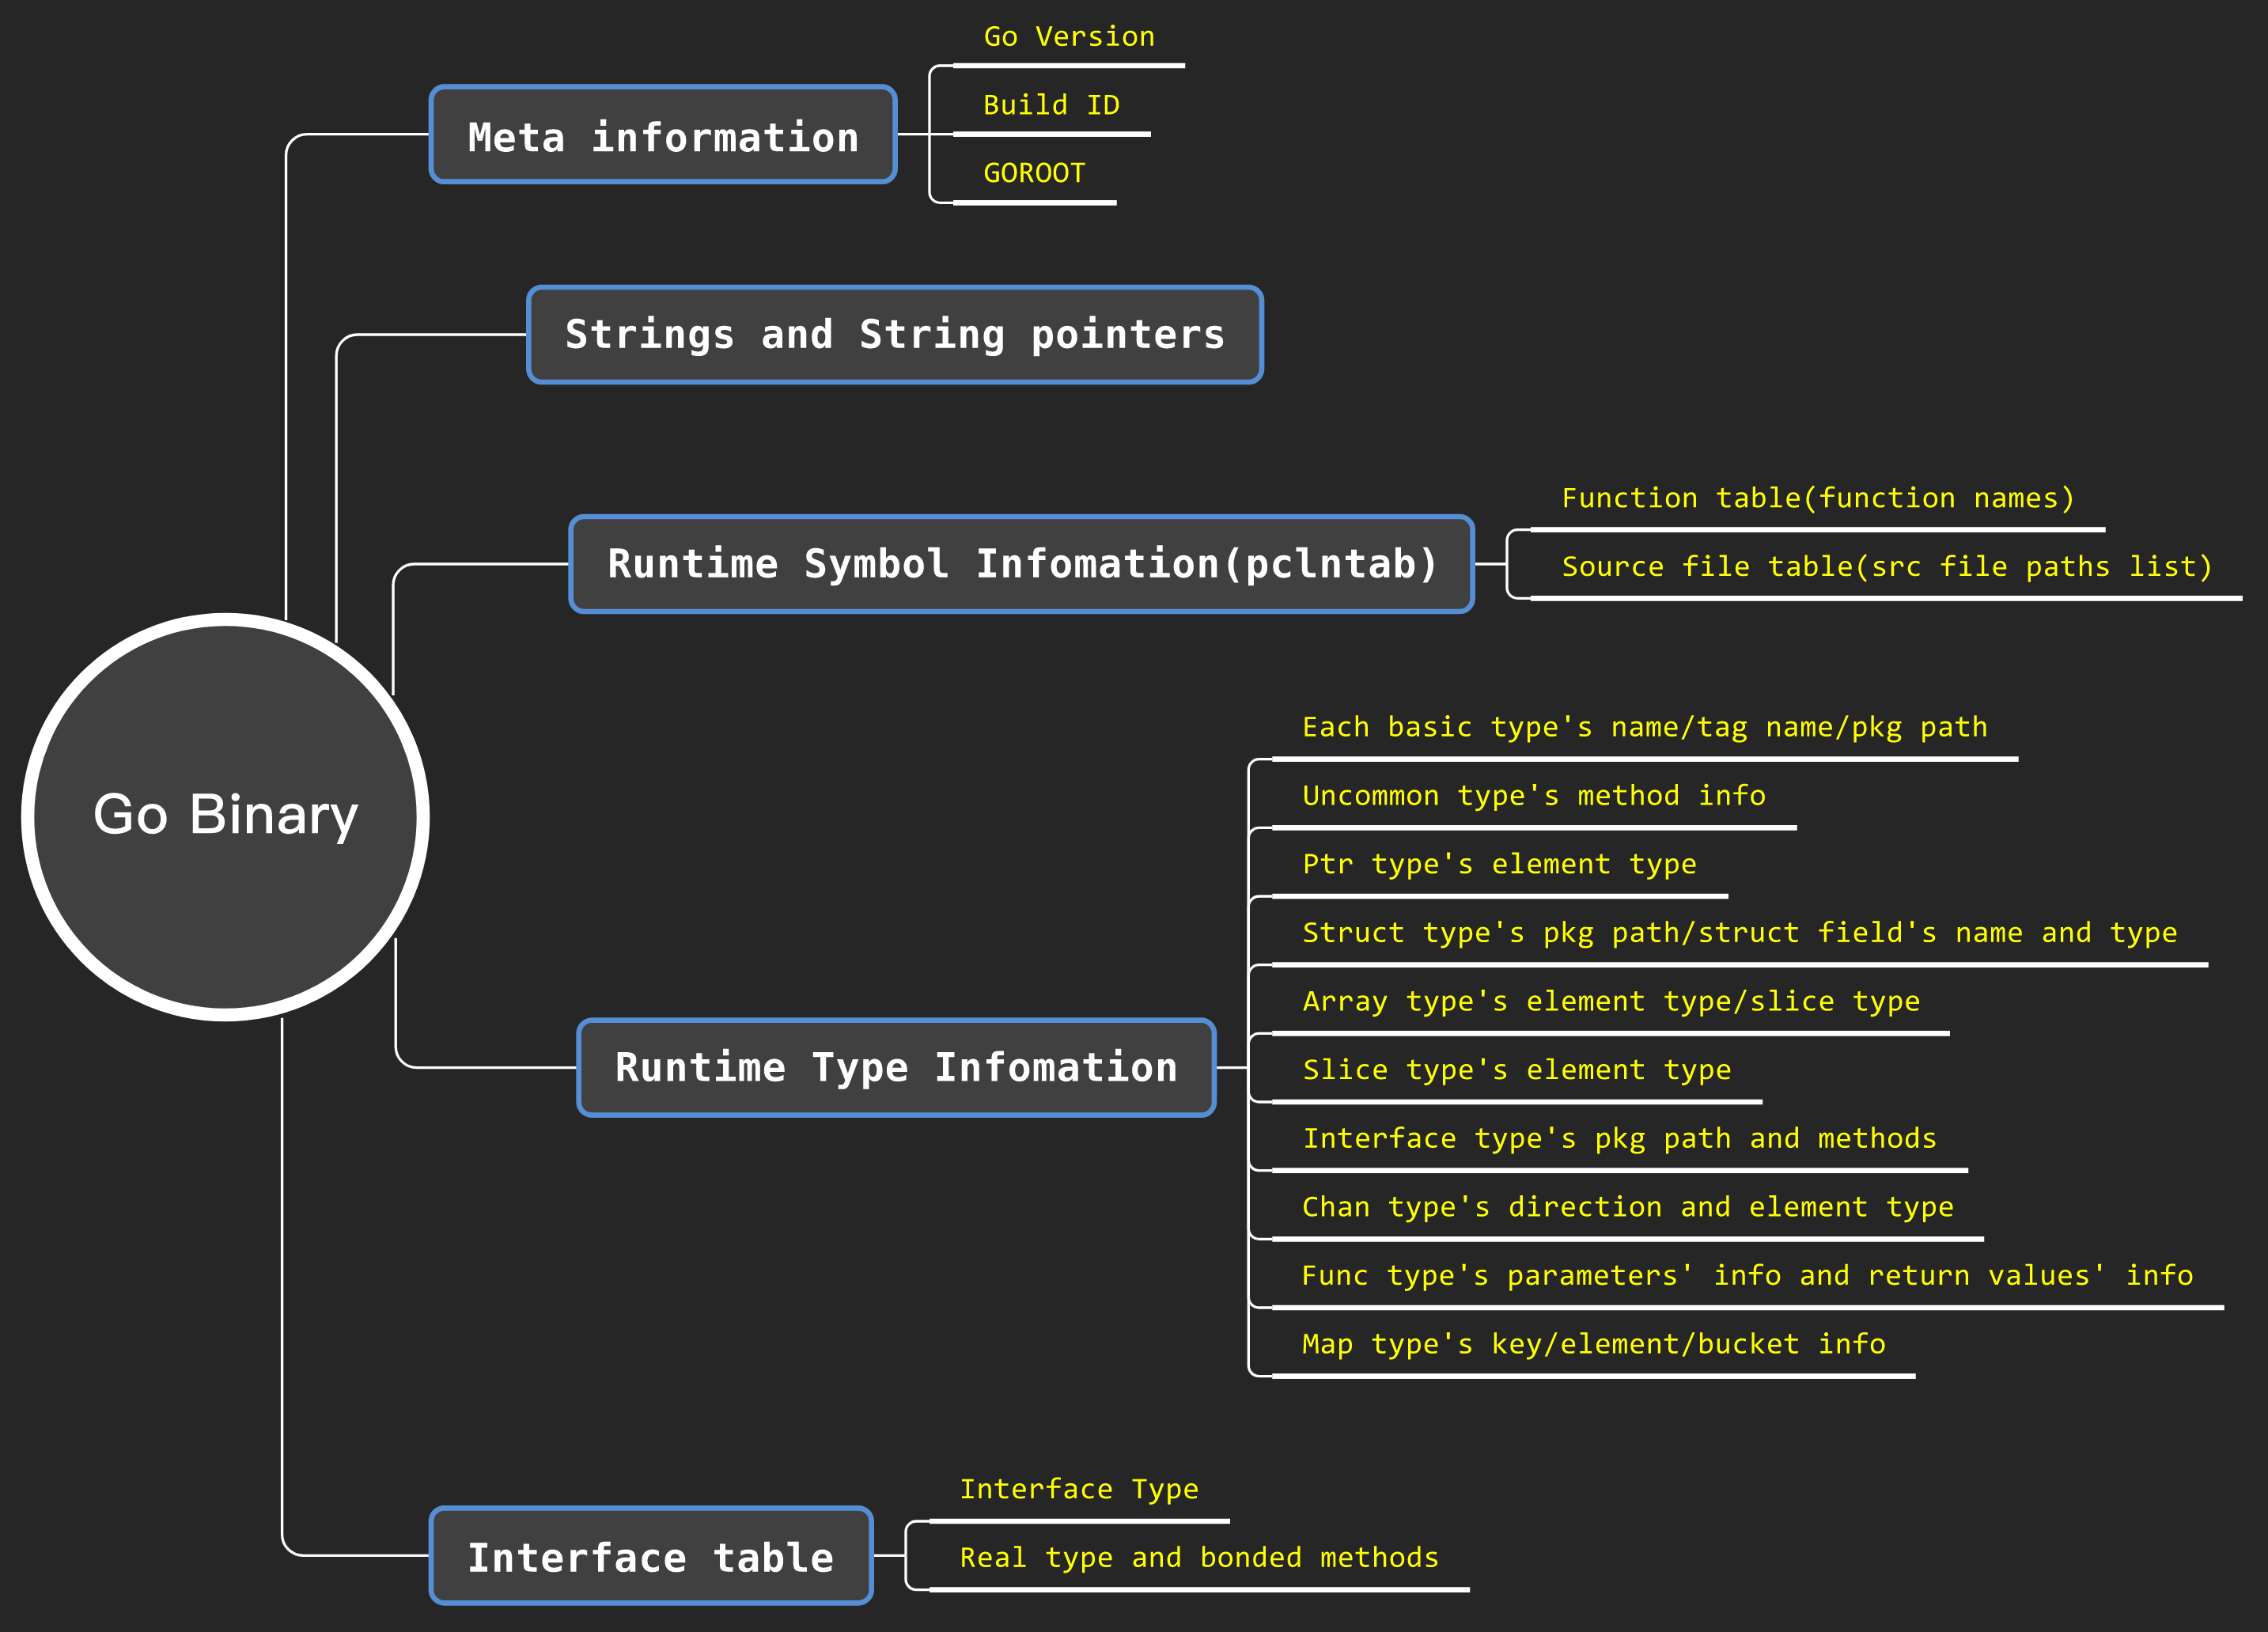
And there are two useful feature in go_parser:
- It also work fine for binaries with malformed File Header information, especially malformed Section Headers information;
- All those features above are valid for binaries built with buildmode=pie.
A config data structure in DDGMiner v5029 (MD5: 95199e8f1ab987cd8179a60834644663) parsing result as below:
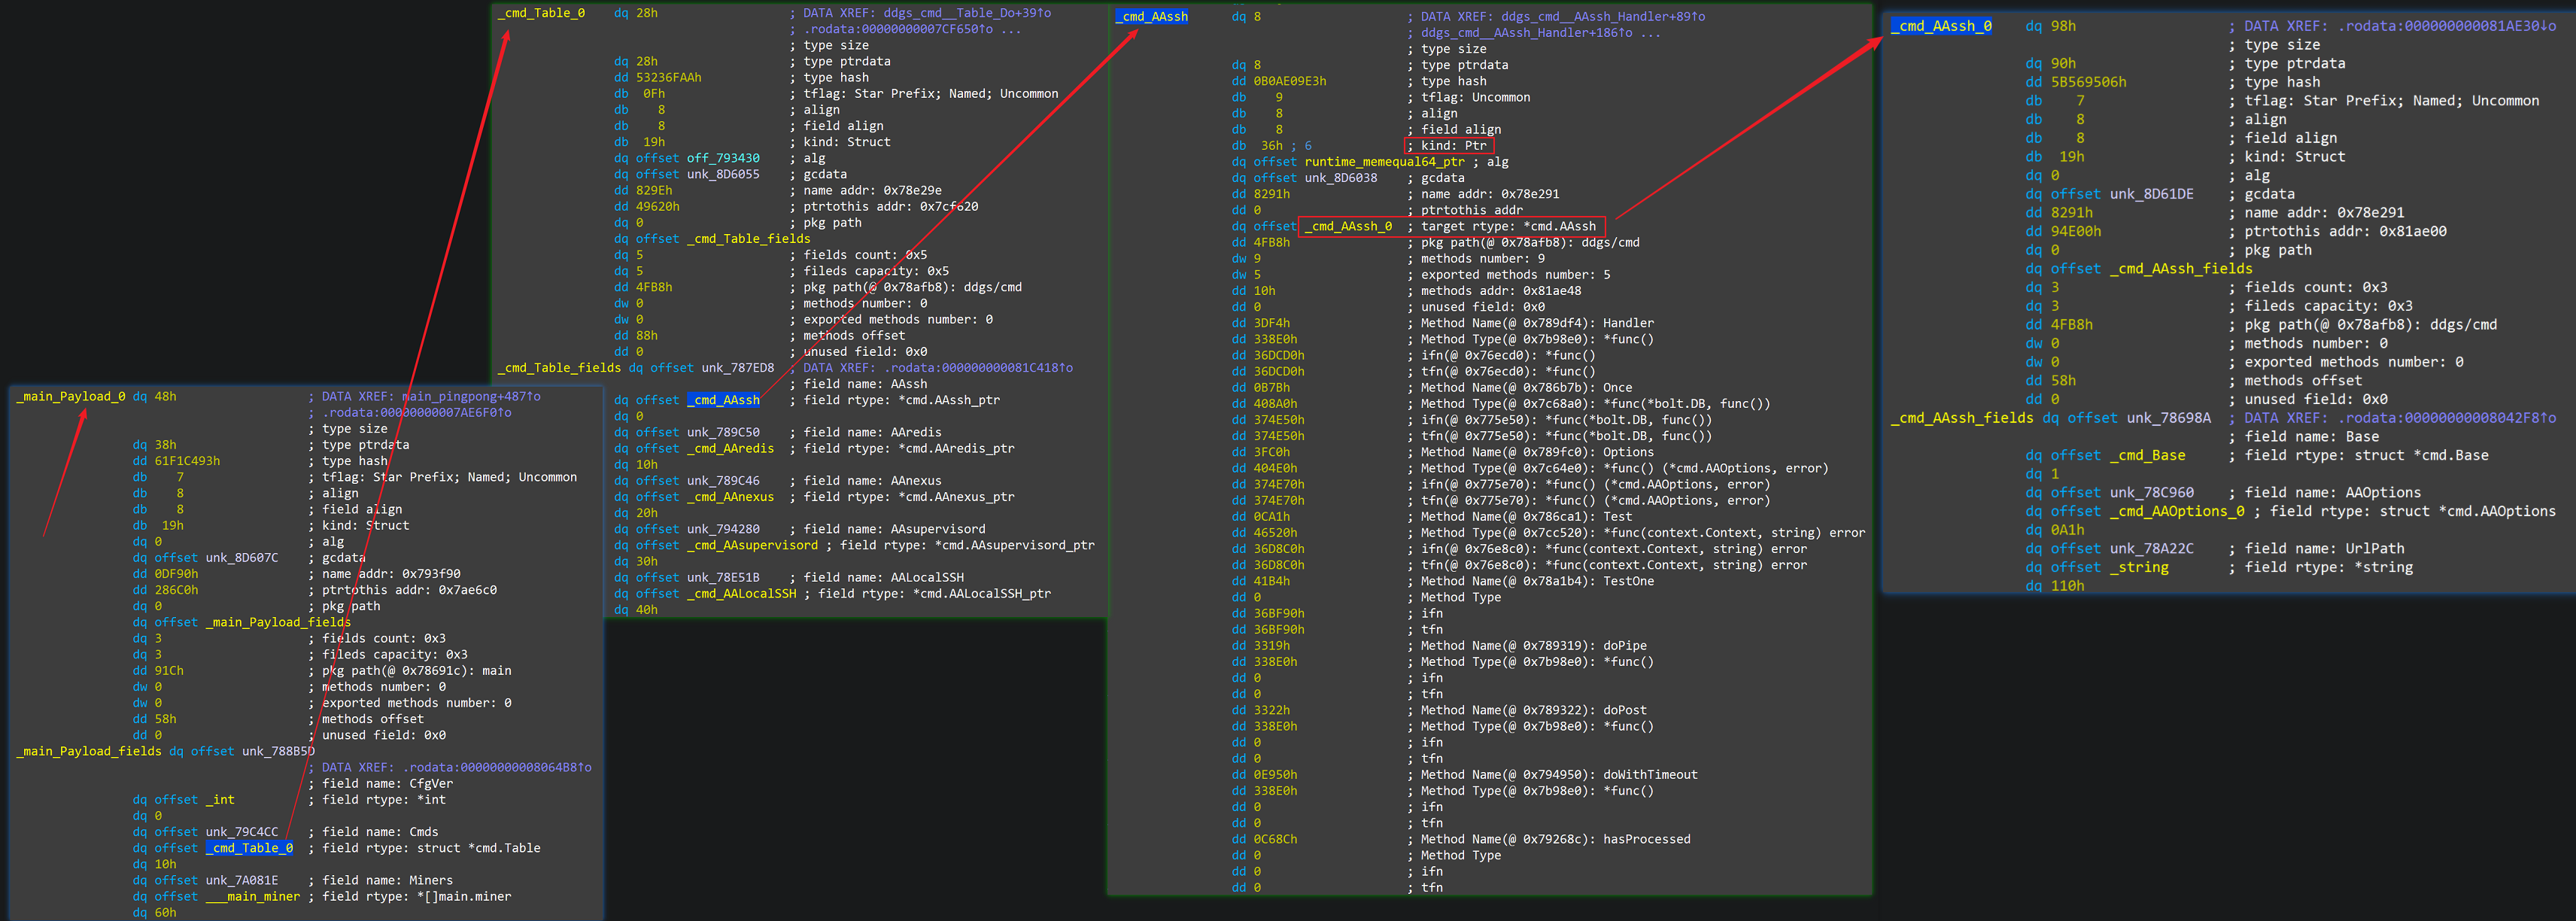
And the user-defined source file paths list:

Project files:
- go_parser.py :Entry file, press [Alt+F7] , select and execute this file;
- common.py: Common variables and functions definition;
- pclntbl.py: Parse pclntab(PC Line Table);
- strings.py: Parse strings 和 string pointers;
- moduldata.py: Parse firstmoduledata;
- types_builder.py: Parse types ;
- itab.py: Parse itab(Interface Table);
Additionally, the str_ptr.py will parse string pointers by specify the start address and end address of string pointers manually.
Note
- This tool is written in Python3, and tested on IDA7.4+;
- The strings parsing module was migrated from golang_loader_assist, and I added the feature of string pointers parsing. It only supports x86(32bit & 64bit) architecture for now.
Refer
- Analyzing Golang Executables
- Reversing GO binaries like a pro
- Reconstructing Program Semantics from Go binaries.pdf
- Go二进制文件逆向分析从基础到进阶——综述
- Go二进制文件逆向分析从基础到进阶——MetaInfo、函数符号和源码文件路径列表
- Go二进制文件逆向分析从基础到进阶——数据类型
- Go二进制文件逆向分析从基础到进阶——itab与strings
- Go二进制文件逆向分析从基础到进阶——Tips与实战案例

 0xjiayu/go_parser







