
Bus_Pirate
 elderlypirate/bus_pirate
Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…
debuggersembedded-systems-securityfirmware-analysis+5
693
elderlypirate/bus_pirateMulti-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…
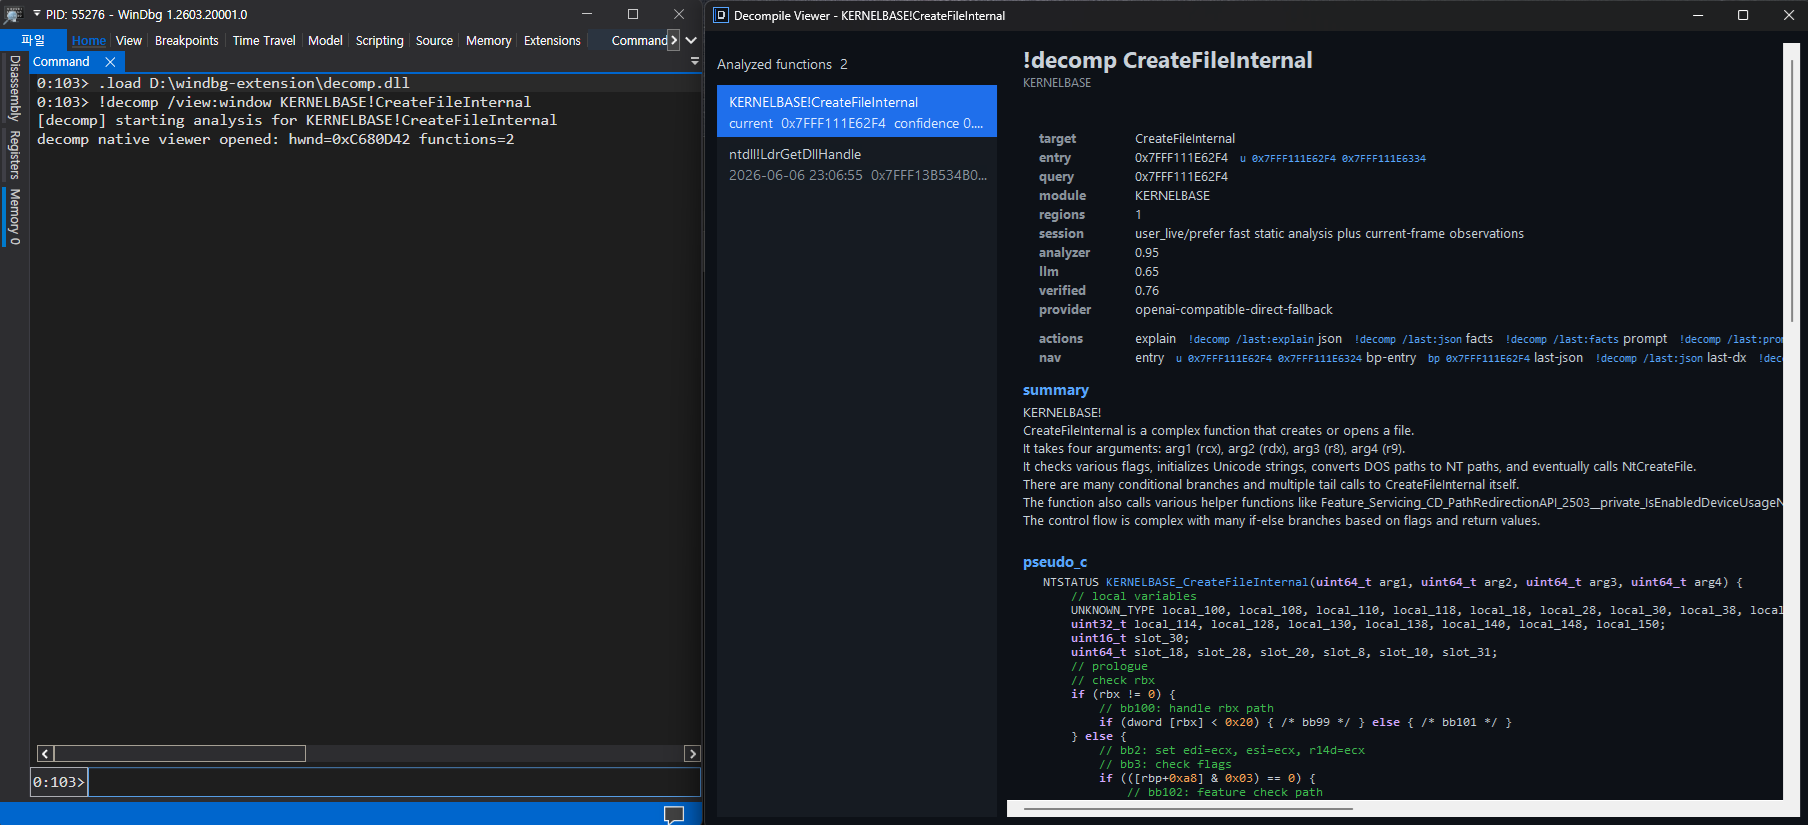 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
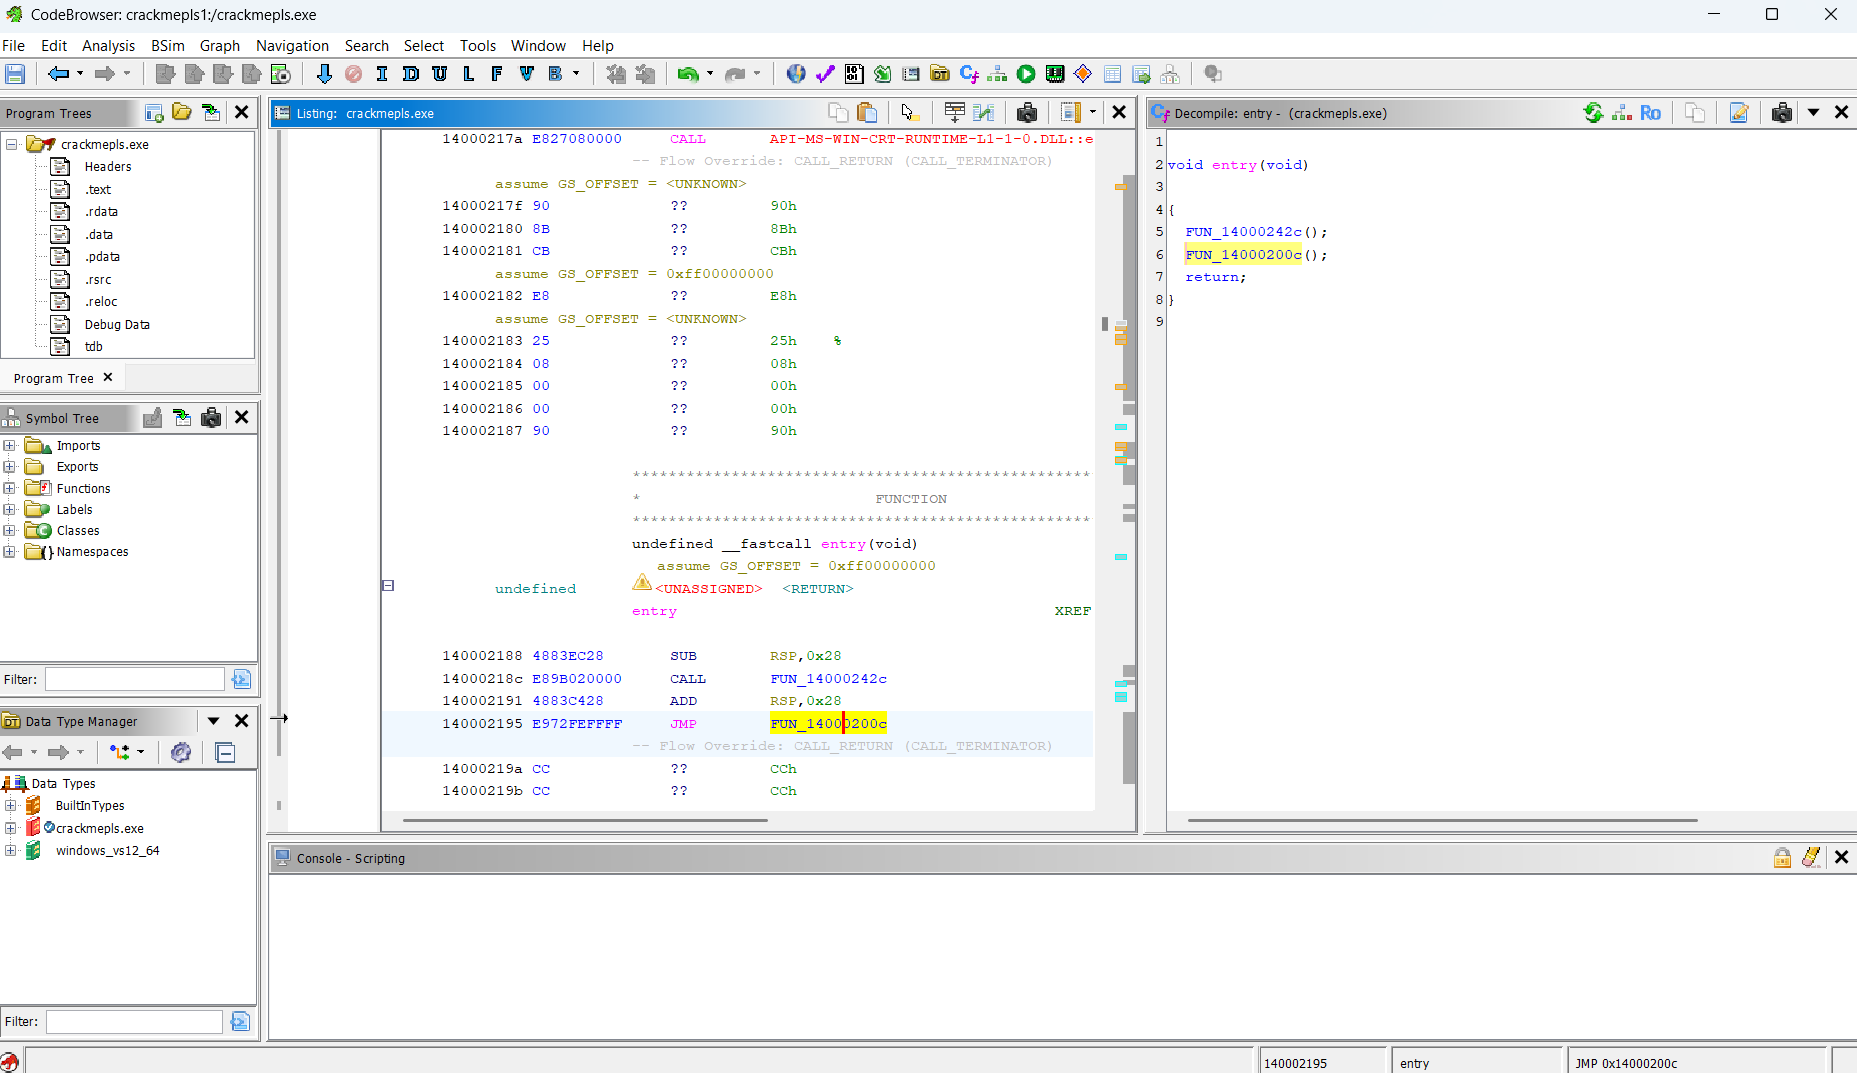 markoglasgow/gemma_crackme_tutorial
Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…
 yasharote/dll-injector
A desktop tool that allows injecting DLLs, hooking WinAPI functions like CreateFileW, and modifying process behavior at runtime — designed for…
 pravin761/cve-2026-54107
Root-cause analysis of CVE-2026-54107: a use-after-free in Windows win32kfull.sys with race condition debugging, static analysis, MSRC triage…
 day6reak/cve-2014-1773
Technical analysis of CVE-2014-1773, a heap corruption vulnerability in Internet Explorer's MSHTML engine, with detailed crash callstack,…
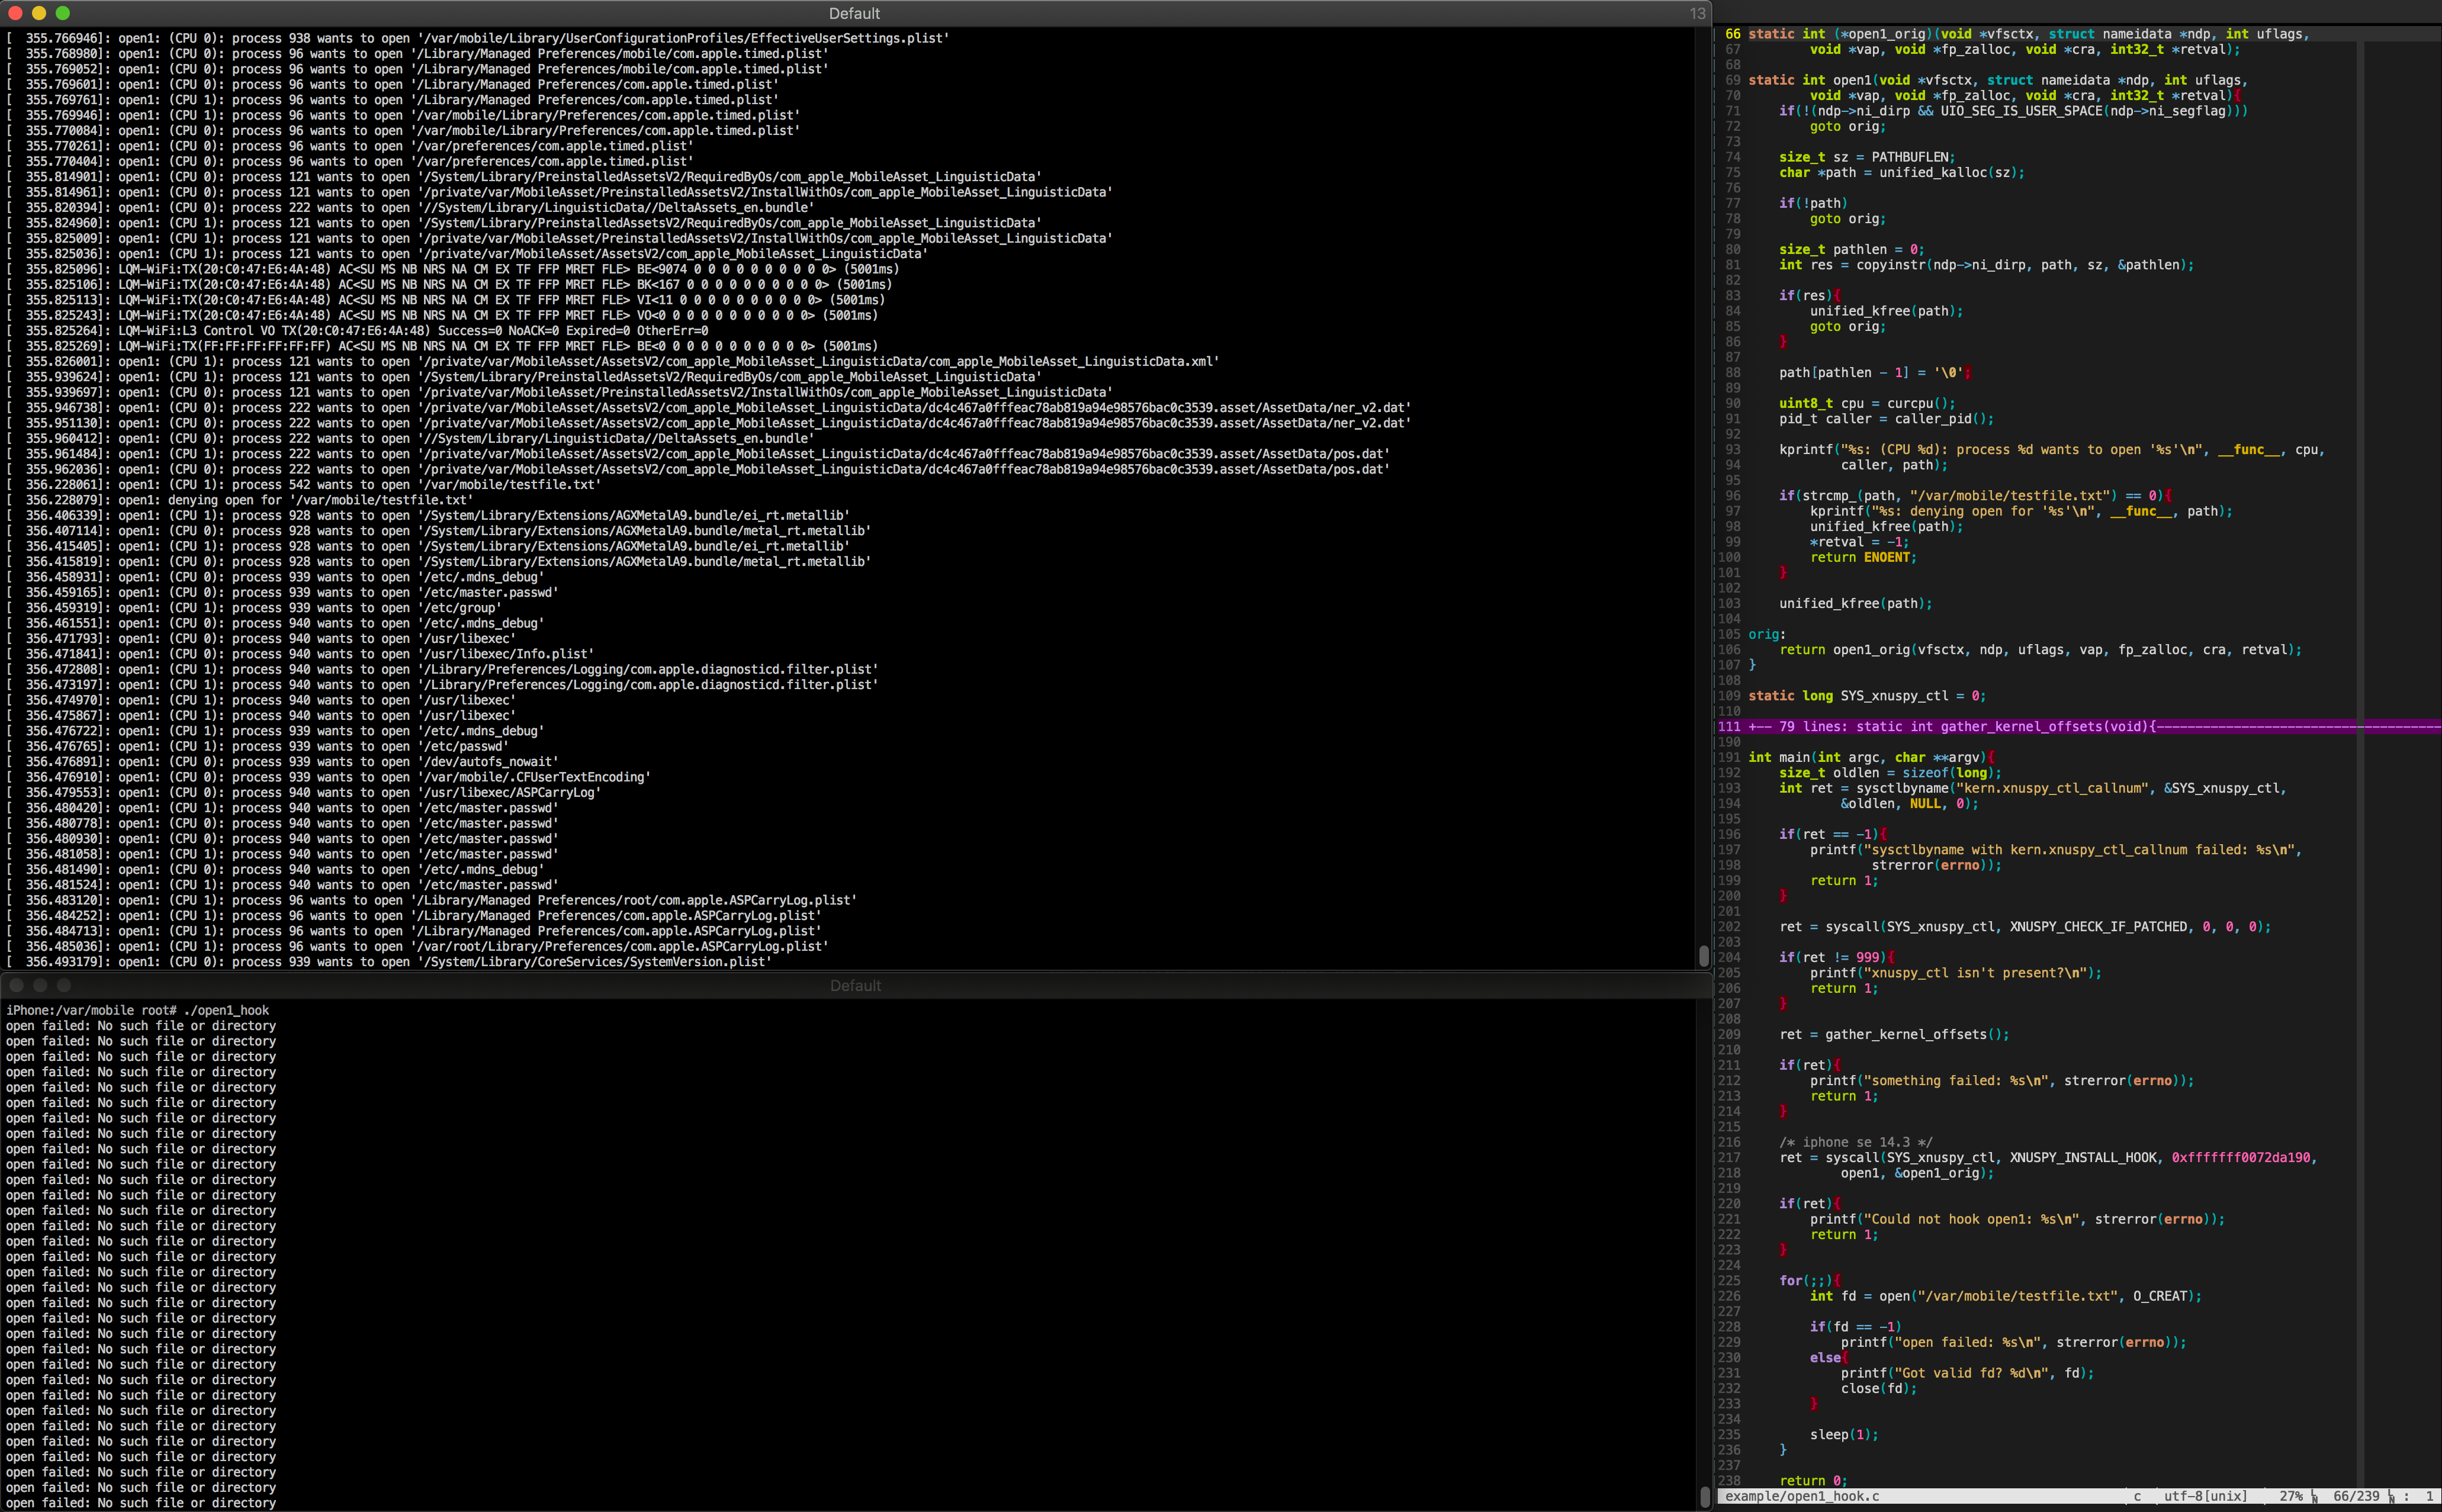 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
 mfthomps/resim
Reverse engineering software using a full system simulator
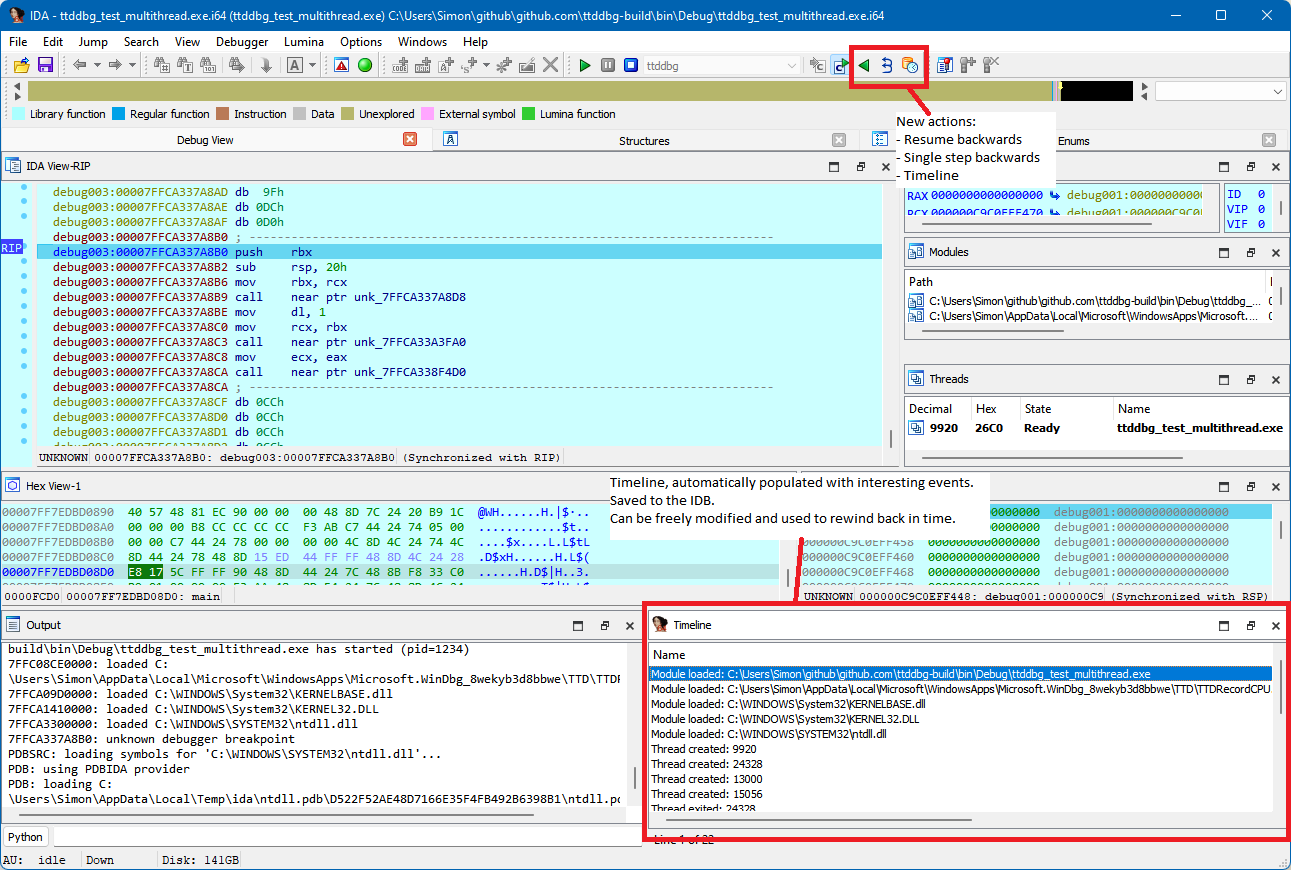 airbus-cert/ttddbg
Time Travel Debugging IDA plugin
 tufanturhan/cve-2022-21971-windows-runtime-rce
Proof-of-concept exploit for CVE-2022-21971, an uninitialized pointer free vulnerability in Windows Runtime's prauthproviders.dll, triggered via…
 vrikodar/cve-2003-0264_exploit
Buffer Overflow in Seattle Lab Mail (SLmail) 5.5 - POP3
 0vercl0k/cve-2022-21971
PoC for CVE-2022-21971 "Windows Runtime Remote Code Execution Vulnerability"
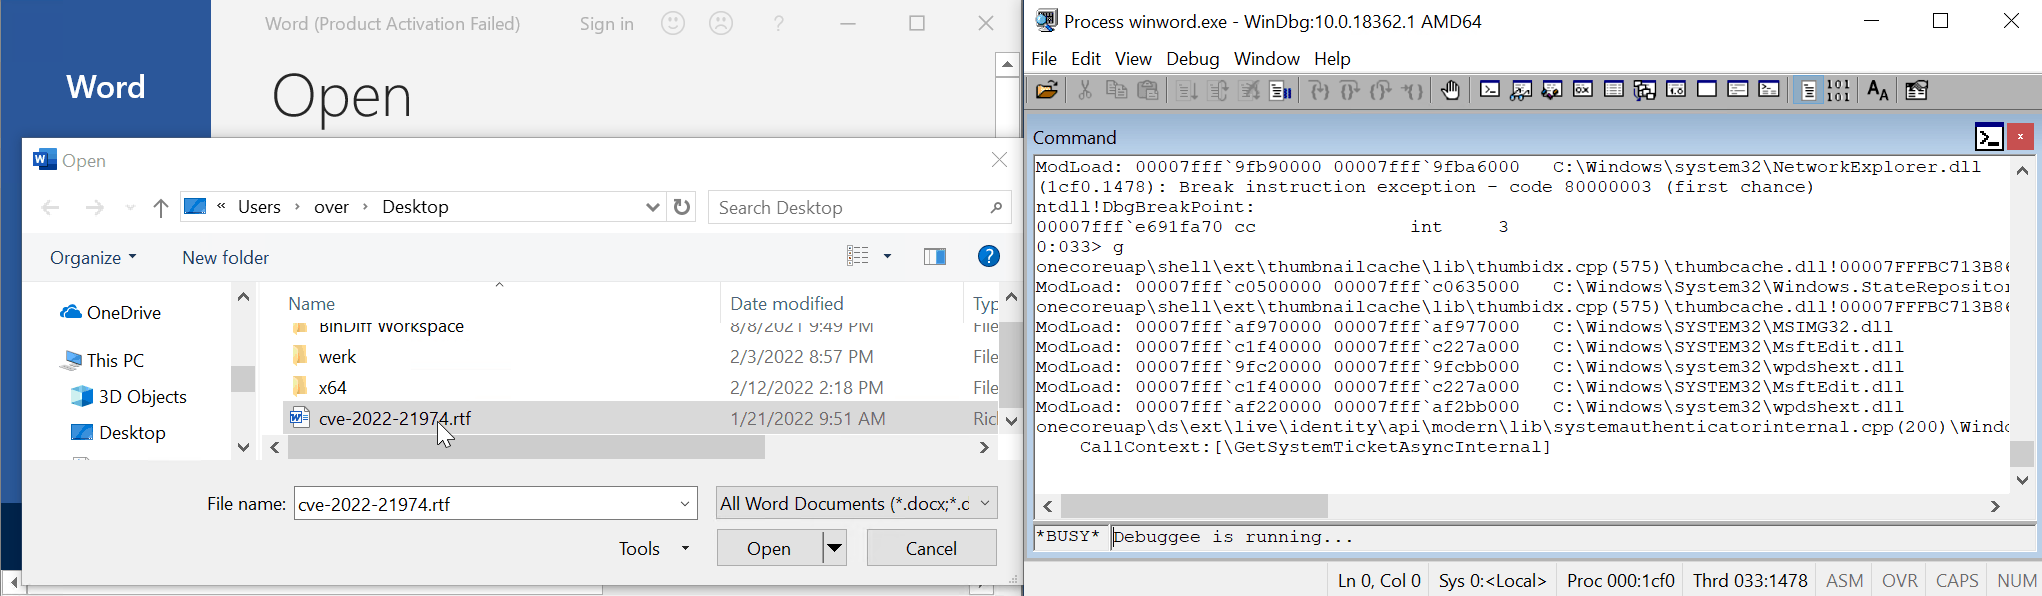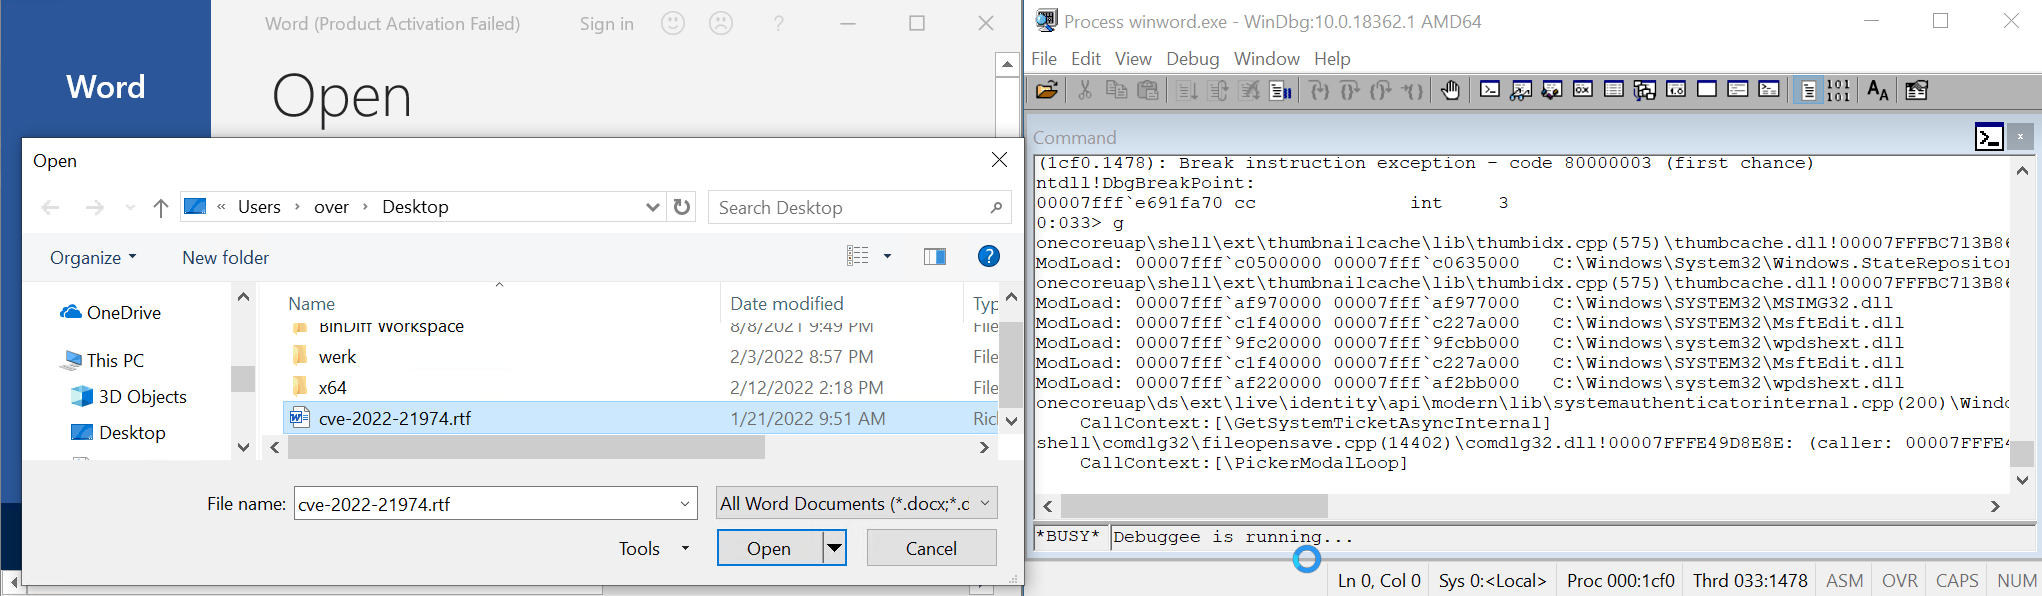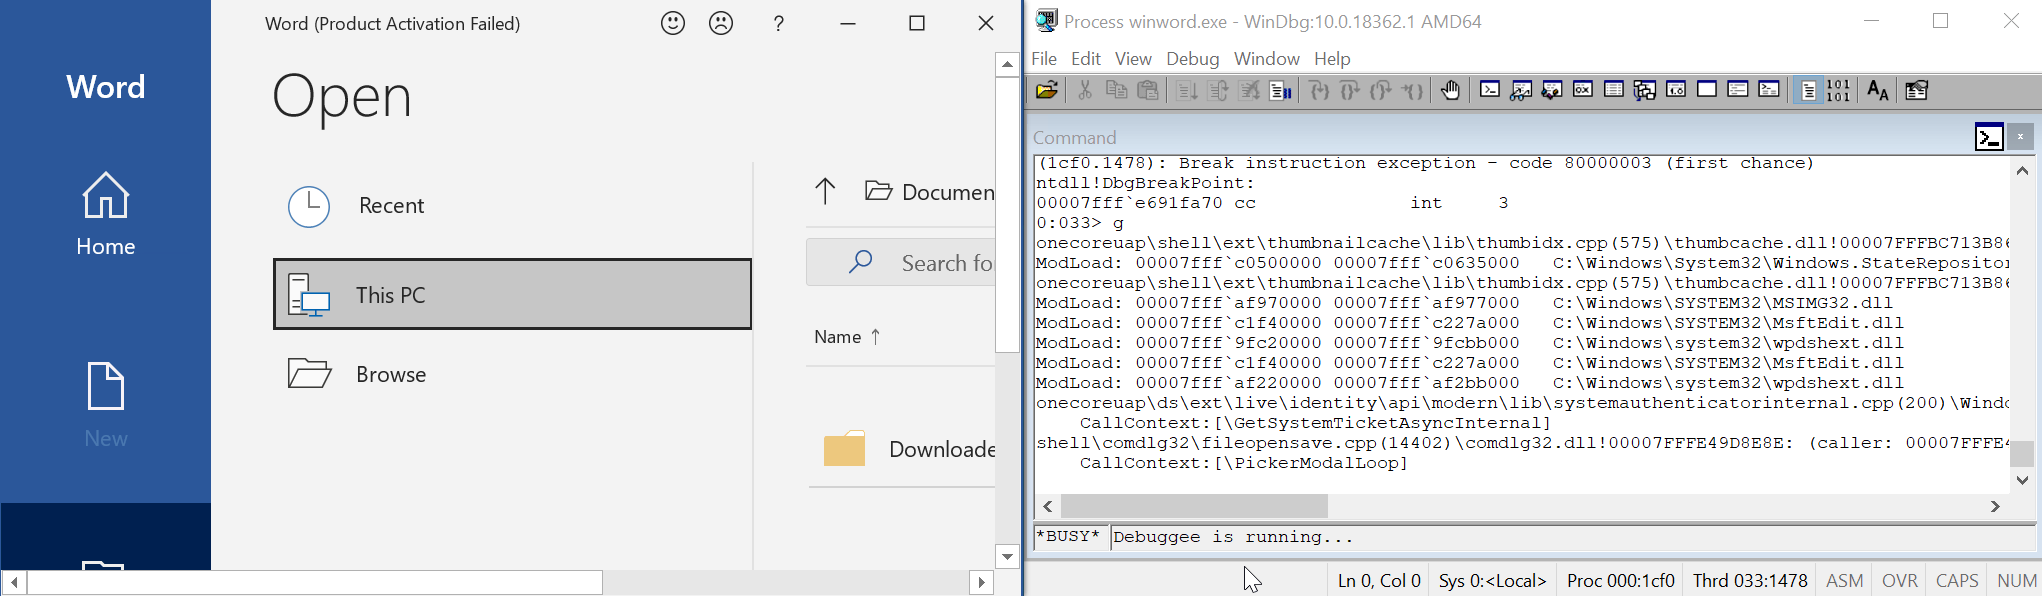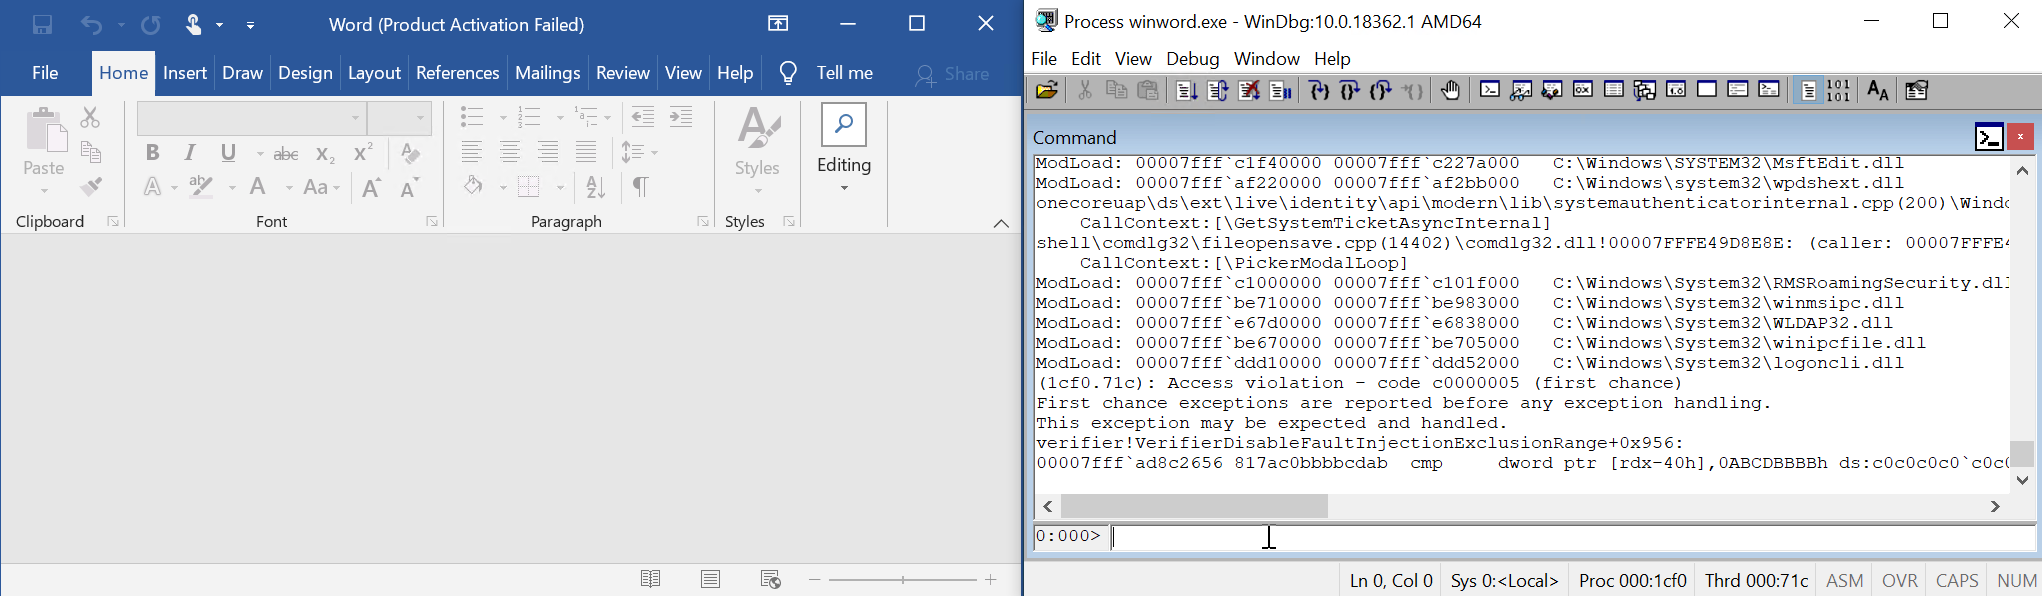 0vercl0k/cve-2022-21974
PoC for CVE-2022-21974 "Roaming Security Rights Management Services Remote Code Execution Vulnerability"
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
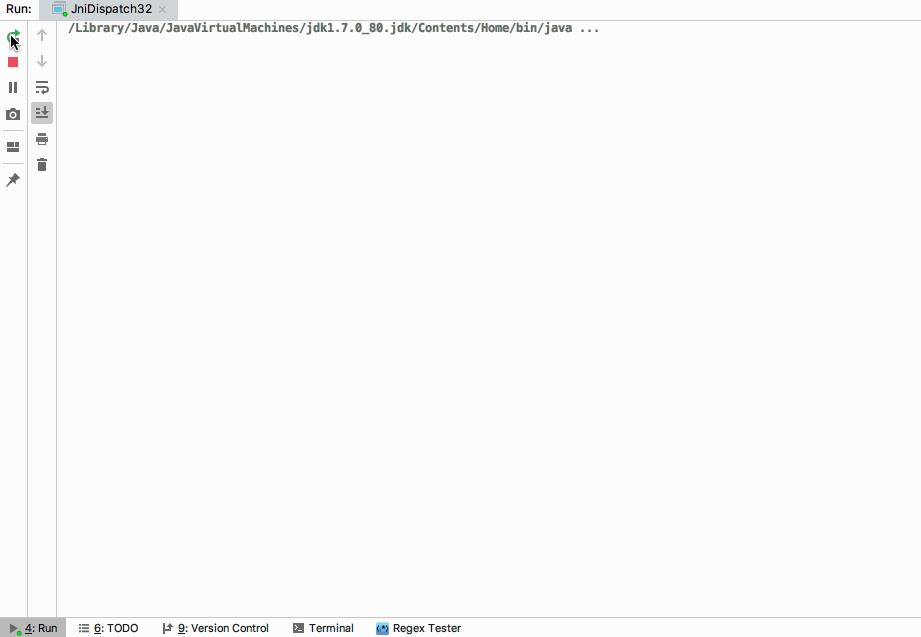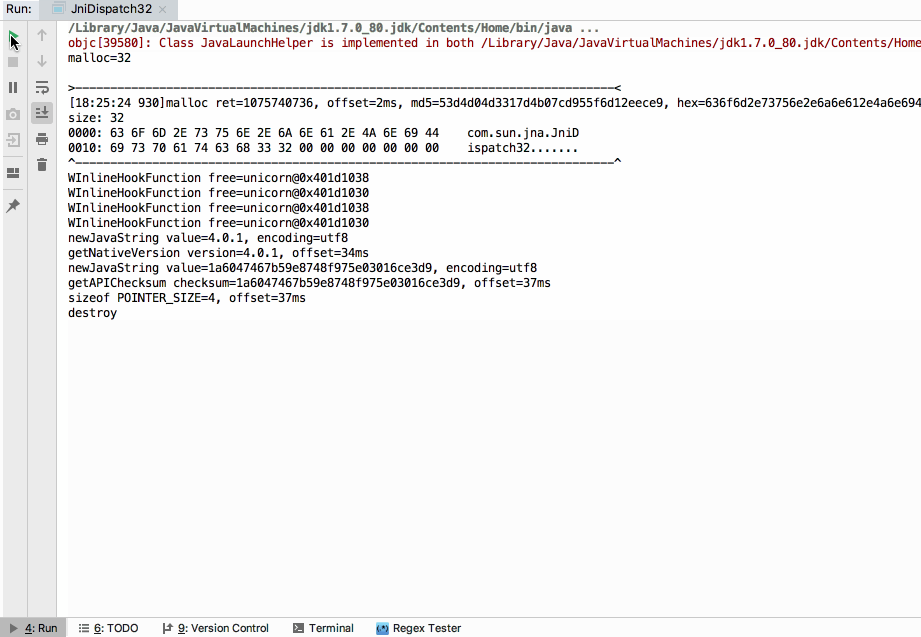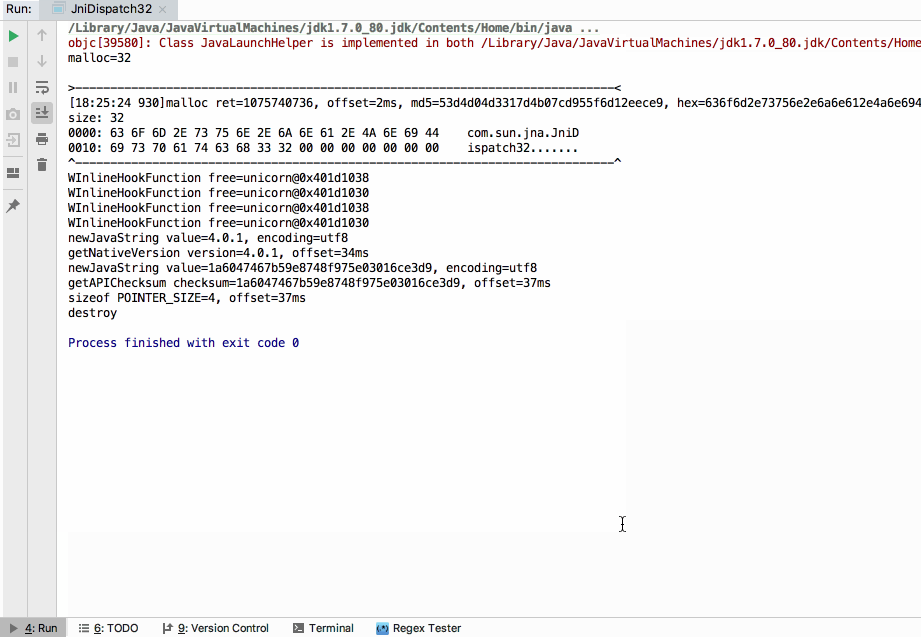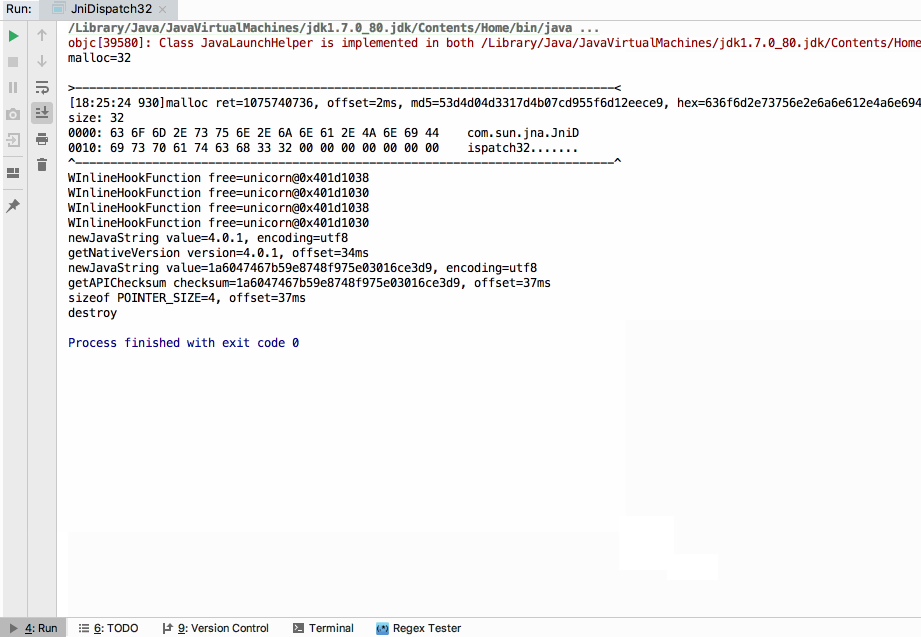 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
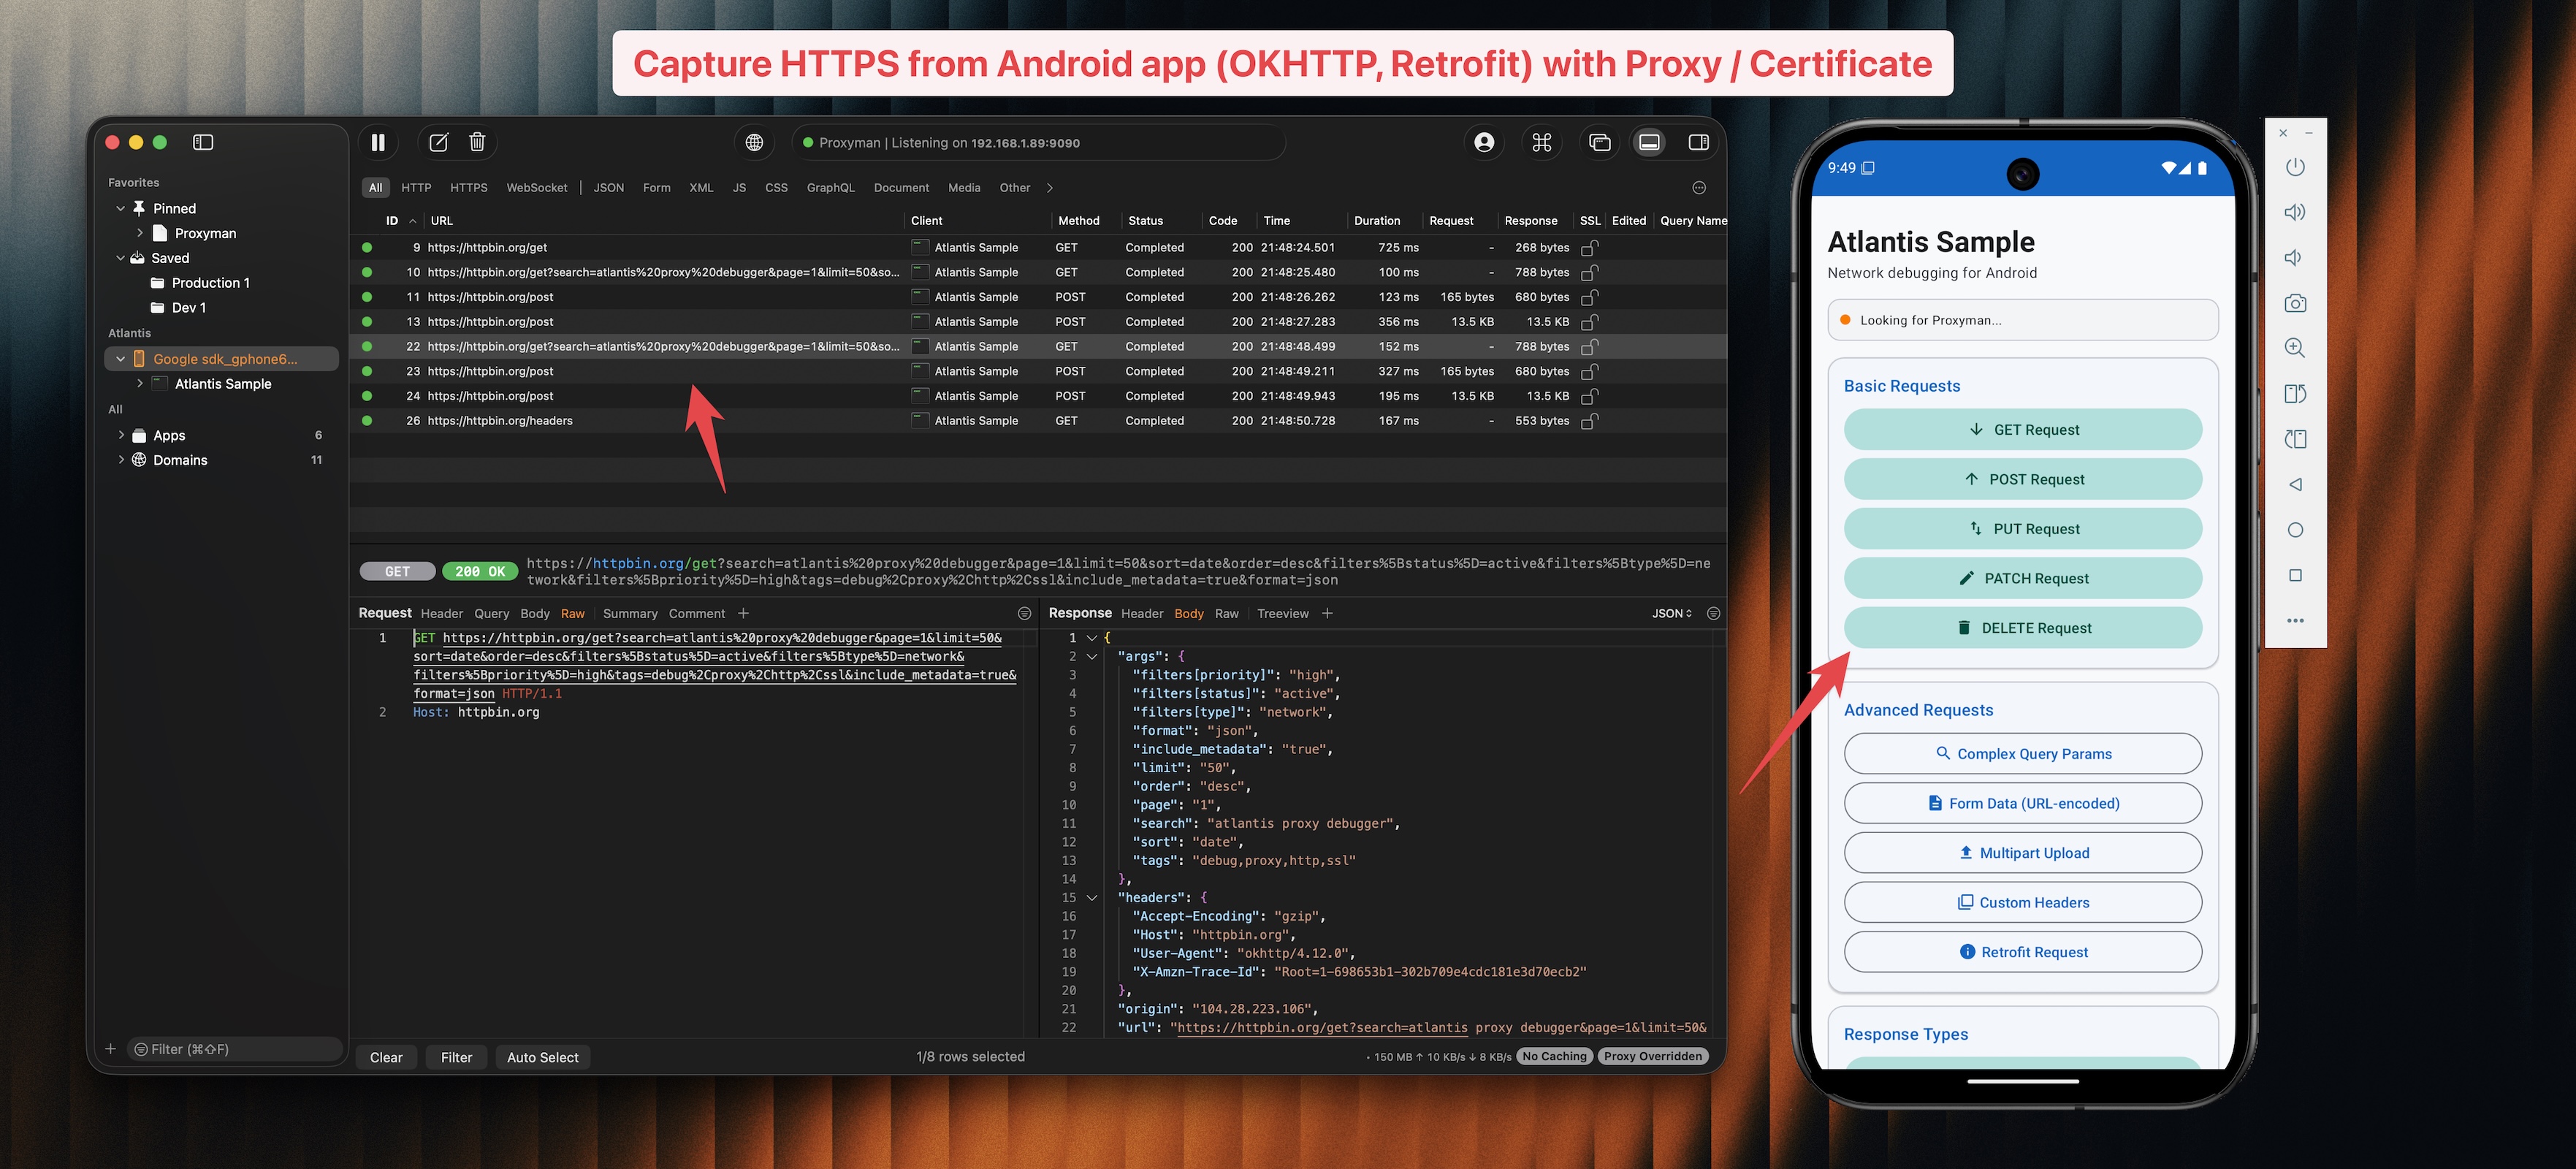 proxymanapp/atlantis-android
Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.
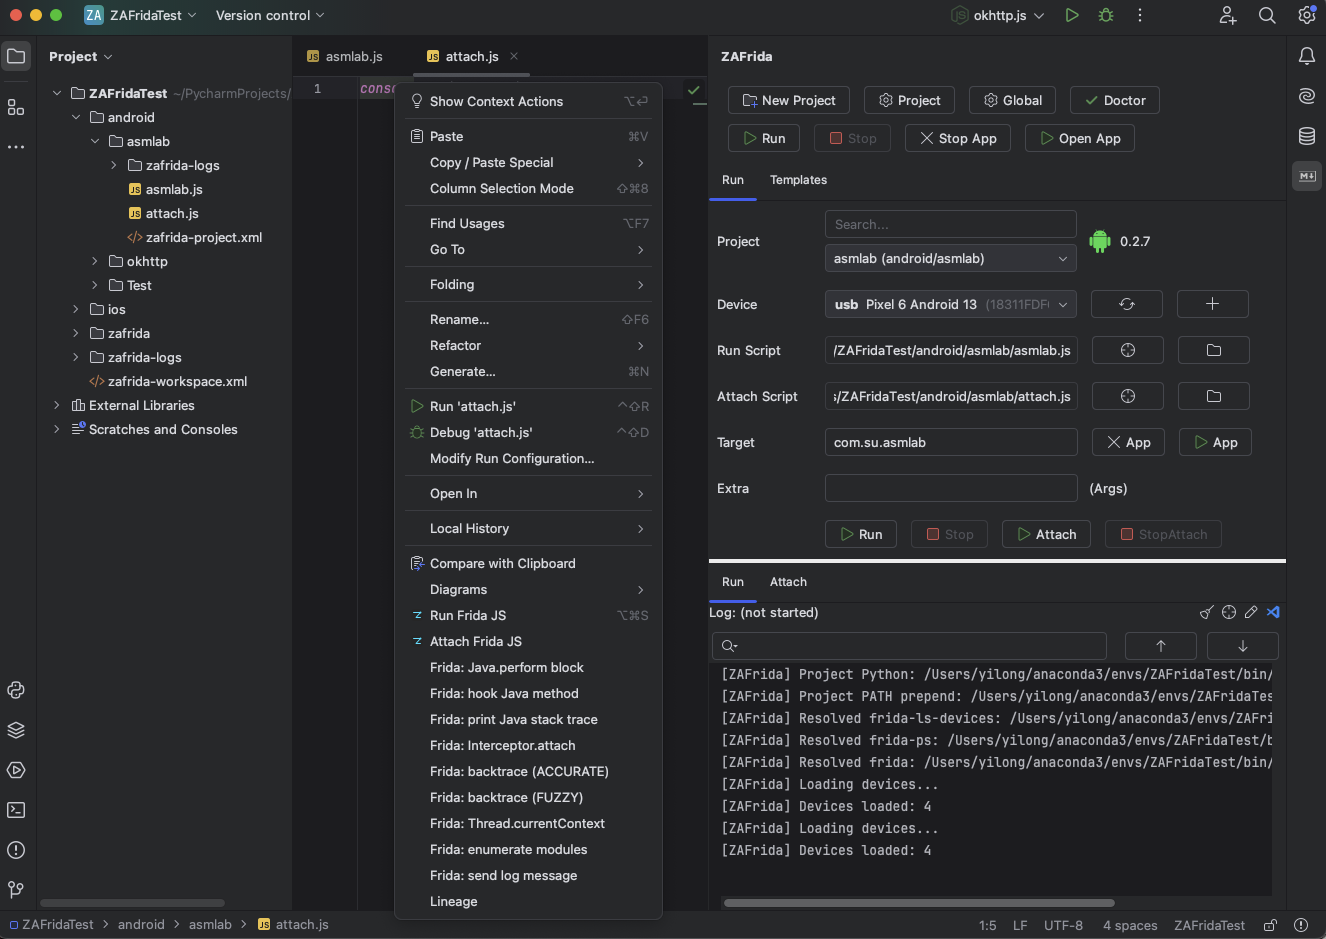 yilongmd/zafrida-ui
A Frida UI tool window inside PyCharm / JetBrains IDEs.