
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
dll-injector — A desktop tool that allows injecting DLLs, hooking WinAPI functions like CreateFileW, and modifying process behavior at runtime — designed for developers, testers, and reverse engineers. | Kitploit
Tools/GitHubGitHub/yasharote/dll-injector
Reverse EngineeringDebuggersBinary Analysis
GitHubyasharote/dll-injector

dll-injector

A desktop tool that allows injecting DLLs, hooking WinAPI functions like CreateFileW, and modifying process behavior at runtime — designed for developers, testers, and reverse engineers.

View Repository
61311 year agoNot yet reviewed
Share

About

As the name suggests, the application primarily performs injecting a DLL into any process running on Windows. With the power of this, it is able to perform several operations on a process such as loading a DLL, unloading a DLL, and hooking primary WinAPI functions (e.g., CreateFileW, ReadFile, etc.).

Its frontend is built using Flutter, and the core functionality is performed using C++. This project bridges the gap in the availability of simplified and effective tools for debugging and behavior modification of Windows processes. Current tools either lack user accessibility due to complexity or do not offer sufficient functionality for comprehensive system-level operations.


Functions

  • The ability to list all running processes, select a target, and inject a DLL
  • Hooking support for specific Windows API functions and modification of parameters in real time
  • Check for the presence of a specific function in a process (only works for exported functions)
  • The ability to unload DLLs from target processes

🪝 Hooking a Function — Getting Started

The application can be downloaded from the Releases section. Below is a step-by-step example of how to hook the CreateFileW function in Notepad.exe and configure it to redirect all file creations to a specific name.


🔹 Step 1: Select a Target Process

Start by launching the DLL Injector application. You'll see a grid of running processes with their names and Process IDs (PIDs).

➡️ Click on the hook option for Notepad.exe.
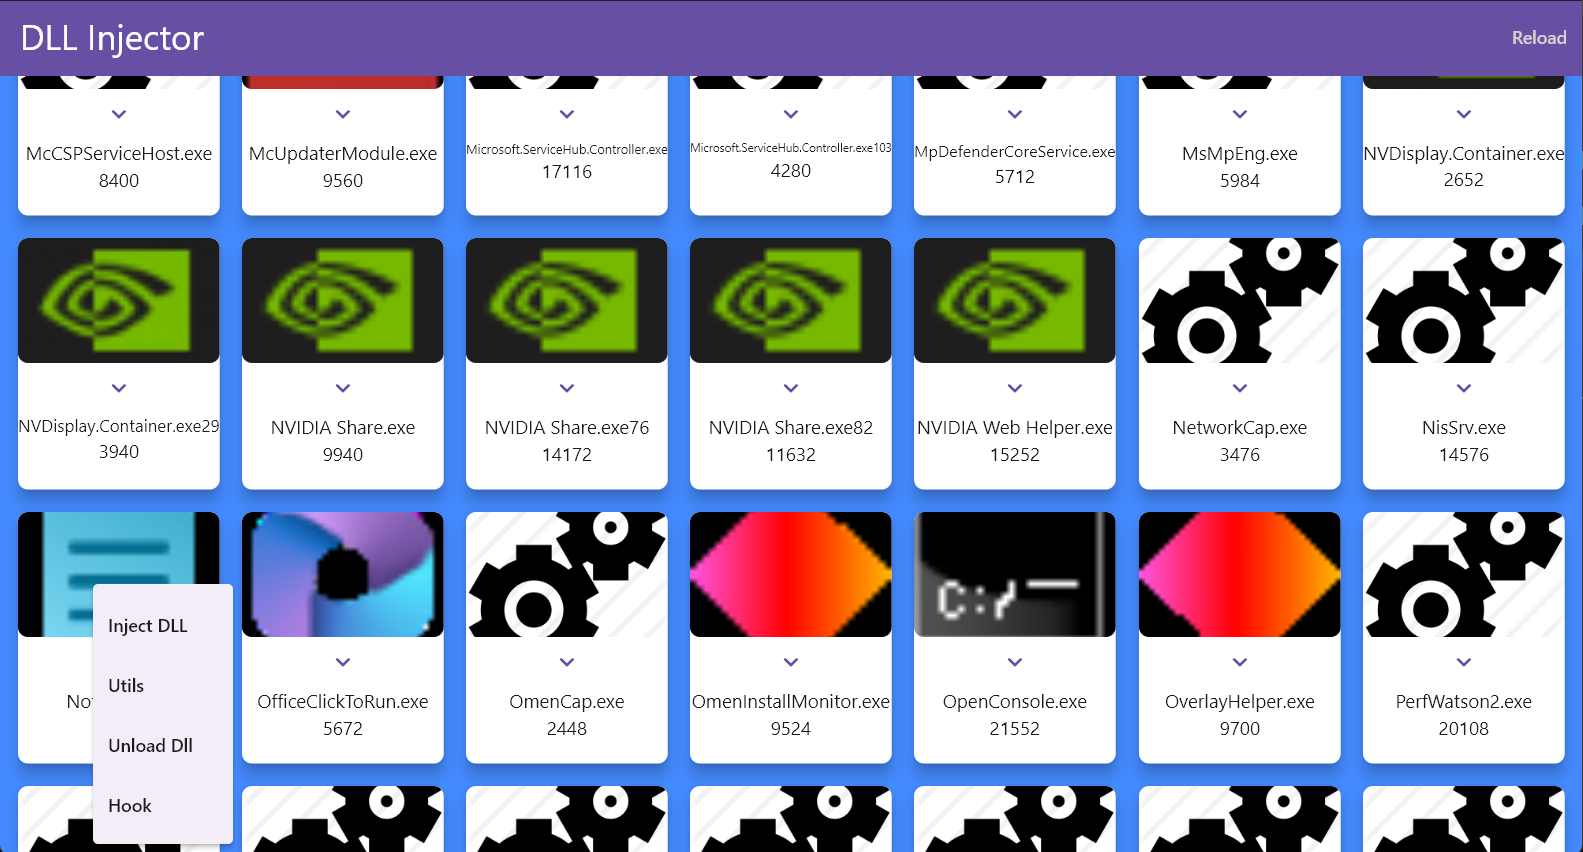
Step 1: Select Process


🔹 Step 2: Configure the Hook

After selecting a process, a popup will appear prompting you to configure which function to hook and under what conditions.

In this example:

  • Function: CreateFileW
  • match_path: E:\Downloads\
  • lpFileName: E:\Downloads\hooked.txt
  • block: Disabled (to allow execution)

Once configured, click Hook to inject the DLL and activate the hook.

Step 2: Configure Hook


🔹 Step 3: Hook Success Confirmation

If the hook was applied successfully, you'll see a confirmation dialog.
You must press "Unhook" when you're done, to safely remove the hook from the target process.

⚠️ If the hook is not removed, the process may need to be restarted manually.
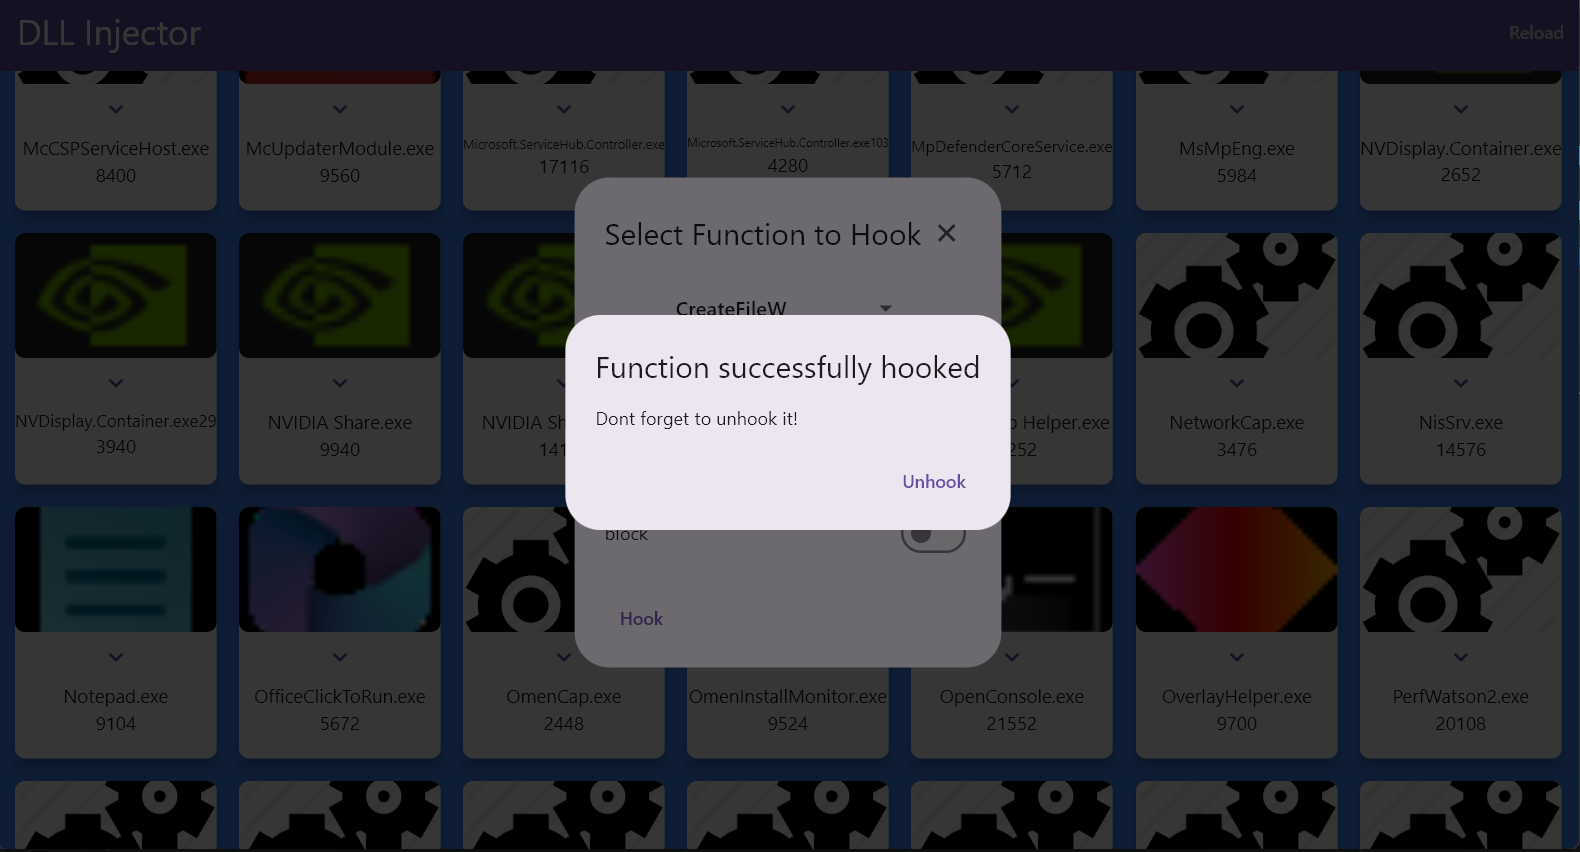
Step 3: Hook Success


🔎 Test the Hook

To check what happened:

Try saving any file inside E:\Downloads\ — regardless of the file name, it will be forced to be named hooked.txt.

This demonstrates how you can intercept and manipulate file system operations at the API level using the injected hook.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →




