
usbsnoop
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
debuggersdynamic-analysis-sandboxingembedded-systems-security+7
87
yeet-src/usbsnoopLive, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
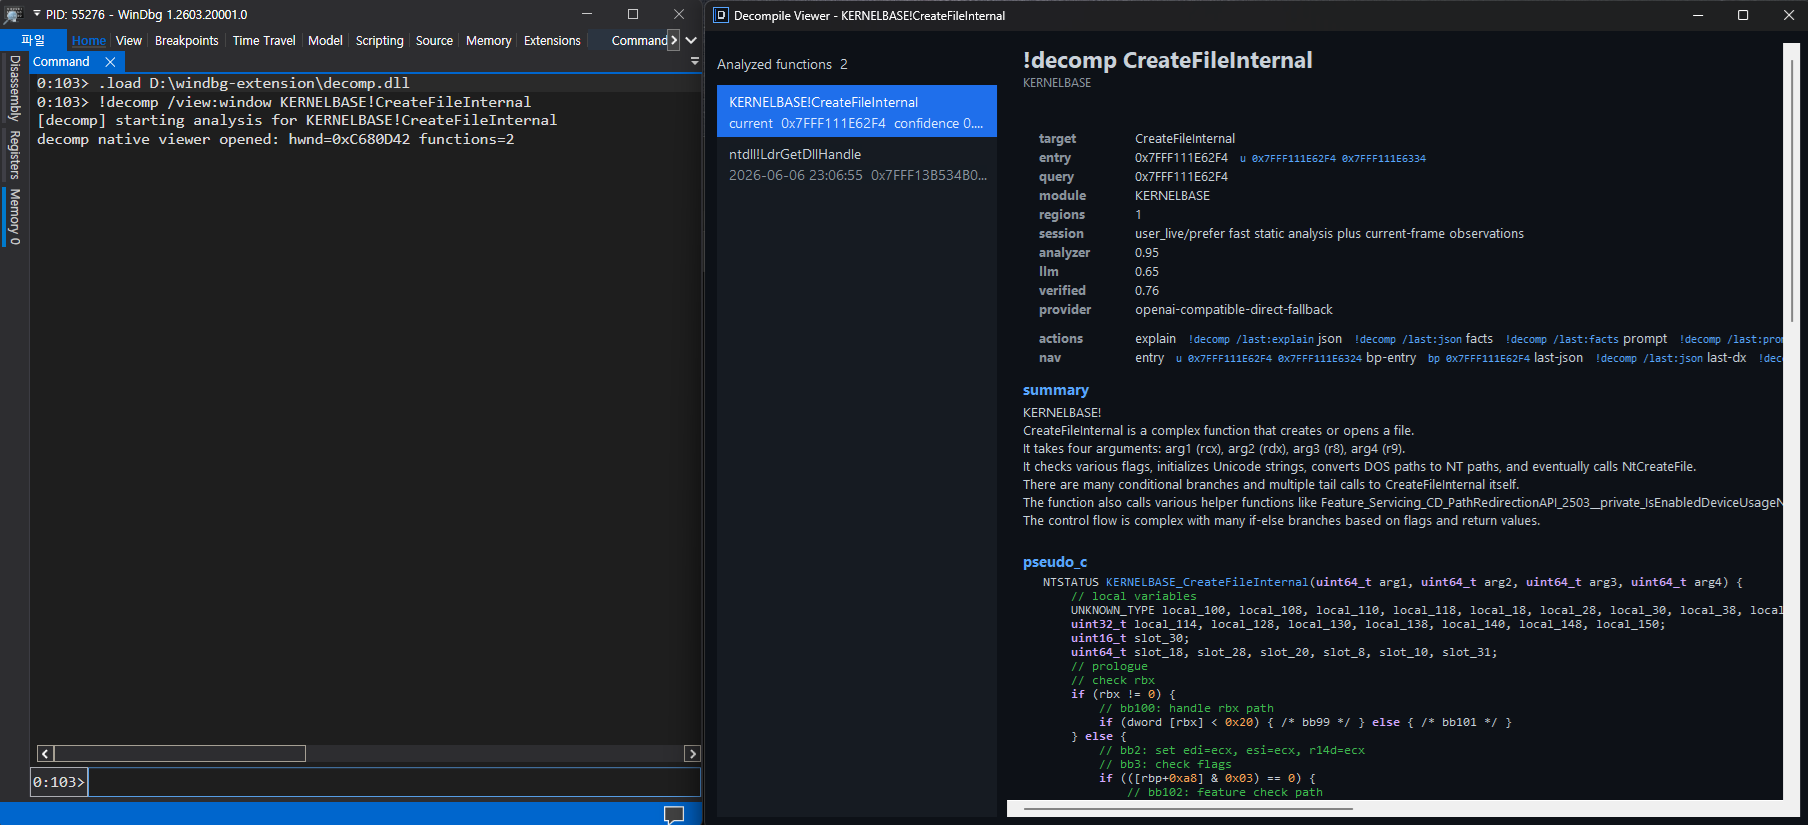 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
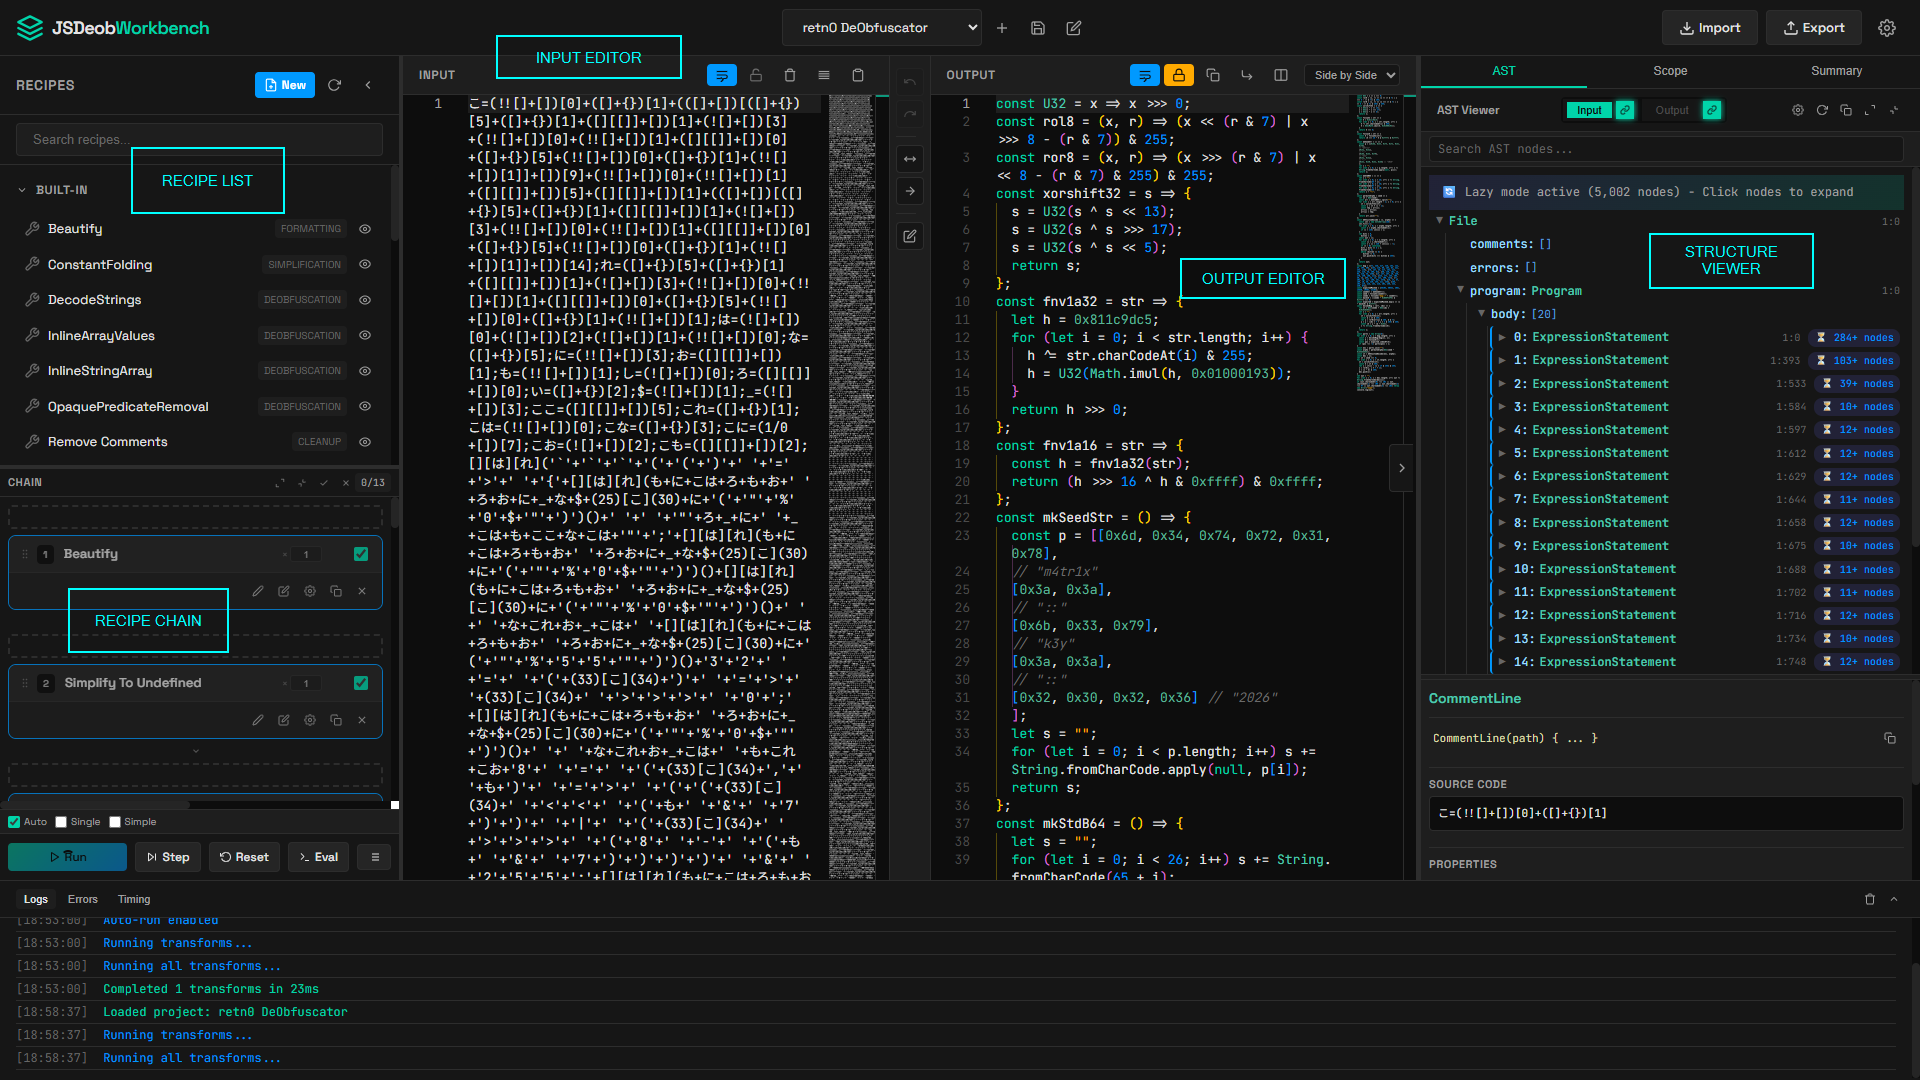 owl4444/jsdeob-workbench
Reverse engineer obfuscated JavaScript visually. Chain transforms, inspect AST changes, write reusable deobfuscation plugins.
 ggfuchsi-oss/spectrida-reverse_engineering_stack
Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…
 daniellmcguire/xboxseries
Personal research into the Xbox Series Architecture
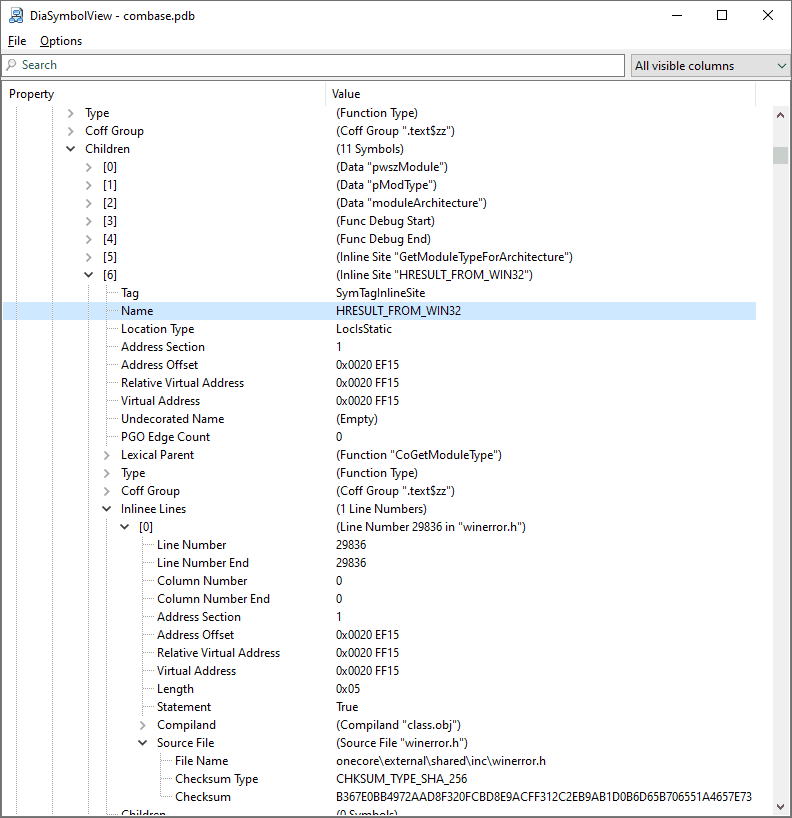 diversenok/diasymbolview
PDB file inspection tool
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 pownjs/cdb
Automate common Chrome Debug Protocol tasks to help debug web applications from the command-line and actively monitor and intercept HTTP requests and…
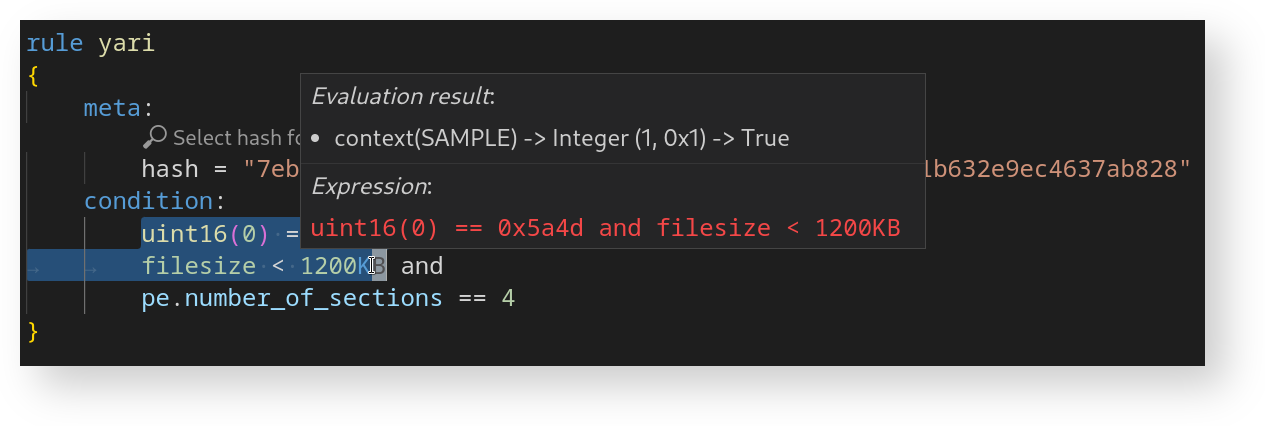 avast/yari
YARI is an interactive debugger for YARA Language.
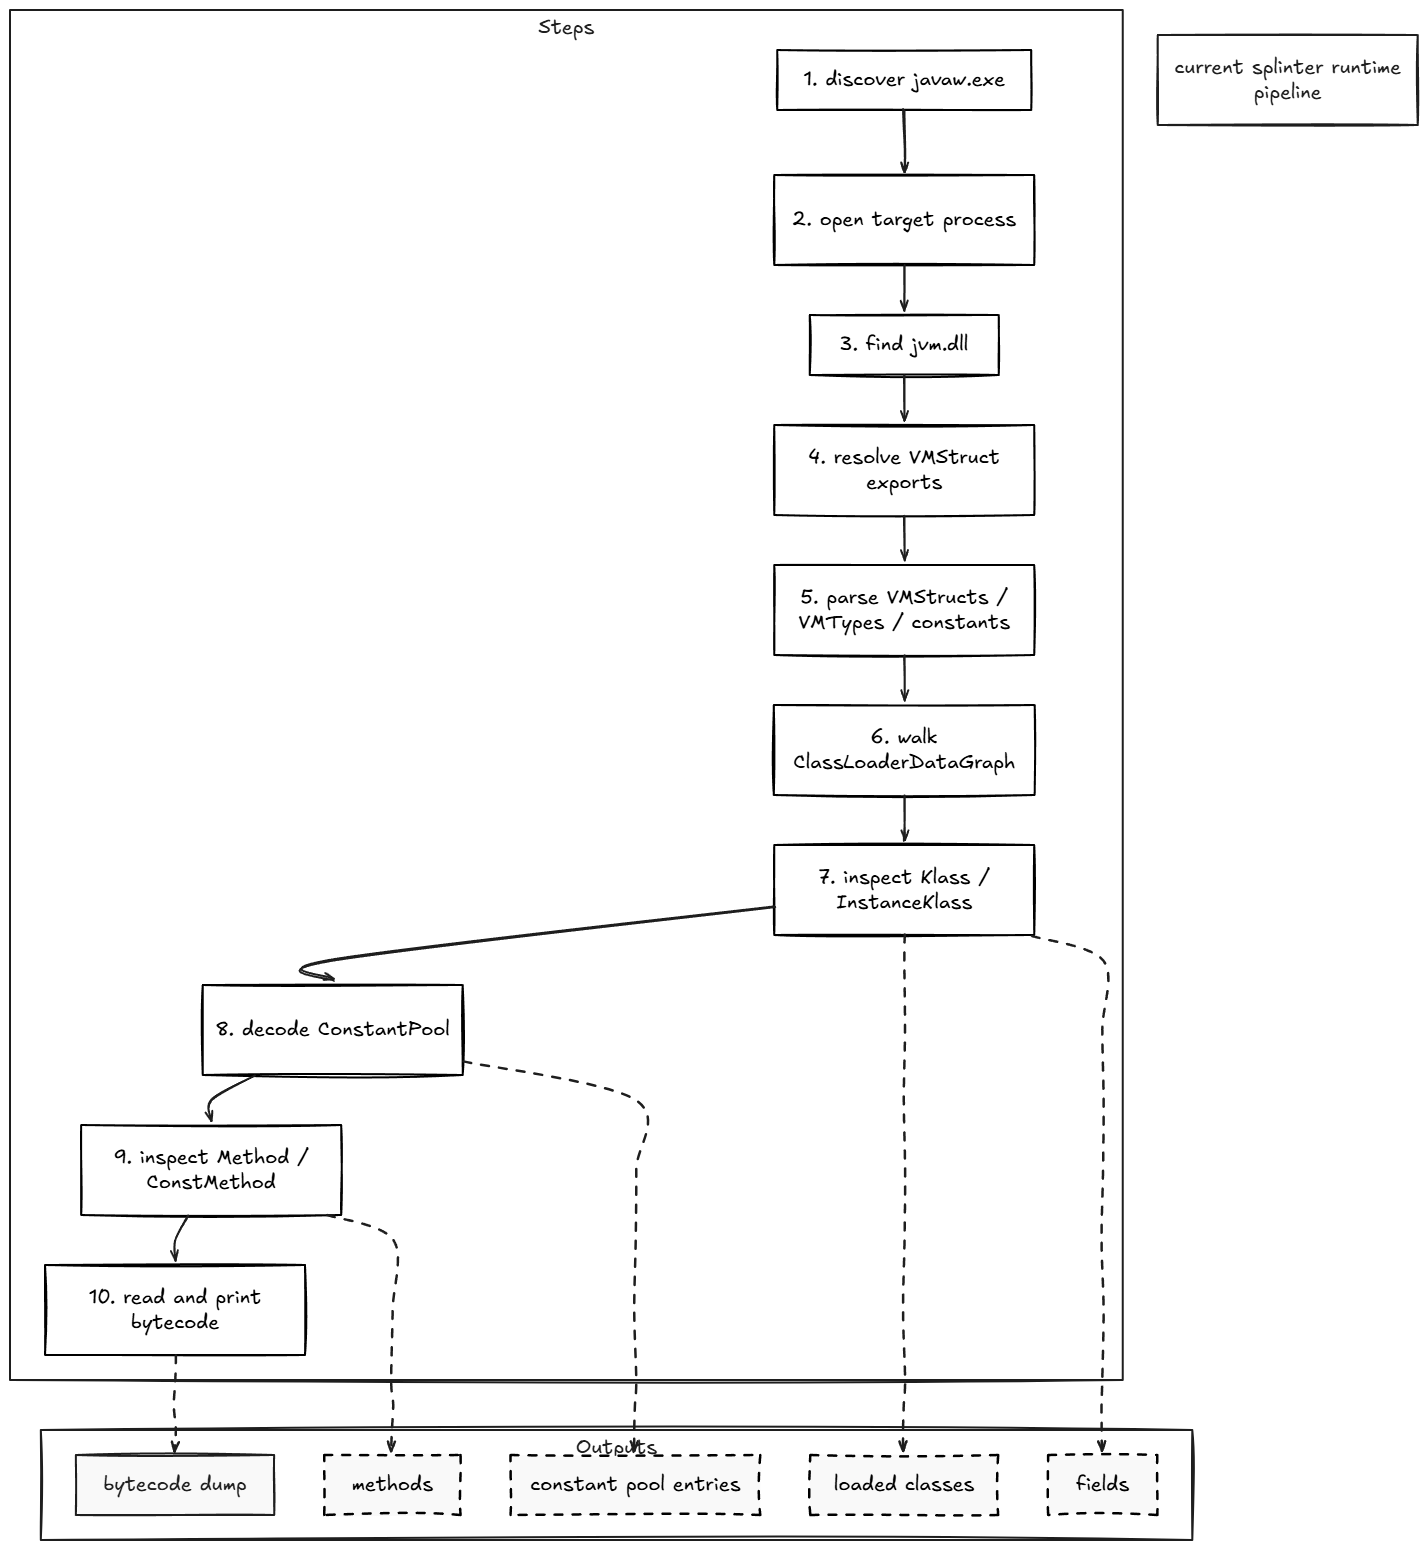 awrped/splinter
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
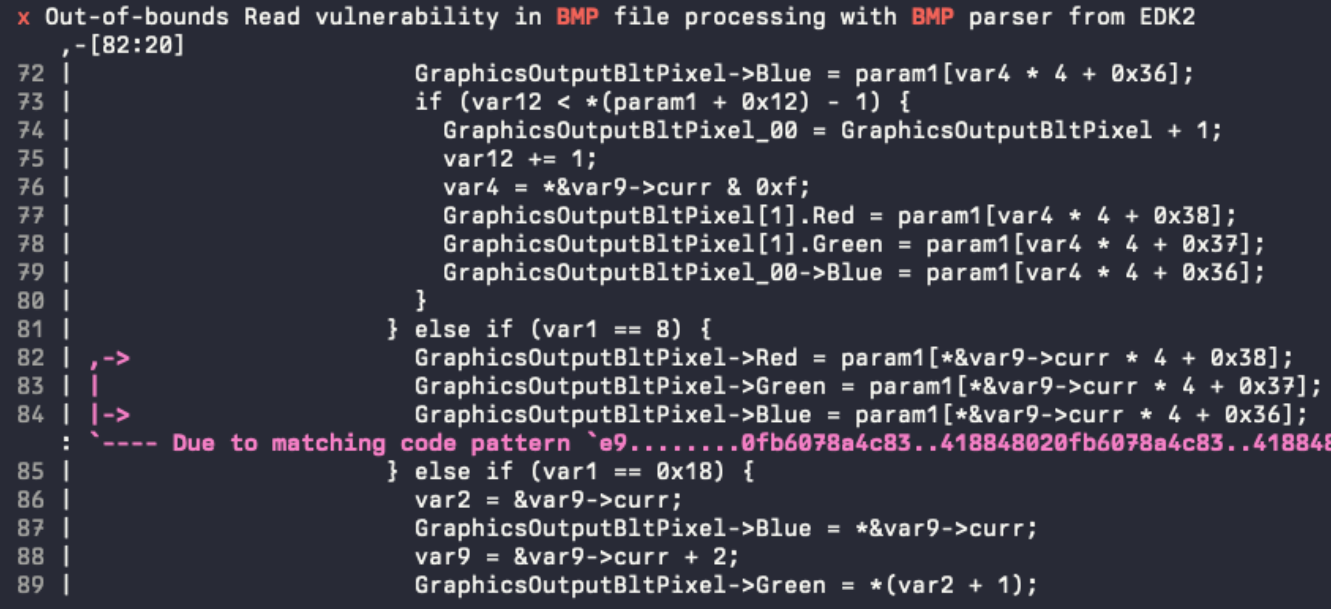 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
 sadopc/machscope
All-in-one macOS binary analysis: Mach-O parsing, ARM64 disassembly, code signatures, and debugging.
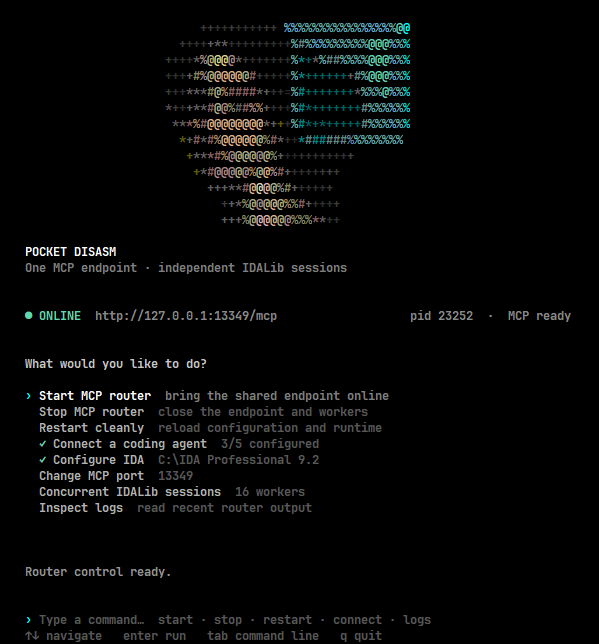 whoisqwerz/pocket_disasm
Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.
 libtero/idaguides
indent guides plugin for hex-rays decompiler
 euva-project/euva
A lightweight hex editor and decompiler to solve your binary file analysis problems.
 kartoffelpflanze/odis-project-explorer
Python dumper/explorer for MCD Runtime Projects used by ODIS
 ddudle/ctxdebug
MCP-powered reverse engineering platform connecting WinDbg, IDA Pro & x64dbg with 160+ AI-accessible debugging and analysis tools.
 therealdreg/ida_bochs_windows
Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)