
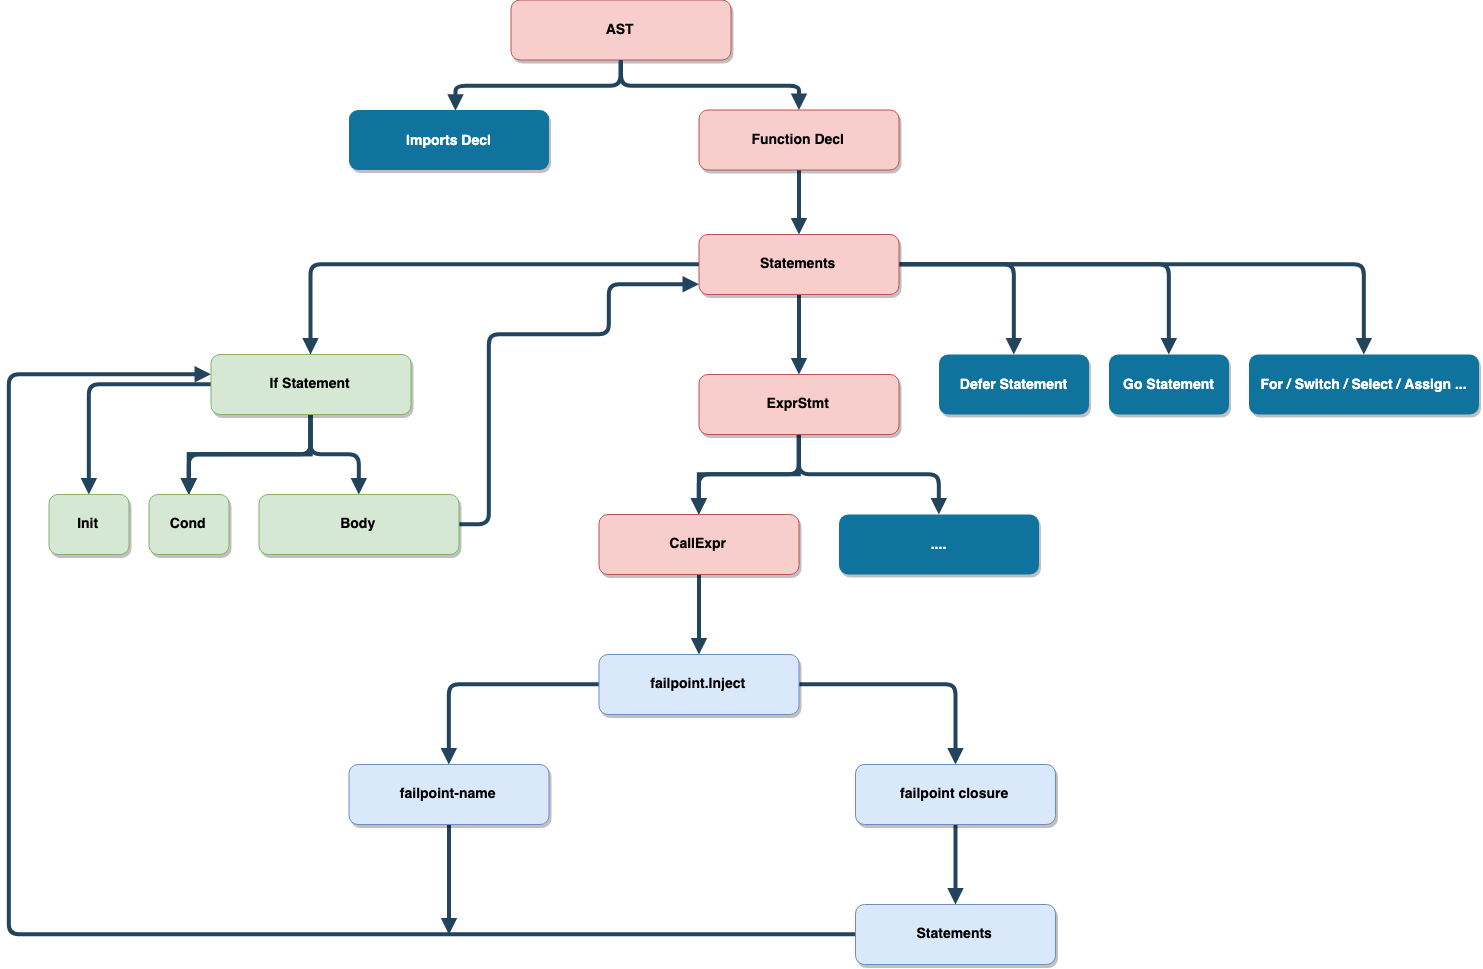
failpoint
 pingcap/failpoint
Fault-injection library for Go that adds runtime-controllable failpoints to trigger panics, sleeps, returns, and conditional error paths via…
chaos-engineeringdebuggersgeneral-purpose-utilities
pingcap/failpointFault-injection library for Go that adds runtime-controllable failpoints to trigger panics, sleeps, returns, and conditional error paths via…
 ioactive/jdwp-shellifier
Exploitation script for exposed Java Debug Wire Protocol (JDWP) services, enabling pentesters to inject Java code and execute arbitrary OS commands…
 grammatech/ddisasm
Datalog-based disassembler producing reassemblable assembly from ELF/PE binaries, with GTIRB intermediate representation for binary analysis and…
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 rocky/python-decompile3
Python decompiler for 3.7-3.8 Stripped down from uncompyle6 so we can refactor and start to fix up some long-standing problems
 symgraph/ghidrassist
An LLM extension for Ghidra to enable AI assistance in RE.
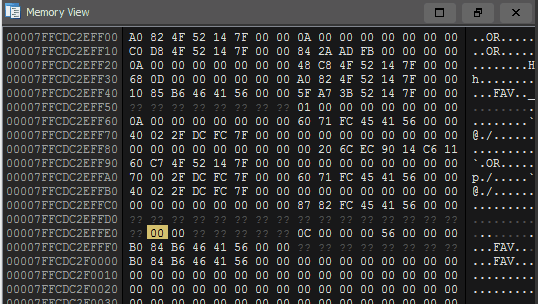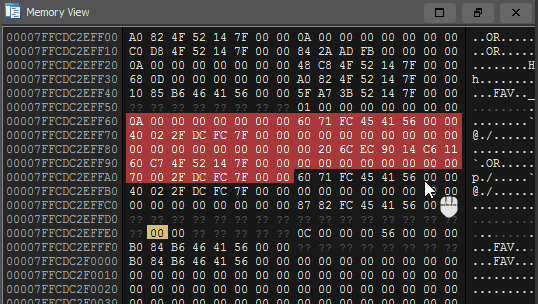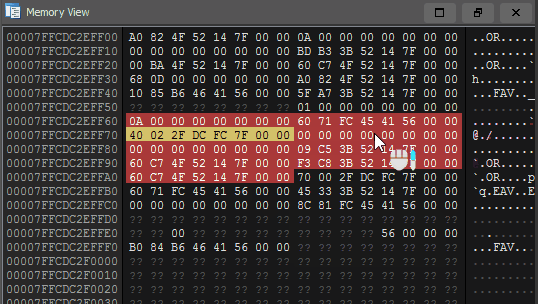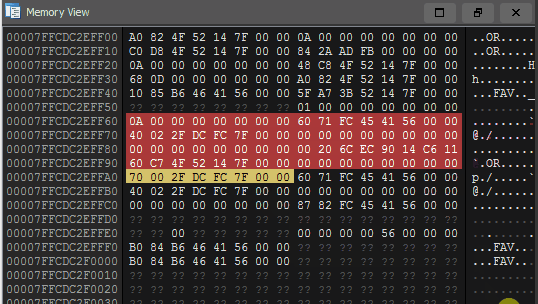 gaasedelen/tenet
A Trace Explorer for Reverse Engineers
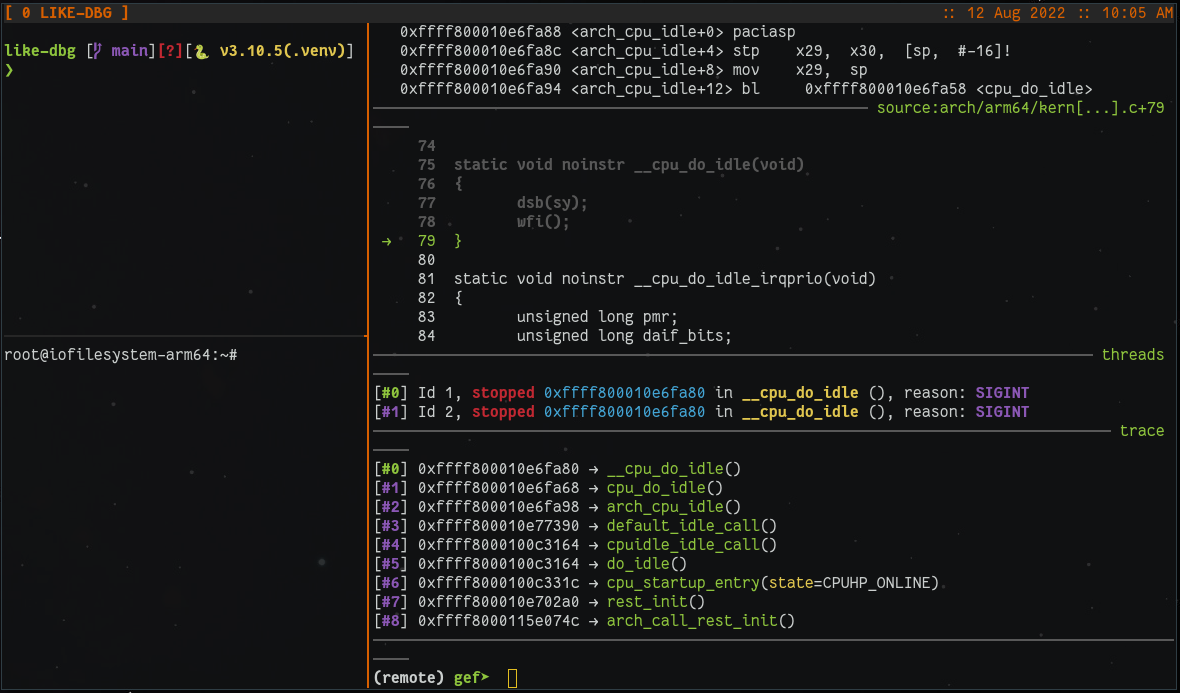 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment for Linux and MacOS
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
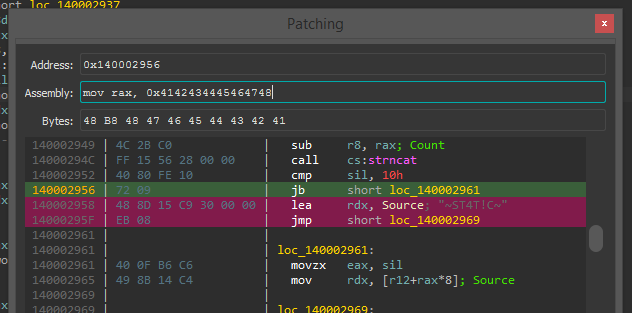 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
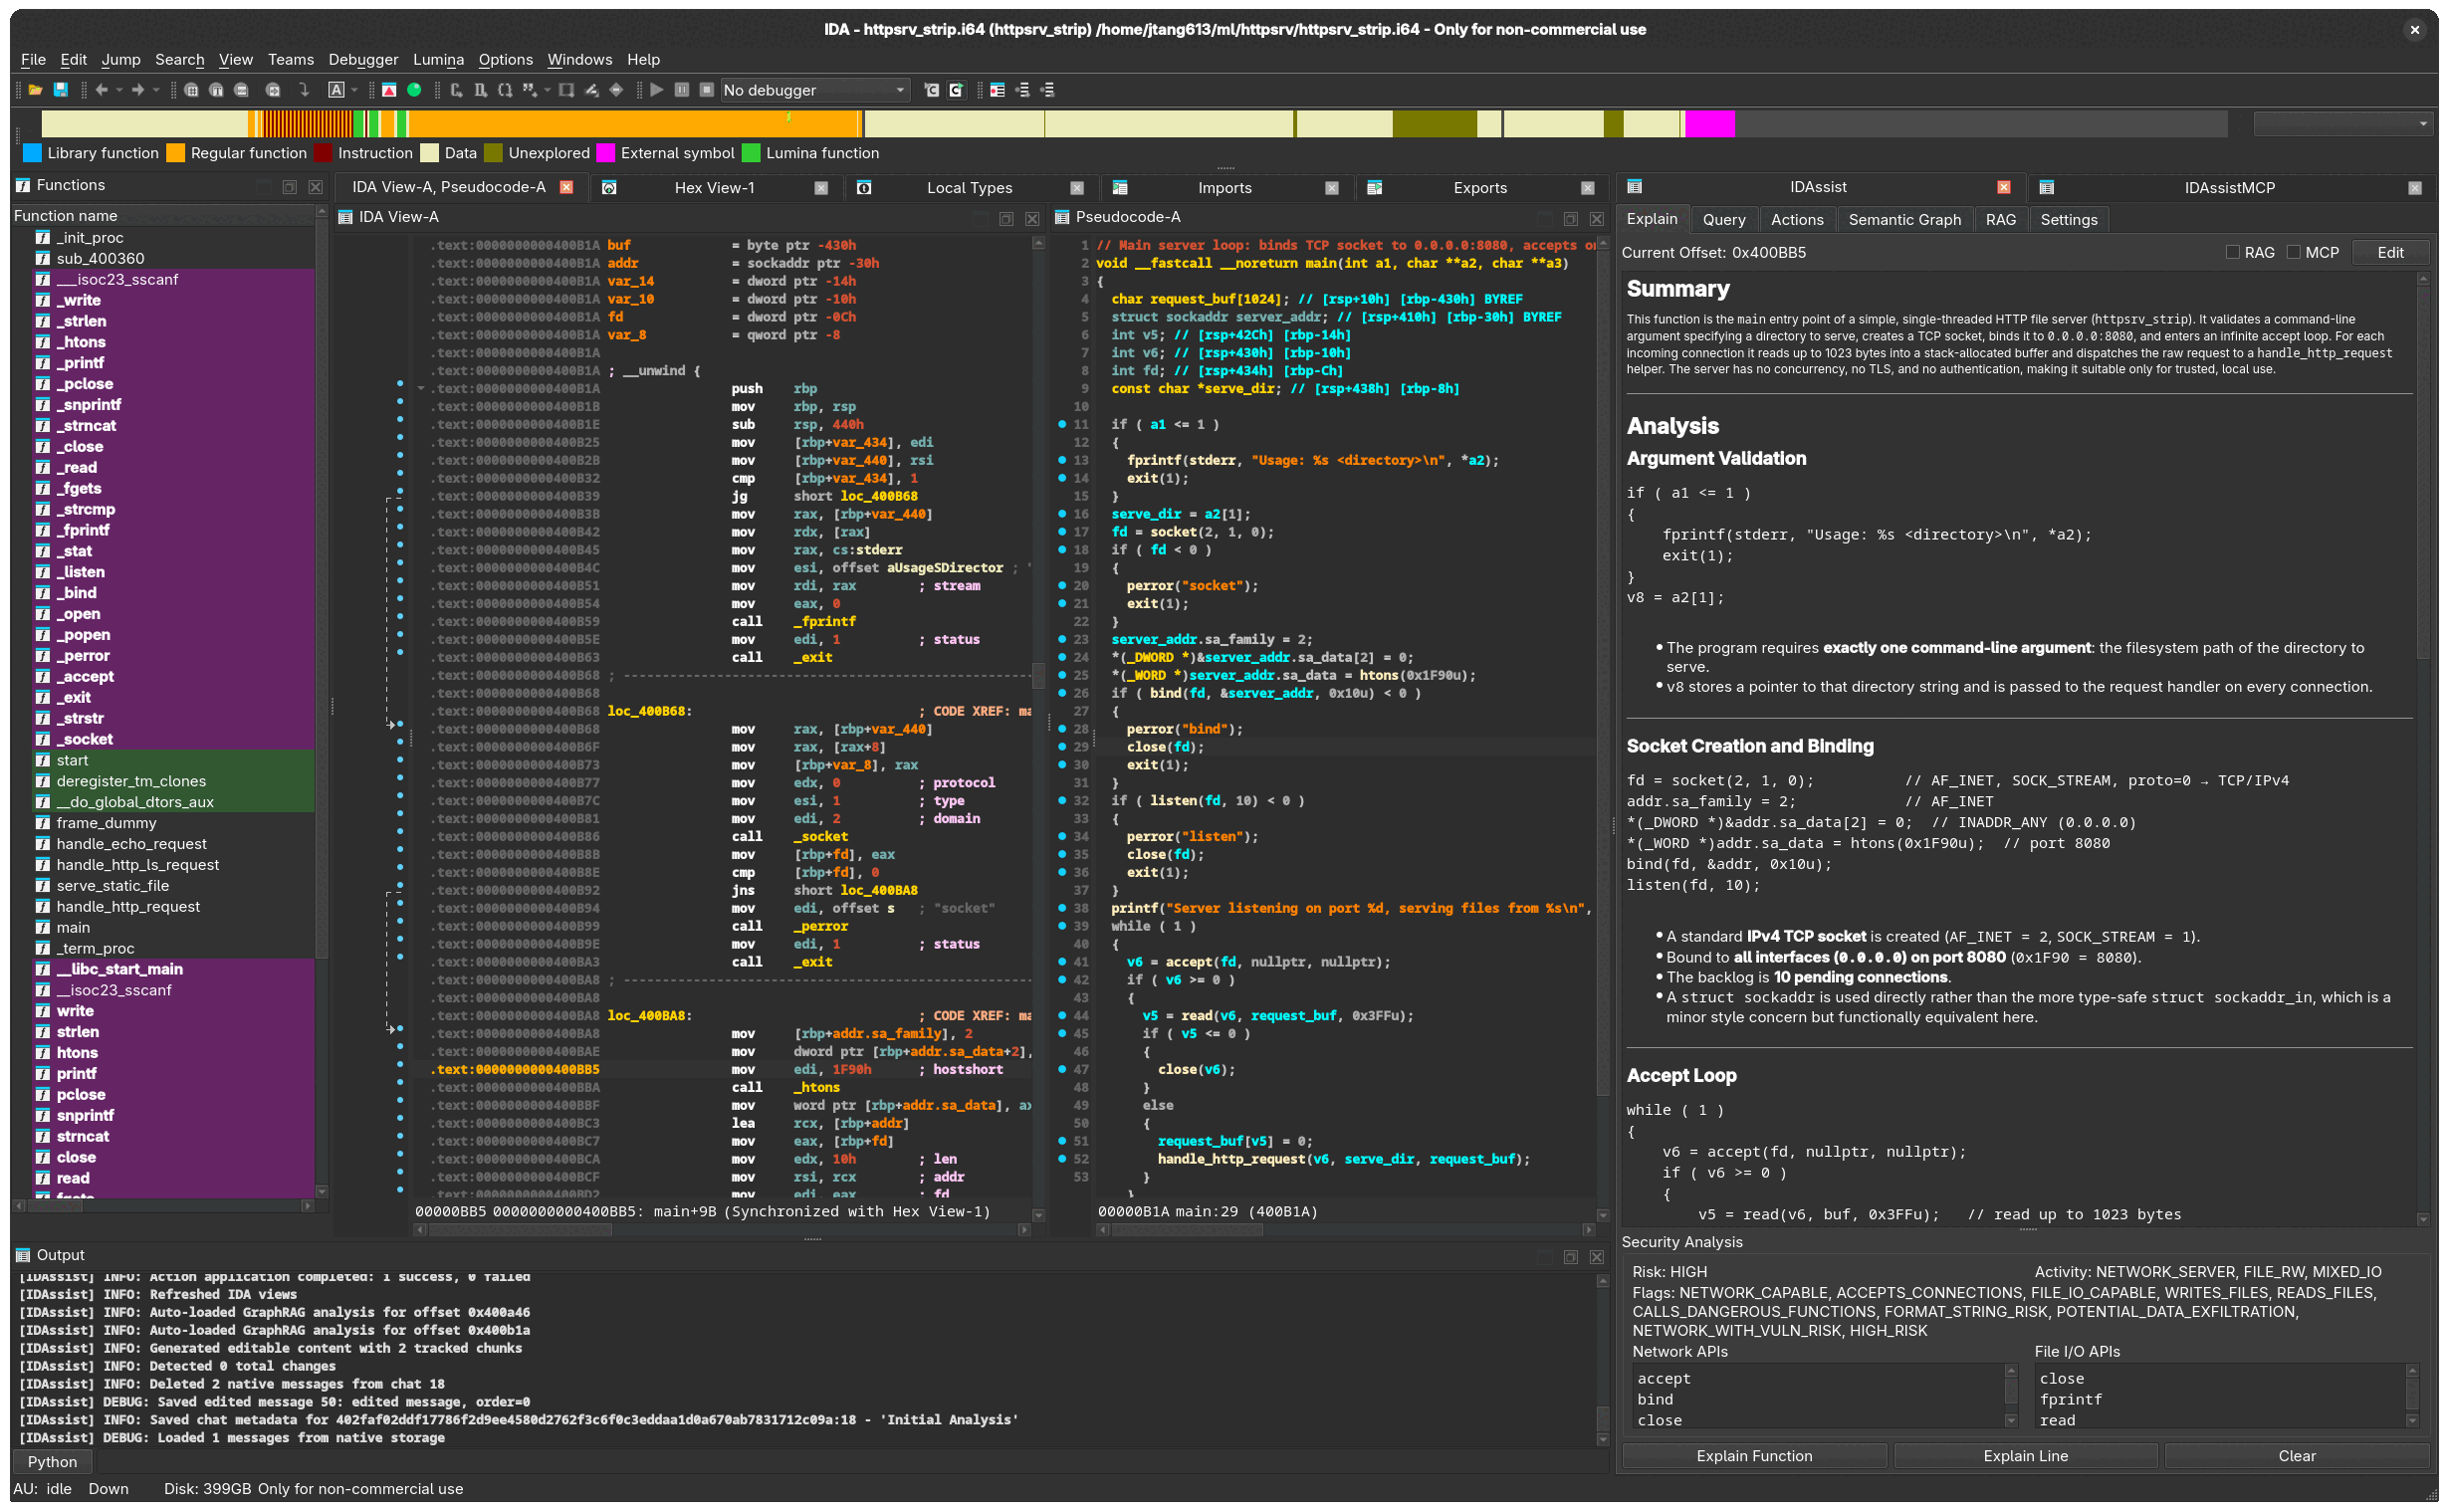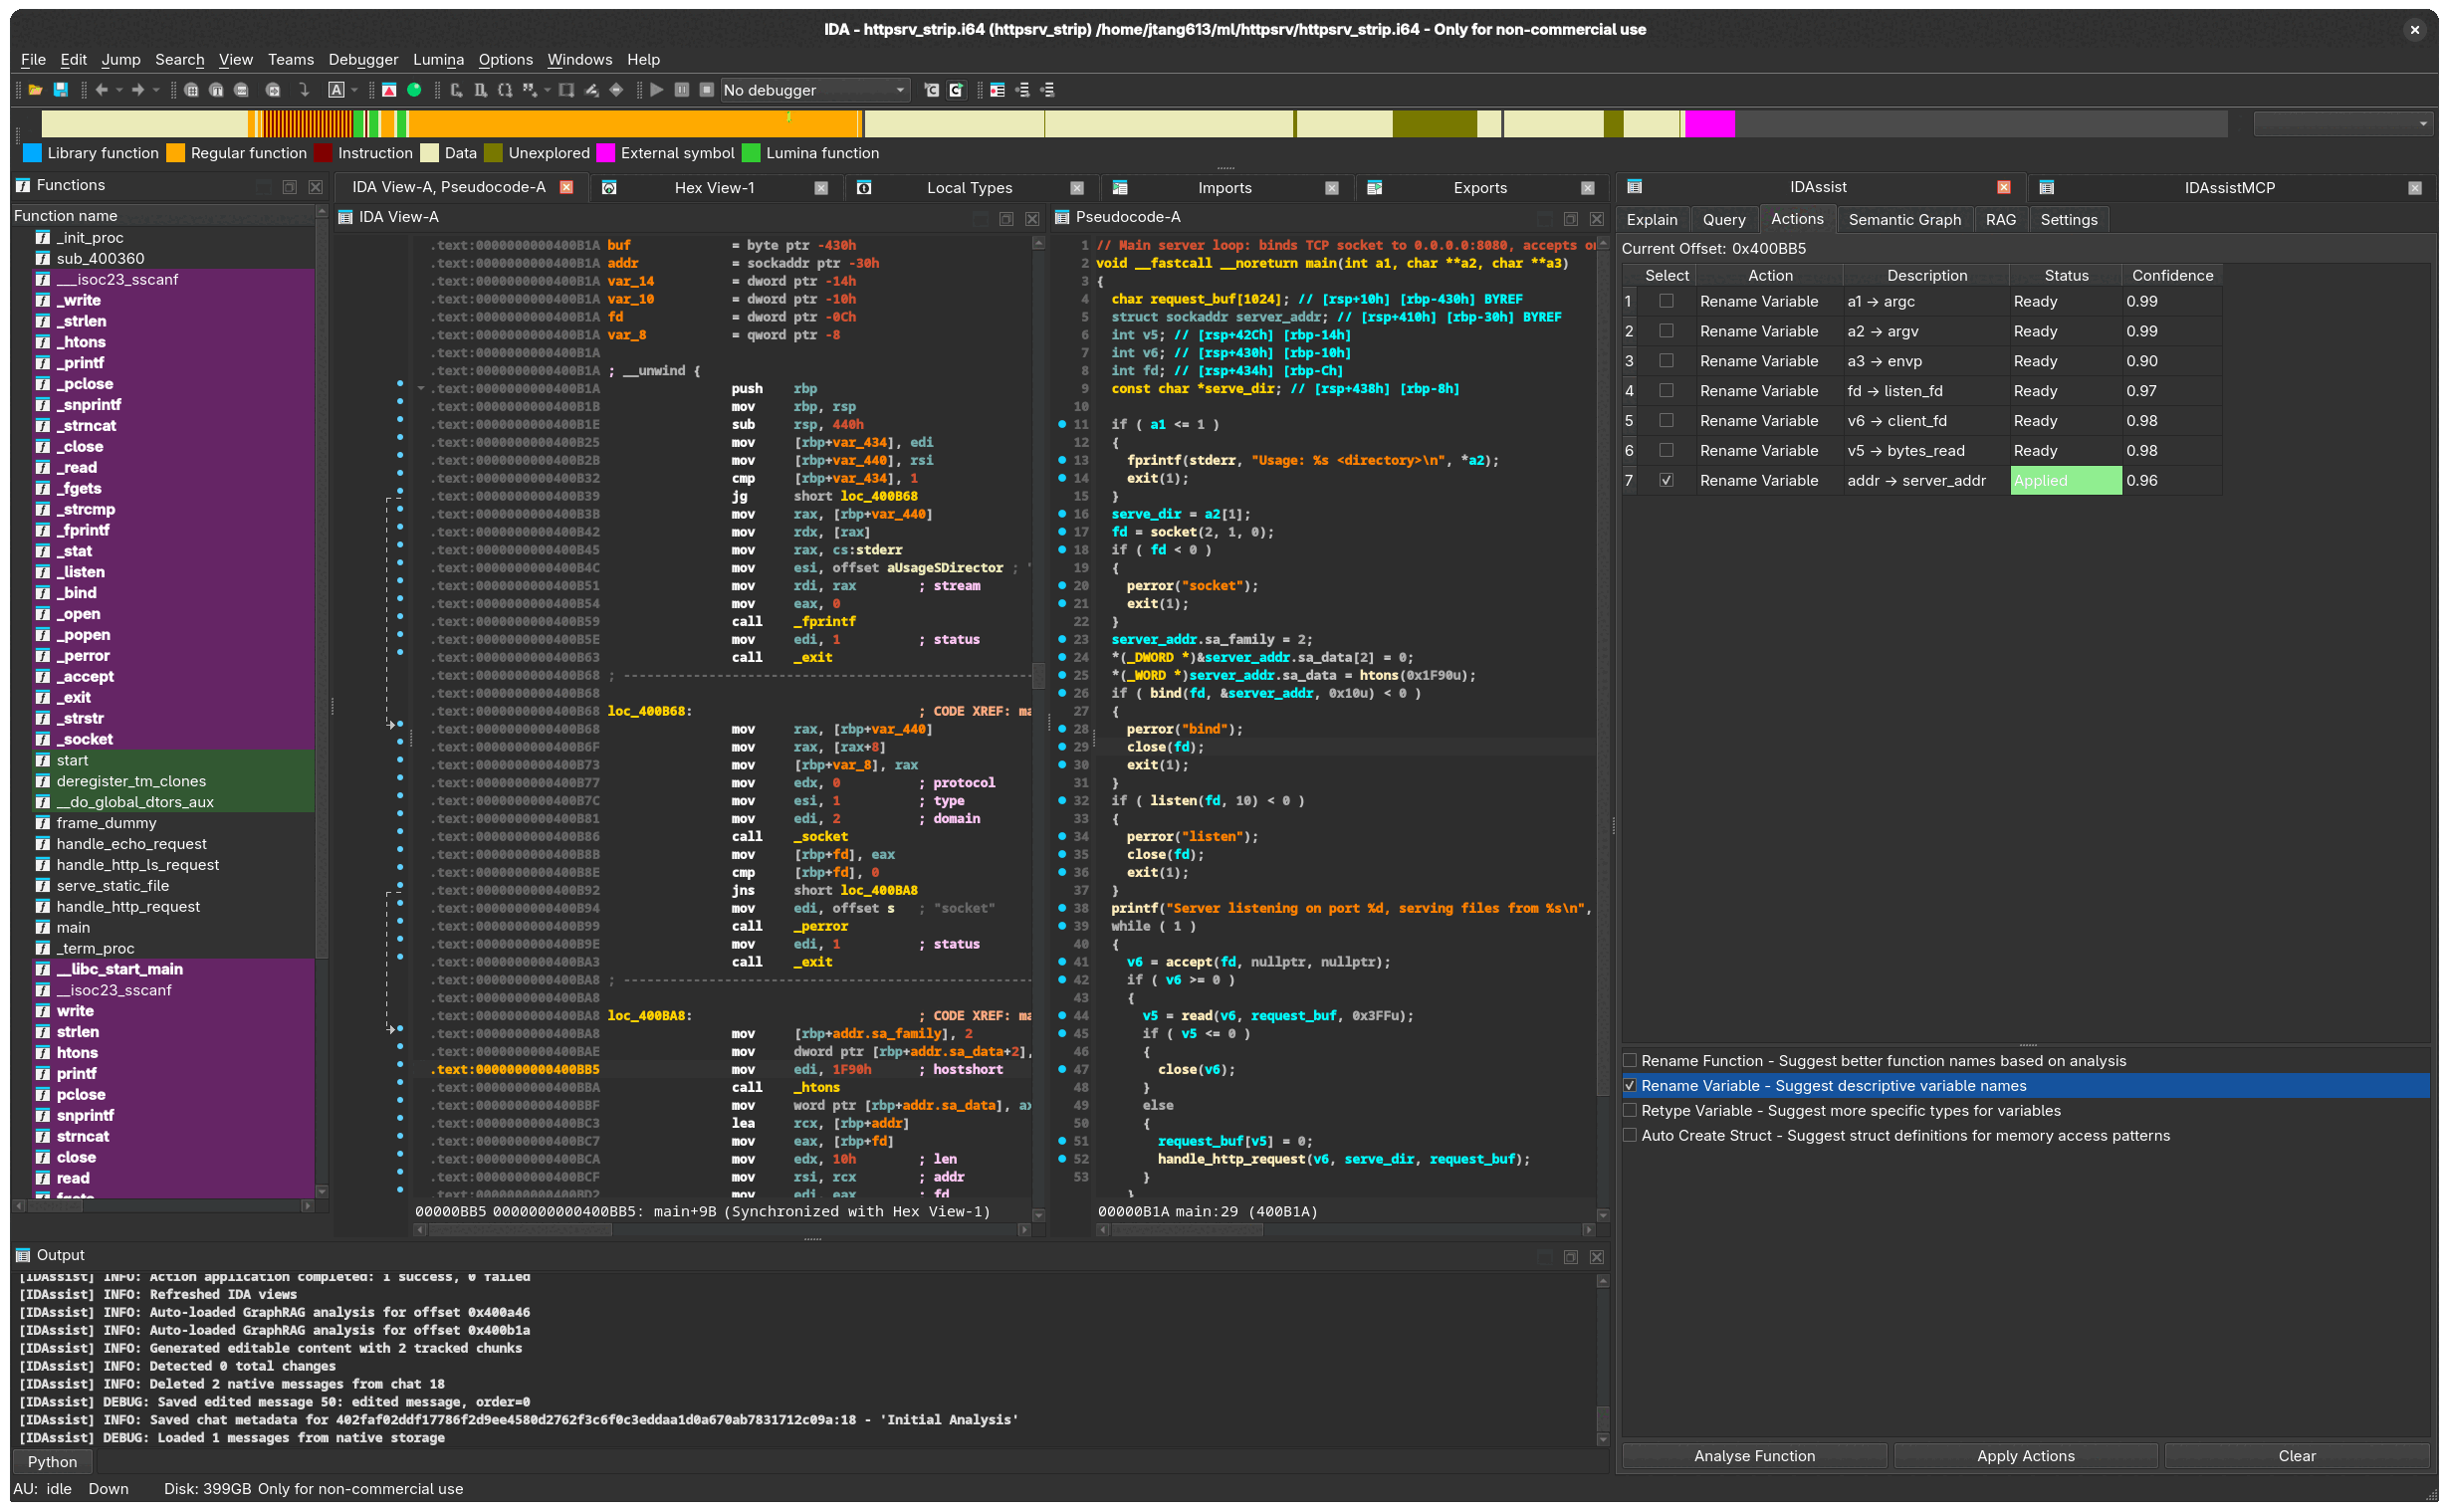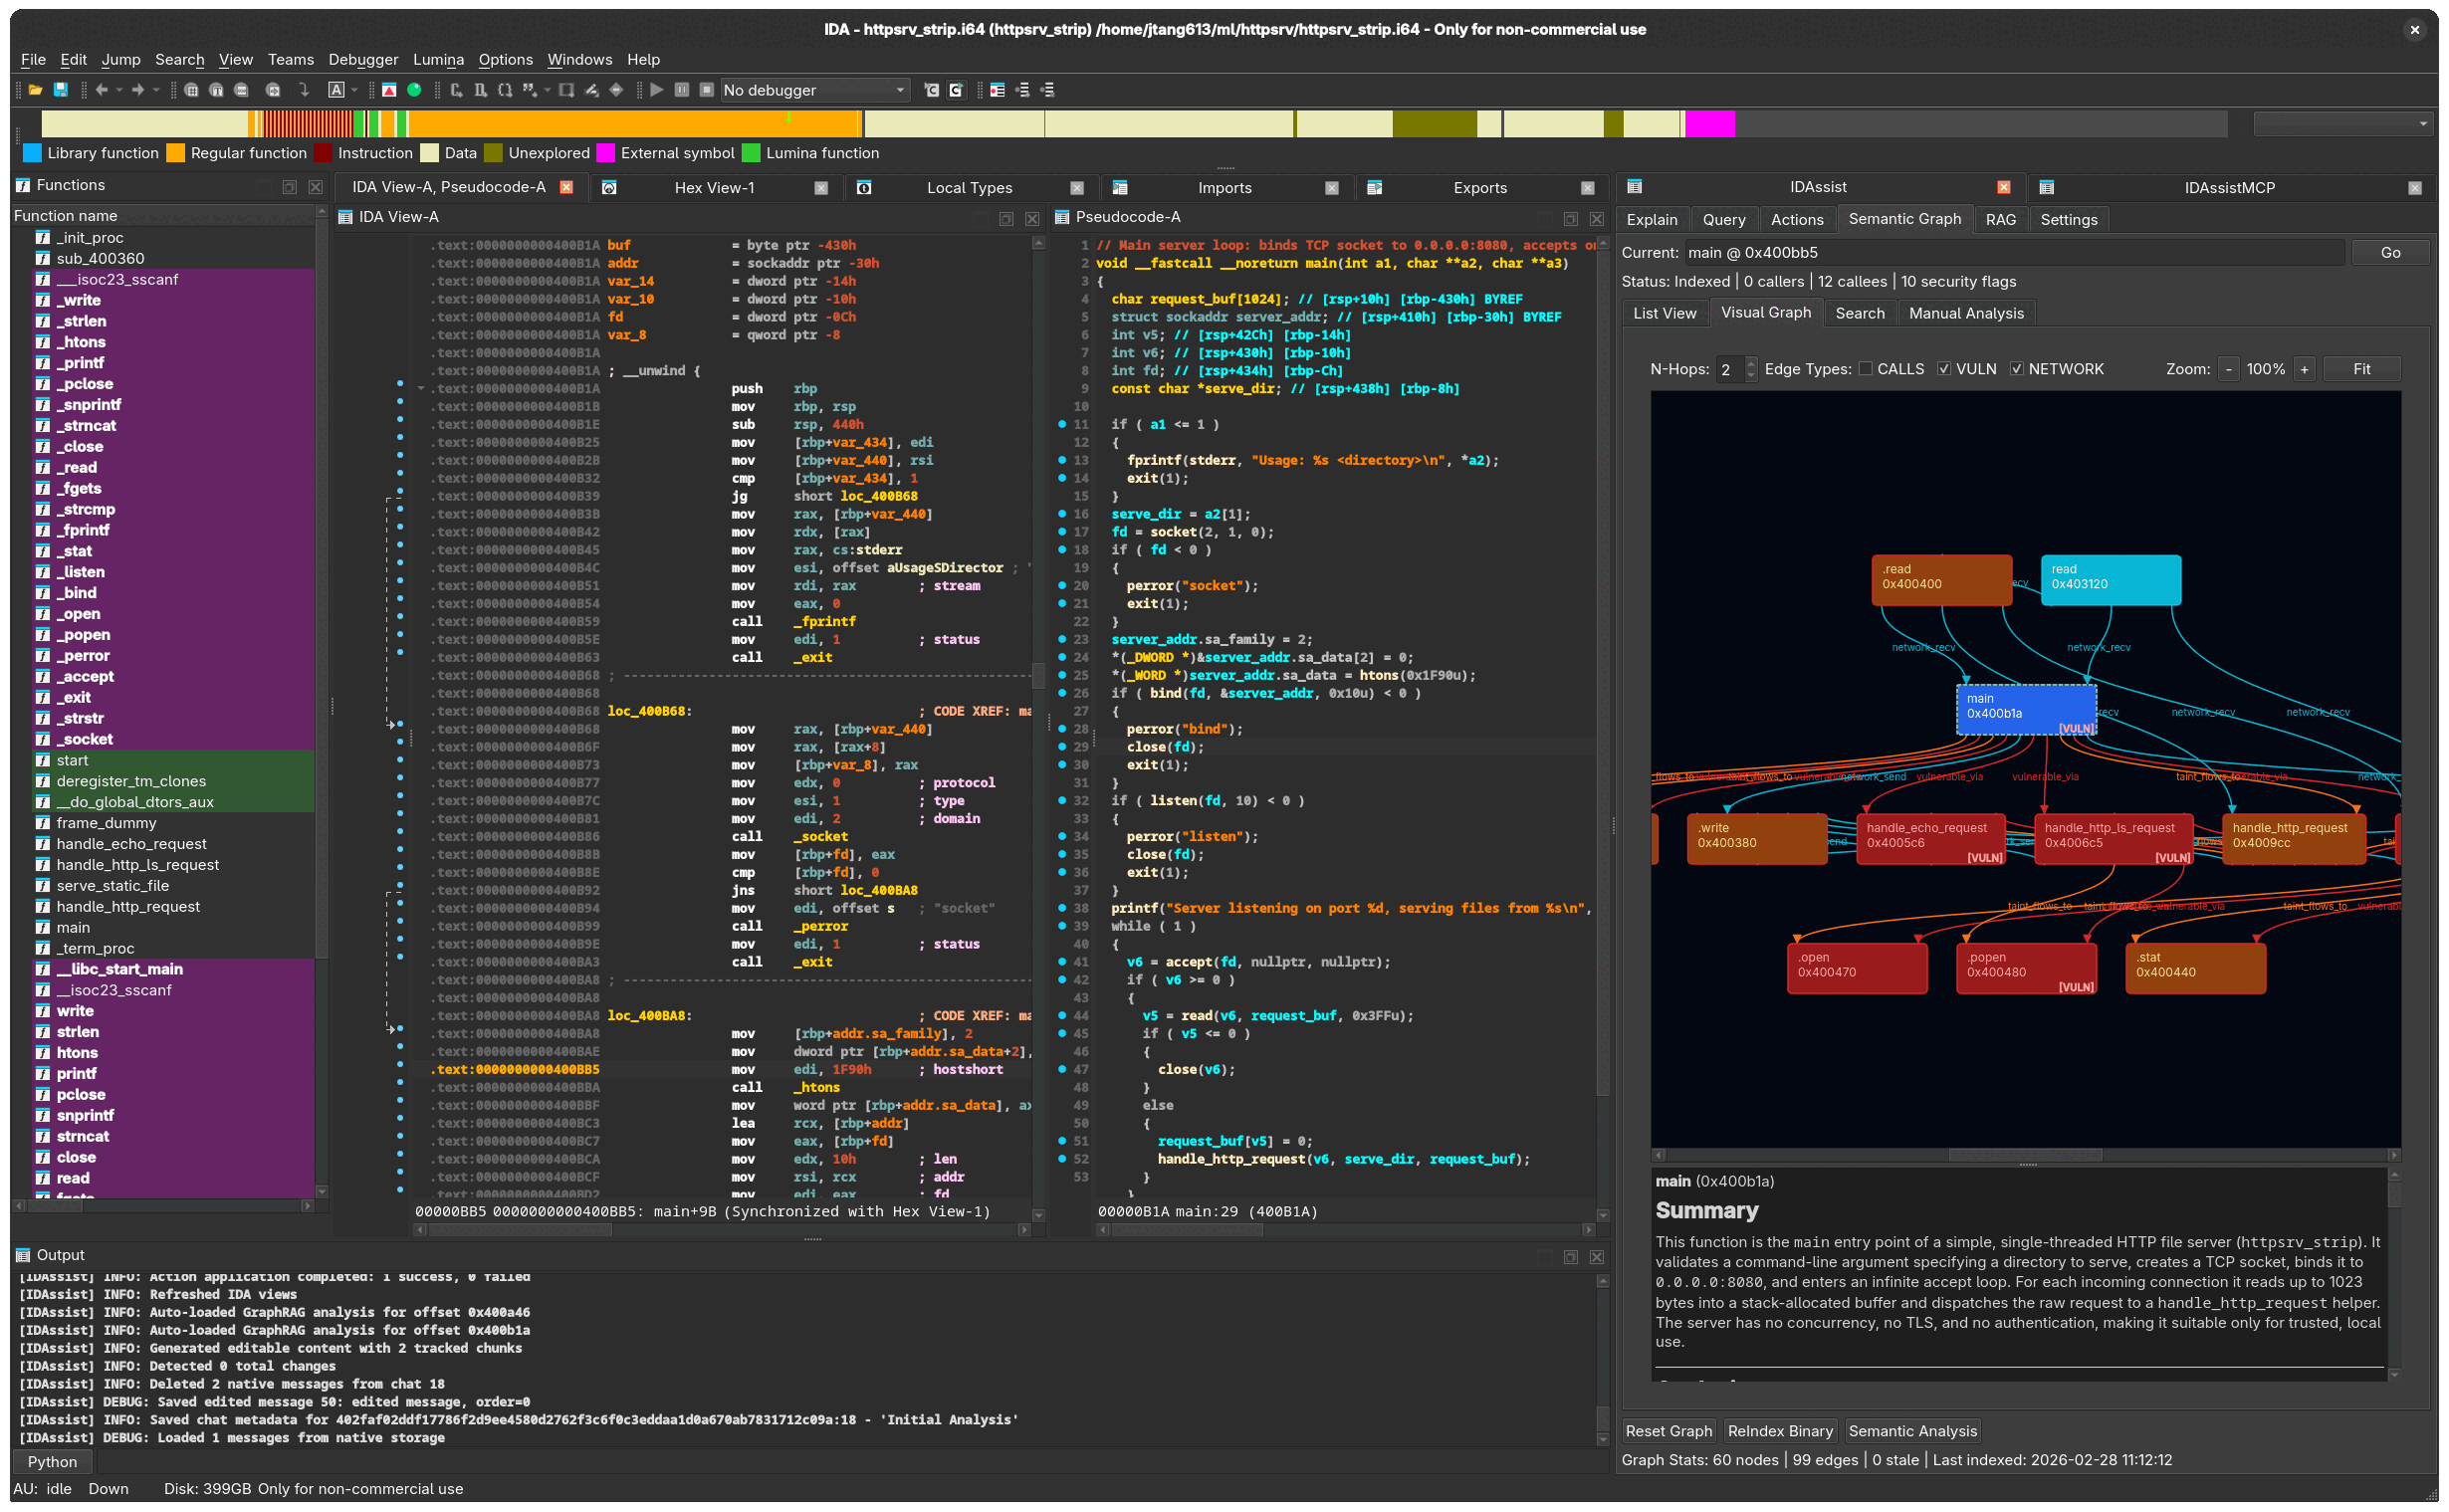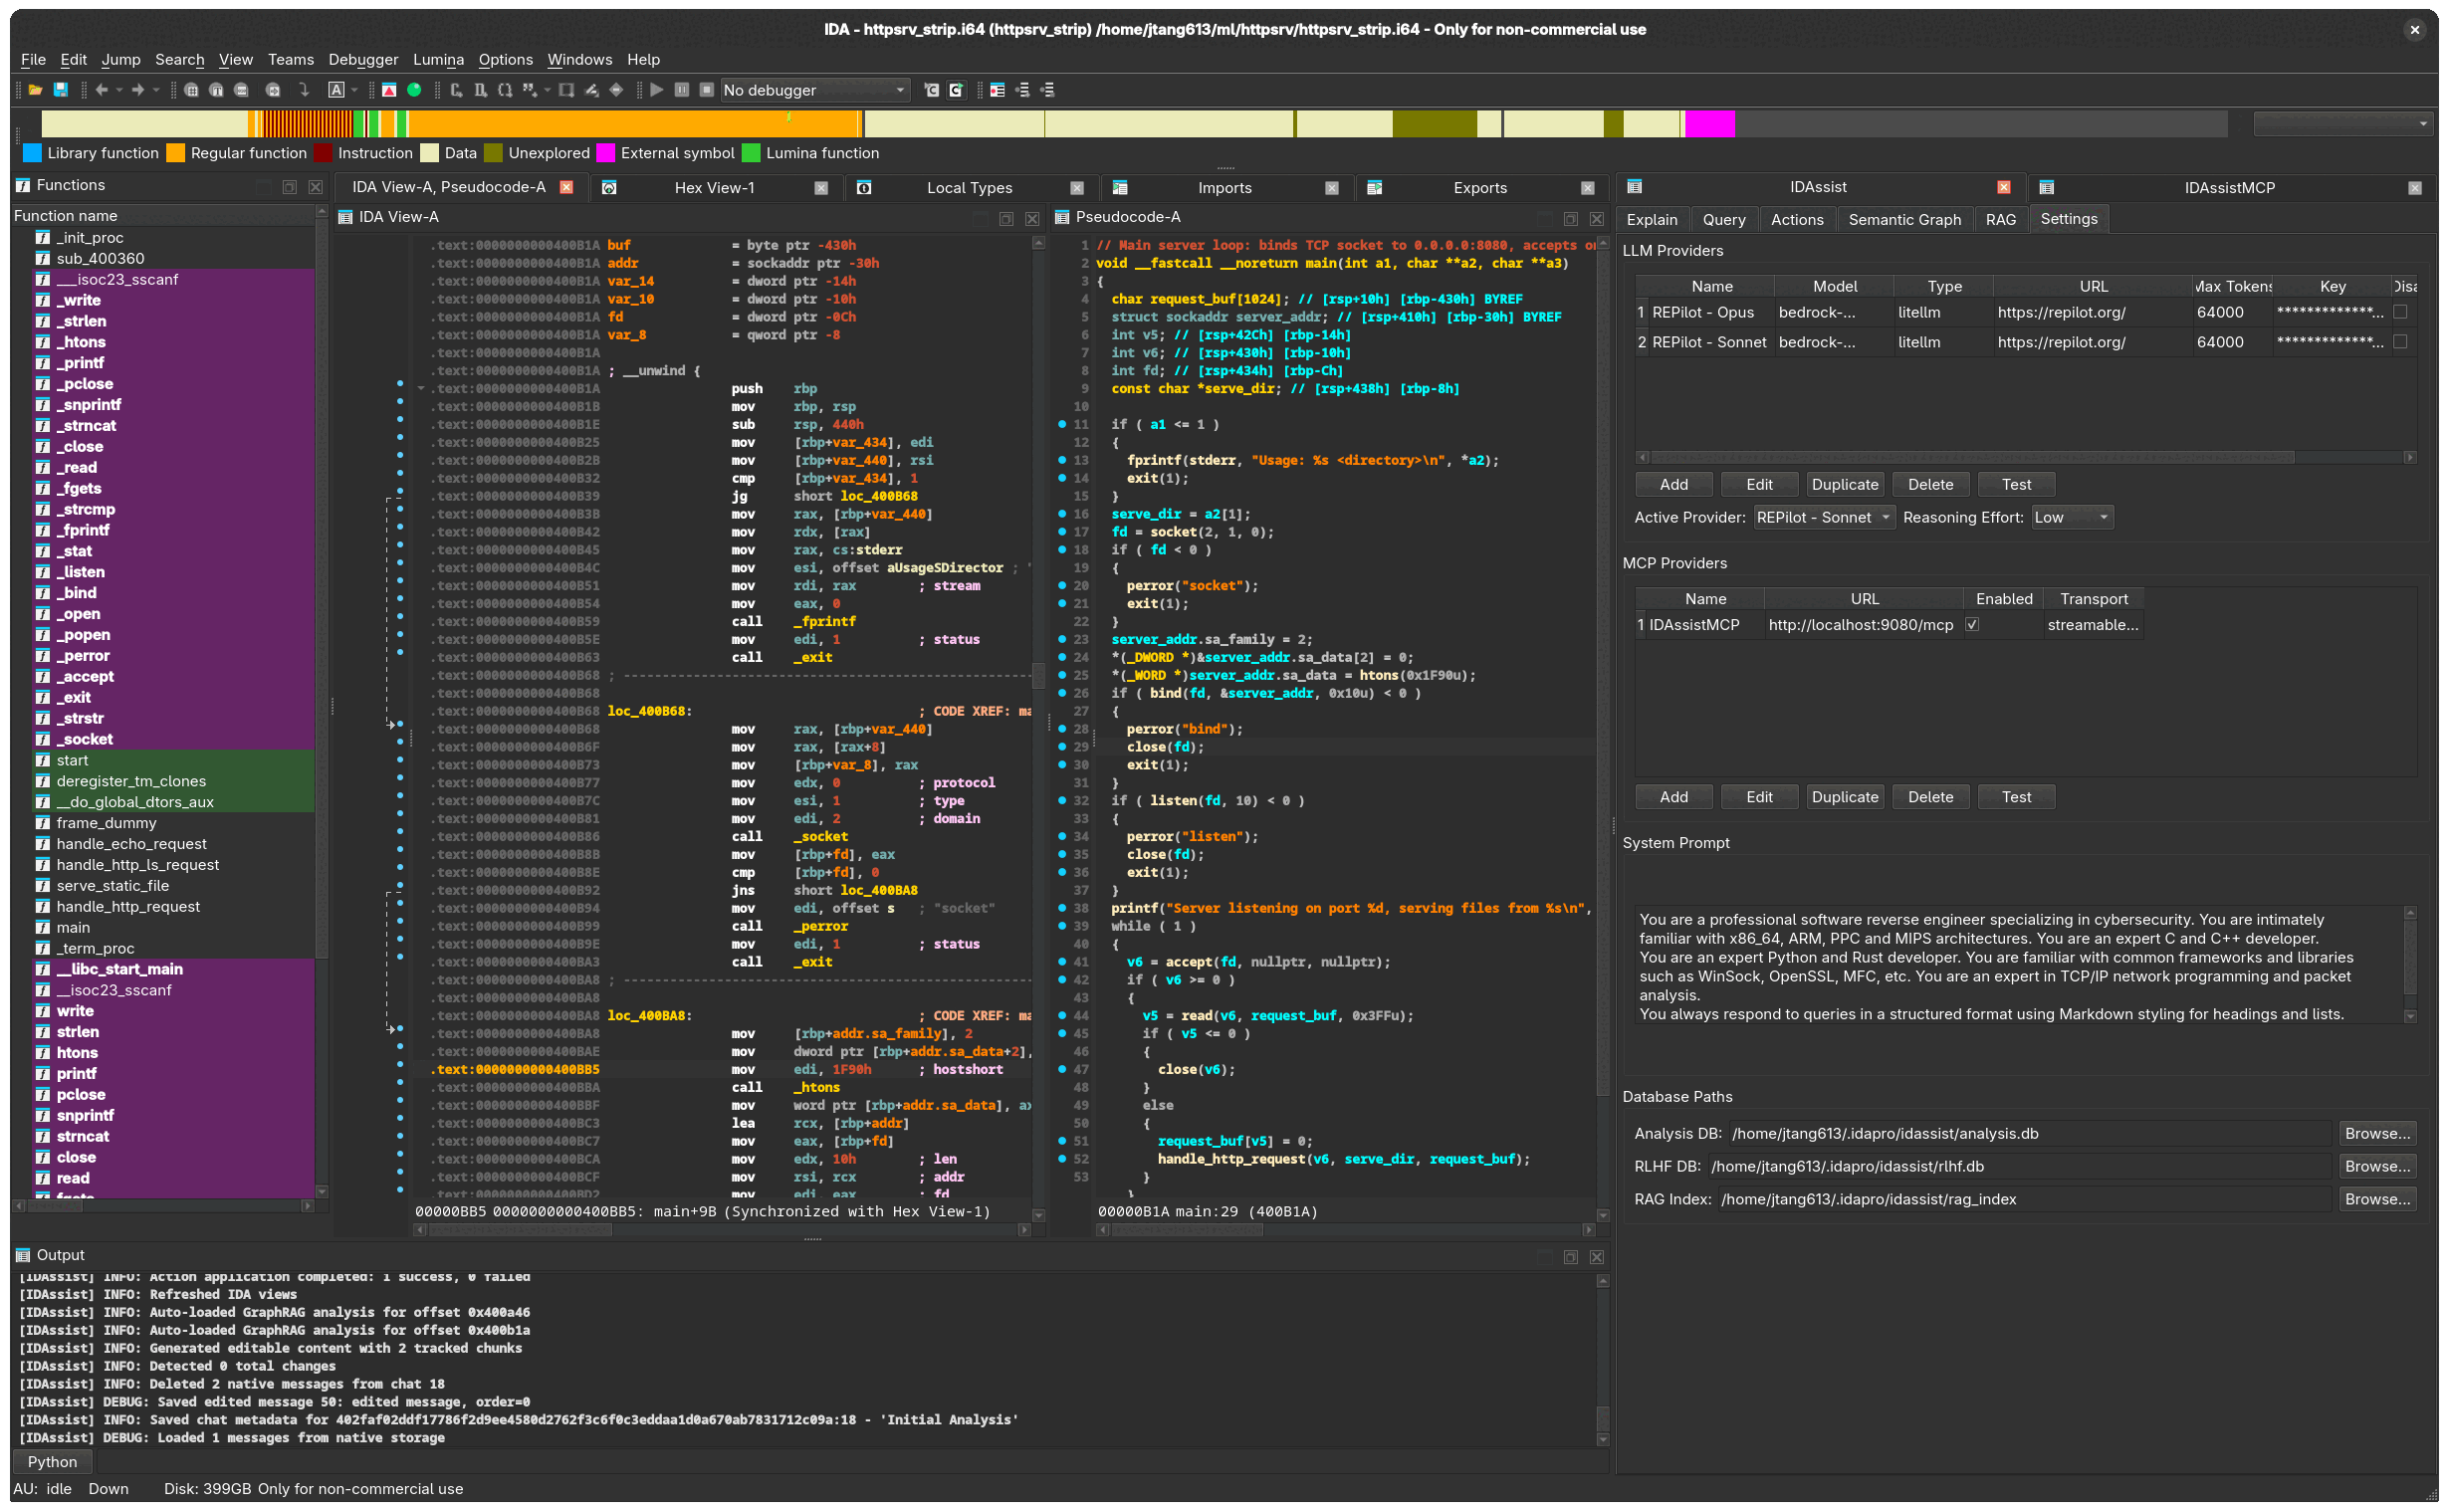 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
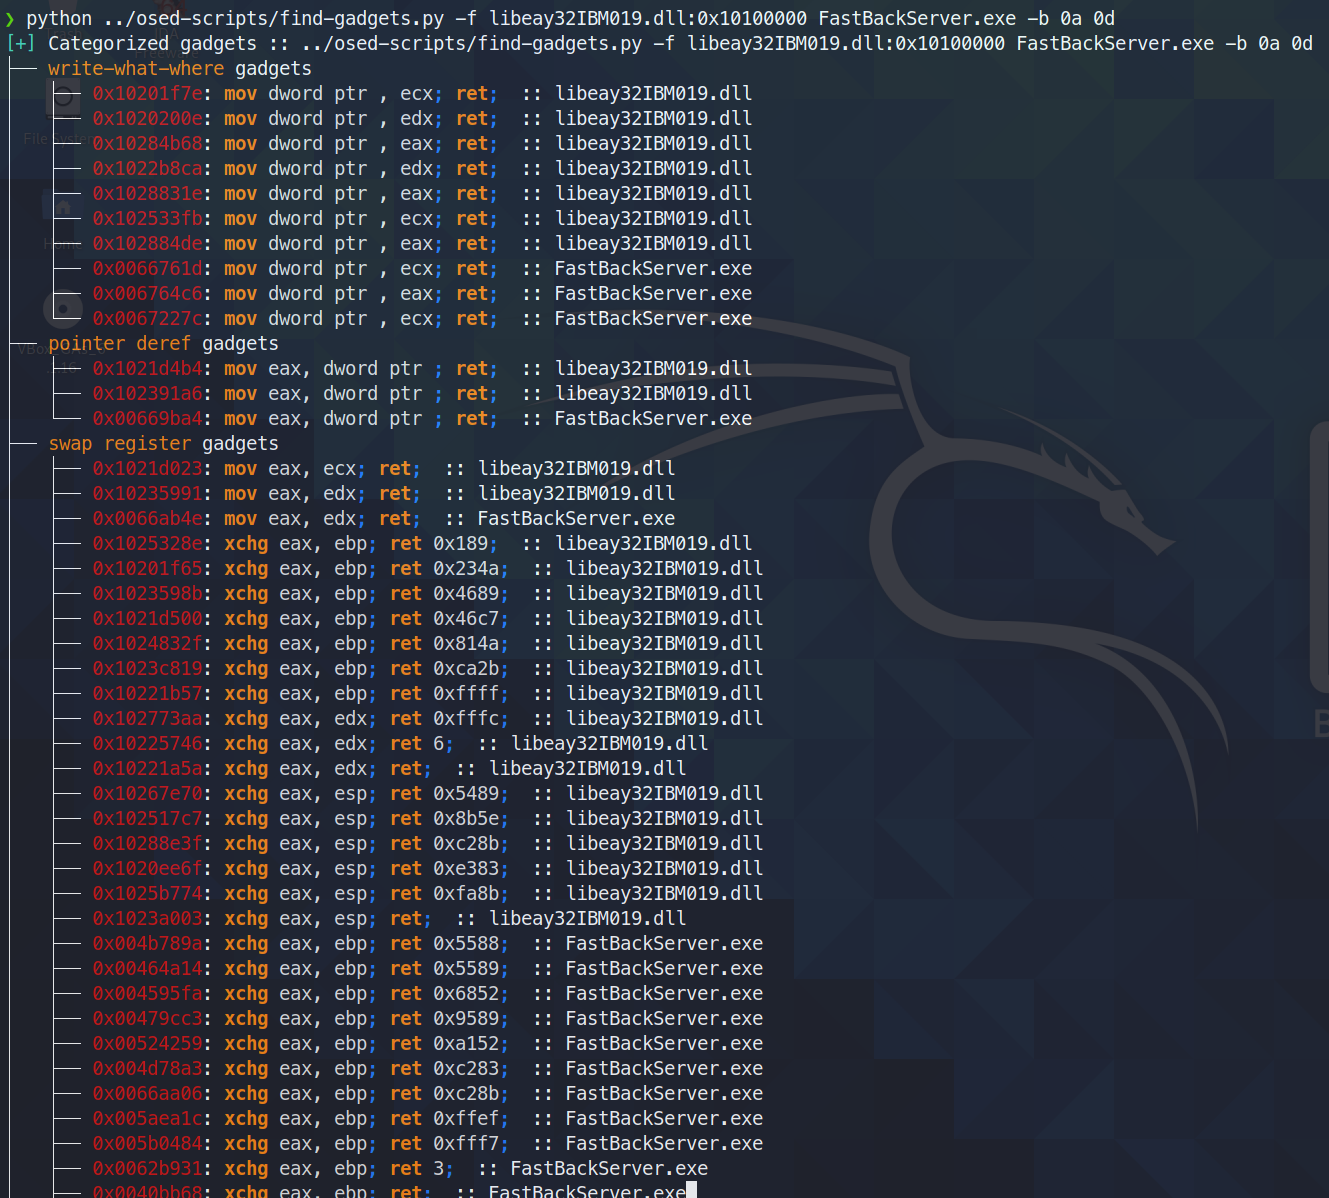 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
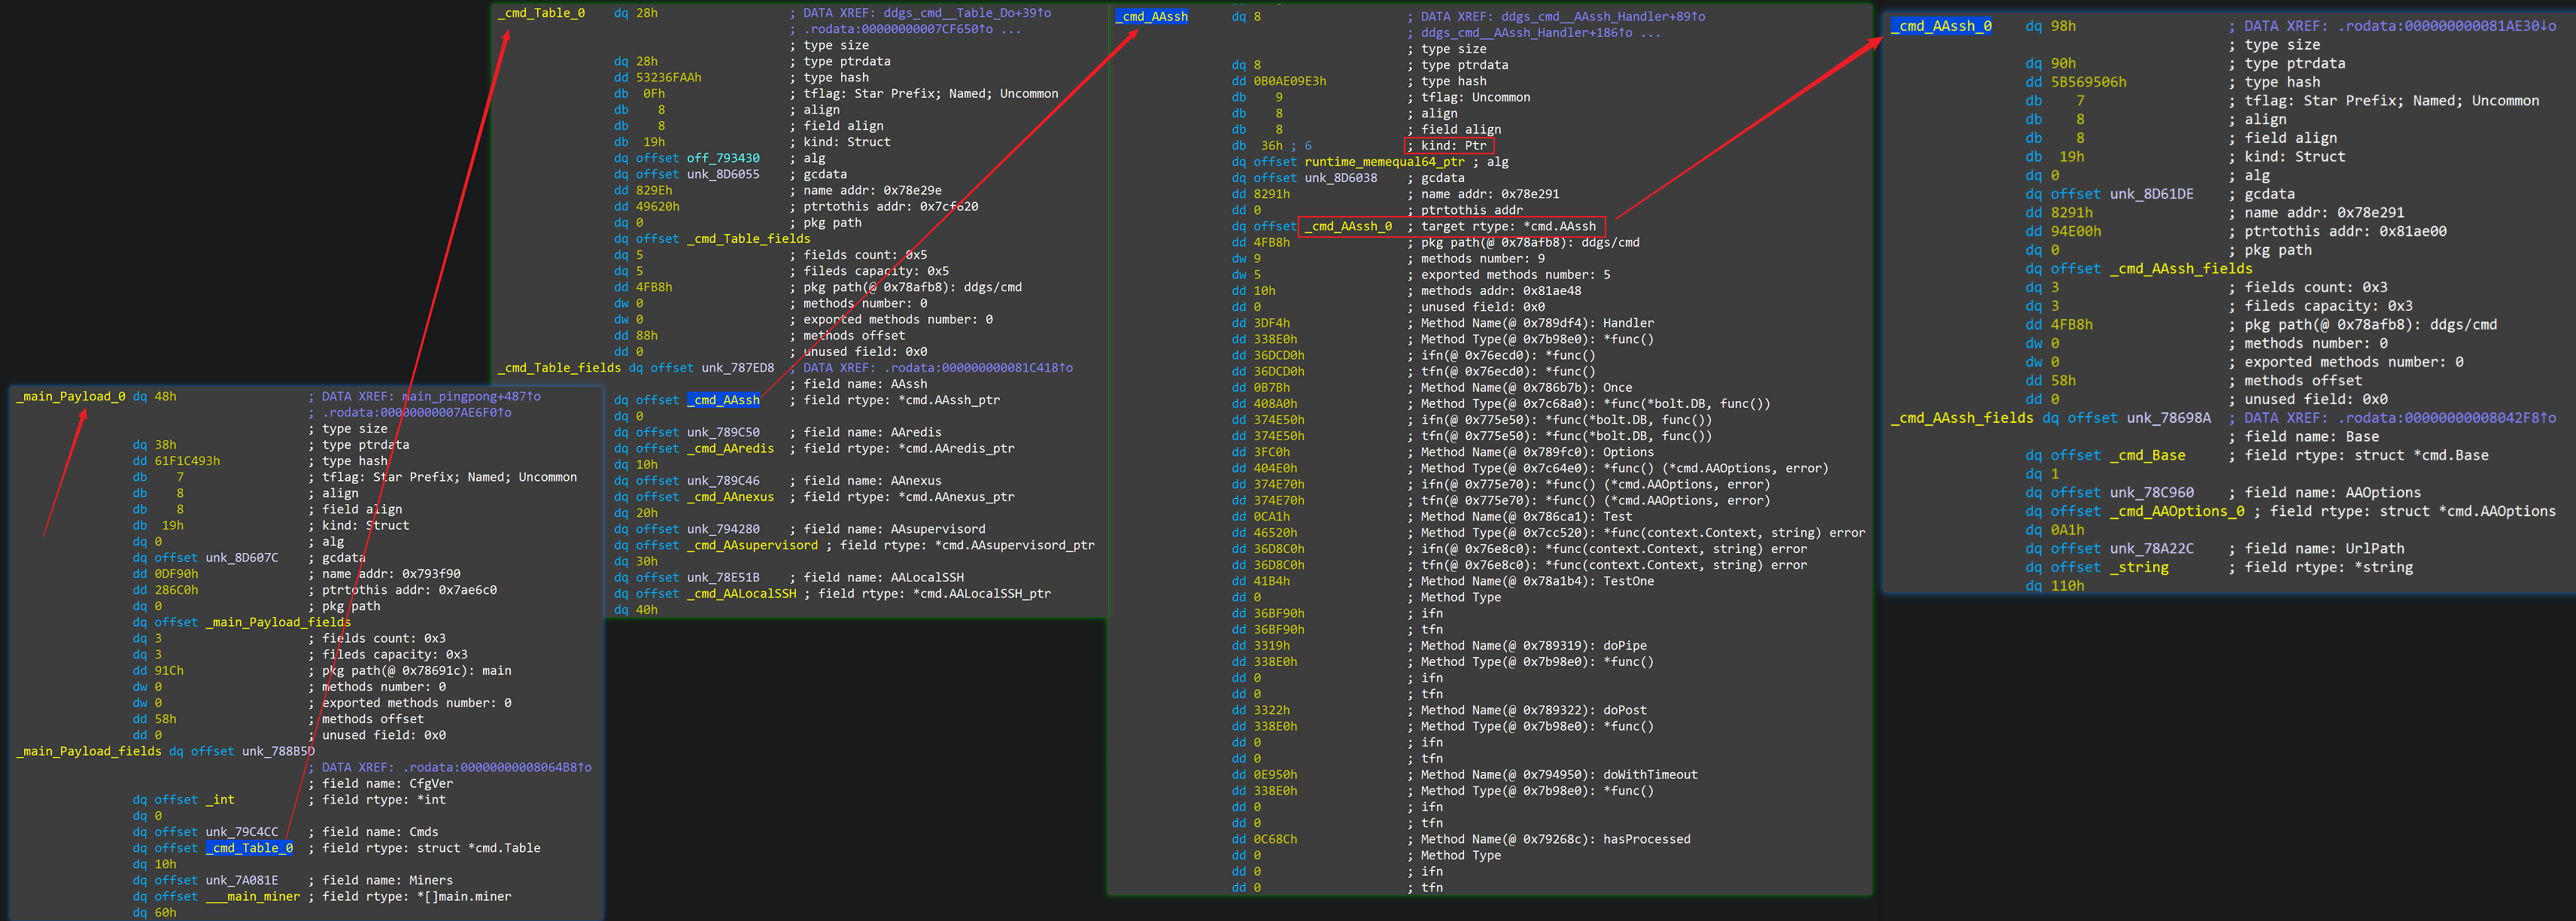 0xjiayu/go_parser
Yet Another Golang binary parser for IDAPro
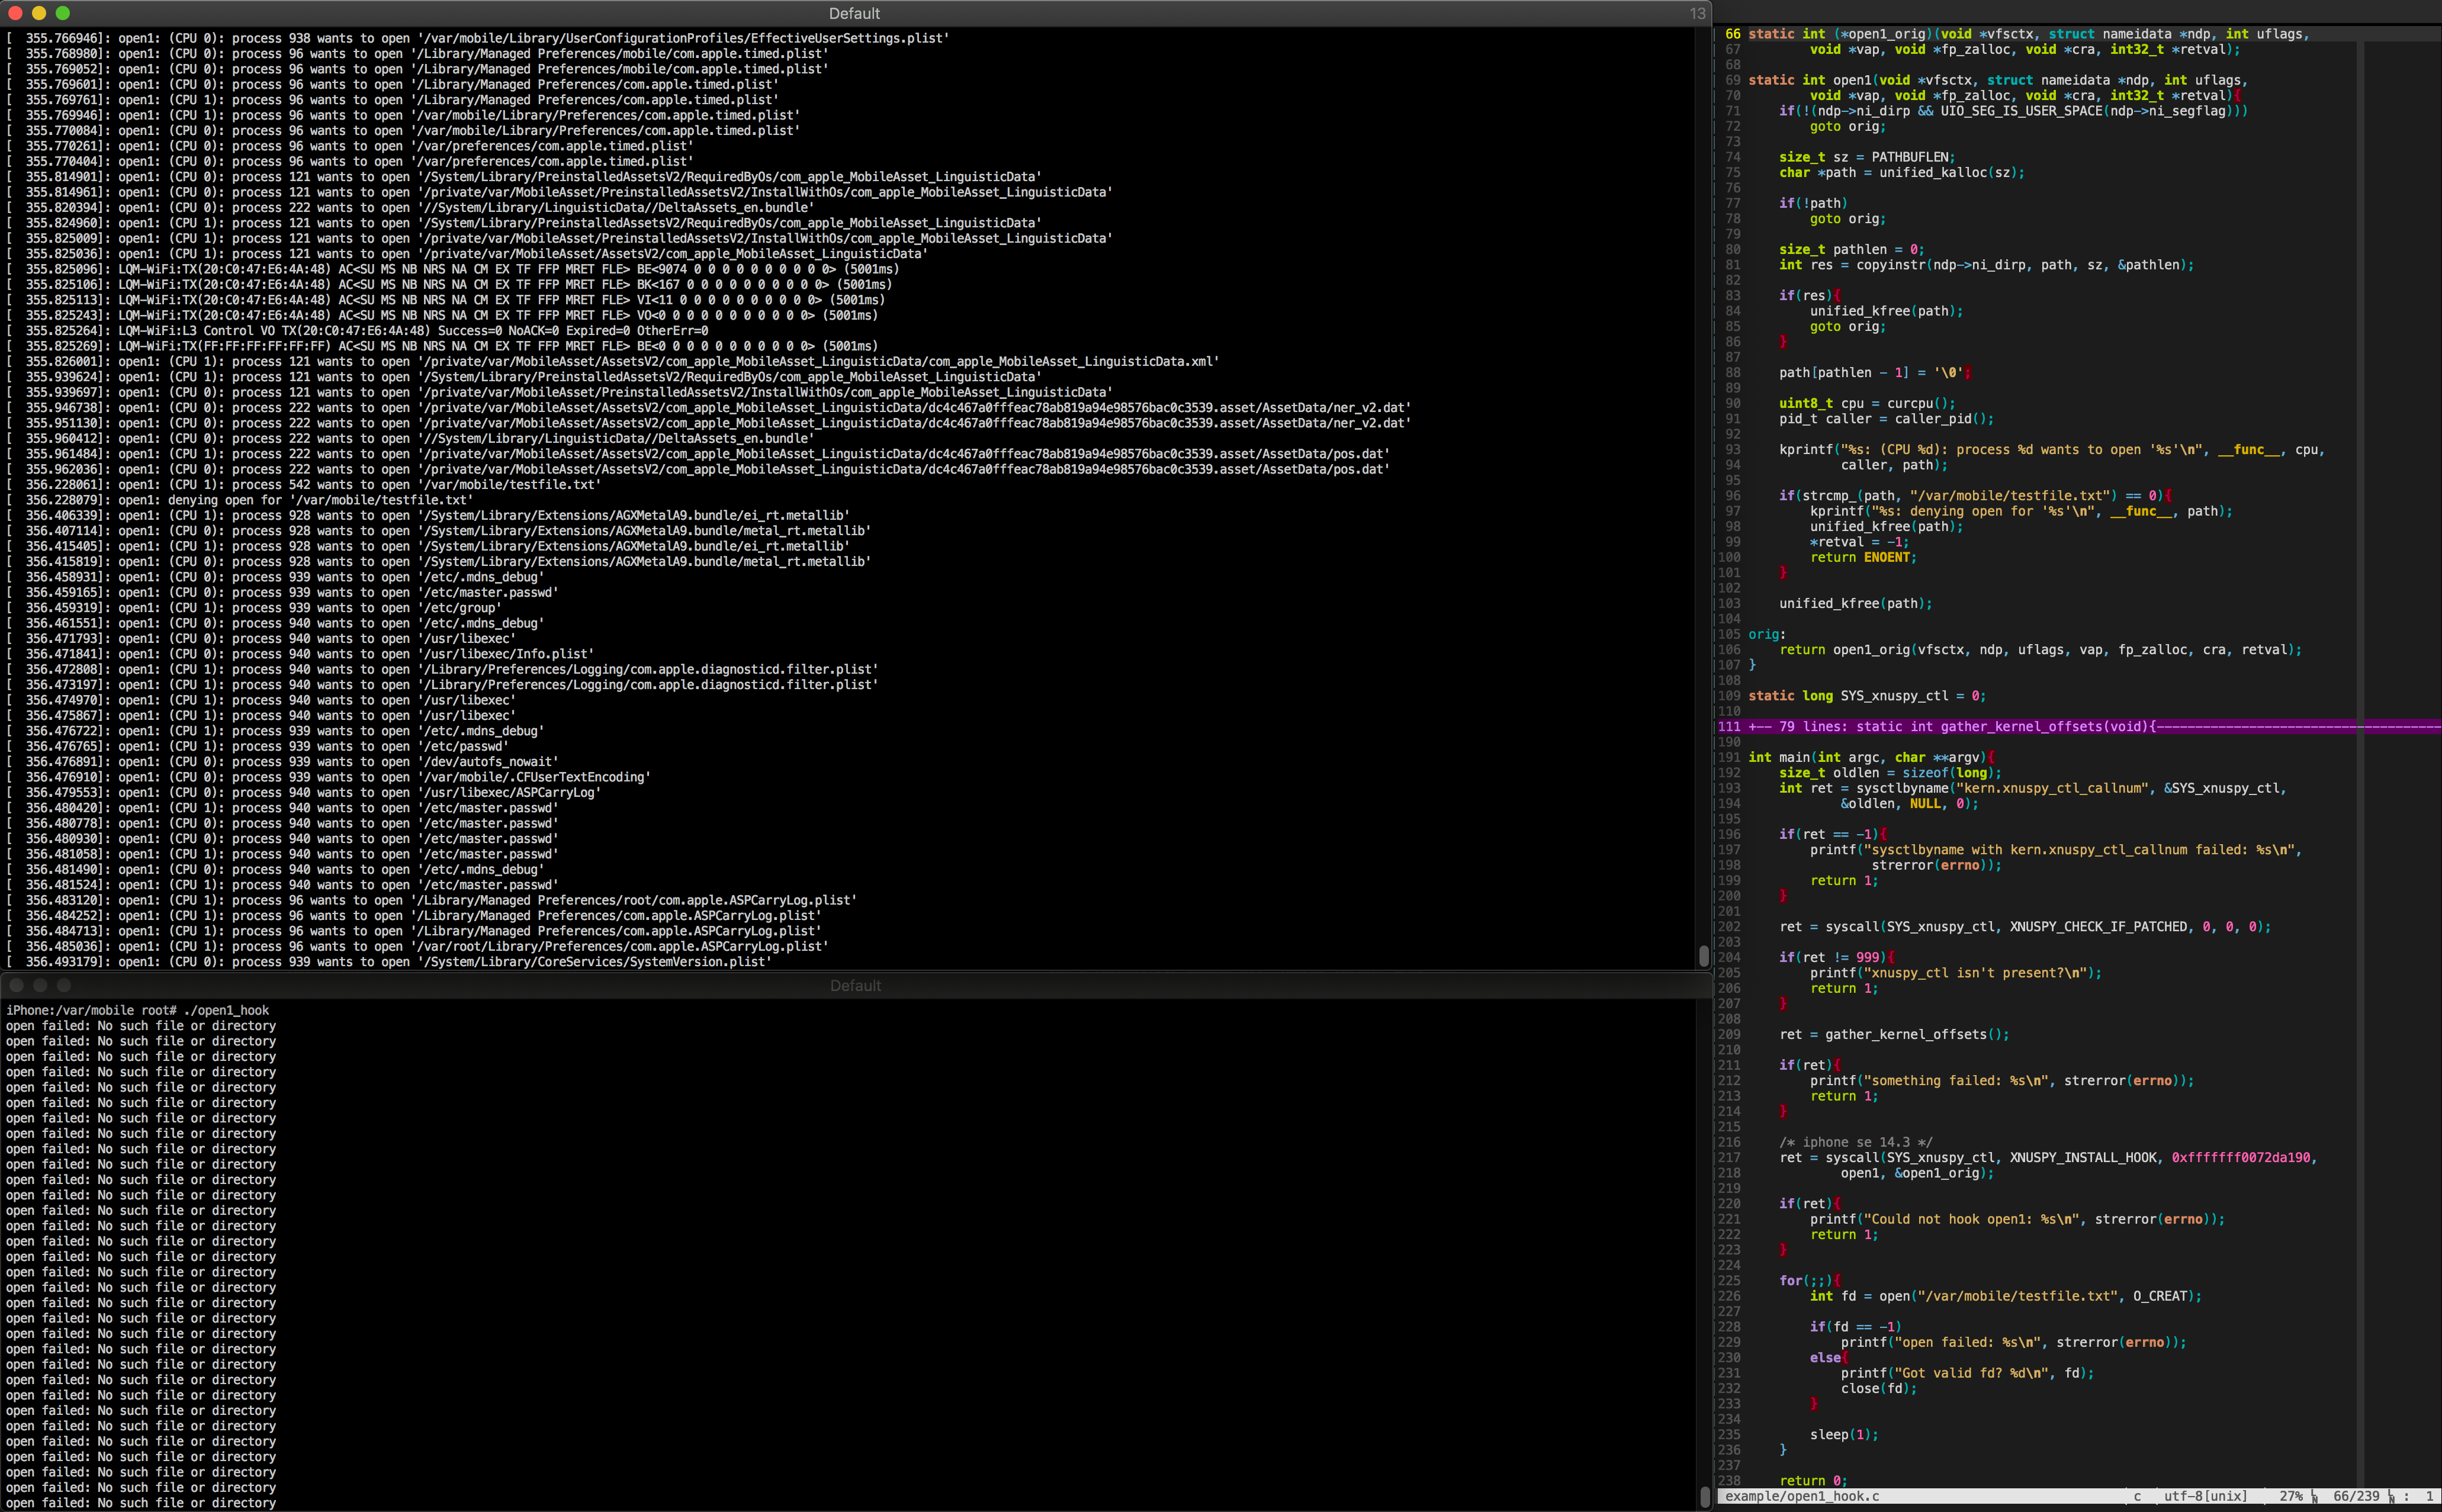 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
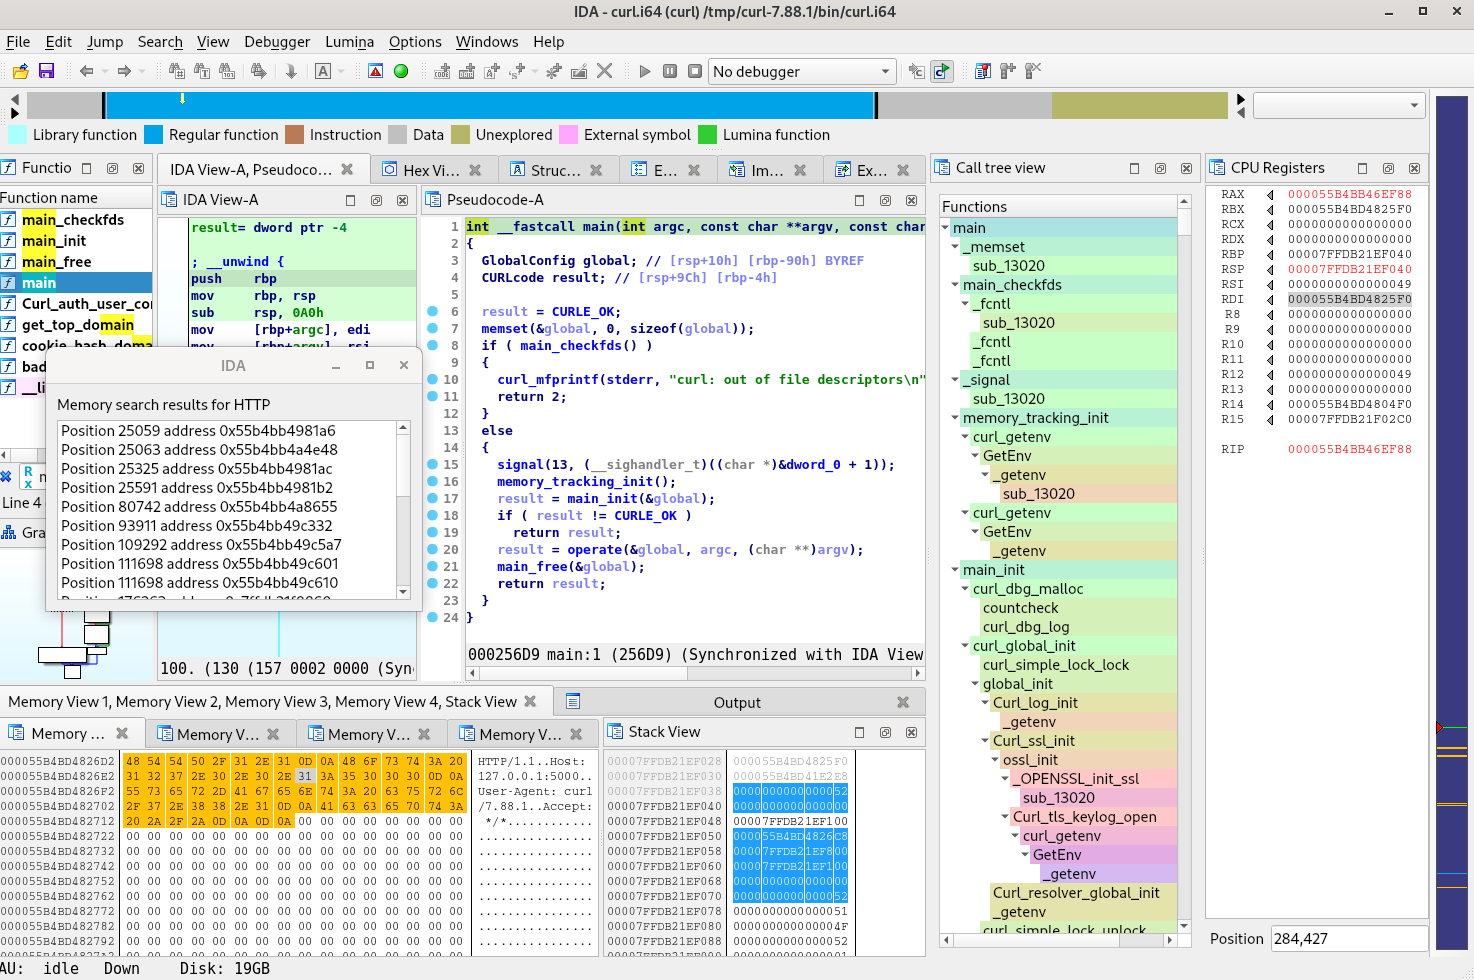 synacktiv/frinet
Frida-based tracer for easier reverse-engineering on Android, iOS, Linux, Windows and most related architectures.
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
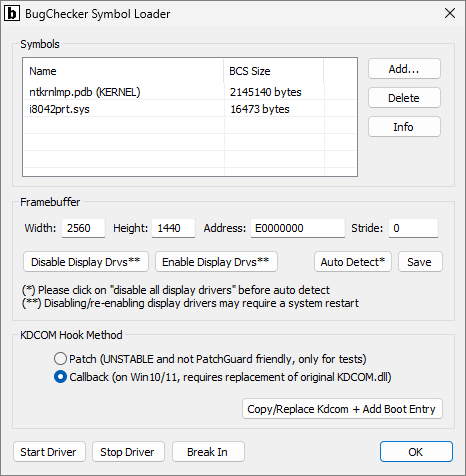 vitoplantamura/bugchecker
SoftICE-like kernel debugger for Windows 11
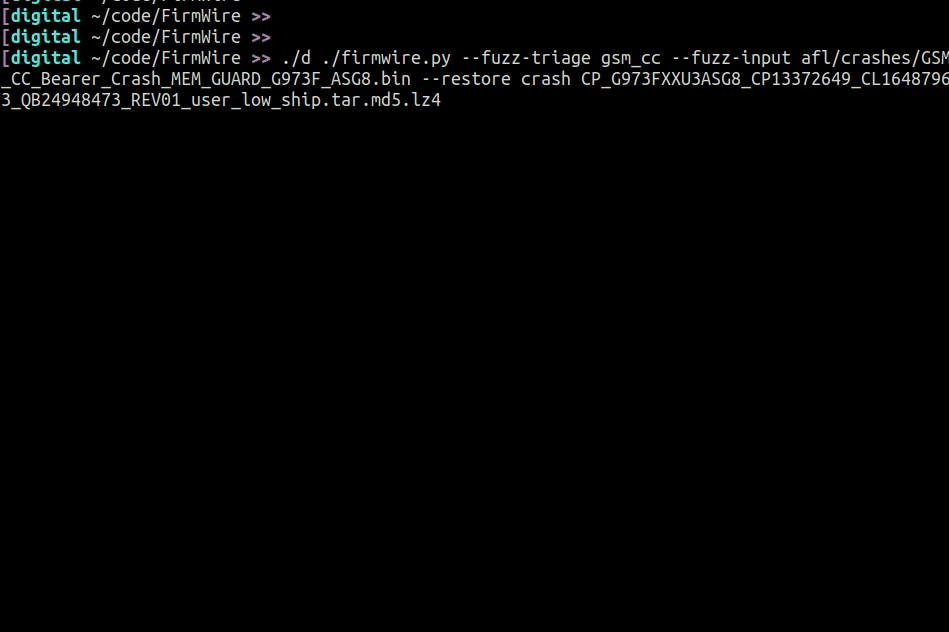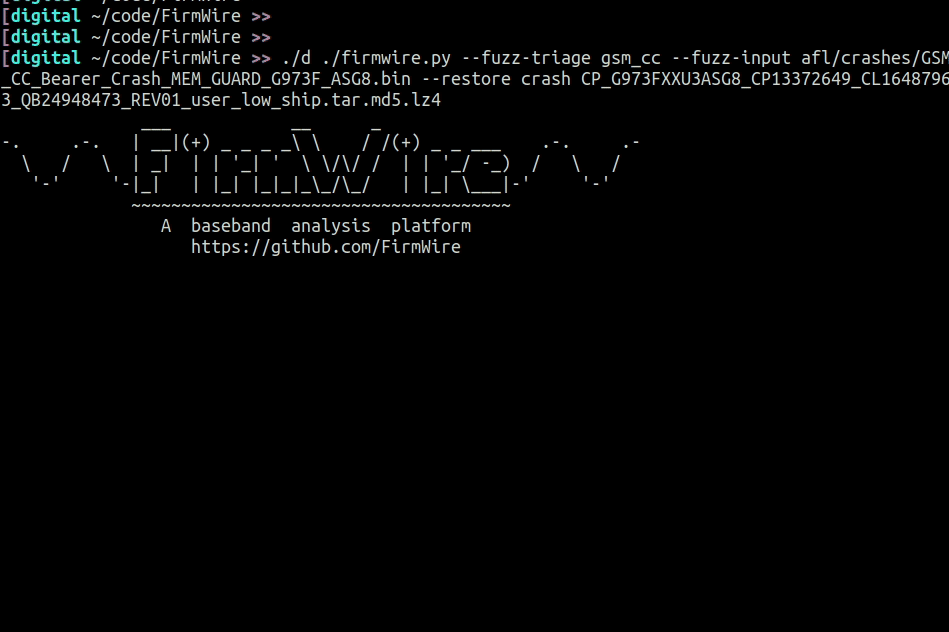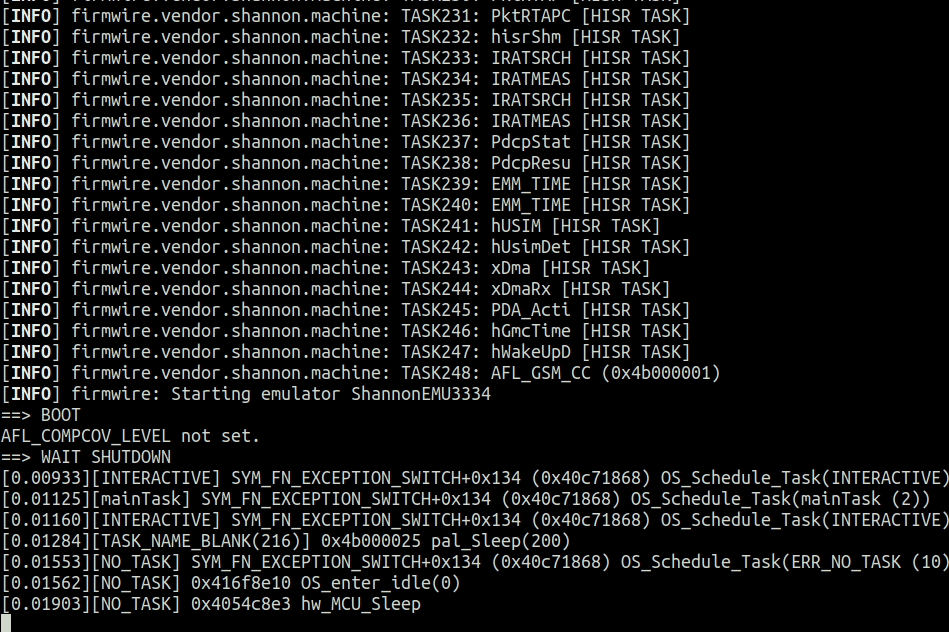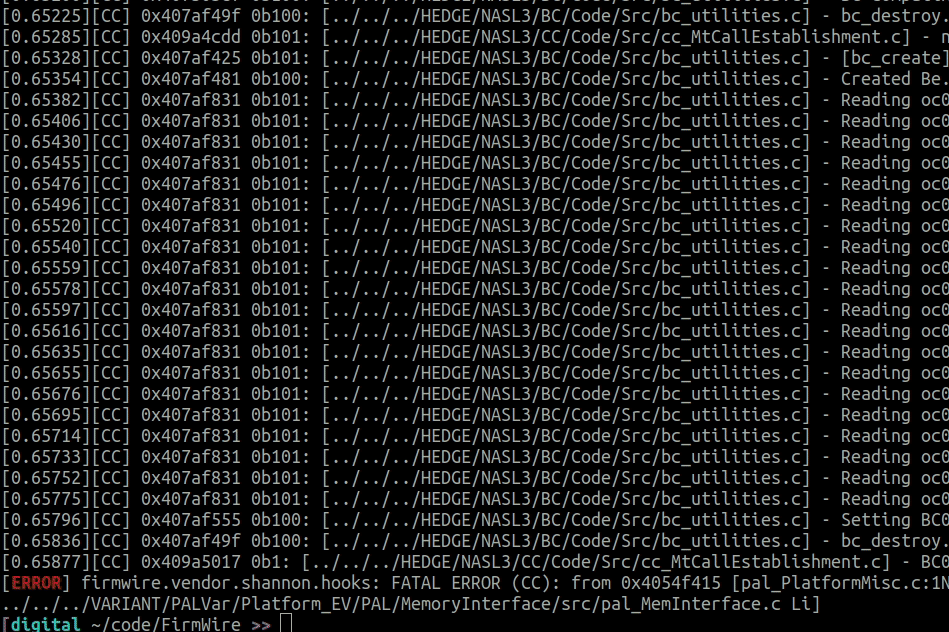 firmwire/firmwire
FirmWire is a full-system baseband firmware emulation platform for fuzzing, debugging, and root-cause analysis of smartphone baseband firmwares