
bytecode-viewer
 konloch/bytecode-viewer
A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)
android-securitybinary-analysiscode-analysis+6
15.7k
konloch/bytecode-viewerA Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)
 lauriewired/ghidramcp
MCP Server for Ghidra
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 kevoreilly/capev2
Malware Configuration And Payload Extraction
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
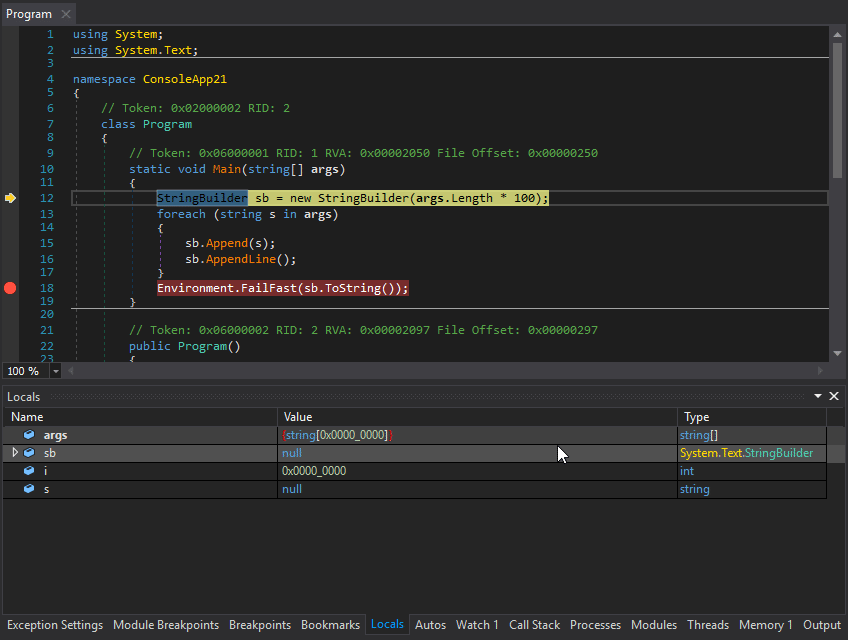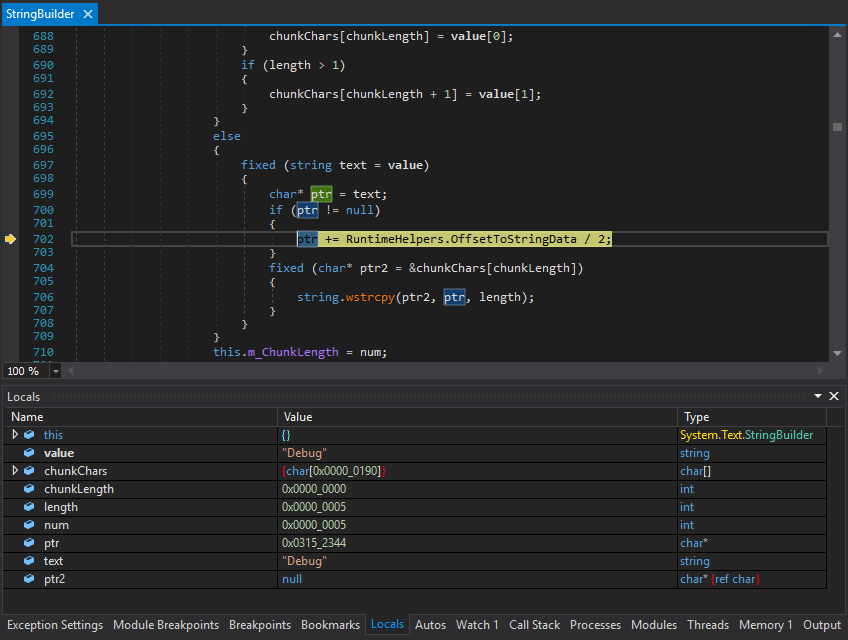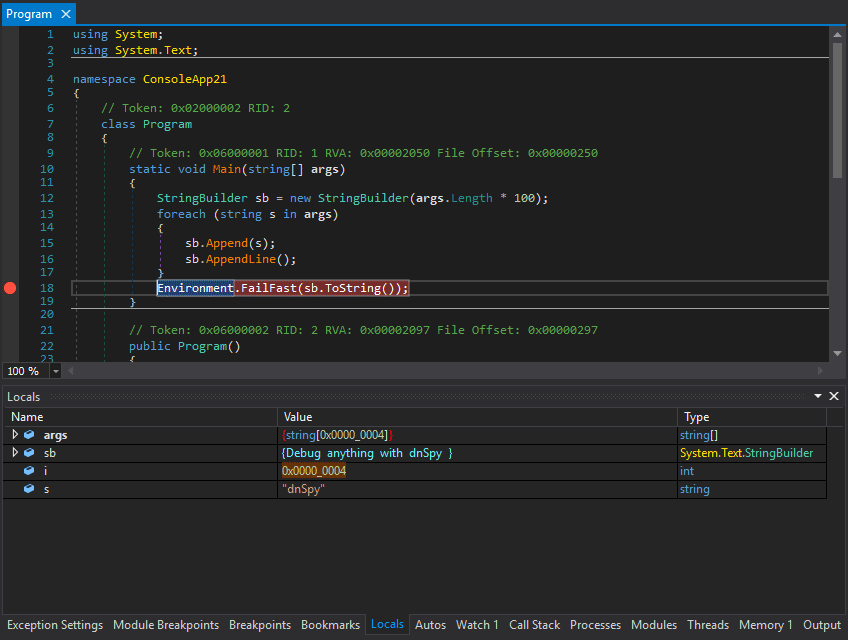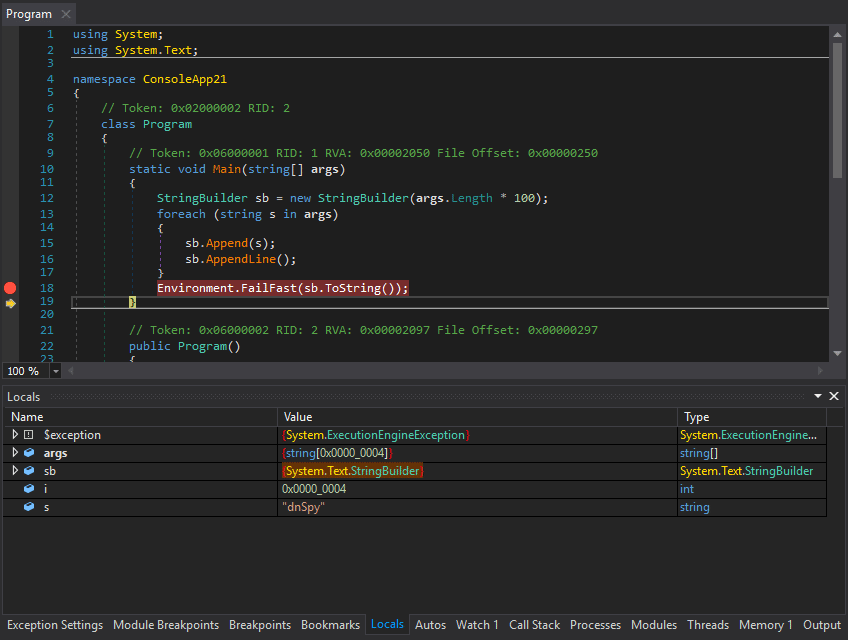 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
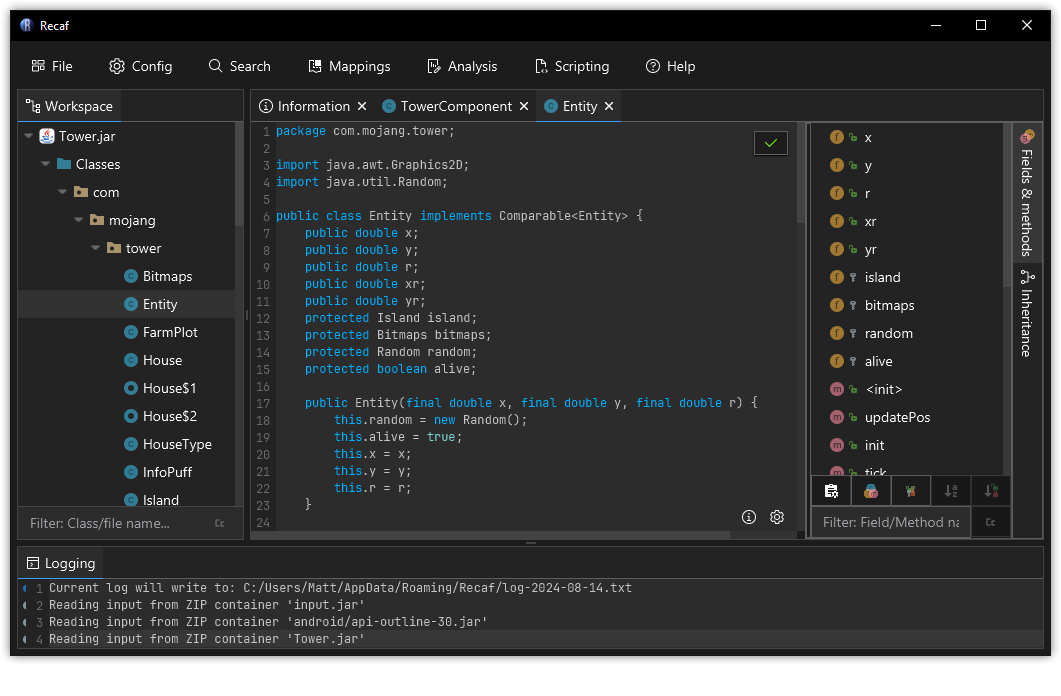
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 zrax/pycdc
C++ python bytecode disassembler and decompiler
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 cea-sec/miasm
Reverse engineering framework in Python
 rocky/python-uncompyle6
A cross-version Python bytecode decompiler
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 openocd-org/openocd
Official OpenOCD Read-Only Mirror (no pull requests)