

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
162 results
ctxdebug preview

ctxdebug

GitHubddudle/ctxdebug

MCP-powered reverse engineering platform connecting WinDbg, IDA Pro & x64dbg with 160+ AI-accessible debugging and analysis tools.

ai-assisted-reversingbinary-analysisdebuggers+4
29
1 month ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…

debuggersdigital-forensicsdisk-forensics+7
253 months ago
ImHex preview

ImHex

GitHubwerwolv/imhex

🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

ai-assisted-reversingbinary-analysisbinary-exploitation+10
55.5k15 days ago
dnSpy preview

dnSpy

GitHubdnspyex/dnspy

Unofficial revival of the well known .NET debugger and assembly editor, dnSpy

ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.3k6 days ago
flare-vm preview

flare-vm

GitHubmandiant/flare-vm

A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…

binary-analysisdebuggersdigital-forensics+10
9.2k16 days ago
jshookmcp preview

jshookmcp

GitHubvmoranv/jshookmcp

A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.

ai-securitybinary-analysisdebuggers+9
2.1k3h 19m ago
frida-gum preview

frida-gum

GitHubfrida/frida-gum

Cross-platform instrumentation and introspection library written in C
binary-analysiscode-analysisdebuggers+6
1.0k17h 22m ago
AllTools preview

AllTools

GitHubzodiacon/alltools

All reasonably stable tools
binary-analysisdebuggersgeneral-purpose-utilities+1
1.5k4 months ago
antispy preview

antispy

GitHubmohuihui/antispy

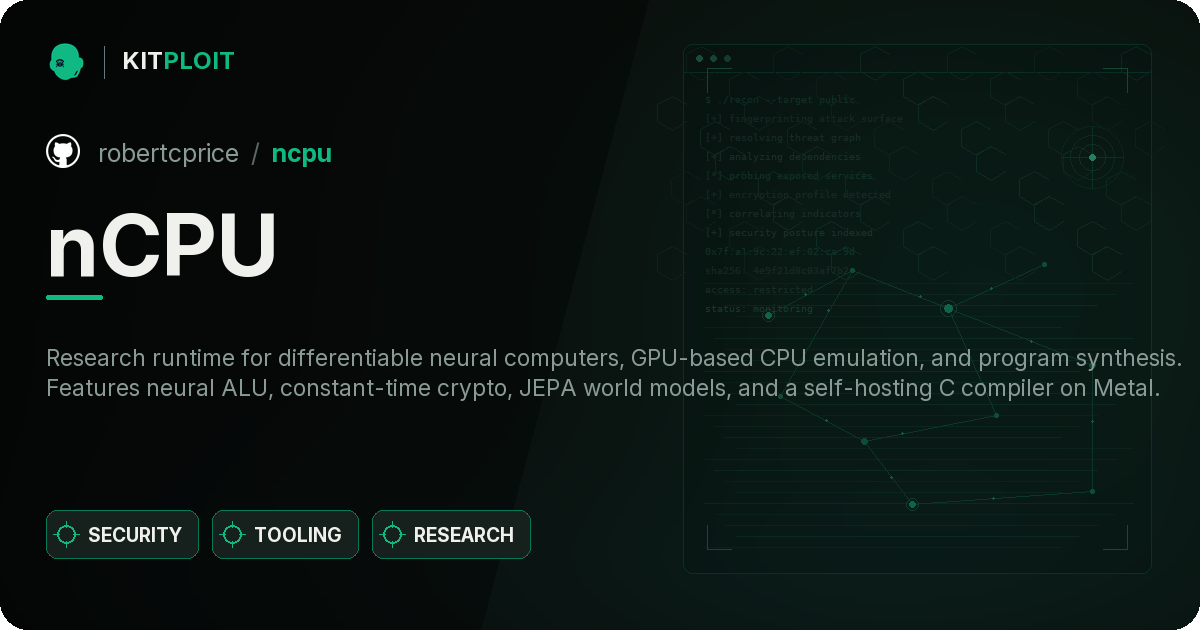
AntiSpy is a free but powerful anti virus and rootkits toolkit.It offers you the ability with the highest privileges that can detect,analyze and…
binary-analysisdebuggersdefensive-tools+3
1.1k5 years ago
nCPU preview

nCPU

GitHubrobertcprice/ncpu

Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…

ai-securitybinary-analysiscryptography+8
6633 months ago
PyMemoryEditor preview

PyMemoryEditor

GitHubjeanextreme002/pymemoryeditor

A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
binary-analysisdebuggerseducation+3
22611 days ago
memoro preview

memoro

GitHubepfl-vlsc/memoro

Memoro: A Detailed Heap Profiler
binary-analysisdebuggersdynamic-analysis-sandboxing+1
1855 years ago
DotDumper preview

DotDumper

GitHubadvanced-threat-research/dotdumper

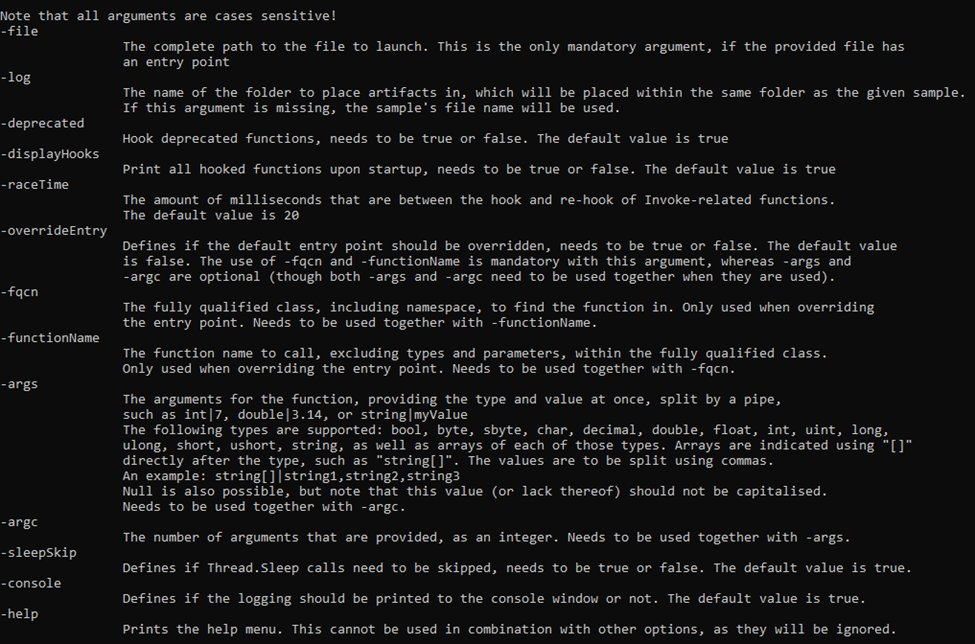
An automatic unpacker and logger for DotNet Framework targeting files

binary-analysisdebuggersdynamic-analysis-sandboxing+4
2643 years ago
dezlock-dump preview

dezlock-dump

GitHubdougwithseismic/dezlock-dump

Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
binary-analysisdebuggersdynamic-code-analysis+6
1025 days ago
asadbg preview

asadbg

GitHubnccgroup/asadbg

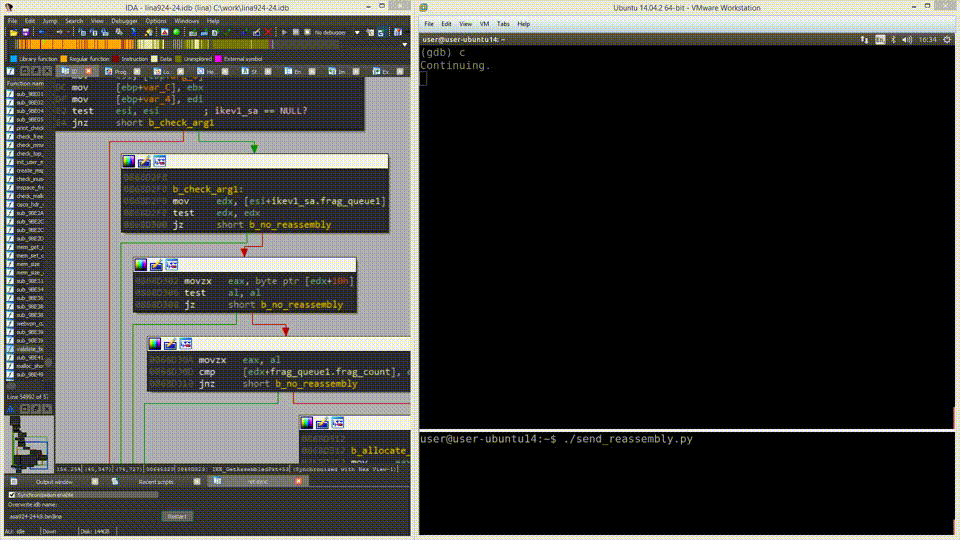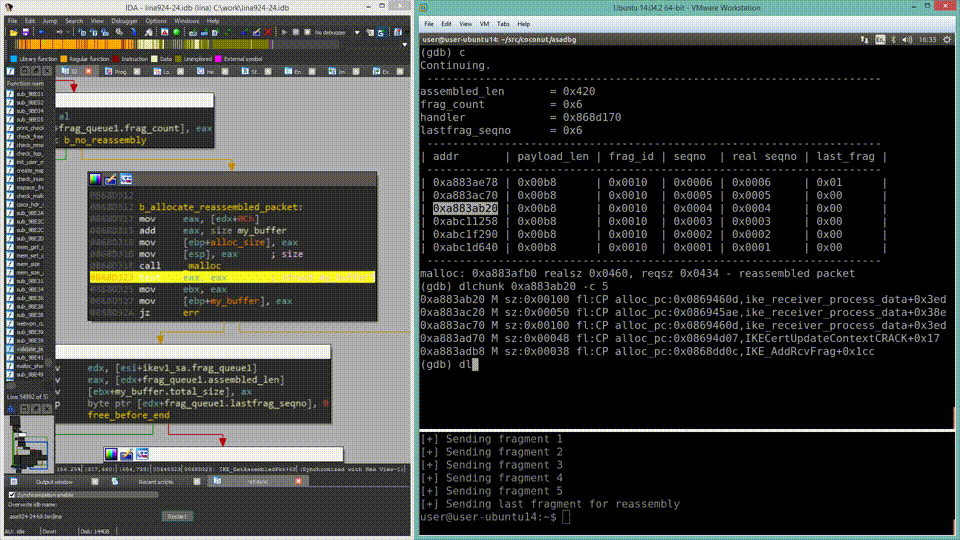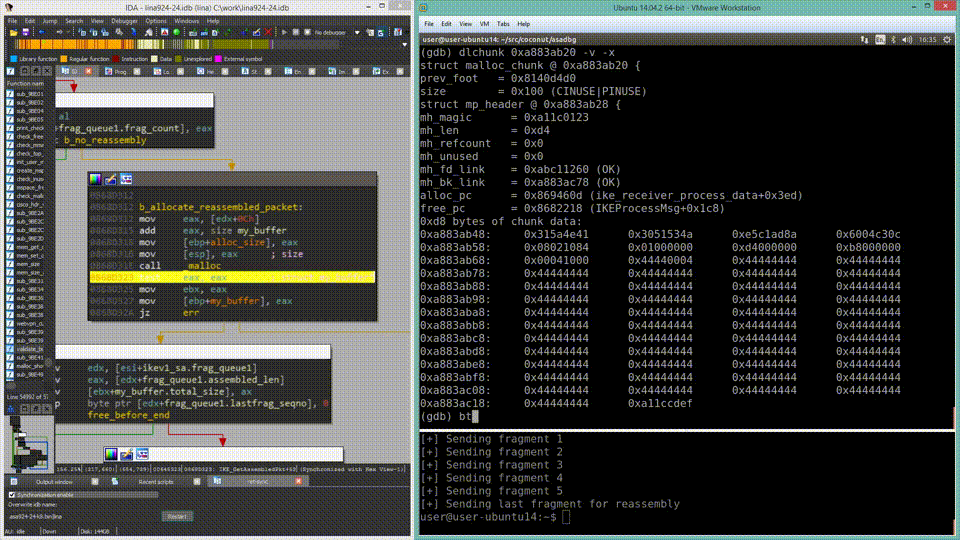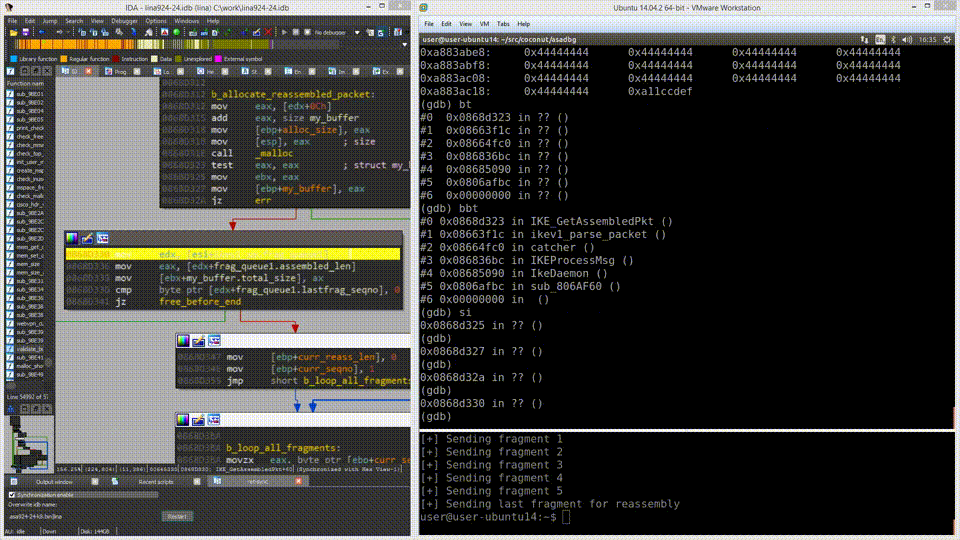
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
binary-analysisdebuggersembedded-systems-security+5
814 years ago
snoop preview

snoop

GitHubpandaadir05/snoop

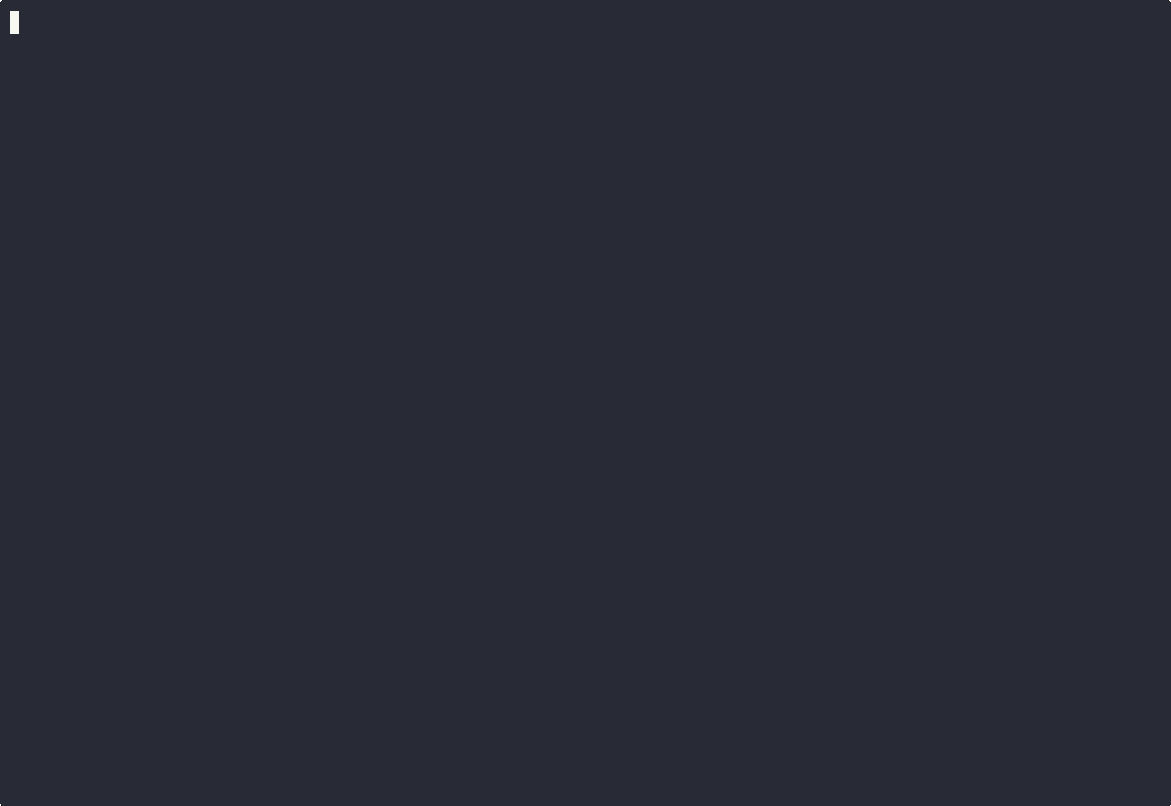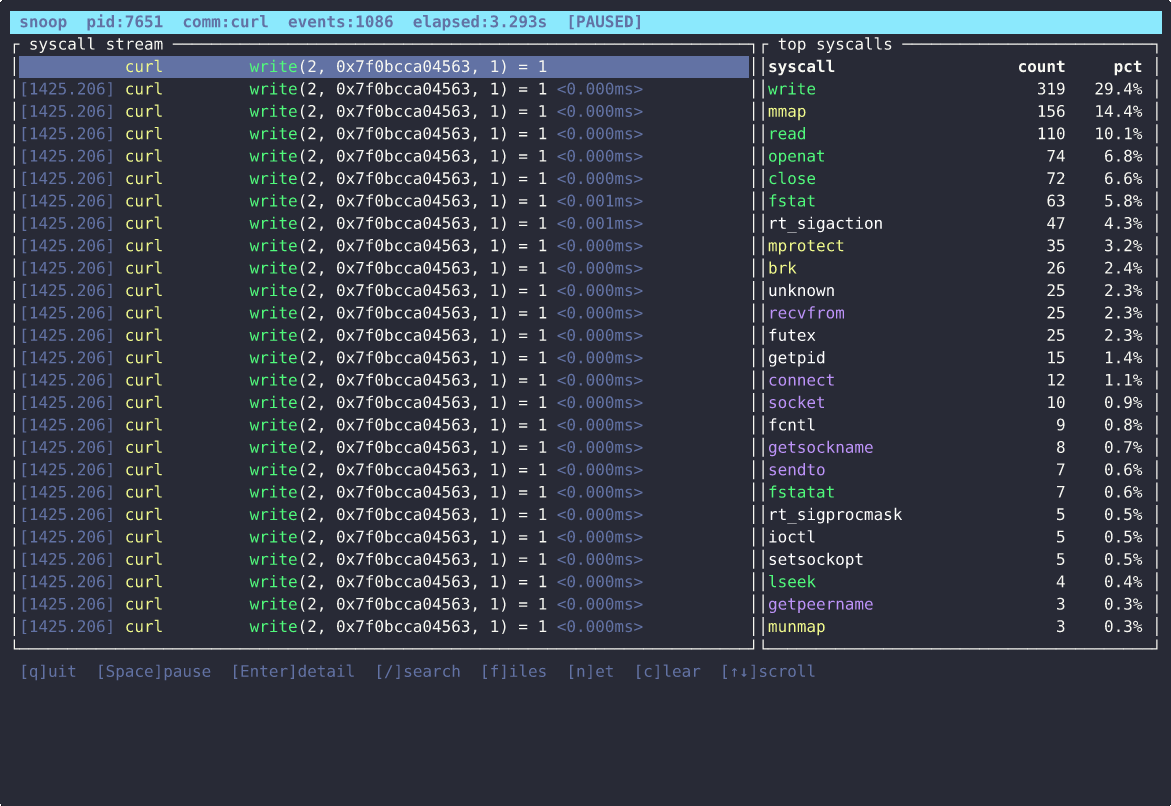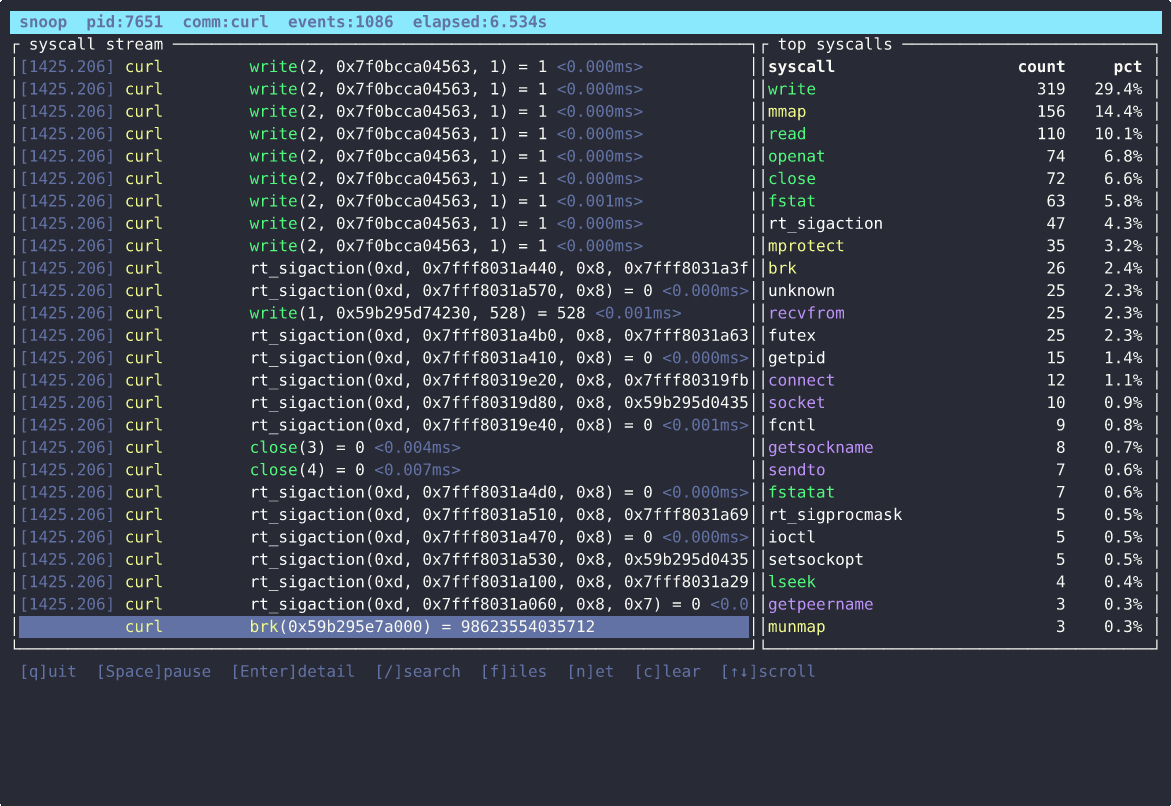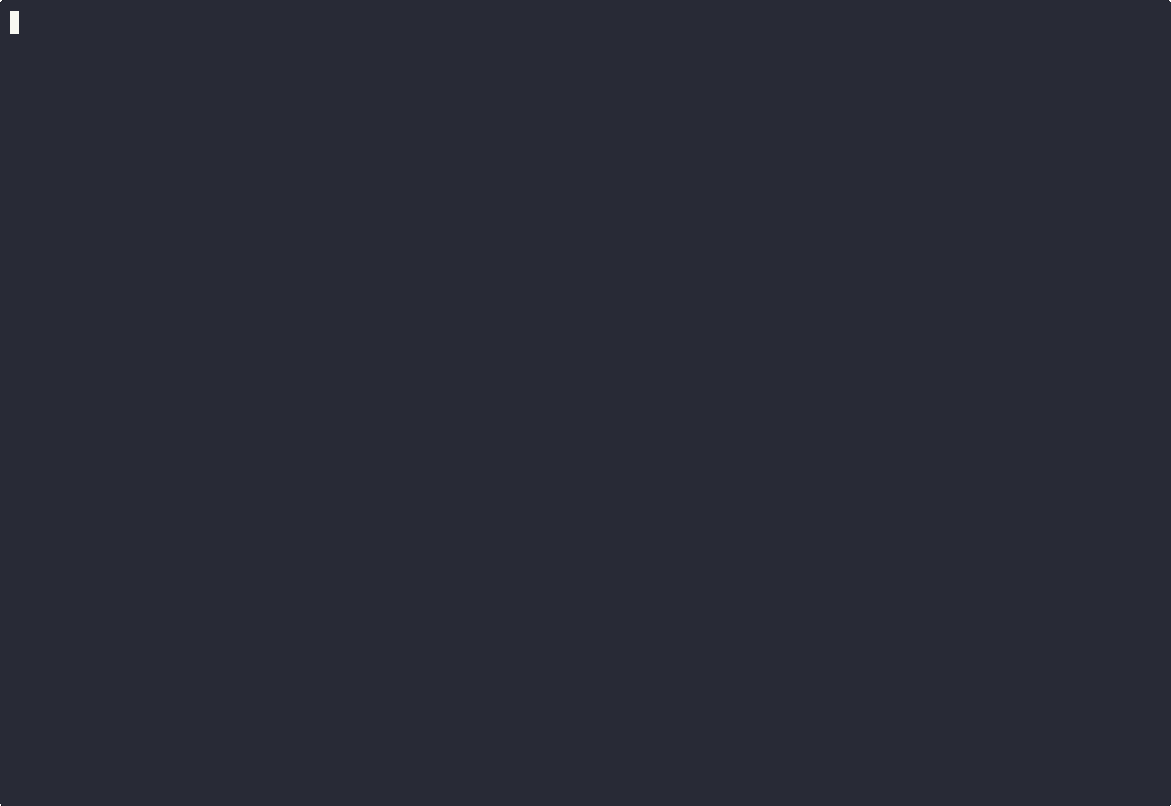
A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.
binary-analysisdebuggersdynamic-analysis-sandboxing+7
2226 months ago
windbg-mcp preview

windbg-mcp

GitHubgengstah/windbg-mcp

An MCP (Model Context Protocol) server that turns all pybag Windows debugger functions into native MCP tools. It lets MCP-compatible clients (Claude…
binary-analysisdebuggersdynamic-analysis-sandboxing+7
945 months ago
splinter preview

splinter

GitHubawrped/splinter

Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode

binary-analysisdebuggersdynamic-analysis-sandboxing+4
912 months ago
Previous123…9Next