osed-scripts
 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
binary-analysisbinary-exploitationdebuggers+5
6312 years ago
epi052/osed-scriptsbespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 harryanon/r0ak
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
 fortra/cve-2023-28252
Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…
 encrypter15/cve-2025-29824
Proof-of-concept exploit for CVE-2025-29824, a use-after-free vulnerability in the Windows CLFS kernel driver, demonstrating privilege escalation to…
 martinclauss/exim-rce-cve-2018-6789
This repository provides a learning environment to understand how an Exim RCE exploit for CVE-2018-6789 works.
 piffd0s/ntoskrnl-metadata
eprocess offset puller for relevant member offsets and function addresses for cve-2026-40369
 davidcarliez/cve-2026-62737-lab
Elevates a low-privilege Windows process to SYSTEM via a gdb-assisted ROP token-swap chain, demonstrating CVE-2026-62737 in a lab-only QEMU…
 tufanturhan/cve-2022-21971-windows-runtime-rce
Proof-of-concept exploit for CVE-2022-21971, an uninitialized pointer free vulnerability in Windows Runtime's prauthproviders.dll, triggered via…
 theman001/cve-2025-62215
CVE-2025-62215: Windows Kernel Race Condition + Double-Free EoP
 pravin761/cve-2026-54107
Root-cause analysis of CVE-2026-54107: a use-after-free in Windows win32kfull.sys with race condition debugging, static analysis, MSRC triage…
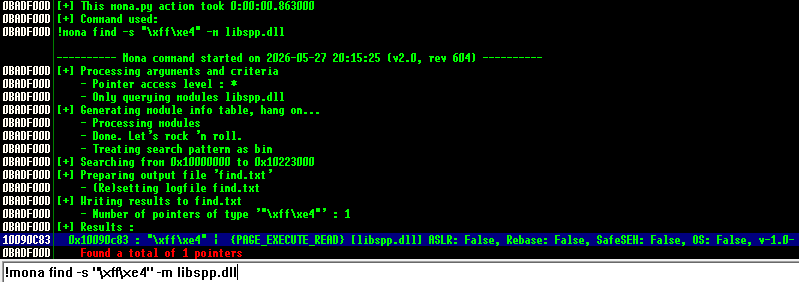 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 tnot123/cve-2017-9822
In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…
 lorenzoporrasduque/cve-2025-5548-poc
Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…
 diego57709/cve-2025-5548
Structured lab for controlled exploitation of CVE-2025-5548 (FreeFloat FTP Server). Includes environment setup, fuzzing, EIP control, badchars…
 alberto-galindo/cve-2025-5548
Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…
 charlyrr/cve-2025-5548
Educational lab documenting step-by-step exploitation of CVE-2025-5548 (Stack Buffer Overflow) on Windows 11, from fuzzing and crash analysis to…
 anasrami12/cve-2025-5548
Methodology for vulnerability analysis and exploit development, covering static/dynamic analysis, fuzzing, patch diffing, and 0-day research with…