

systeminformer
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
debuggersdigital-forensicsforensics+6
16.2k
winsiderss/systeminformerReal-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
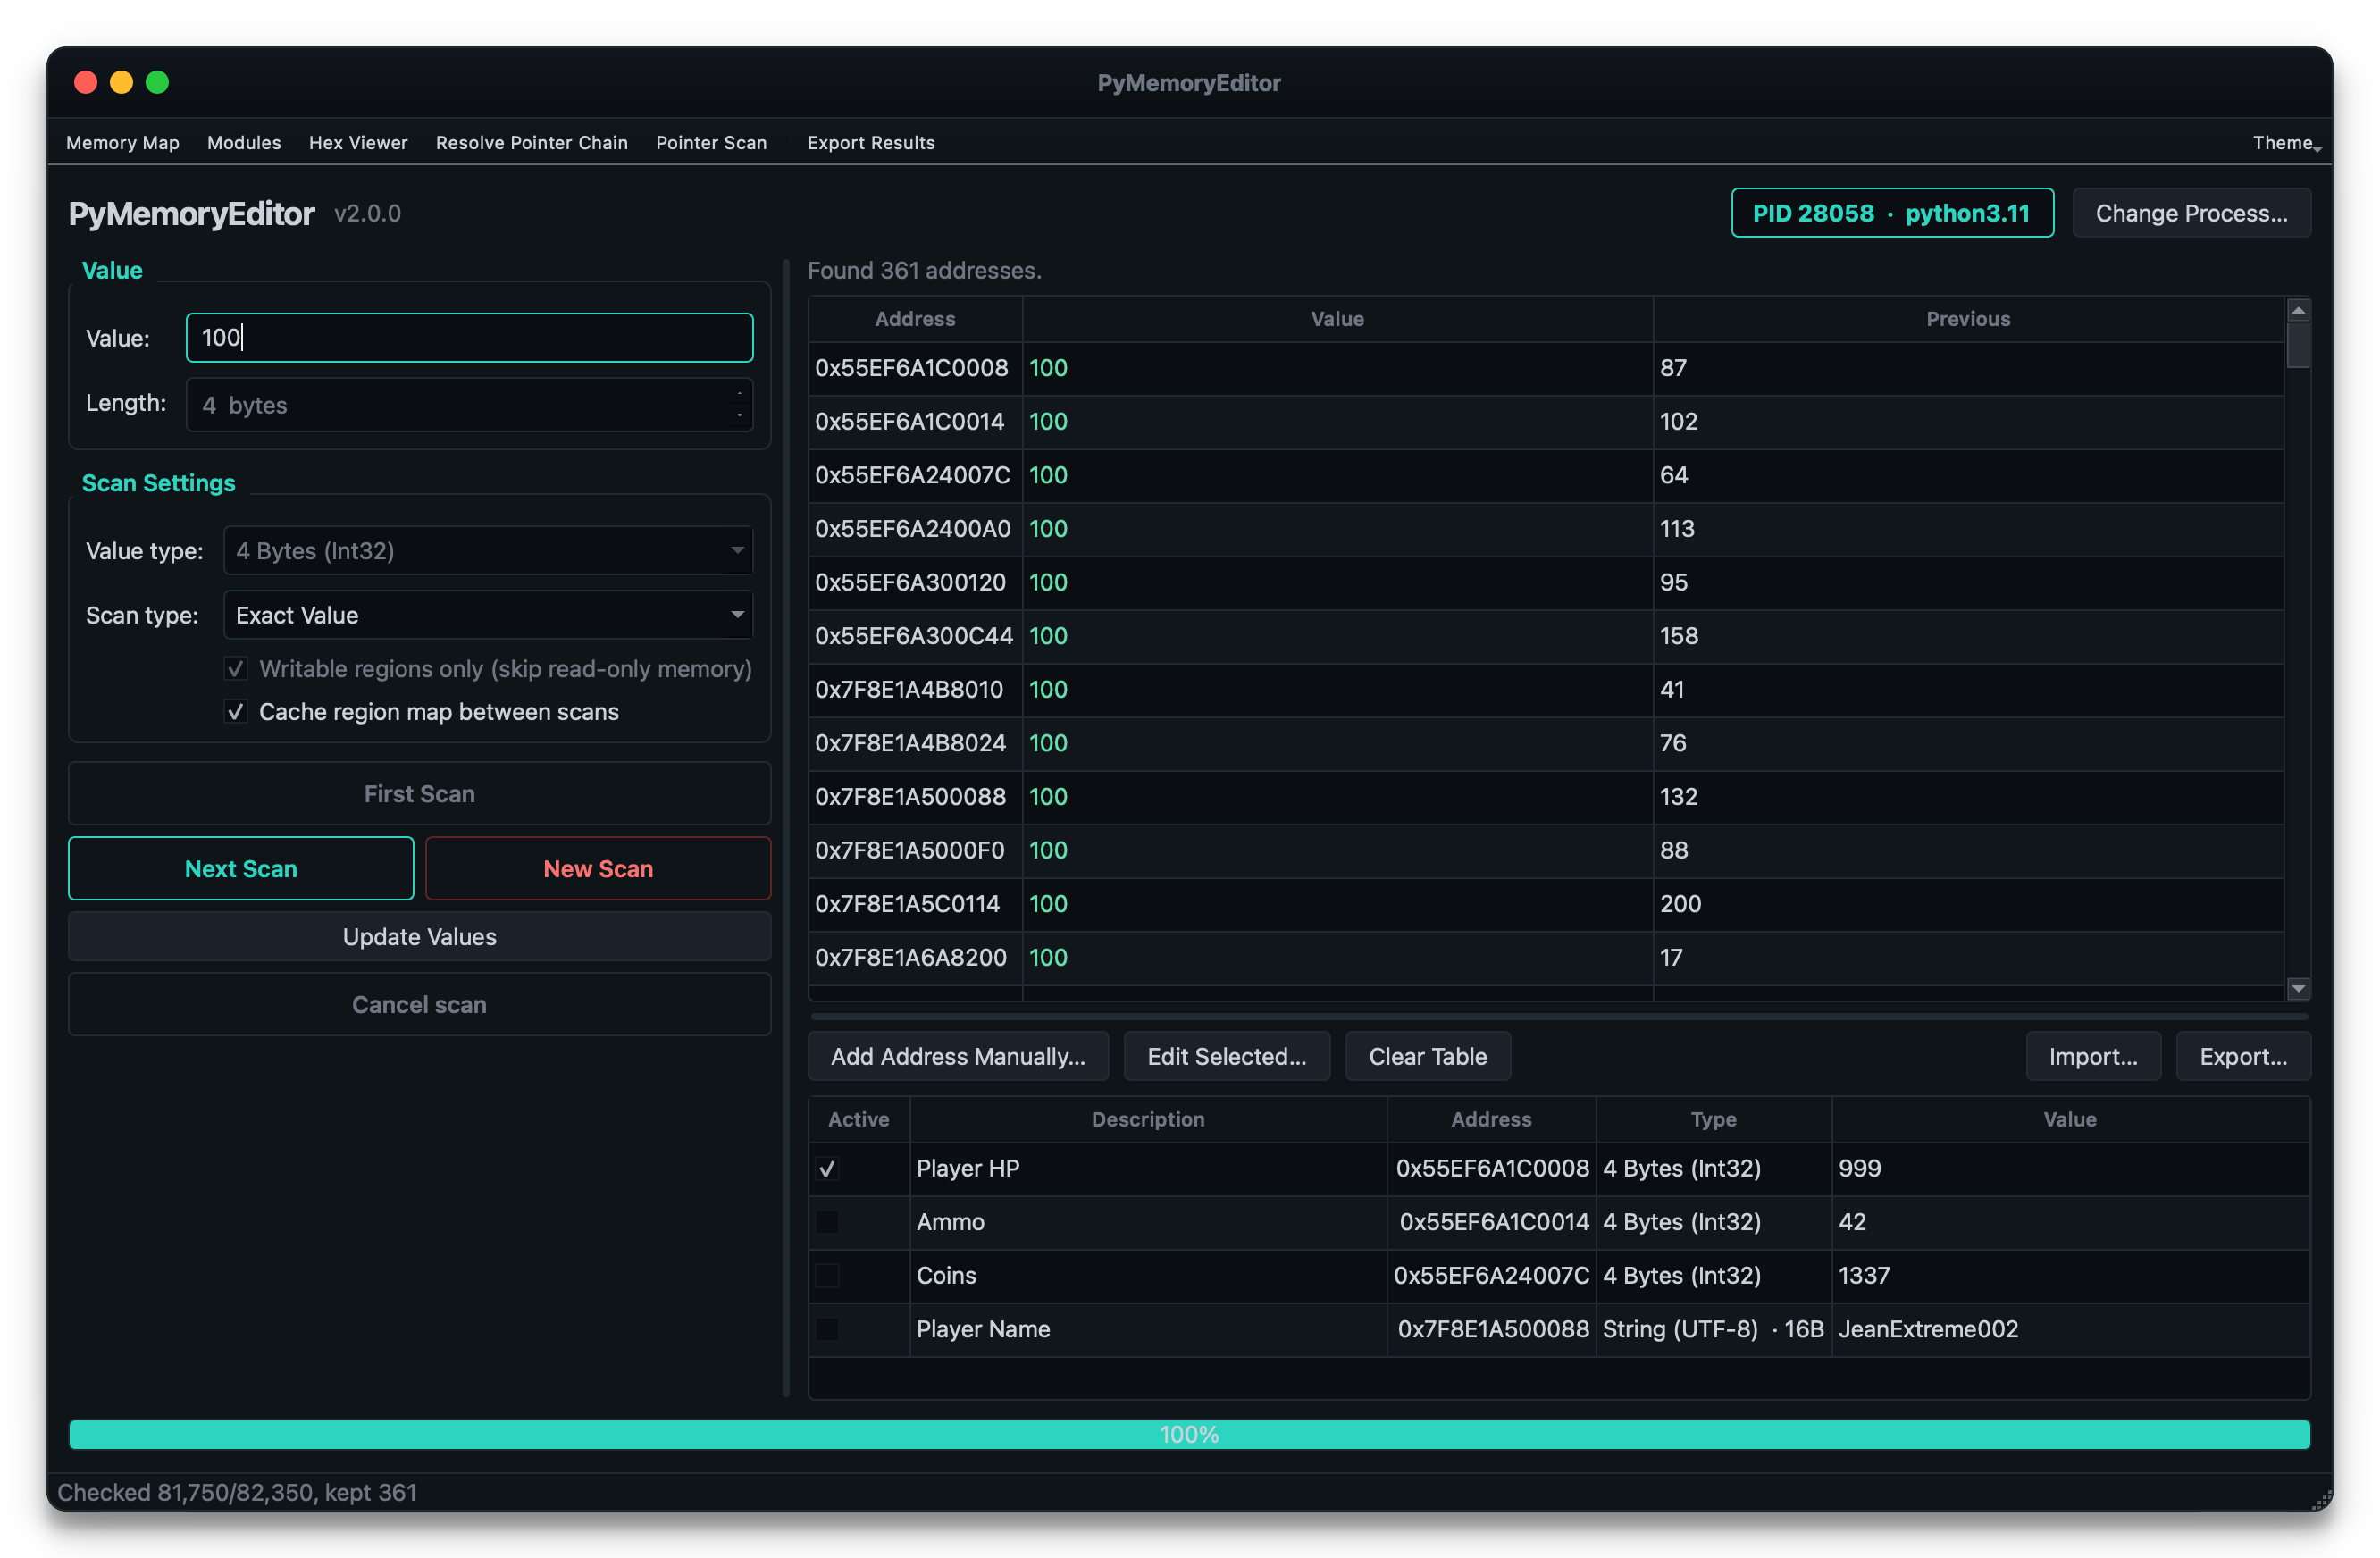 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 lauriewired/ghidramcp
MCP Server for Ghidra
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 angr/angr
A powerful and user-friendly binary analysis platform!
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 allthingsida/idasql
Vibe Reverse Engineer with IDA Pro: An interface for IDA in SQL via live virtual tables. Don't let appearances deceive you! :)
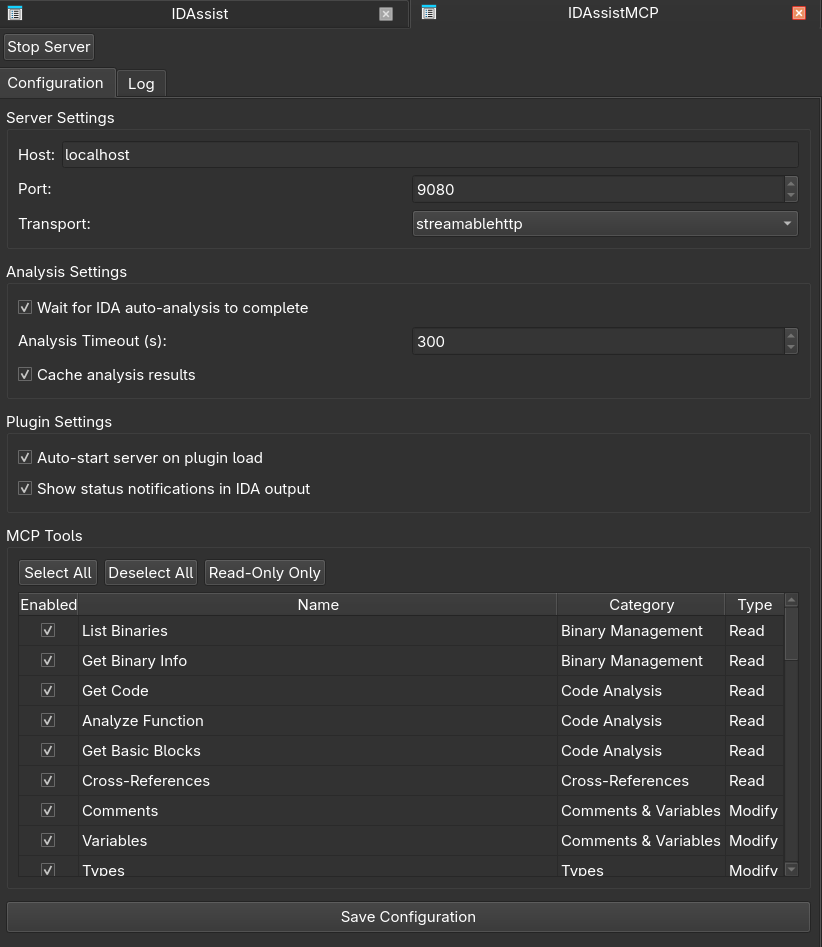 symgraph/idassistmcp
Standalone MCP server plugin for IDA Pro.
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 gilnett/wstrace
Standalone zero-driver Windows system and API monitor in Rust