

kraken
 adam-atlassoftware/kraken
Reverse-engineering workbench built on Ghidra's decompiler with a native Java-free engine, AI-assisted function analysis, byte patching, sandboxed…
ai-assisted-reversingai-securitybinary-analysis+8
31
adam-atlassoftware/krakenReverse-engineering workbench built on Ghidra's decompiler with a native Java-free engine, AI-assisted function analysis, byte patching, sandboxed…
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
 pdb333/cortex
A Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 gmh5225/ida-claude-code-plugins
Plugins integrating Claude Code with IDA Pro to assist reverse engineering and binary analysis workflows through AI-driven disassembly and code…
 gmh5225/ida_plugin_pcodegpt
IDA Pro plugin that uses OpenAI GPT-3.5/GPT-4 to automate reverse engineering tasks such as function naming, code explanation, and decompiled…
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
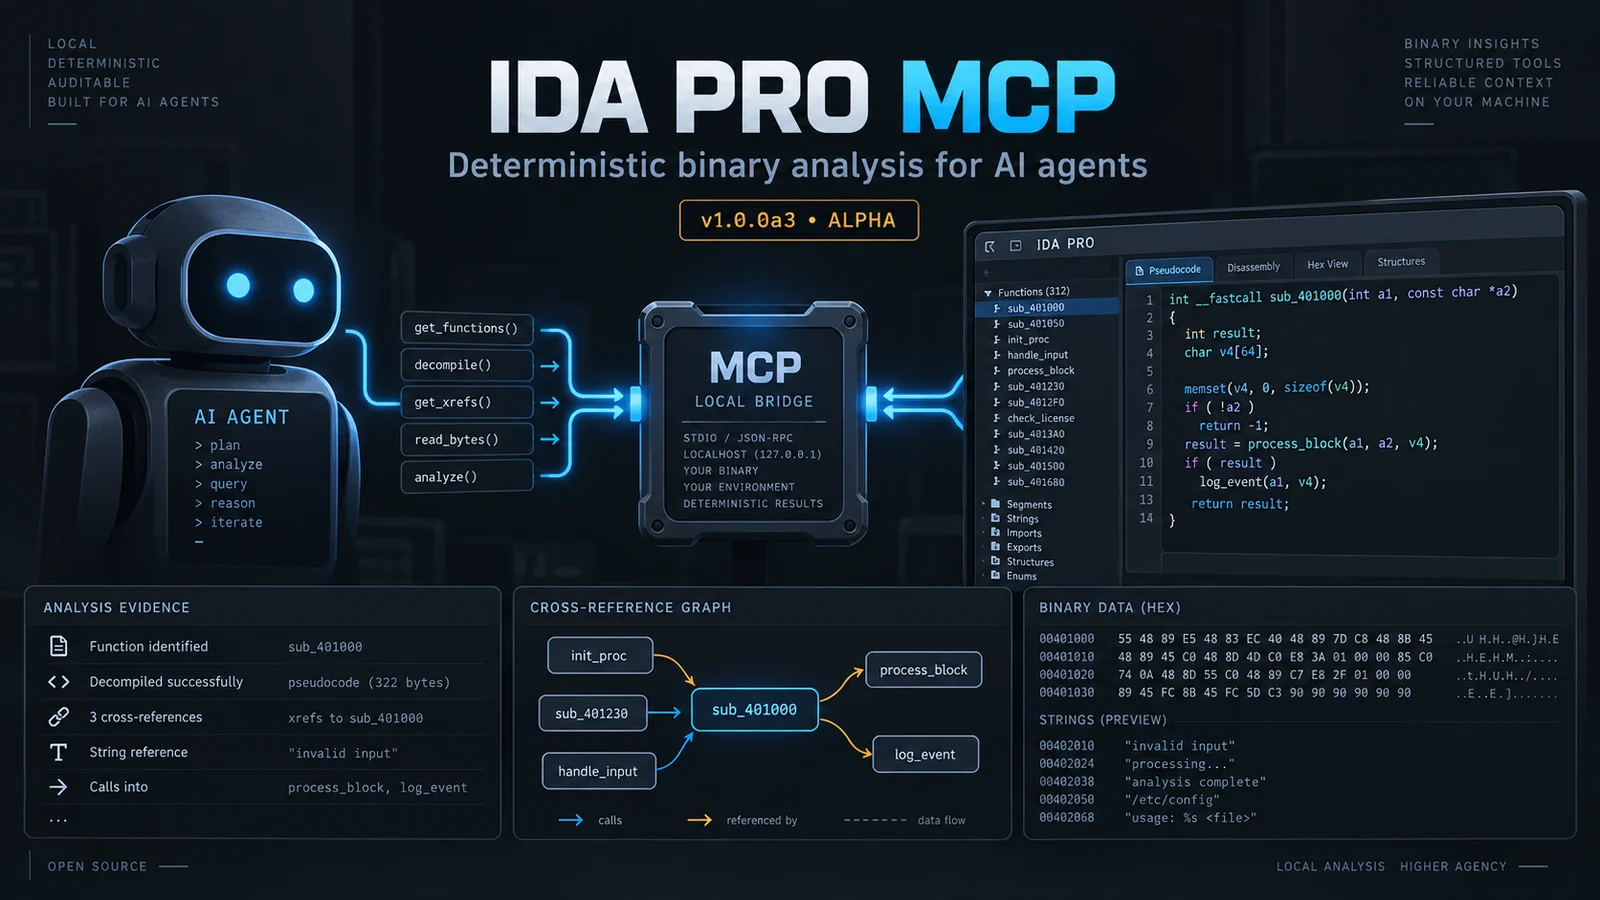 grecandrei/ida-pro-mcp
Local-first, deterministic MCP server for IDA Pro/Home: 109 strict-schema reverse-engineering operations, evidence-backed findings, and policy-gated…
 vsvalinx/cve-2025-5548
Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…
 anpa1200/aidebug
Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
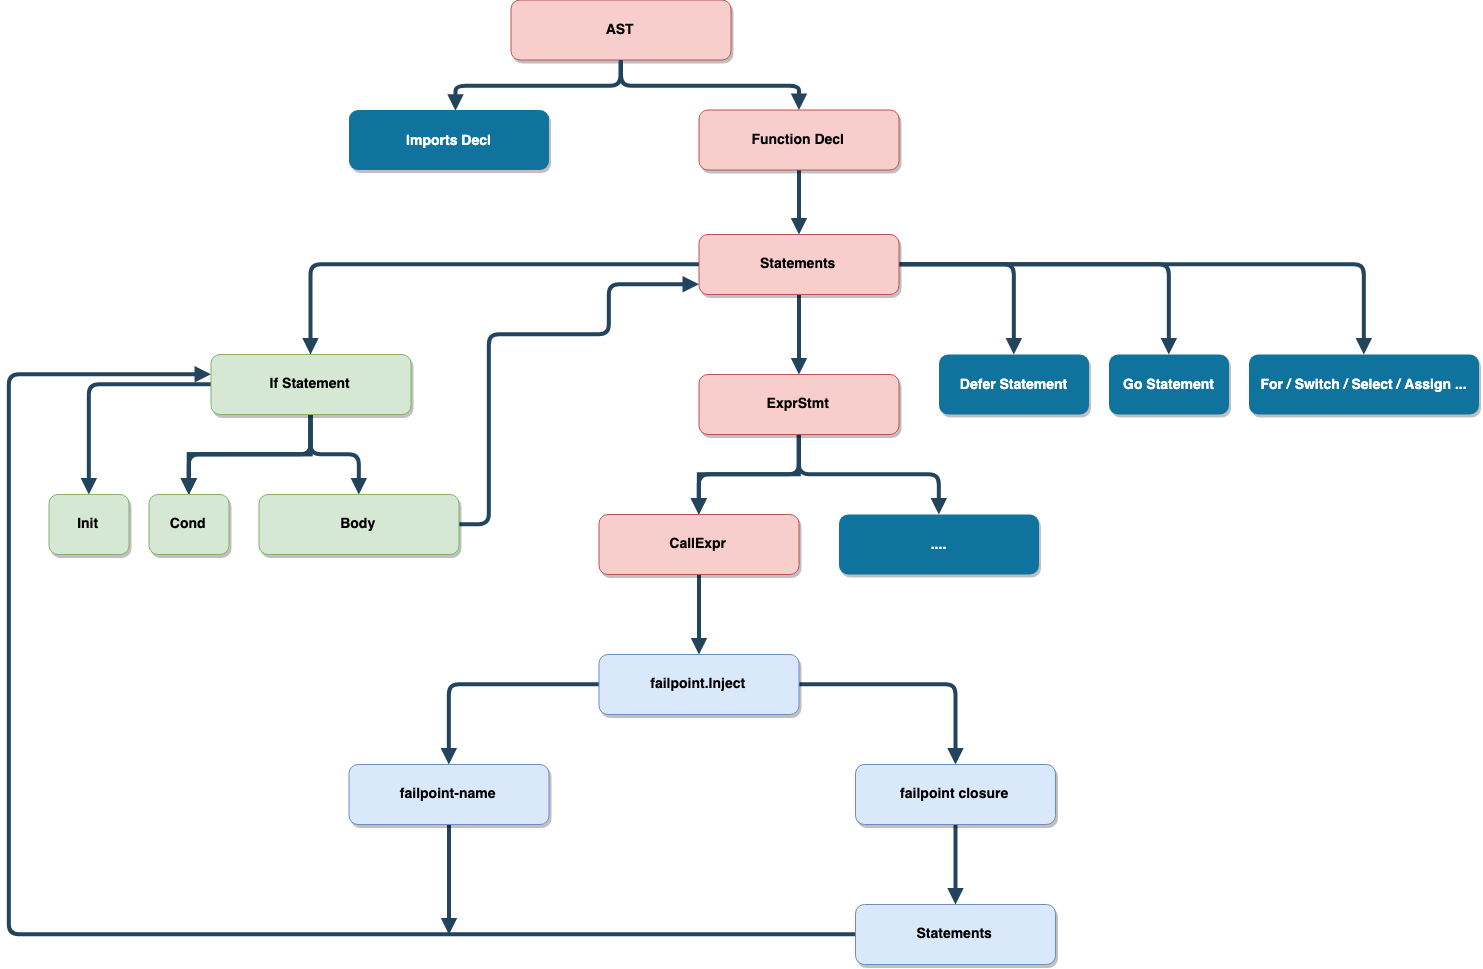 pingcap/failpoint
Fault-injection library for Go that adds runtime-controllable failpoints to trigger panics, sleeps, returns, and conditional error paths via…
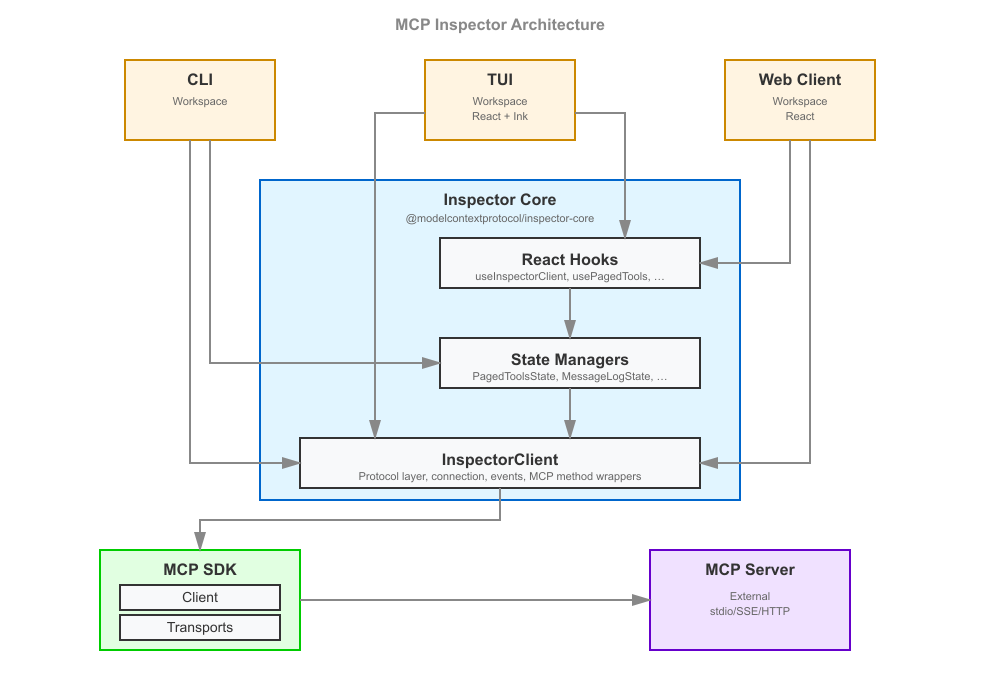 modelcontextprotocol/inspector
Inspect, debug, and visually test Model Context Protocol (MCP) servers from a web UI, CLI, or TUI, with tool/resource exploration, request logging,…
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 gmh5225/asm-obfuscator
Obfuscates x86-64 assembly with instruction injection, junk code, constant obfuscation, and runtime decryption to hinder reverse engineering and…
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
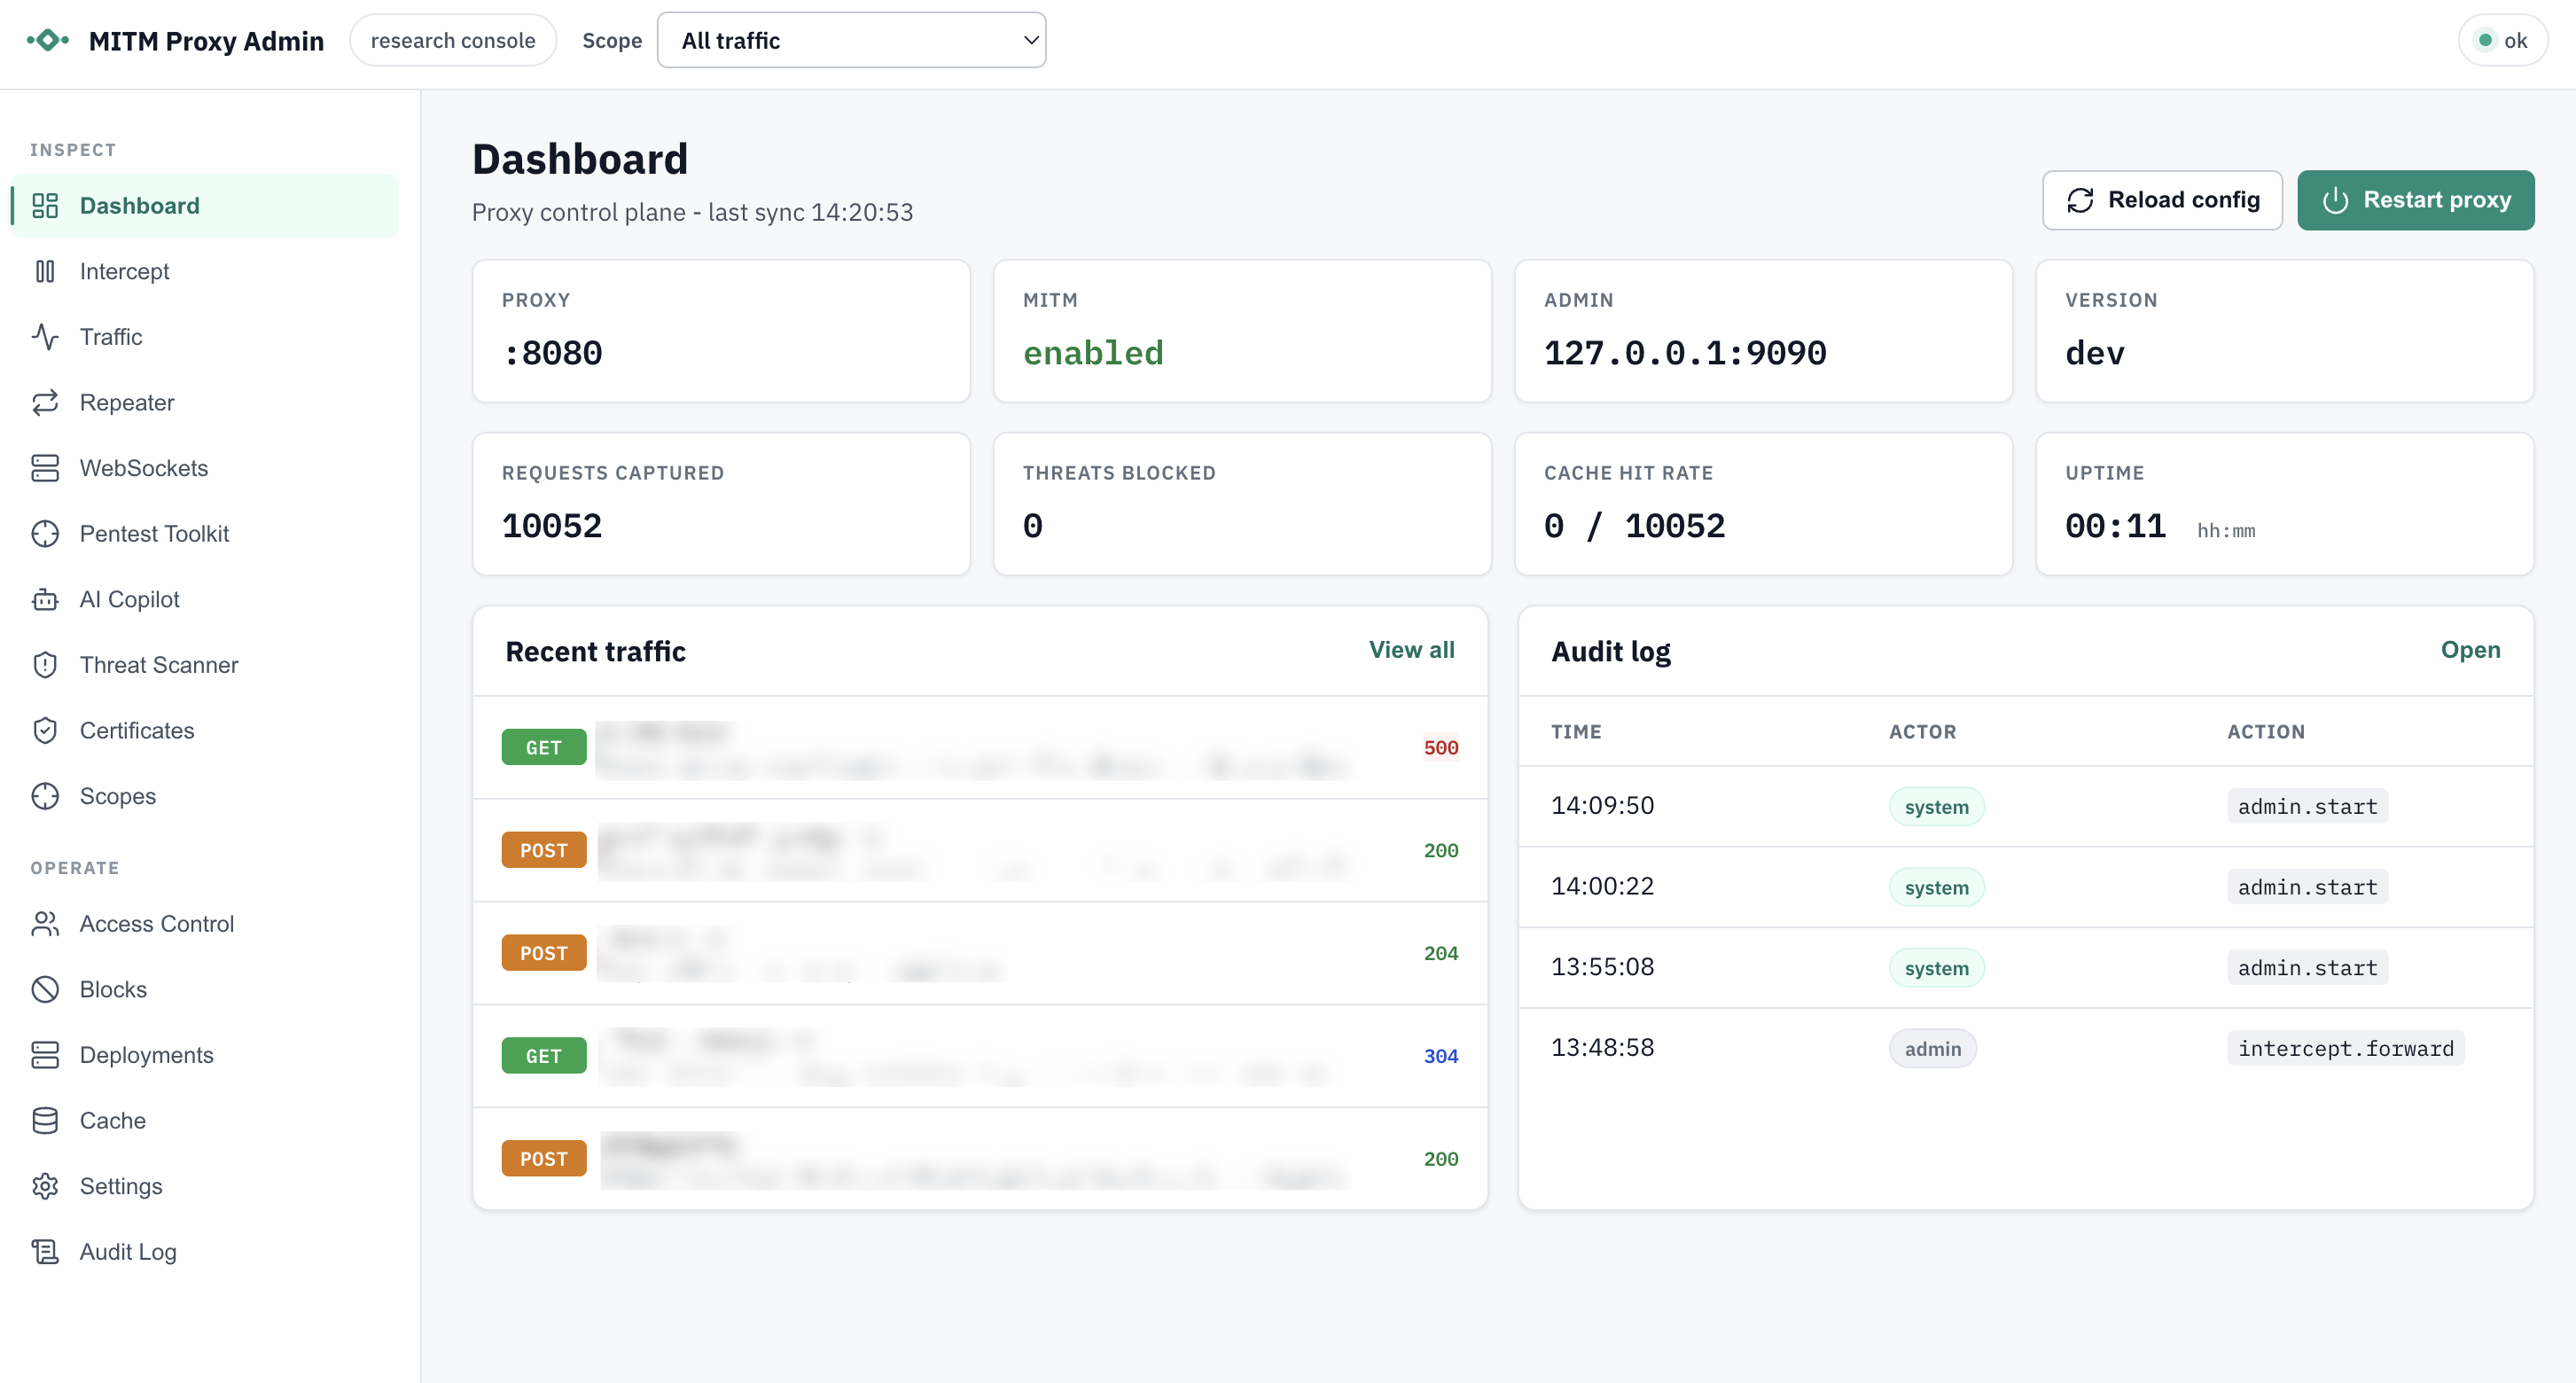 welfordian/mitm-proxy
Go-based MITM HTTP/HTTPS proxy with HTTP/2 and HTTP/1.1 interception, local CA/per-host cert generation, CONNECT/WebSocket tunneling, disk caching,…
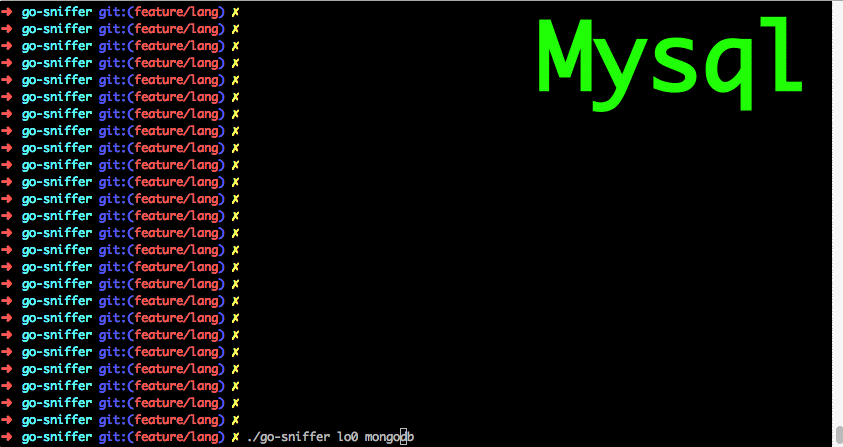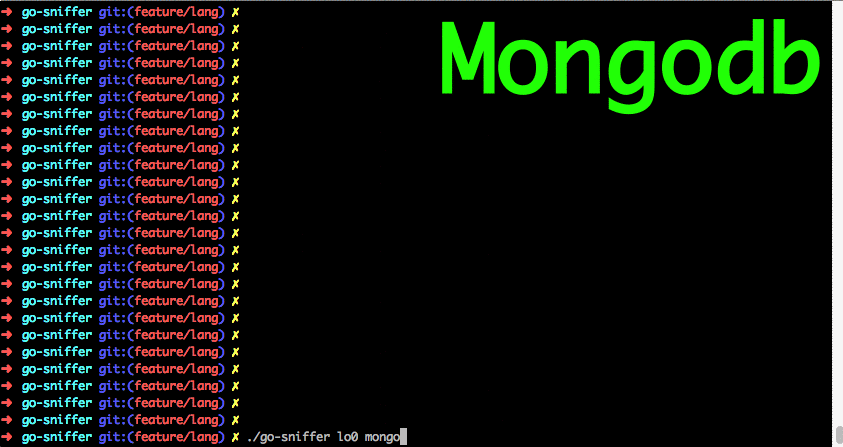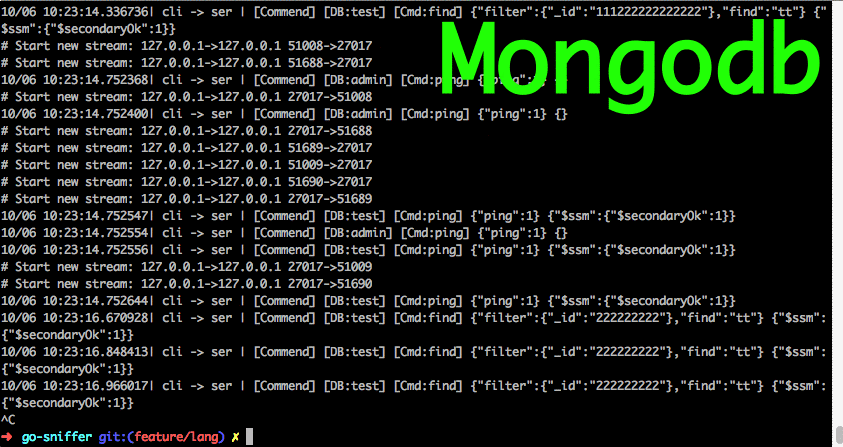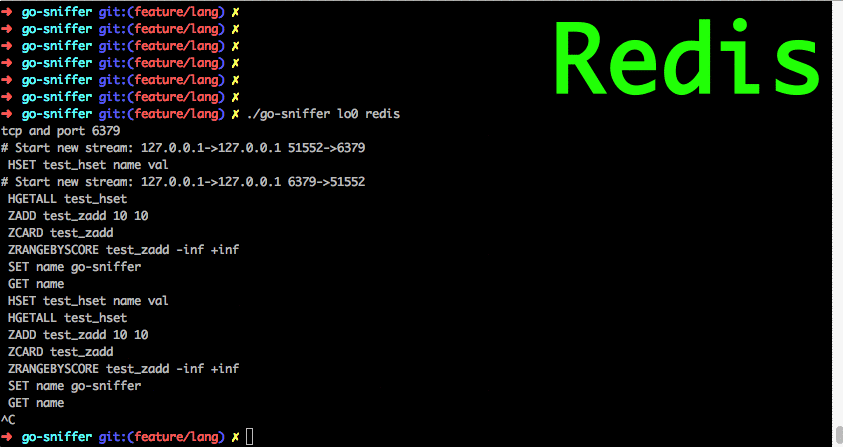 40t/go-sniffer
🔎Sniffing and parsing mysql,redis,http,mongodb etc protocol. 抓包截取项目中的数据库请求并解析成相应的语句。