
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
511 results
icicle-python preview

icicle-python

GitHubicicle-emu/icicle-python

Python bindings for the Icicle emulator, enabling grey-box firmware fuzzing, binary emulation, and reverse-engineering workflows across x64 and ARM64…
binary-analysisdebuggersdynamic-analysis-sandboxing+5
43
11 months ago
revng preview

revng

GitHubrevng/revng

Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
binary-analysiscode-analysisdebuggers+6
1.7k2 days ago
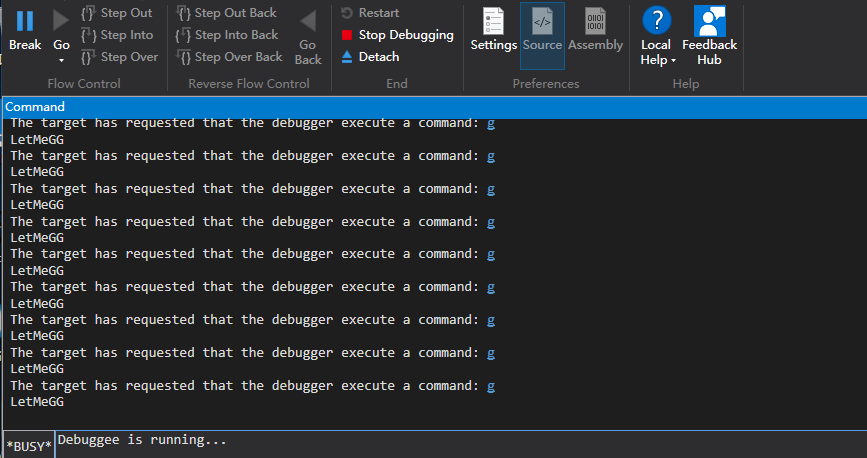
LetMeGG preview

LetMeGG

GitHubgmh5225/letmegg

Windows kernel proof-of-concept demonstrating an anti-debugging technique that prevents WinDbg from breaking by manipulating the kernel exception…
anti-botbinary-analysisdebuggers+1
154 years ago
linux-kernel-debugger preview

linux-kernel-debugger

GitHubgmh5225/linux-kernel-debugger

Kernel hardware debugger module for dumping rootkit operations and inspecting kernel-level activity for malware analysis and reverse engineering.
binary-analysisdebuggersdynamic-analysis-sandboxing+3
4 years ago
TitanHide preview

TitanHide

GitHubmrexodia/titanhide

Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
anti-botbinary-analysisdebuggers+4
2.9k2 months ago
MAccConc preview

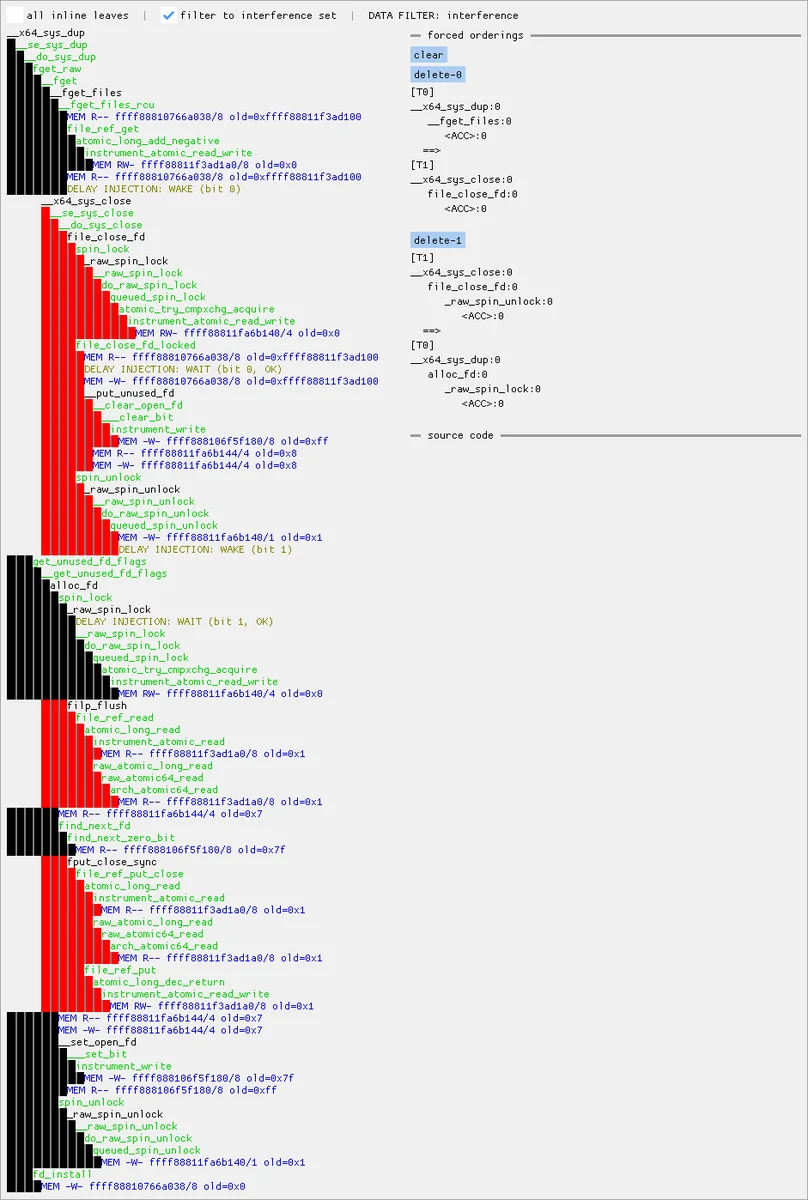
MAccConc

GitHubgoogleprojectzero/maccconc

Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…
binary-analysisdebuggersdynamic-analysis-sandboxing+6
5029 days ago
kernelmode-driver preview

kernelmode-driver

GitHubgmh5225/kernelmode-driver

Kernel Driver for x64 Window System which allows you to read/write Virtual/Physical Memory hooking Win32k
binary-analysisdebuggersmalware-analysis+4
32 years ago
KeyPatchX preview

KeyPatchX

GitHubgmh5225/keypatchx

KeyPatch Enhanced — IDA Pro plugin for symbol-aware x86/x64 assembly patching, powered by Keystone Engine. Fork of Keypatch with automatic IDA symbol…
binary-analysisbinary-exploitationdebuggers+4
97 months ago
frida-gum preview

frida-gum

GitHubfrida/frida-gum

Cross-platform instrumentation and introspection library written in C
binary-analysiscode-analysisdebuggers+6
1.0k3 days ago
static-arm-bins preview

static-arm-bins

GitHubtherealsaumil/static-arm-bins

Statically compiled ARM binaries for debugging and runtime analysis
binary-analysisdebuggersdynamic-analysis-sandboxing+6
5285 years ago
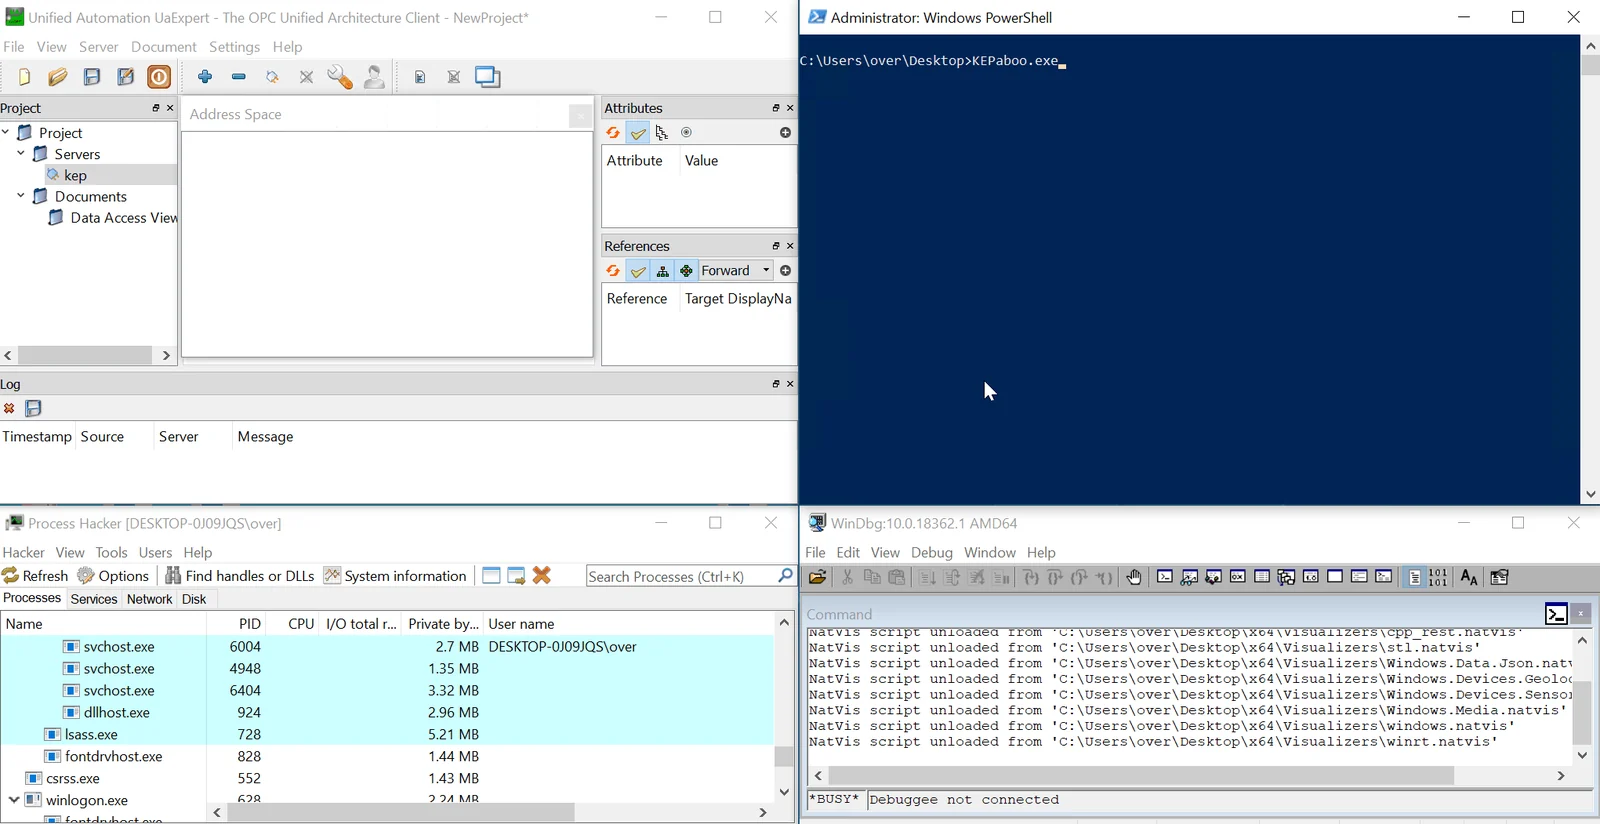
KEPaboo preview

KEPaboo

GitHub0vercl0k/kepaboo

Neutralize KEPServerEX anti-debugging techniques
anti-botbinary-analysisbinary-exploitation+5
333 years ago
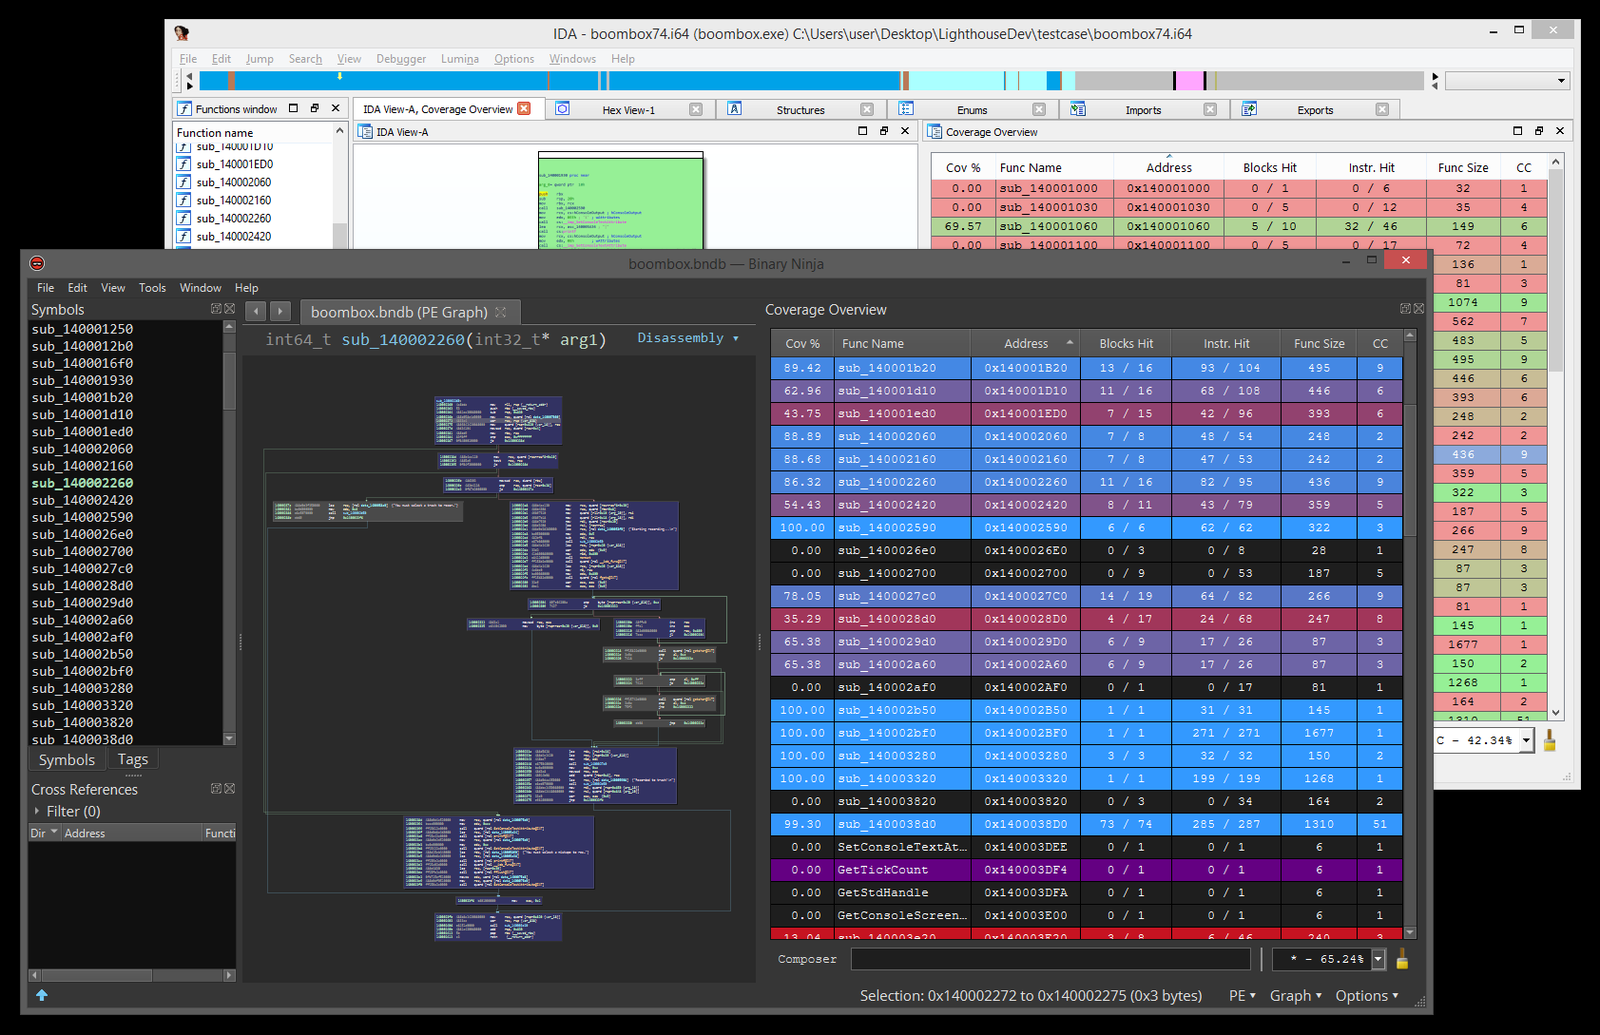
lighthouse preview

lighthouse

GitHubgaasedelen/lighthouse

A Coverage Explorer for Reverse Engineers
binary-analysiscode-analysisdebuggers+6
2.6k7 months ago
Jackalope preview

Jackalope

GitHubgoogleprojectzero/jackalope

Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
binary-analysisdebuggersdynamic-analysis-sandboxing+6
1.4k1 month ago
luadec preview

luadec

GitHubviruscamp/luadec

Lua Decompiler for lua 5.1 , 5.2 and 5.3

binary-analysiscode-analysisdebuggers+4
1.3k2 years ago
N0xis preview

N0xis

GitHubstructio-labs/n0xis

AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).

ai-assisted-reversingbinary-analysisbinary-exploitation+7
24 days ago
cortex preview

cortex

GitHubpdb333/cortex

A Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.

ai-assisted-reversingai-securitybinary-analysis+7
257 days ago
KernelFlirt preview

KernelFlirt

GitHubakatorich/kernelflirt

Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…

ai-assisted-reversingai-securityanti-bot+9
444 months ago
Formbook-Payload-Extraction-XOR-Decryption-Net-Assembly-Analysis preview

Formbook-Payload-Extraction-XOR-Decryption-Net-Assembly-Analysis

GitHubkaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…

binary-analysisdebuggersdigital-forensics+6
610 days ago
Previous12…29Next