
kernelmode-driver
 gmh5225/kernelmode-driver
Kernel Driver for x64 Window System which allows you to read/write Virtual/Physical Memory hooking Win32k
binary-analysisdebuggersmalware-analysis+4
3
gmh5225/kernelmode-driverKernel Driver for x64 Window System which allows you to read/write Virtual/Physical Memory hooking Win32k
 gmh5225/keypatchx
KeyPatch Enhanced — IDA Pro plugin for symbol-aware x86/x64 assembly patching, powered by Keystone Engine. Fork of Keypatch with automatic IDA symbol…
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
 therealsaumil/static-arm-bins
Statically compiled ARM binaries for debugging and runtime analysis
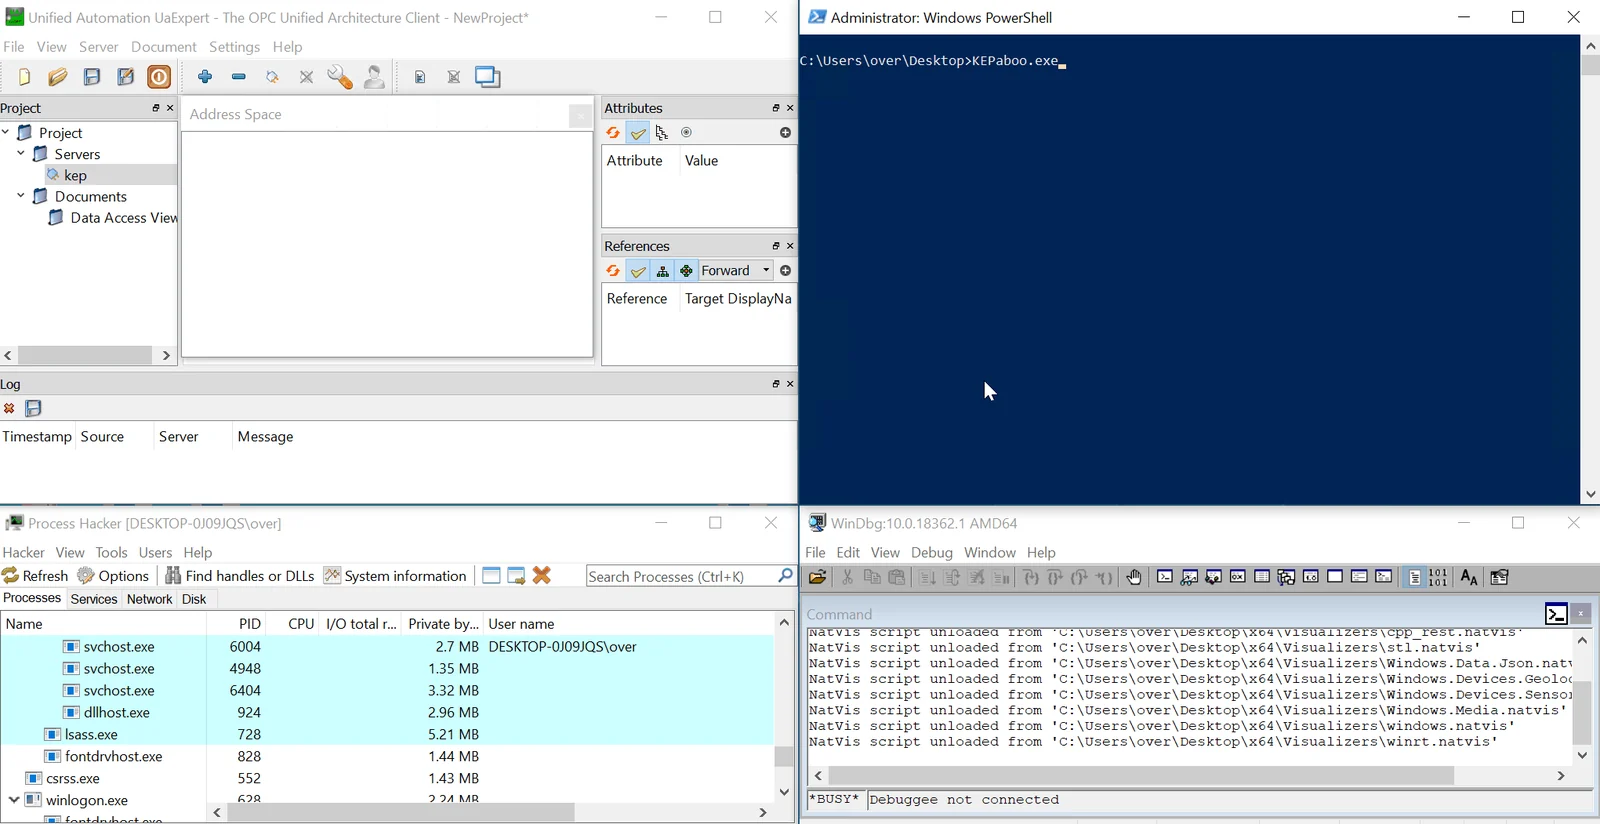 0vercl0k/kepaboo
Neutralize KEPServerEX anti-debugging techniques
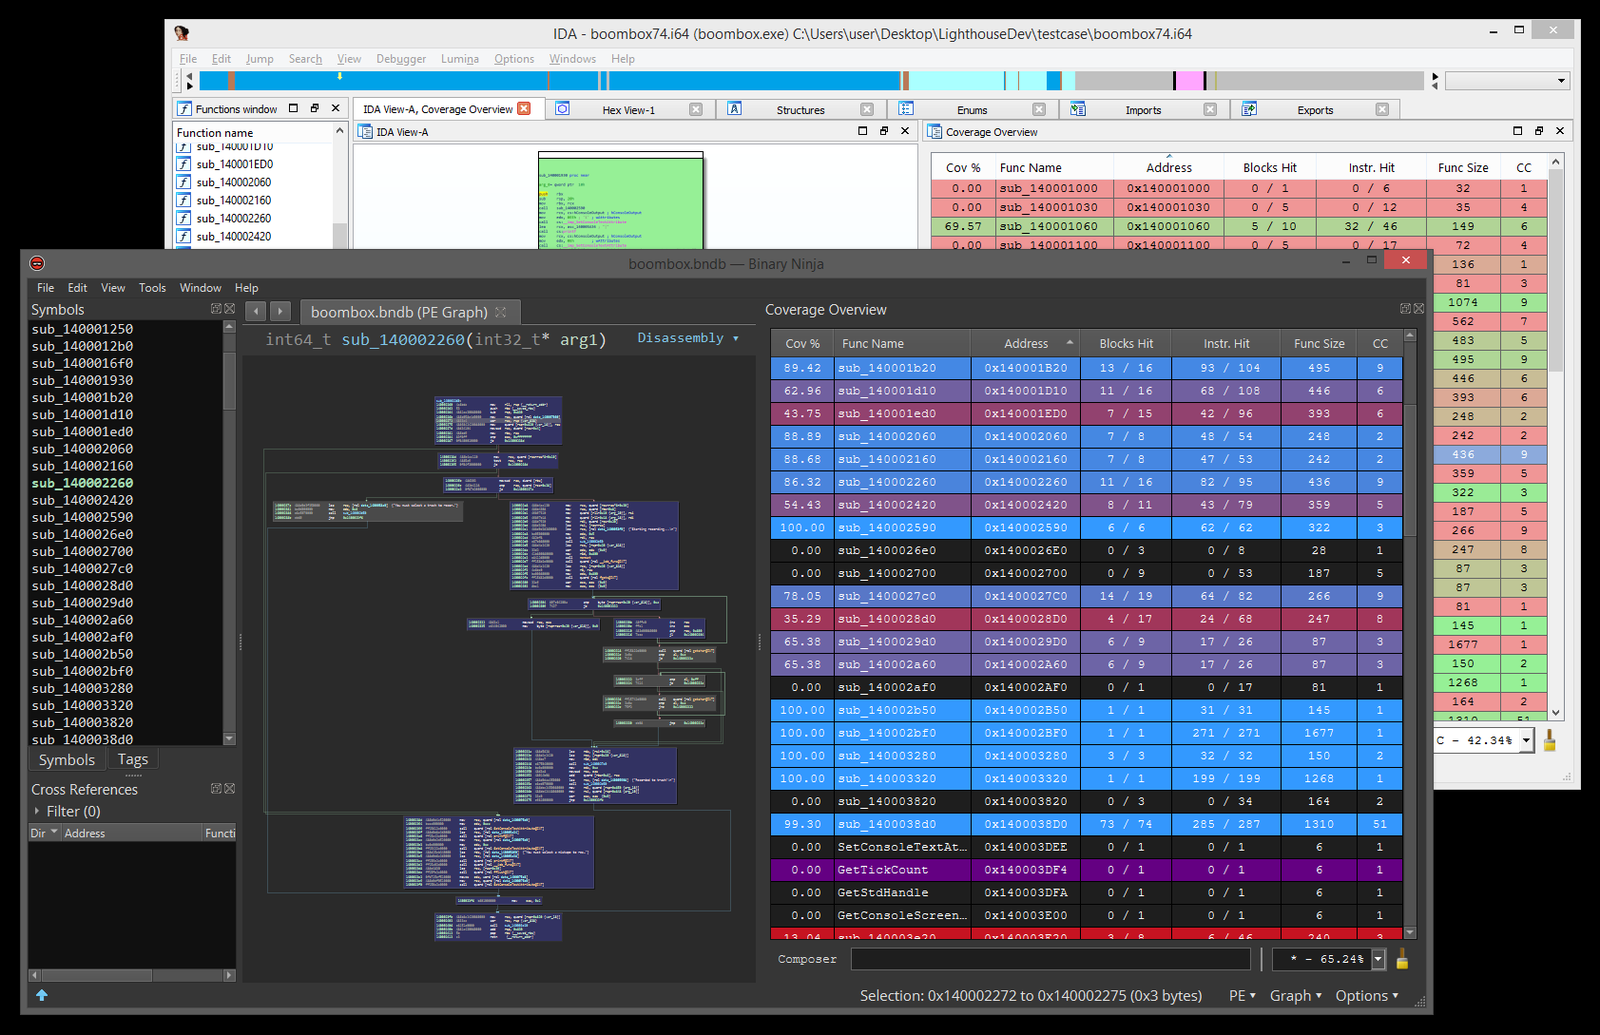 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
 viruscamp/luadec
Lua Decompiler for lua 5.1 , 5.2 and 5.3
 structio-labs/n0xis
AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
 rasetsuu/vmp-devirt
Trace-assisted VMProtect devirtualization research platform: version front-ends feed a shared Remill/LLVM backend to lift handlers, recover dataflow,…
 pdb333/cortex
A Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 kaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis
Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…
 gmh5225/hooktools
Basic injectable for analyzing the behavior of evasive malware
 gmh5225/ida-claude-code-plugins
Plugins integrating Claude Code with IDA Pro to assist reverse engineering and binary analysis workflows through AI-driven disassembly and code…
 gmh5225/ida-sdk
Official IDA Pro SDK headers and libraries for building plugins that disassemble, decompile, and analyze binaries within the IDA reverse engineering…
 gmh5225/ida_plugin_pcodegpt
IDA Pro plugin that uses OpenAI GPT-3.5/GPT-4 to automate reverse engineering tasks such as function naming, code explanation, and decompiled…
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…