

ceasta
 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
ai-assisted-reversingbinary-analysisbinary-exploitation+6
138
ngwg/ceastadisassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
 gmh5225/driver-kaldereta
Unsigned Kernel Mode Driver that does memory modifications
 vsvalinx/cve-2025-5548
Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 davidcarliez/cve-2026-62737-lab
Elevates a low-privilege Windows process to SYSTEM via a gdb-assisted ROP token-swap chain, demonstrating CVE-2026-62737 in a lab-only QEMU…
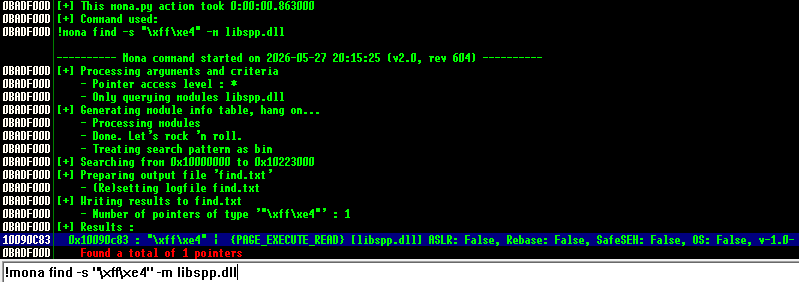 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 pravin761/cve-2026-54107
Root-cause analysis of CVE-2026-54107: a use-after-free in Windows win32kfull.sys with race condition debugging, static analysis, MSRC triage…
 canomer/cve-2026-36980-kernel-bsod-dos-poc
Project Date : Feb 2026 / Discovered a buffer overflow vulnerability in the IOCTL handler of the kernel driver. The vulnerability allows an…
 theman001/cve-2025-62215
CVE-2025-62215: Windows Kernel Race Condition + Double-Free EoP
 lorenzoporrasduque/cve-2025-5548-poc
Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…
 diego57709/cve-2025-5548
Structured lab for controlled exploitation of CVE-2025-5548 (FreeFloat FTP Server). Includes environment setup, fuzzing, EIP control, badchars…
 piffd0s/ntoskrnl-metadata
eprocess offset puller for relevant member offsets and function addresses for cve-2026-40369
 martinclauss/exim-rce-cve-2018-6789
This repository provides a learning environment to understand how an Exim RCE exploit for CVE-2018-6789 works.
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…