

ceasta
 ngwg/ceasta
Disassembler, decompiler and x64dbg-style debugger for PE/ELF binaries with IDA-style listing, function graphs, Lua plugins, CLI, and a built-in MCP…
ai-assisted-reversingbinary-analysisbinary-exploitation+6
181
ngwg/ceastaDisassembler, decompiler and x64dbg-style debugger for PE/ELF binaries with IDA-style listing, function graphs, Lua plugins, CLI, and a built-in MCP…
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 kaandemir993/amadey-loader-multi-stage-malware-with-keylogging-clipboard-hijack-privilege-escalation-analysis
Reverse engineering Amadey Loader with x64dbg: dynamic API resolution, token privilege escalation, keylogger hooks, clipboard capture, and…
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 pdb333/cortex
A Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.
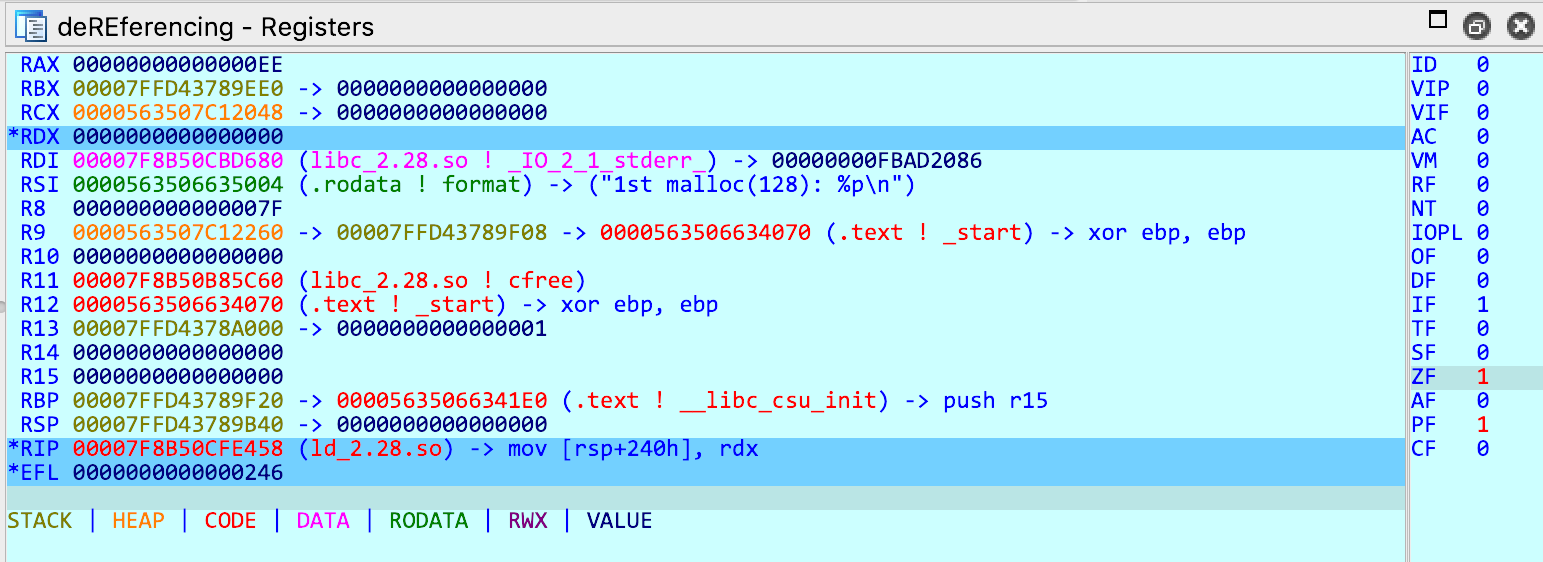 danigargu/dereferencing
IDA Pro plugin that implements more user-friendly register and stack views
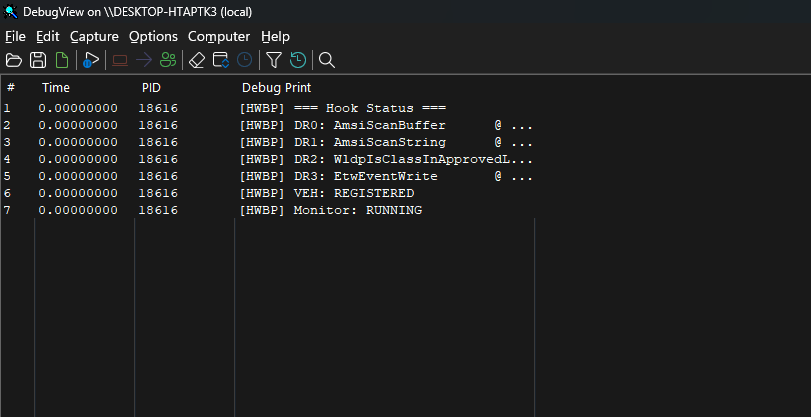 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 gilnett/wstrace
Standalone zero-driver Windows system and API monitor in Rust
 structio-labs/n0xis
Reverse-engineering toolkit: disassembler, SSA decompiler, C++ class recovery and live-process analysis for PE and ELF. Scriptable CLI, every answer…
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
 morluto/awesome-reverse-engineering
Curated reverse-engineering tools and learning resources for binaries, apps, firmware, formats, and protocols.
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…
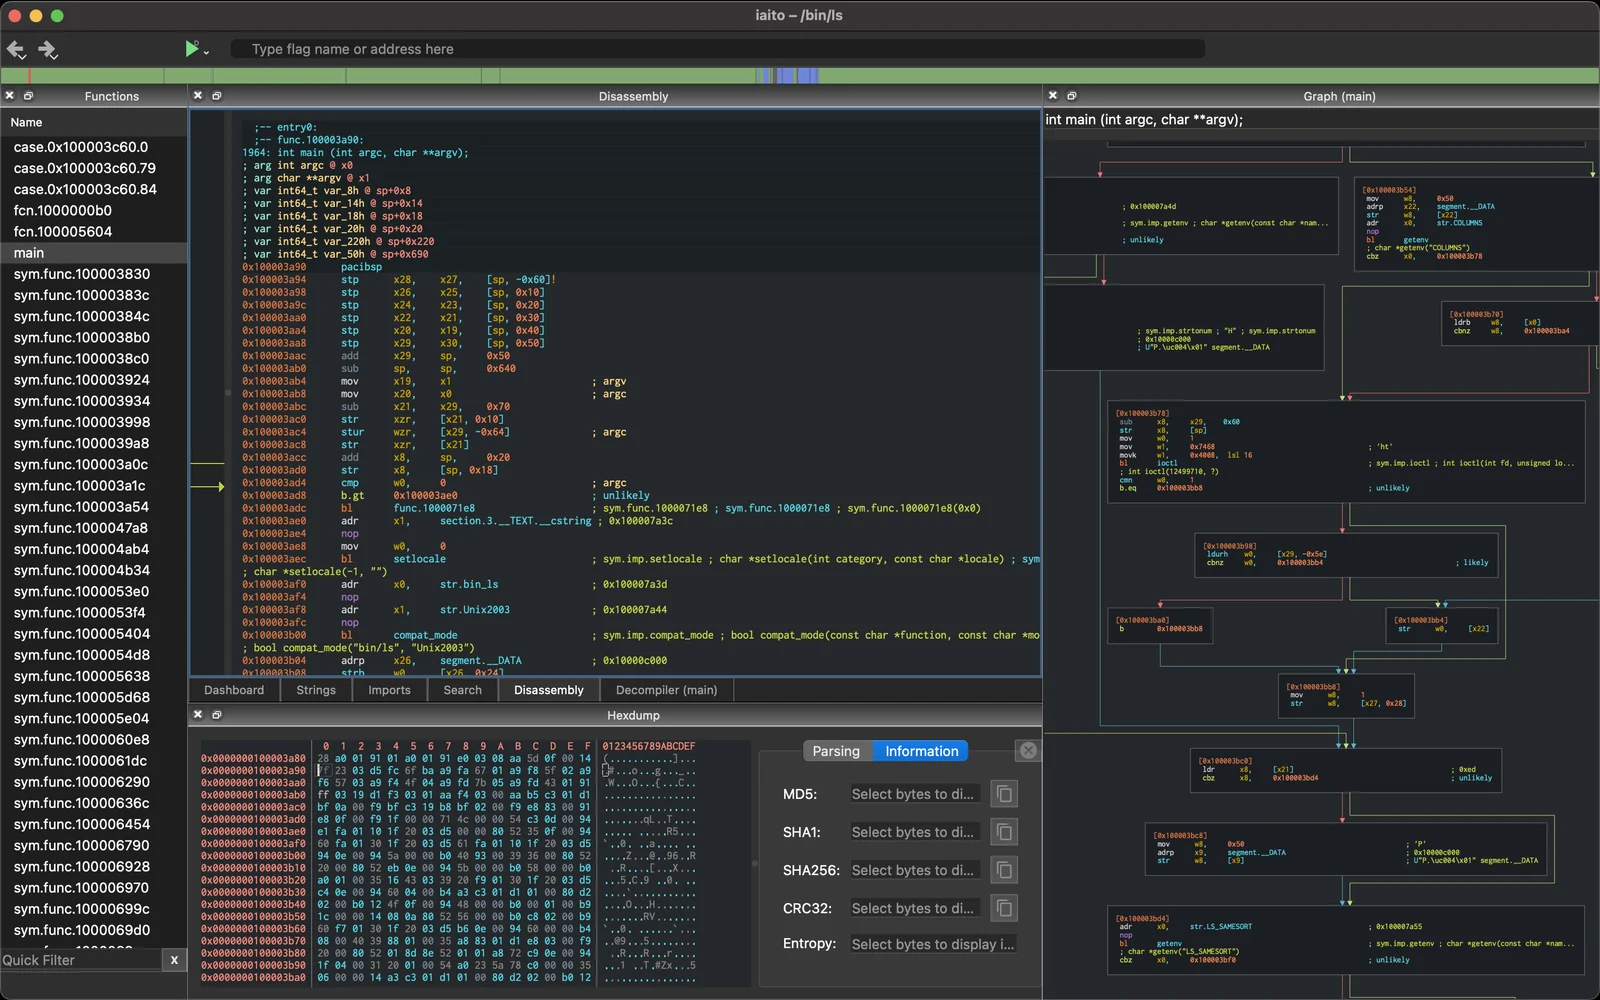 radareorg/iaito
Qt-based graphical interface for the radare2 reverse engineering framework, providing disassembly, binary analysis, debugging, patching and forensics…
 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…