Amadey-Loader-Multi-Stage-Malware-with-Keylogging-Clipboard-Hijack-Privilege-Escalation-Analysis

Reverse engineering Amadey Loader with x64dbg: dynamic API resolution, token privilege escalation, keylogger hooks, clipboard capture, and…

Reverse engineering Amadey Loader with x64dbg: dynamic API resolution, token privilege escalation, keylogger hooks, clipboard capture, and…

Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…

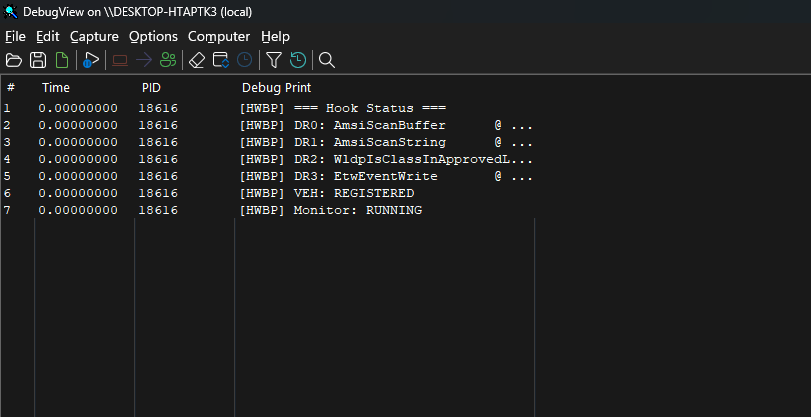
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).

N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…

Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)

Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…

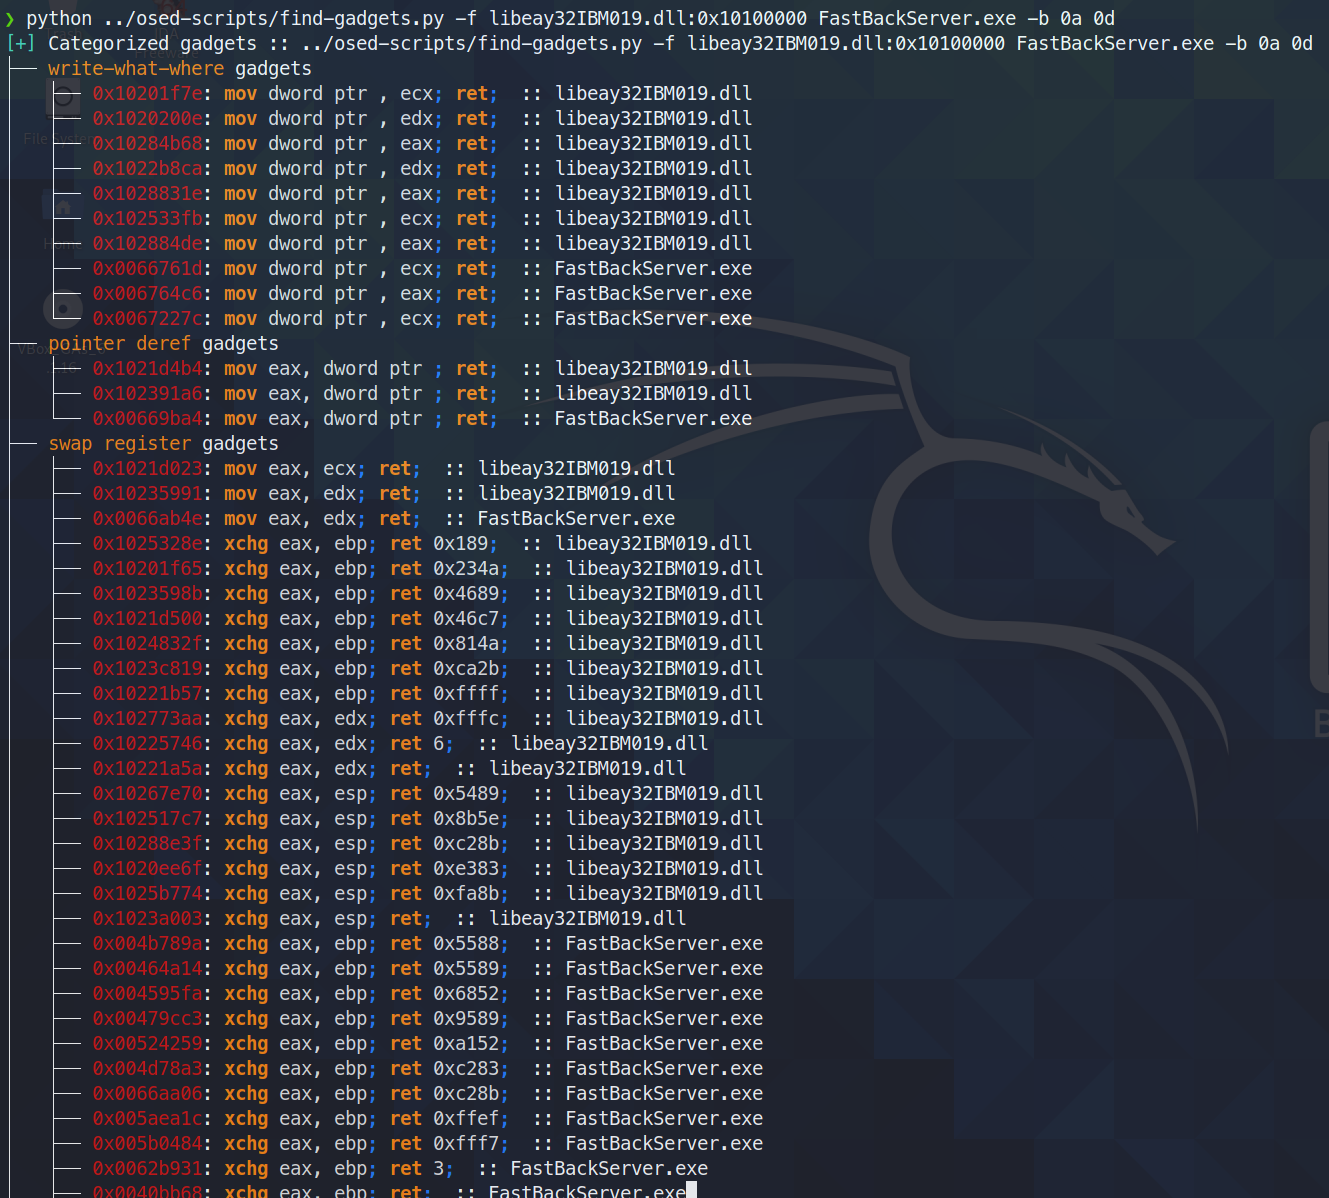
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)

Python Command-Line Ghidra MCP

Classic stack-based buffer overflow in SLMail 5.1 showing how early mail servers could be compromised through oversized SMTP and POP3 commands.

Dump cookies and credentials directly from Chrome/Edge process memory

Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.

A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.

Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU

Tiny cute emulator plugin for IDA based on unicorn.

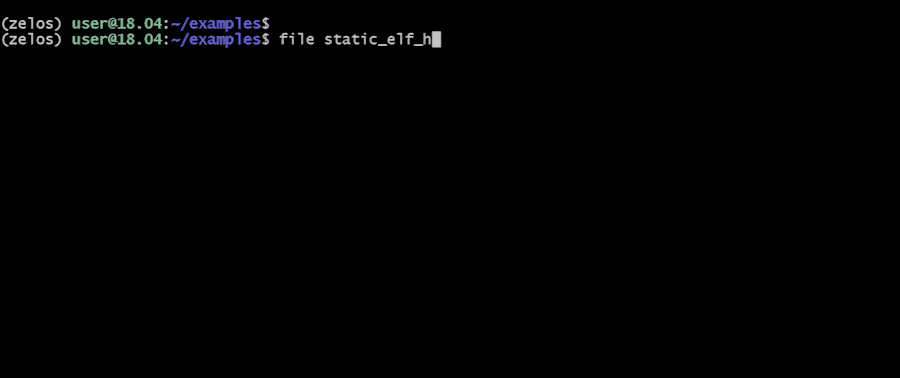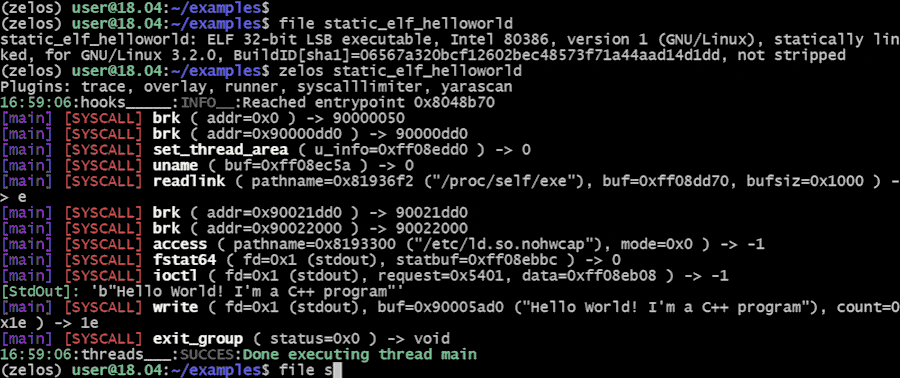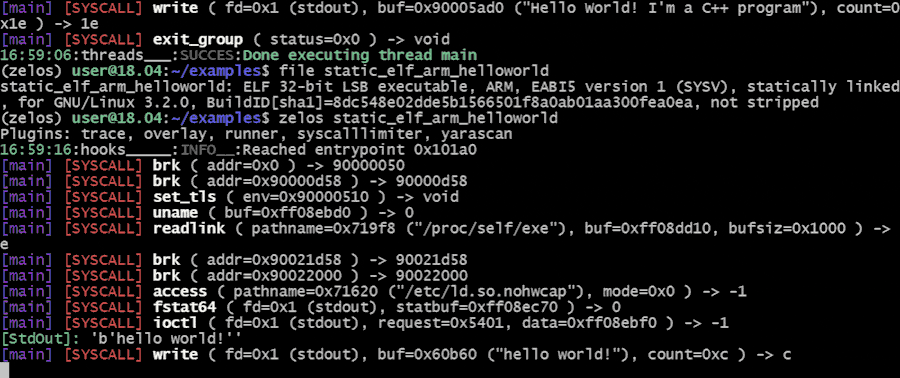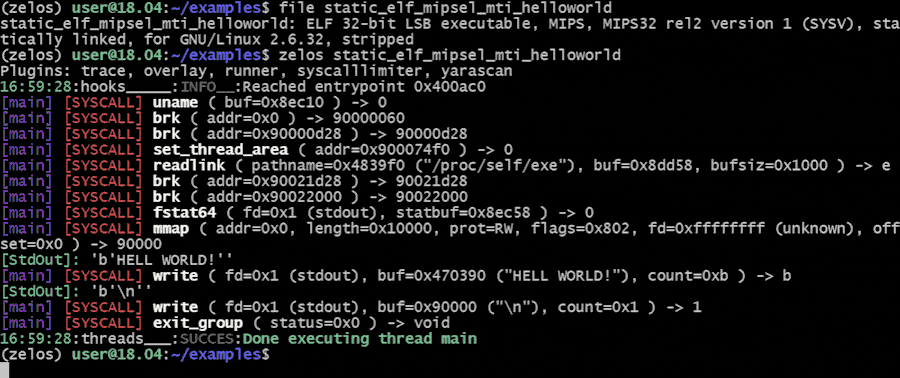
A comprehensive binary emulation and instrumentation platform.

From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)

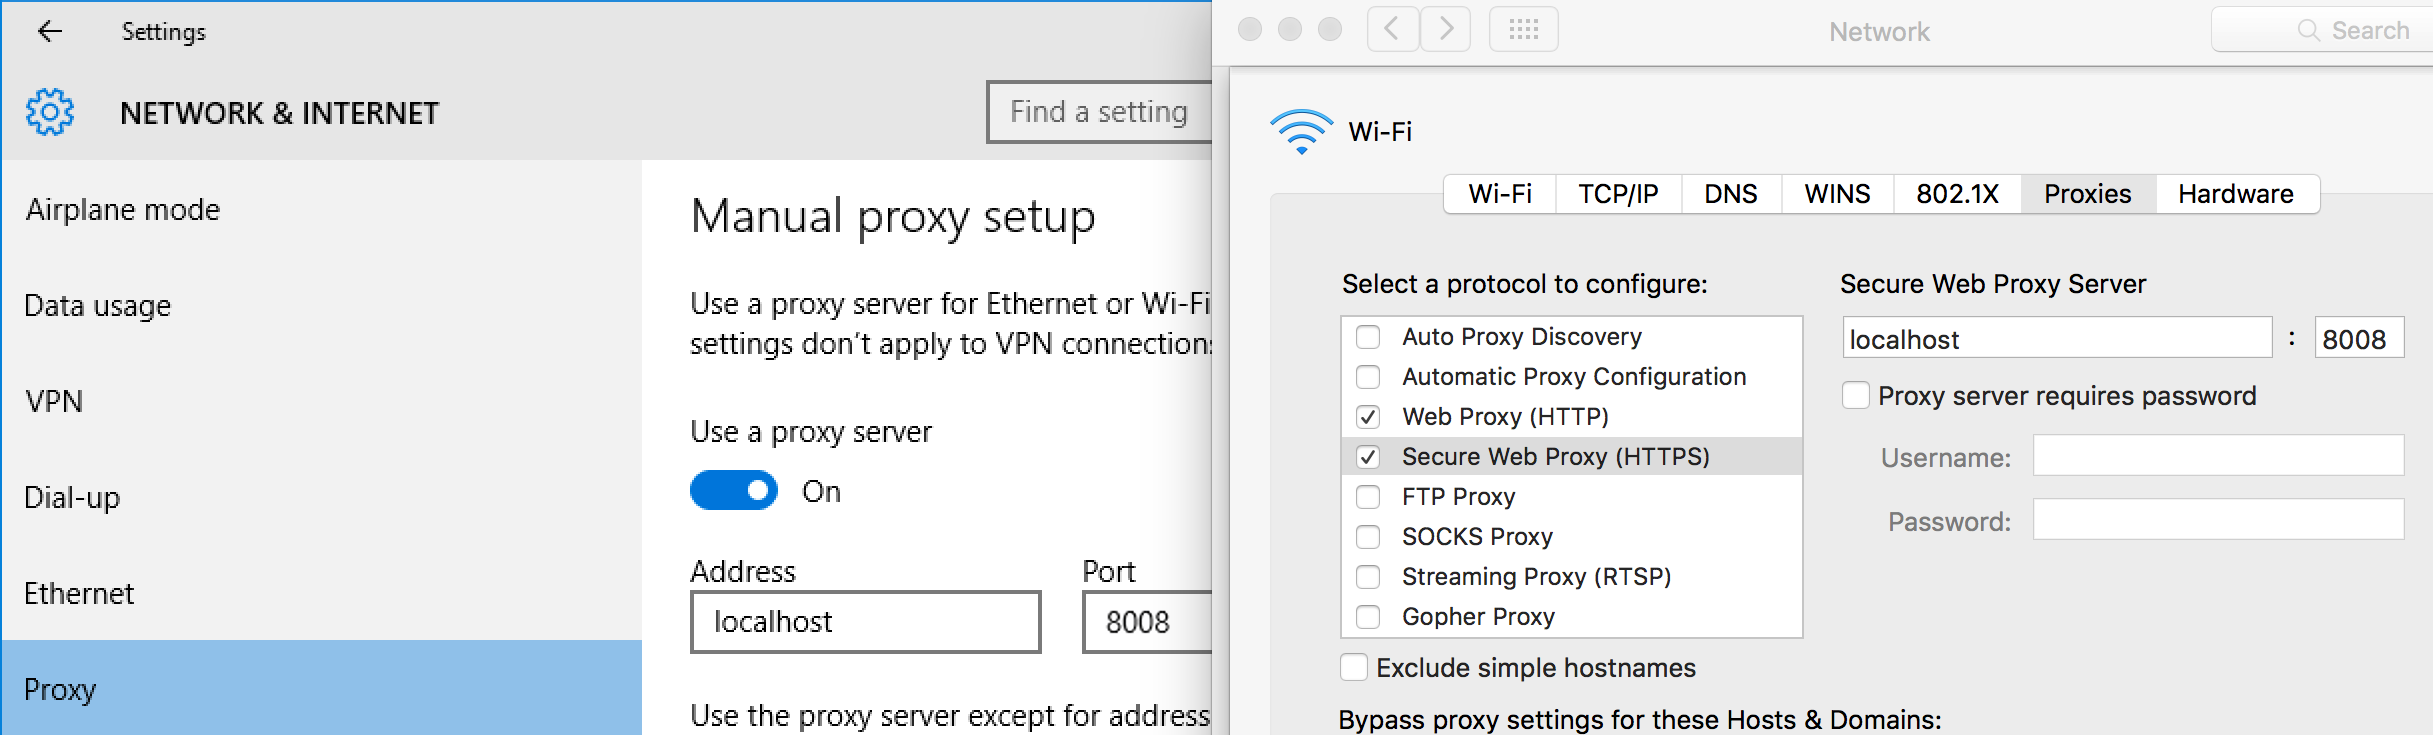
:zap: Web Debugging Proxy based on Chrome DevTools Network panel.

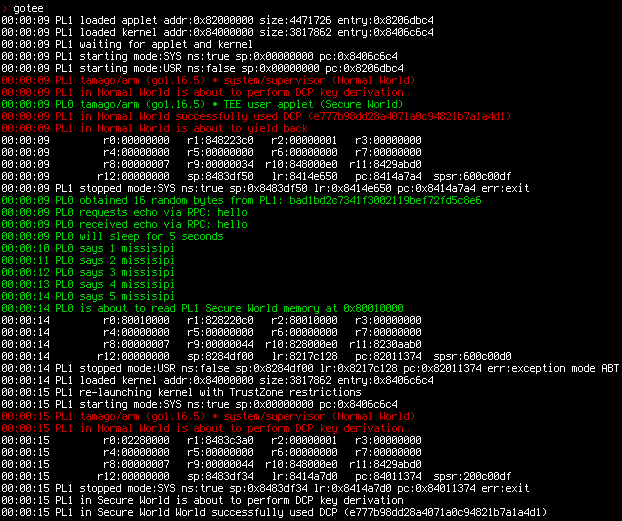
GoTEE - example application