

ceasta
 ngwg/ceasta
Disassembler, decompiler and x64dbg-style debugger for PE/ELF binaries with IDA-style listing, function graphs, Lua plugins, CLI, and a built-in MCP…
ai-assisted-reversingbinary-analysisbinary-exploitation+6
179
ngwg/ceastaDisassembler, decompiler and x64dbg-style debugger for PE/ELF binaries with IDA-style listing, function graphs, Lua plugins, CLI, and a built-in MCP…
 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
 1llu50ry/mcp-reverse
MCP server exposing 180+ reverse-engineering tools that aggregate Ghidra, IDA, x64dbg, Frida and 56 other backends with native binary parsers and a…
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 adam-atlassoftware/kraken
Reverse-engineering workbench built on Ghidra's decompiler with a native Java-free engine, AI-assisted function analysis, byte patching, sandboxed…
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 konloch/bytecode-viewer
A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 kaandemir993/amadey-loader-multi-stage-malware-with-keylogging-clipboard-hijack-privilege-escalation-analysis
Reverse engineering Amadey Loader with x64dbg: dynamic API resolution, token privilege escalation, keylogger hooks, clipboard capture, and…
 mrexodia/ida-pro-mcp
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
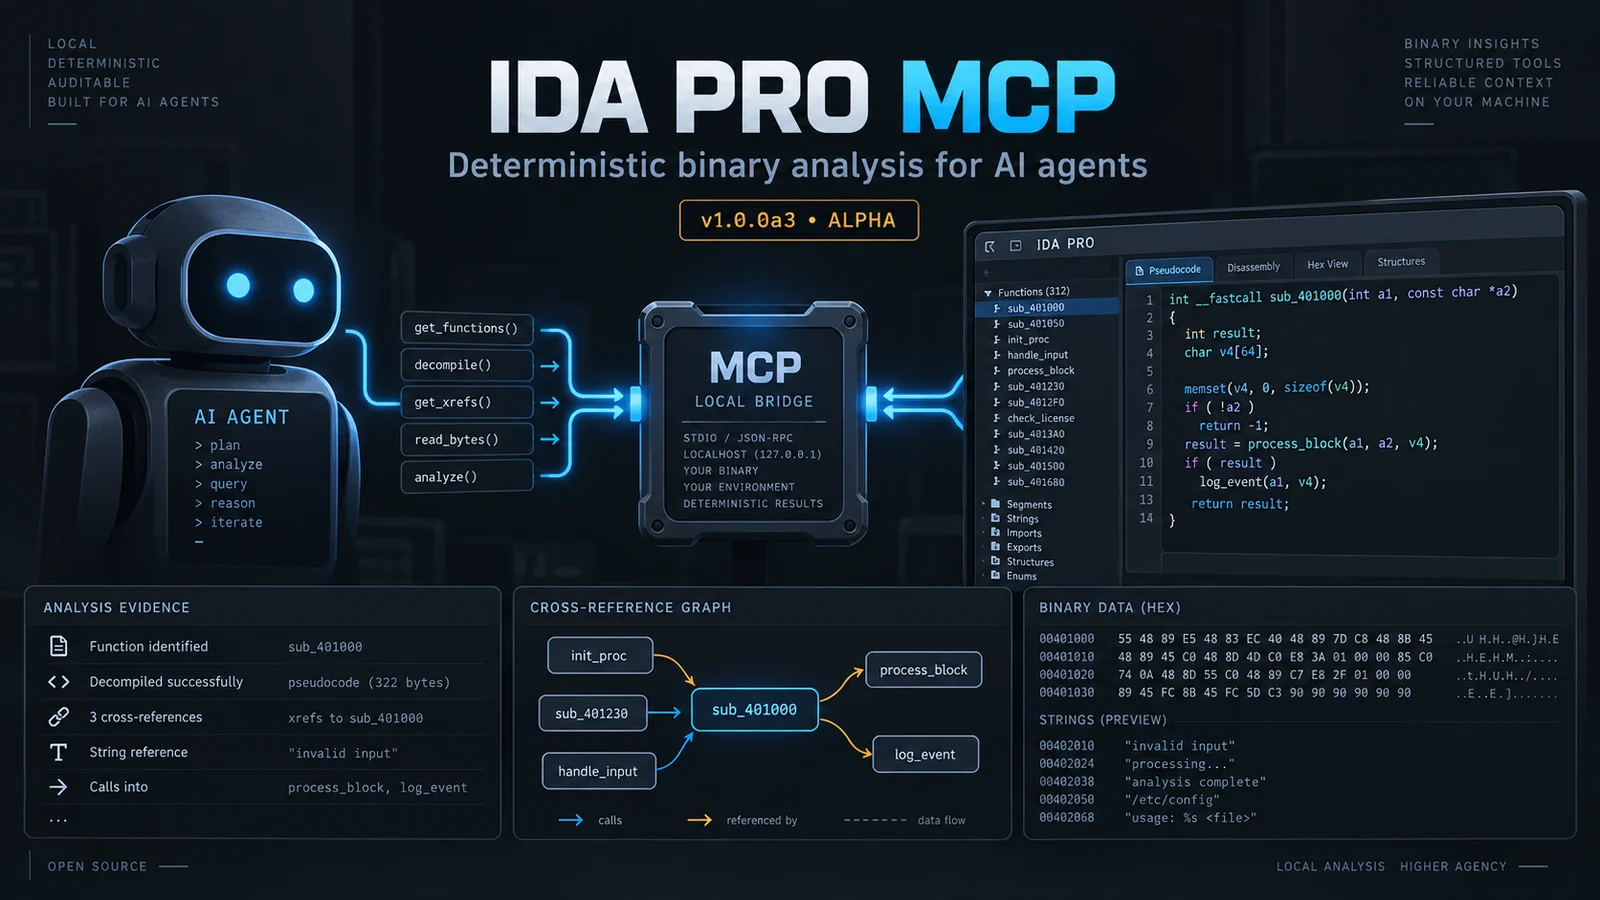 grecandrei/ida-pro-mcp
Local-first, deterministic MCP server for IDA Pro/Home: 109 strict-schema reverse-engineering operations, evidence-backed findings, and policy-gated…
 mrexodia/titanhide
Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
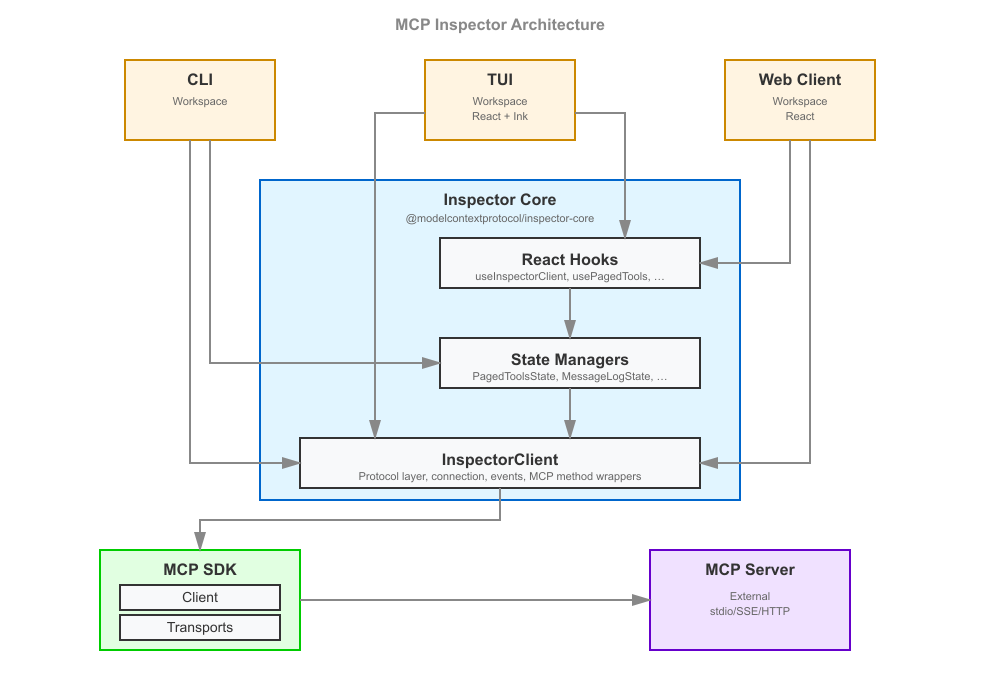 modelcontextprotocol/inspector
Inspect, debug, and visually test Model Context Protocol (MCP) servers from a web UI, CLI, or TUI, with tool/resource exploration, request logging,…