
CVE-2025-14847
 joshuavanderpoll/cve-2025-14847
CVE-2025-14847 (MongoBleed)
database-securityexploitationinformation-gathering+3
310 months ago
joshuavanderpoll/cve-2025-14847CVE-2025-14847 (MongoBleed)
 dldygnl/cve-2021-24741
Proof-of-concept exploit demonstrating multiple unauthenticated SQL injection vulnerabilities in Support Board 3.3.3, with error-based and time-based…
 0xdeku/cve-2021-42670
CVE-2021-42670 - SQL Injection vulnerability in the Engineers online portal system.
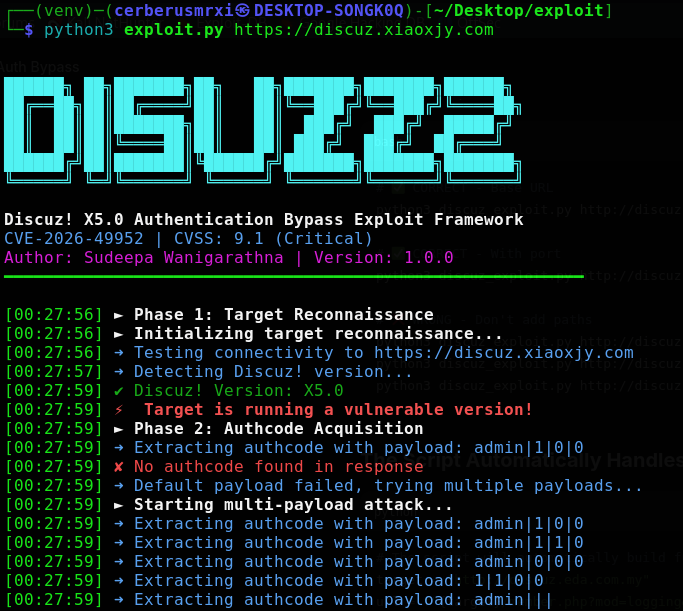 cerberusmrxi/discuz-x5.0-authentication-bypass-exploit-framework
Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…
 0xdeku/cve-2021-42667
CVE-2021-42667 - SQL Injection vulnerability in the Online event booking and reservation system.
 nu1l0/cve-2024-46636-sqli-modaps
SQL Injection vulnerability in NASA EOSDIS MODAPS due to improper input validation in the `category` parameter. This flaw allows attackers to…
 nma-io/mongobleed
golang test tool for mongobleed (cve-2025-14847)
 v1c0mmrt/redis-cve-2026-23479-scanner
CVE-2026-23479 Redis Use-After-Free vulnerability detection tool
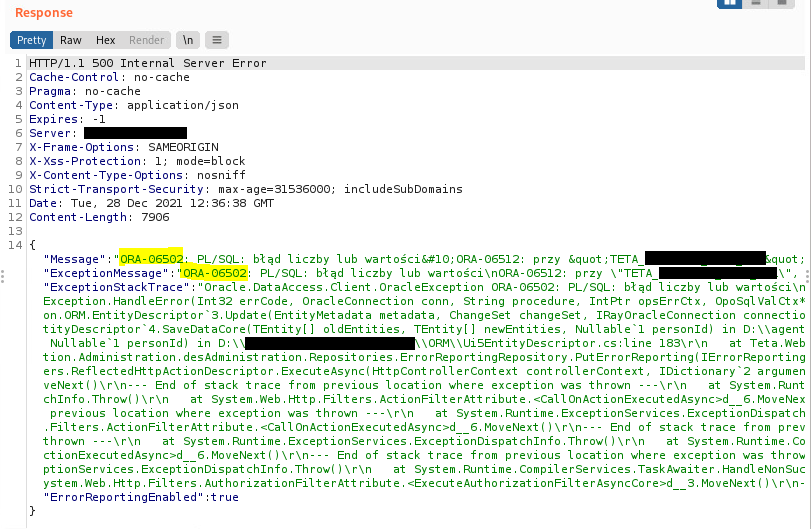 longwayhomie/cve-2022-27434
UNIT4 TETA Mobile Edition 29HF13 was discovered to contain a SQL injection vulnerability via the ProfileName parameter in the errorReporting page.
 chrissub08/cve-2026-29187_sqlinjectionvulnerabilityopenemr7.0.4
CVE-2026-29187: SQL Injection Vulnerability in OpenEMR <8.0.0.3
 eyodav/cve-2025-34226
OpenPLC Runtime suffers from a persistent denial of service (DoS) vulnerability in the /upload-program-action endpoint.
 sakthivel10q/sakthivel10q.github.io
🛠 Exploit the CVE-2025-14847 MongoDB vulnerability to reveal sensitive information through crafted zlib-compressed packets and real-time output.
 huangyanqwq/cve-2023-49496_poc
Proof-of-concept exploit for CVE-2023-49496, demonstrating SQL injection in UCServer via the /login/wwx_corpInfo/ endpoint to extract sensitive…
 0xdeku/cve-2021-42666
CVE-2021-42666 - SQL Injection vulnerability in the Engineers online portal system.
 geraldoalcantara/cve-2023-49968
Customer Support System 1.0 - SQL Injection Vulnerability in manage_department.php via "id" URL Parameter
 bde574786/sequelize-1day-cve-2023-25813
Proof-of-concept and technical analysis of CVE-2023-25813, a SQL injection vulnerability in Sequelize ORM versions prior to 6.19.1, including…
 sshipanoo/cve-2024-44542
Documentation of a SQL injection vulnerability in Todesk v1.1 via the title parameter, enabling remote information disclosure through crafted URL…
 oiyl/cve-2025-46171
Writeup of a Denial of Service vulnerability in the vBulletin 3.8.7 friends list.