
msdat
 quentinhardy/msdat
MSDAT: Microsoft SQL Database Attacking Tool
database-securityexploitationinformation-gathering+3
quentinhardy/msdatMSDAT: Microsoft SQL Database Attacking Tool
 paulsec/hqlmap
(Deprecated) HQLmap, Automatic tool to exploit HQL injections
 cve-search/cve-search
Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
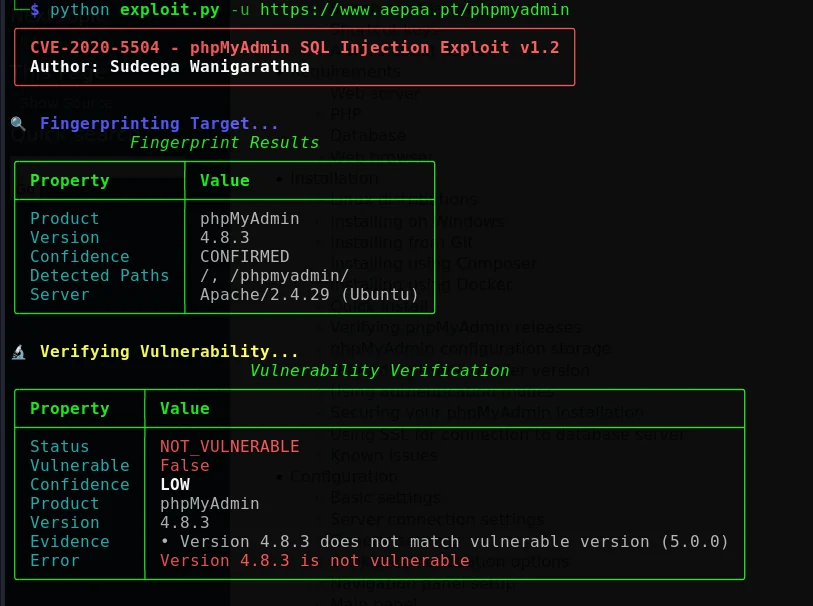 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
 torque59/nosql-exploitation-framework
A Python Framework For NoSQL Scanning and Exploitation
 woj-ciech/leaklooker
Find open databases - Powered by Binaryedge.io
 ddrvahandzo90-hue/cve-2026-42031-sql-injection-scanner
Automated SQL injection scanner for CKAN DataStore, detecting and validating CVE-2026-42031 with multi-target scanning, data dumping, and report…
 synacktiv/sccmsqlclient
MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
 vighneshnair7/cve-2024-48427
Proof-of-concept for CVE-2024-48427: SQL injection in Sourcecodester Packers and Movers Management System v1.0. Exploits the id parameter to execute…
 0xwhoami35/cve-2024-4879
Exploit script for ServiceNow CVE-2024-4879 that enables unauthenticated remote code execution, with mass target scanning and database dumping…
 aboutcode-org/vulnerablecode
Open-source vulnerability database aggregating CVE data from multiple sources with a web UI and API. Maps vulnerabilities to specific software…
 gobysec/cve-2023-1454
Proof-of-concept exploit for CVE-2023-1454, an unauthenticated SQL injection vulnerability in JeecgBoot v3.5.0, enabling database extraction and…
 fantasy-fql/esapi-sqlinjection-cve-2025-5878-exploit
Exploit for CVE-2025-5878 targeting ESAPI's encodeForSQL() method with OracleCodec, enabling time-based blind SQL injection. Supports database…
 iltosec/cve-2026-54596
Proof-of-concept exploit for CVE-2026-54596: authenticated SQL injection in ITFlow's recurring_invoice_frequency parameter enabling full database…
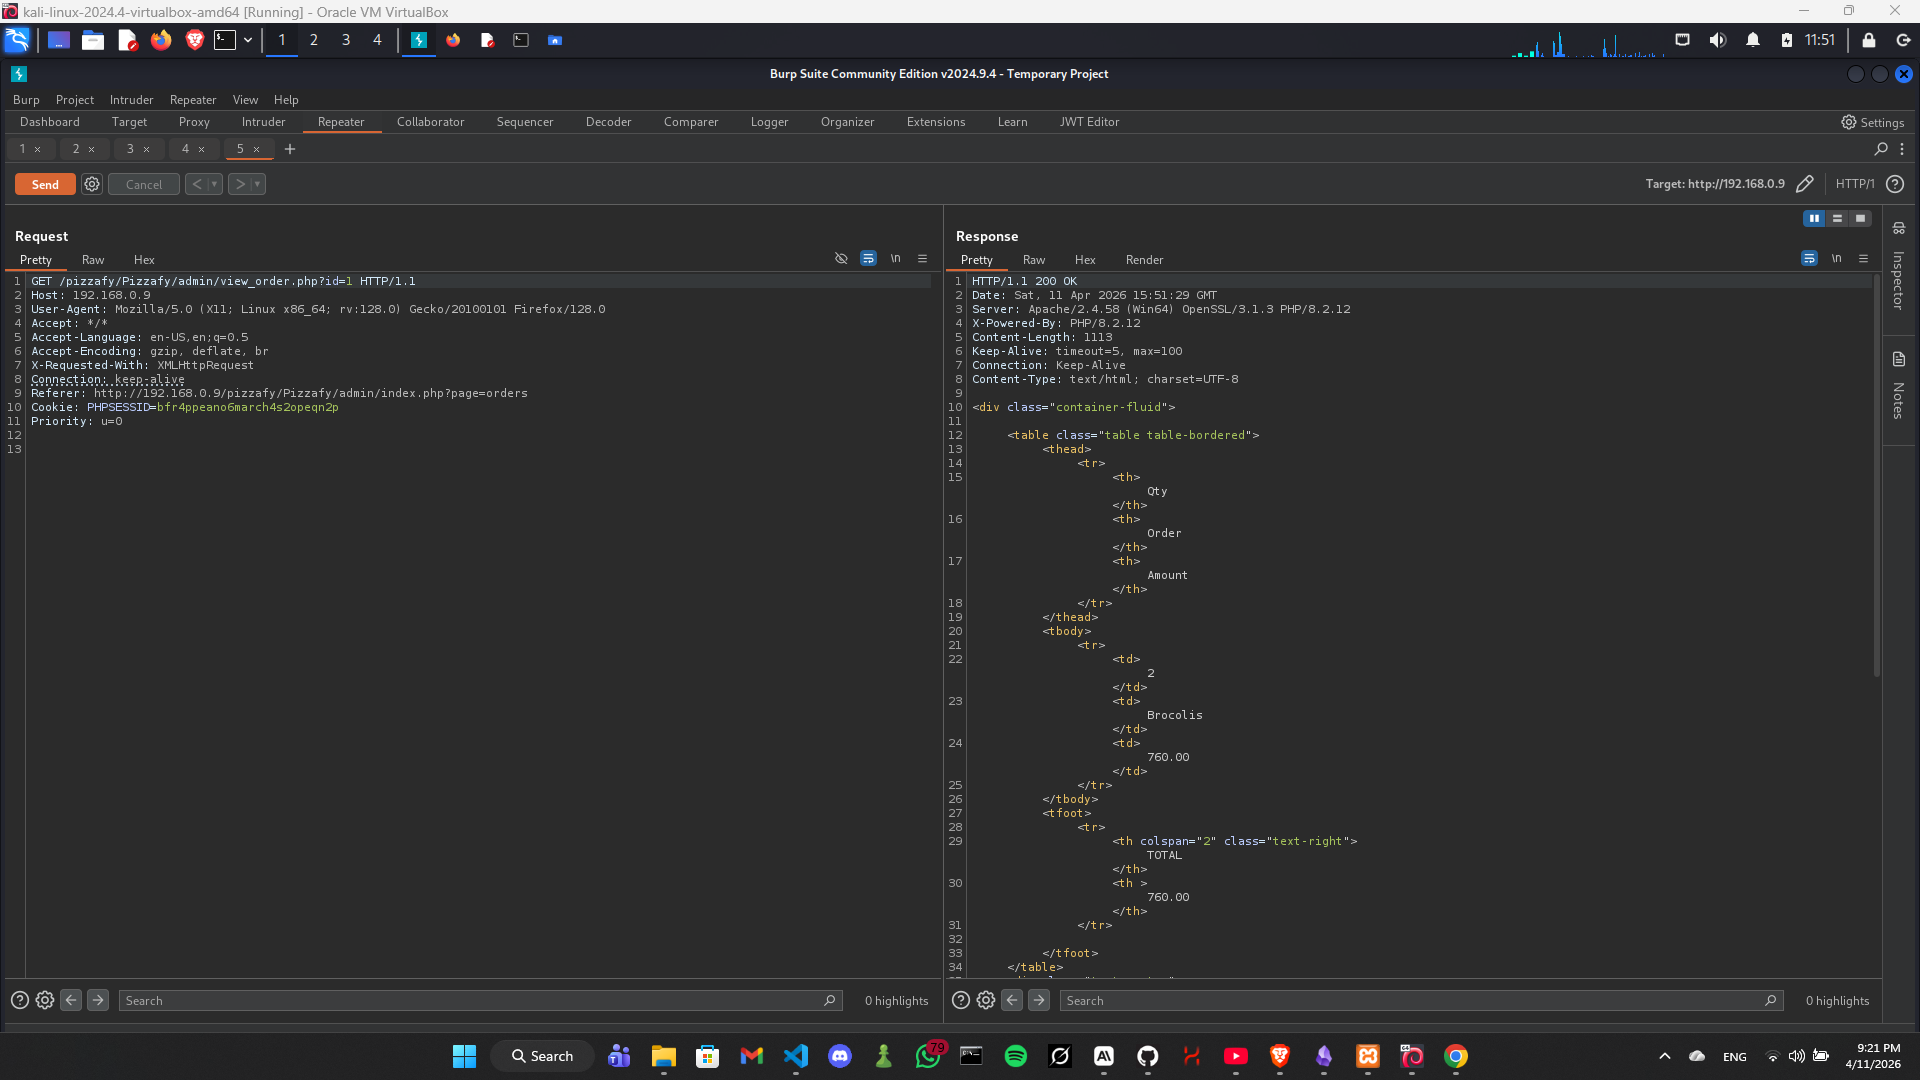 xmyronn/cve-2026-7394-sqli
Proof-of-concept exploit for CVE-2026-7394, a SQL injection vulnerability in SourceCodester Pizzafy Ecommerce System 1.0. Demonstrates authenticated…
 emad-almousa/cve-2021-2173
Proof-of-concept exploit for CVE-2021-2173, demonstrating Oracle Database metadata exposure via broken PDB isolation. Includes technical details and…
 daeseong1209/cve-2024-31449
Proof-of-concept exploit for CVE-2024-31449, a stack buffer overflow in Redis Lua engine via bit.tohex, enabling denial-of-service and potential…
 emad-almousa/cve-2023-22074
Proof-of-concept exploit for CVE-2023-22074, an Oracle Database Sharding component vulnerability enabling password hash exposure in versions 19c,…