
CVE-2025-14847
 sakthivel10q/cve-2025-14847
🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…
database-securityexploitationinformation-gathering+3
1
sakthivel10q/cve-2025-14847🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…
 pedrocruz2202/mongobleed-scanner
🔍 Scan for MongoDB vulnerabilities with MongoBleed, a high-performance tool for detecting CVE-2025-14847 across large networks quickly and…
 aboutcode-org/vulnerablecode
Open-source vulnerability database aggregating CVE data from multiple sources with a web UI and API. Maps vulnerabilities to specific software…
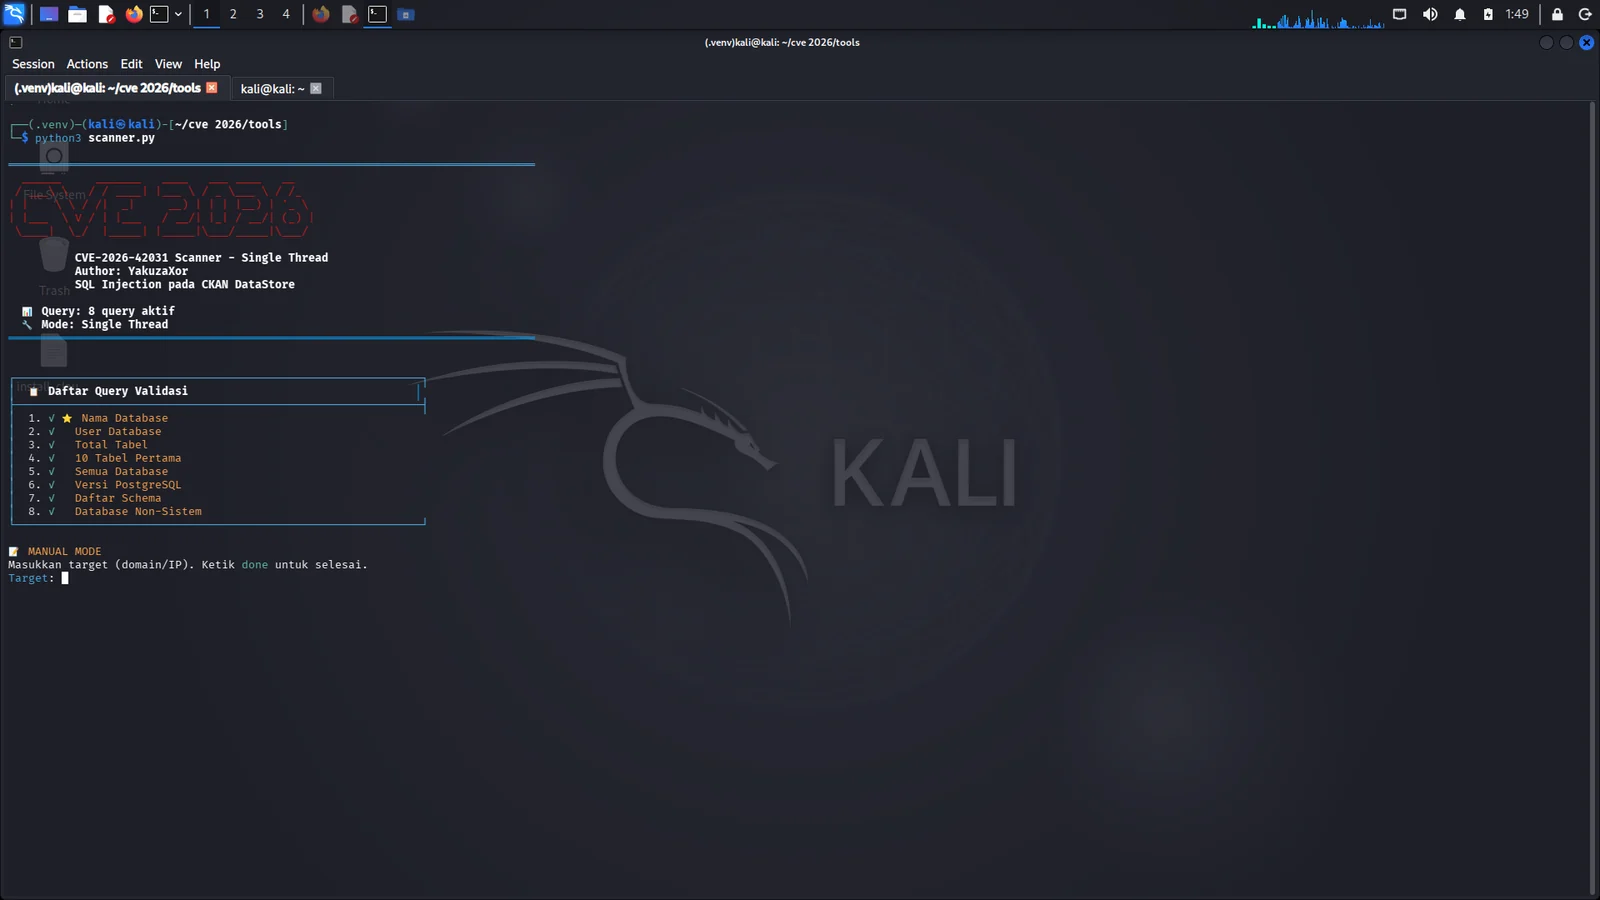 ddrvahandzo90-hue/cve-2026-42031-sql-injection-scanner
Automated SQL injection scanner for CKAN DataStore, detecting and validating CVE-2026-42031 with multi-target scanning, data dumping, and report…
 sw33tlie/bbscope
Scope aggregation tool for HackerOne, Bugcrowd, Intigriti, YesWeHack, and Immunefi!
 cve-search/cve-search
Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
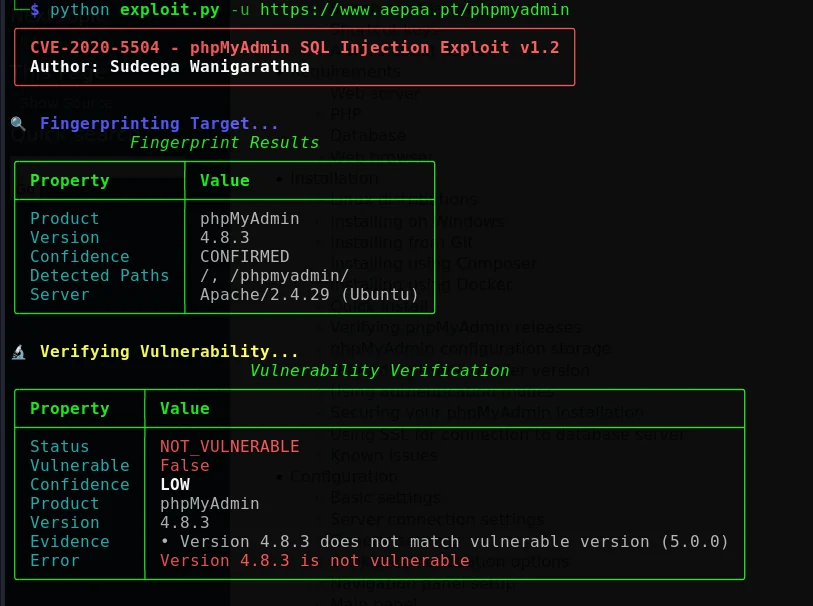 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
 adarshthakur14777-cyber/cve-2026-60137
wpsqli full SQLi extractor + dumper for CVE-2026-60137
 tc4dy/cve-2026-14762-poc-exploit
Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…
 n0bitaemon/cve-2026-26980-poc
Ghost CMS Content API Blind SQL Injection
 tjnull/cygor
An modular asset discovery framework written in python to automate the repeating manual work
 skahwah/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 iltosec/cve-2026-54596
Proof-of-concept exploit for CVE-2026-54596: authenticated SQL injection in ITFlow's recurring_invoice_frequency parameter enabling full database…
 fantasy-fql/esapi-sqlinjection-cve-2025-5878-exploit
Exploit for CVE-2025-5878 targeting ESAPI's encodeForSQL() method with OracleCodec, enabling time-based blind SQL injection. Supports database…
 synacktiv/sccmsqlclient
MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
 strobelpierre/cve-2026-9082
Semi-passive scanner that detects Drupal installations vulnerable to CVE-2026-9082 (PostgreSQL SQL injection) via fingerprinting, version detection,…