

Wormy
 d4vinci/wormy
some python3 functions to add spreading features to any python backdoor
command-and-controldata-exfiltrationlateral-movement+3
d4vinci/wormysome python3 functions to add spreading features to any python backdoor
 viralmaniar/powershell-rat
Python based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
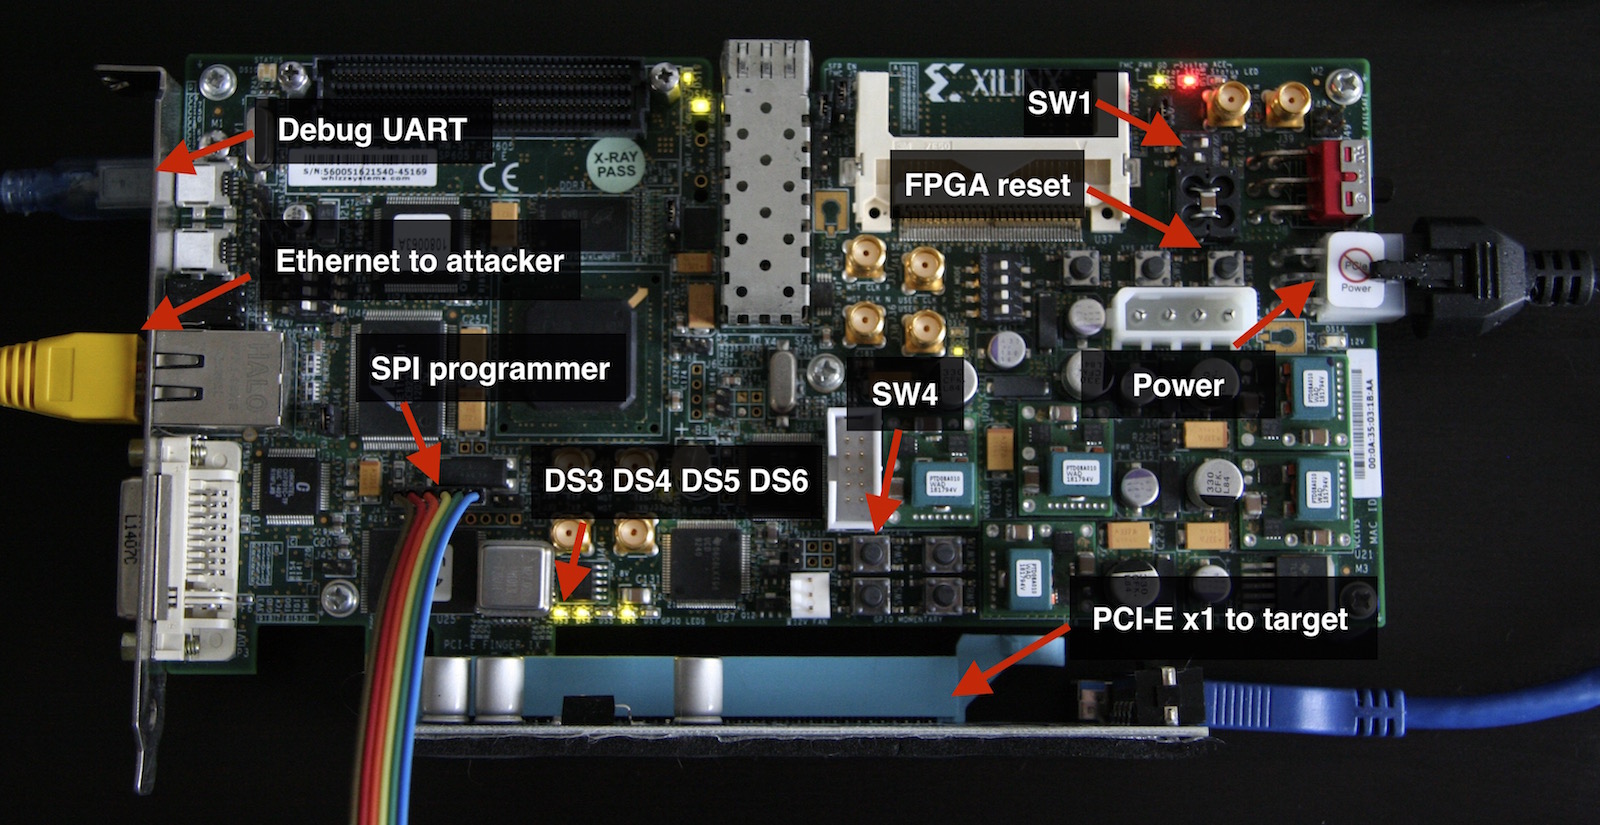 cr4sh/s6_pcie_microblaze
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info
 4n4nk3/tinkerershell
A simple python reverse shell written just for fun.
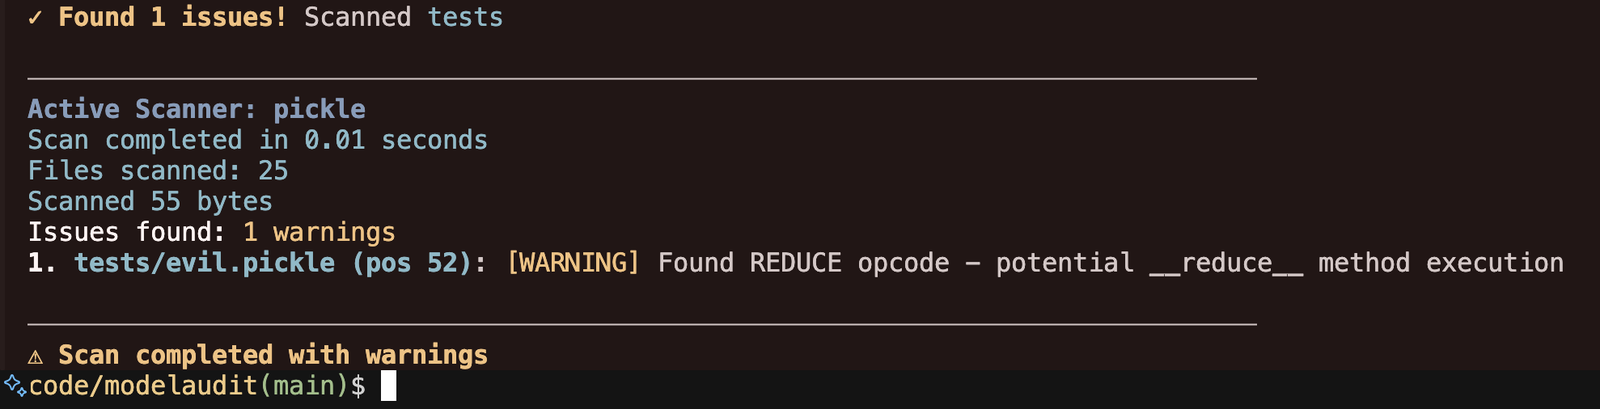 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 imcpwn/browser-backdoor
BrowserBackdoor is an Electron Application with a JavaScript WebSocket Backdoor and a Ruby Command-Line Listener
 thatcherclough/betterbackdoor
A backdoor with a multitude of features.
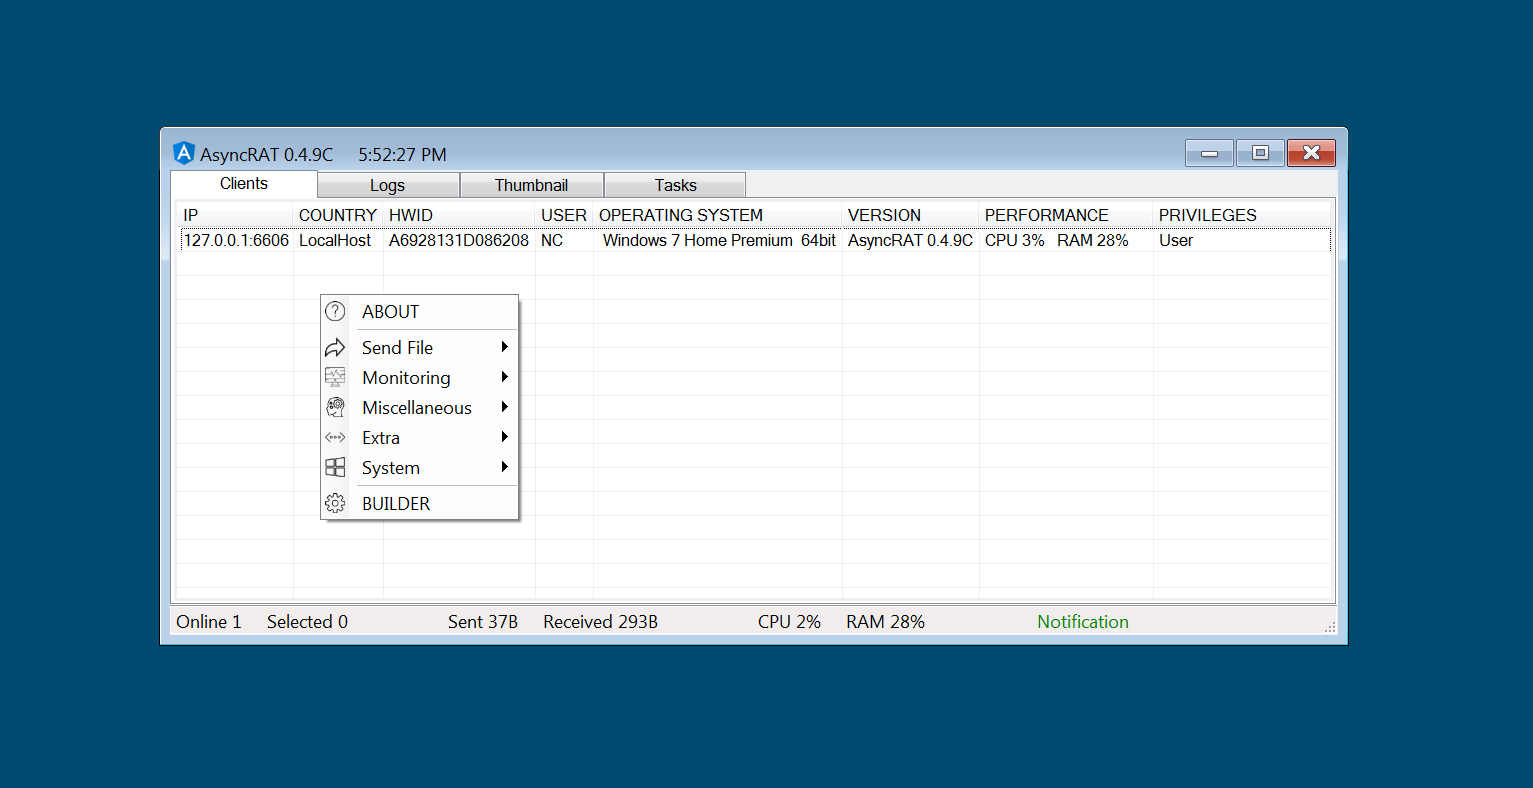 nyan-x-cat/asyncrat-c-sharp
Open-Source Remote Administration Tool For Windows C# (RAT)
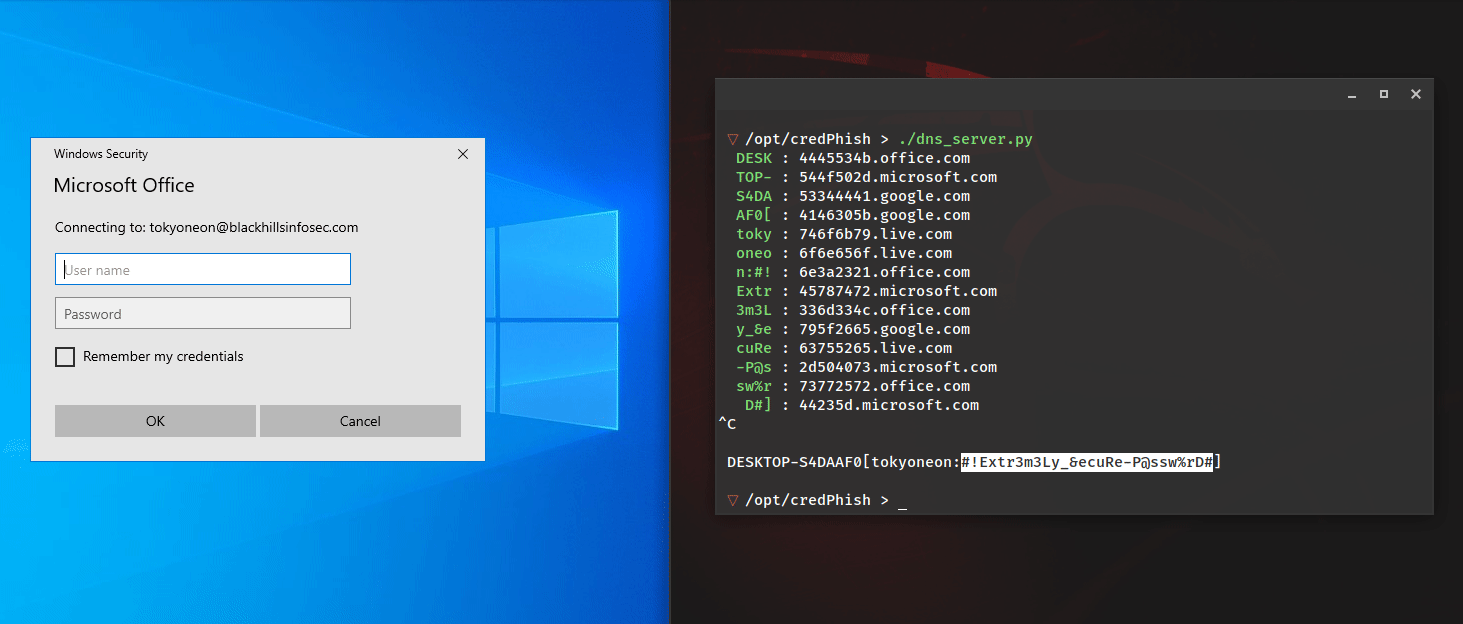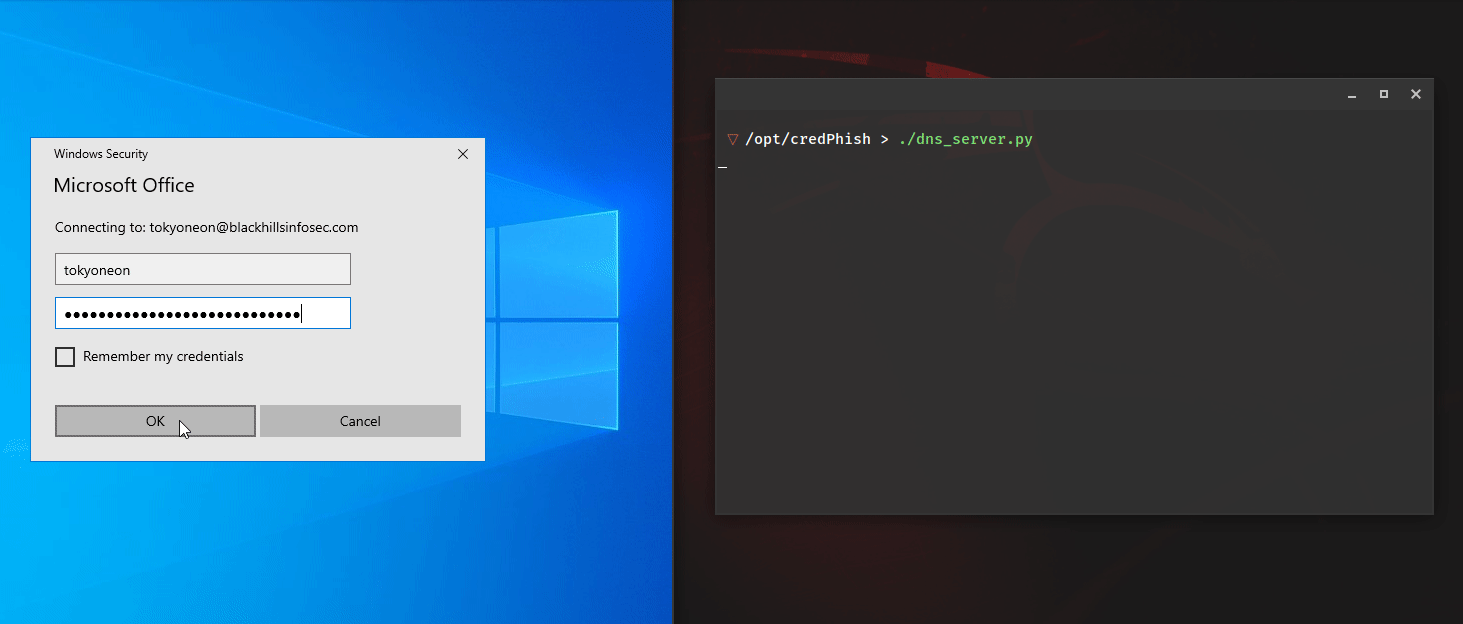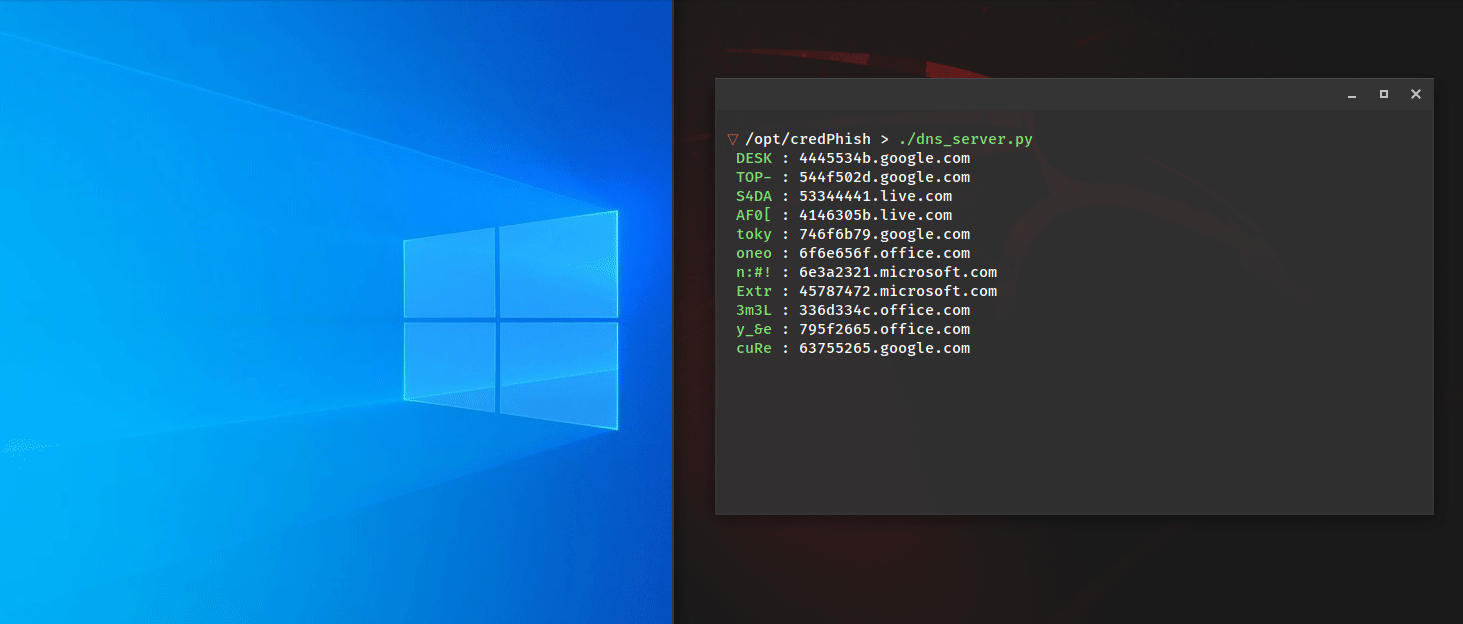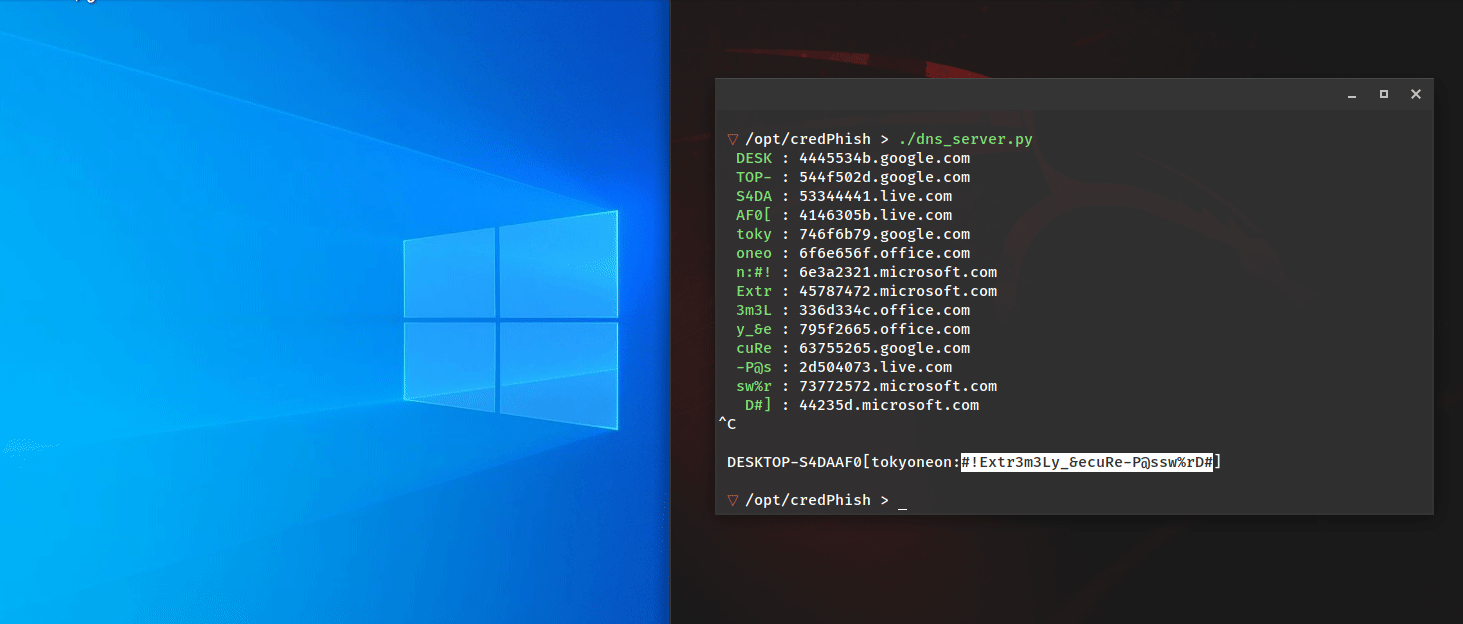 tokyoneon/credphish
PowerShell script that invokes legitimate credential prompts and exfiltrates captured passwords over DNS using CredentialPicker and Resolve-DnsName.
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 r3dteam/casper-shell
Casper@shell:~# is an enhanced, more user-friendly version of p0wny shell with many new features.
 qwqdanchun/dcrat
A simple remote tool in C#.
 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 samyk/poisontap
Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…
 ethicalhackinglabs/metasploitable2-exploitation-metasploit
Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration,…
 nicetop1027/cve-2026-discord
Critical vulnerability report detailing zero-day Remote Debugging Port exposure in Discord macOS client leading to account takeover, spyware, worm…