
 xsanflip/begal-c2
Flask and Socket.IO command-and-control panel with a rogue browser extension agent that harvests credentials, exfiltrates files via Telegram, and issues remote webcam, screenshot, and mic commands.

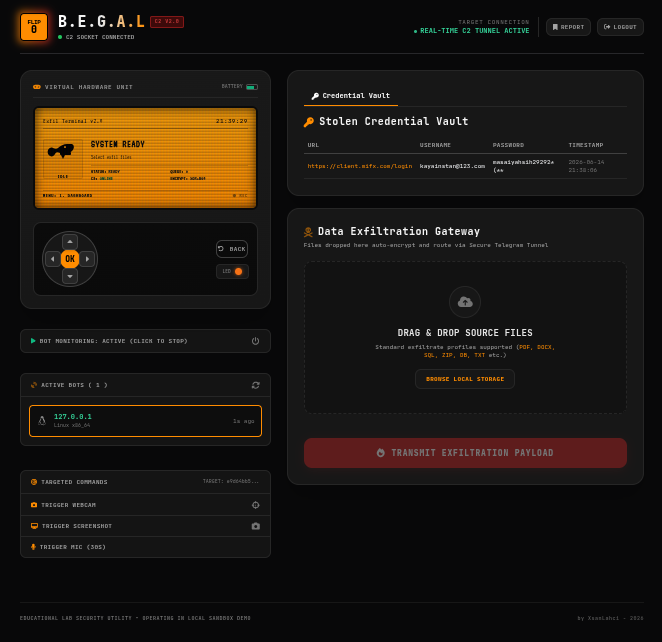
B.E.G.A.L (Backdoor Exfiltration Gateway for Advanced Looting) is an interactive, web-based Command and Control (C2) panel built with Python (Flask & Socket.IO). This platform is specifically designed to facilitate cybersecurity research, Red Teaming simulations, and educational purposes to understand how modern malware/botnets operate in exfiltrating data and controlling targets (bots) remotely.
THIS PROJECT WAS CREATED SOLELY FOR EDUCATIONAL AND CYBERSECURITY RESEARCH PURPOSES.
Any misuse of this tool for illegal activities, unauthorized system attacks, data theft, or other cybercrimes is STRICTLY PROHIBITED. The author, developers, and contributors bear no responsibility for any losses, damages, or legal actions arising from the use of this software.
You are entirely responsible for your own actions. By using this tool, you agree to abide by all applicable laws:
config.yaml file for better security and easier customization.Trigger Webcam (Access target's camera)Trigger Screenshot (Capture target's desktop screen)Trigger Mic (Record target's audio)/report).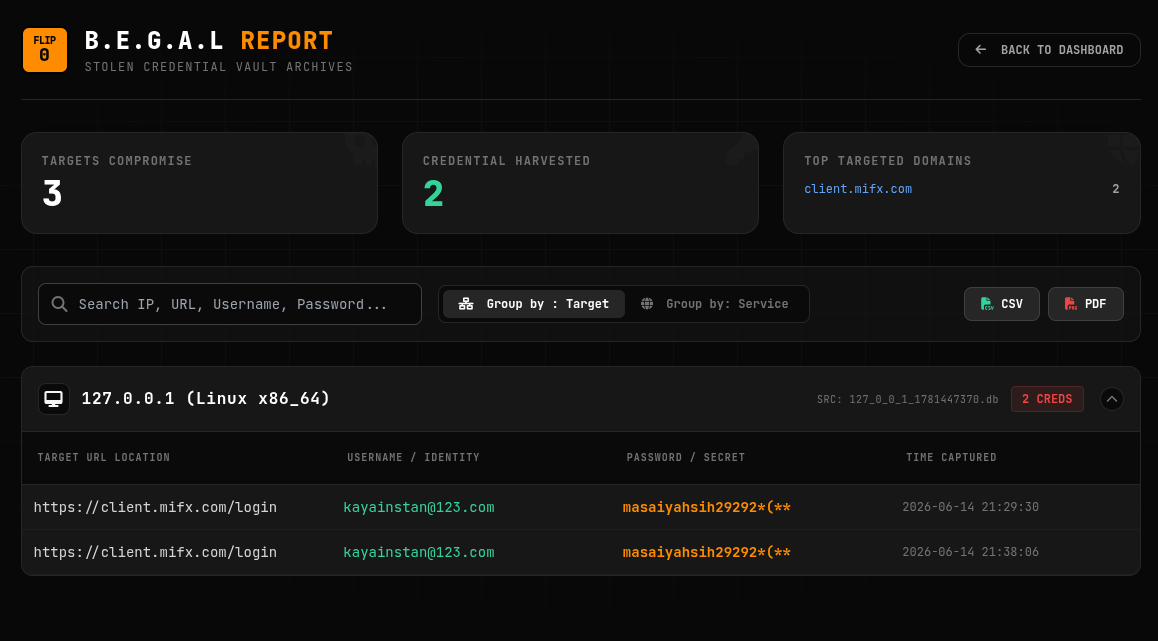
config.yaml)In the latest version of B.E.G.A.L, the settings system has been made dynamic using a YAML configuration file. If this file does not exist, the system will automatically generate it (with default values) the first time begal-fixed.py is run.
Open the config.yaml file created in the same directory and adjust the following parameters:
BOT_TOKEN: 'YOUR_BOT_TOKEN'
CHAT_ID: 'YOUR_CHAT_ID'
XOR_KEY: 'FLIPPER_SECURE_XOR_KEY_1337'
BCRYPT_PASSWORD_HASH: '$2a$12$VZnosb4amZbO1uQ4MniFhuFiqZVEmCF.3p1jXVoiXnG/3oztPLdxe'
BOT_TOKEN: The API Token for your Telegram bot (create one via @BotFather).CHAT_ID: The ID of the Telegram channel/group used as the data exfiltration tunnel.XOR_KEY: A symmetric cryptographic key used to obfuscate data transmission between the bot and the C2 server. Ensure this value matches the one in the browser extension.BCRYPT_PASSWORD_HASH: The hash for C2 login (Default password: datalost1337).DEFAULT USERNAME C2: flippergaruda-vpn)B.E.G.A.L is designed to work in tandem with an "agent" or payload. In this repository, the agent takes the form of a rogue browser extension (addon) disguised as garuda-vpn.
How the Integration Works:
garuda-vpn folder contains the malicious payload (e.g., background.js, content.js, and manifest.json). This extension must be installed on the target browser (e.g., via Load unpacked mode in Chrome/Edge).garuda-vpn agent will be encrypted using the XOR_KEY and silently transmitted (beaconing) to the B.E.G.A.L C2 API endpoints (such as /api/v1/collector).garuda-vpn extension, which then forces the execution of the webcam API on the target browser.python3 begal-c2.py).chrome://extensions in the URL bar. Enable Developer Mode.garuda-vpn folder.pip install bcrypt Flask-SocketIO requests pyyaml
python3 begal-c2.py
datalost1337)