
CVE-2025-30208
 hazavvip/cve-2025-30208
Exploit scanner for CVE-2025-30208 (Vite arbitrary file read) with multi-variant bypass detection, credential harvesting, SSH key extraction, and…
data-exfiltrationexploitationinformation-gathering+3
hazavvip/cve-2025-30208Exploit scanner for CVE-2025-30208 (Vite arbitrary file read) with multi-variant bypass detection, credential harvesting, SSH key extraction, and…
 byt3bl33d3r/dnschef-ng
DNSChef (NG) - DNS proxy for Penetration Testers and Malware Analysts
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
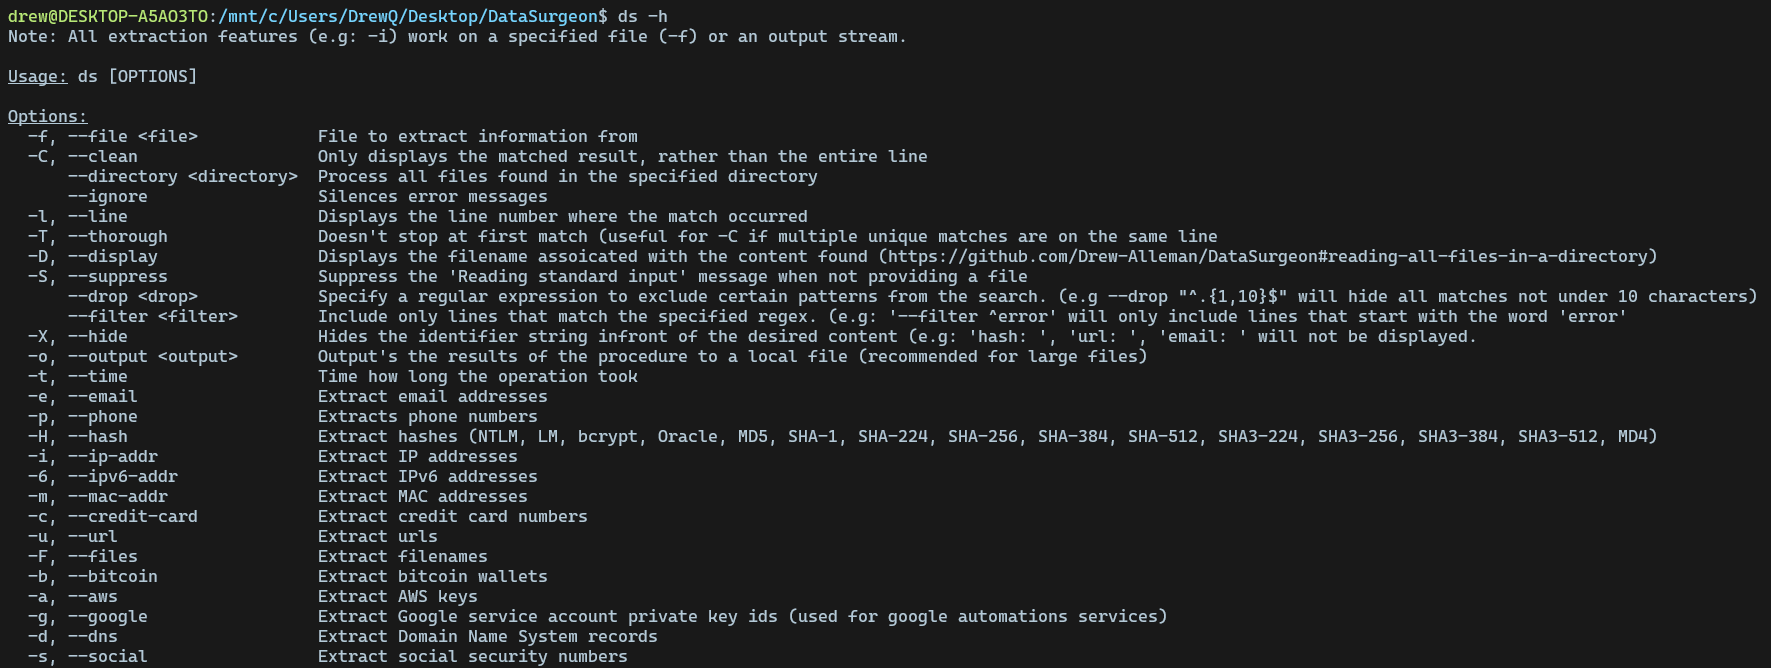 drew-alleman/datasurgeon
Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text
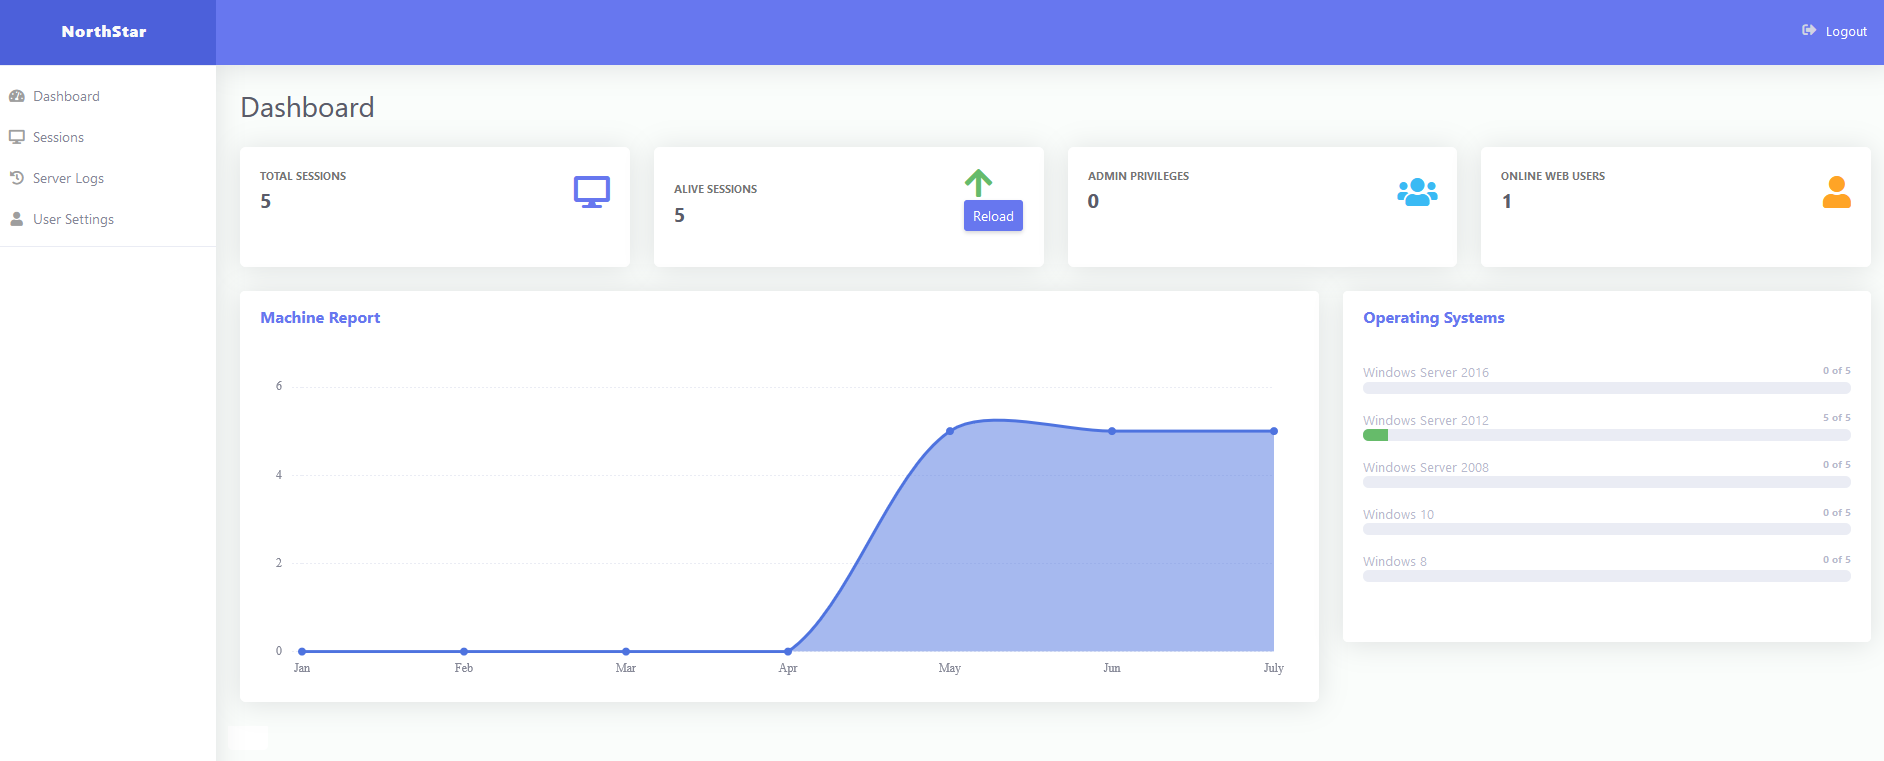 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…
 evkir/phantom-grid
Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly
 azhariramadhan/cve-2026-39047
Printer exploitation framework for security testing via raw port 9100, featuring PCL payload delivery, DoS bombing, C2 QR codes, phishing QR codes,…
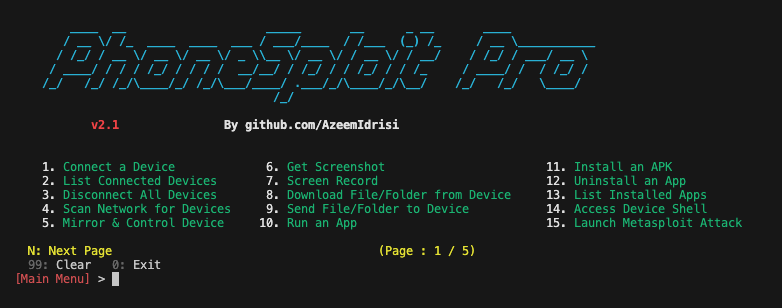 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
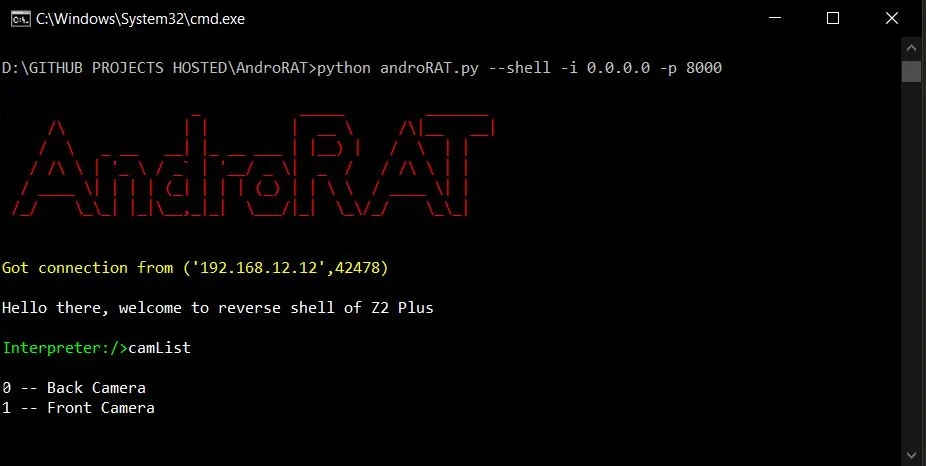 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side

 designativedave/androrat
Remote Administration Tool for Android devices
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 tomiwa-ot/moukthar
Android remote administration tool
 fs0c131y/esfileexploreropenportvuln
ES File Explorer Open Port Vulnerability - CVE-2019-6447
 mwsrc/betterandrorat
Android Remote Access Trojan
 kingofthenops/cookie-monster
BOF-based tool to extract browser cookies and credentials from Chrome, Edge, and Firefox via handle duplication and fileless download, with offline…
 nccgroup/crosssitecontenthijacking
Content hijacking proof-of-concept using Flash, PDF and Silverlight
 globalpolicy/phonemonitor
A Remote Administration Tool for Android devices