metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.

opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis

Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…

An all-in-one hacking tool to remotely take over Android devices.

Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…

PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…

Go exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE Workhorse via URL-encoding bypass, with concurrent requests and…

Source code minh họa máy chủ c2 demo kịch bản thực thi của CVE-2024-23700

Apple MacOS Screen Sharing Arbitrary File read/write -> RCE

Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…

Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly

POC of CVE-2026-51031 for arbitrary local file read

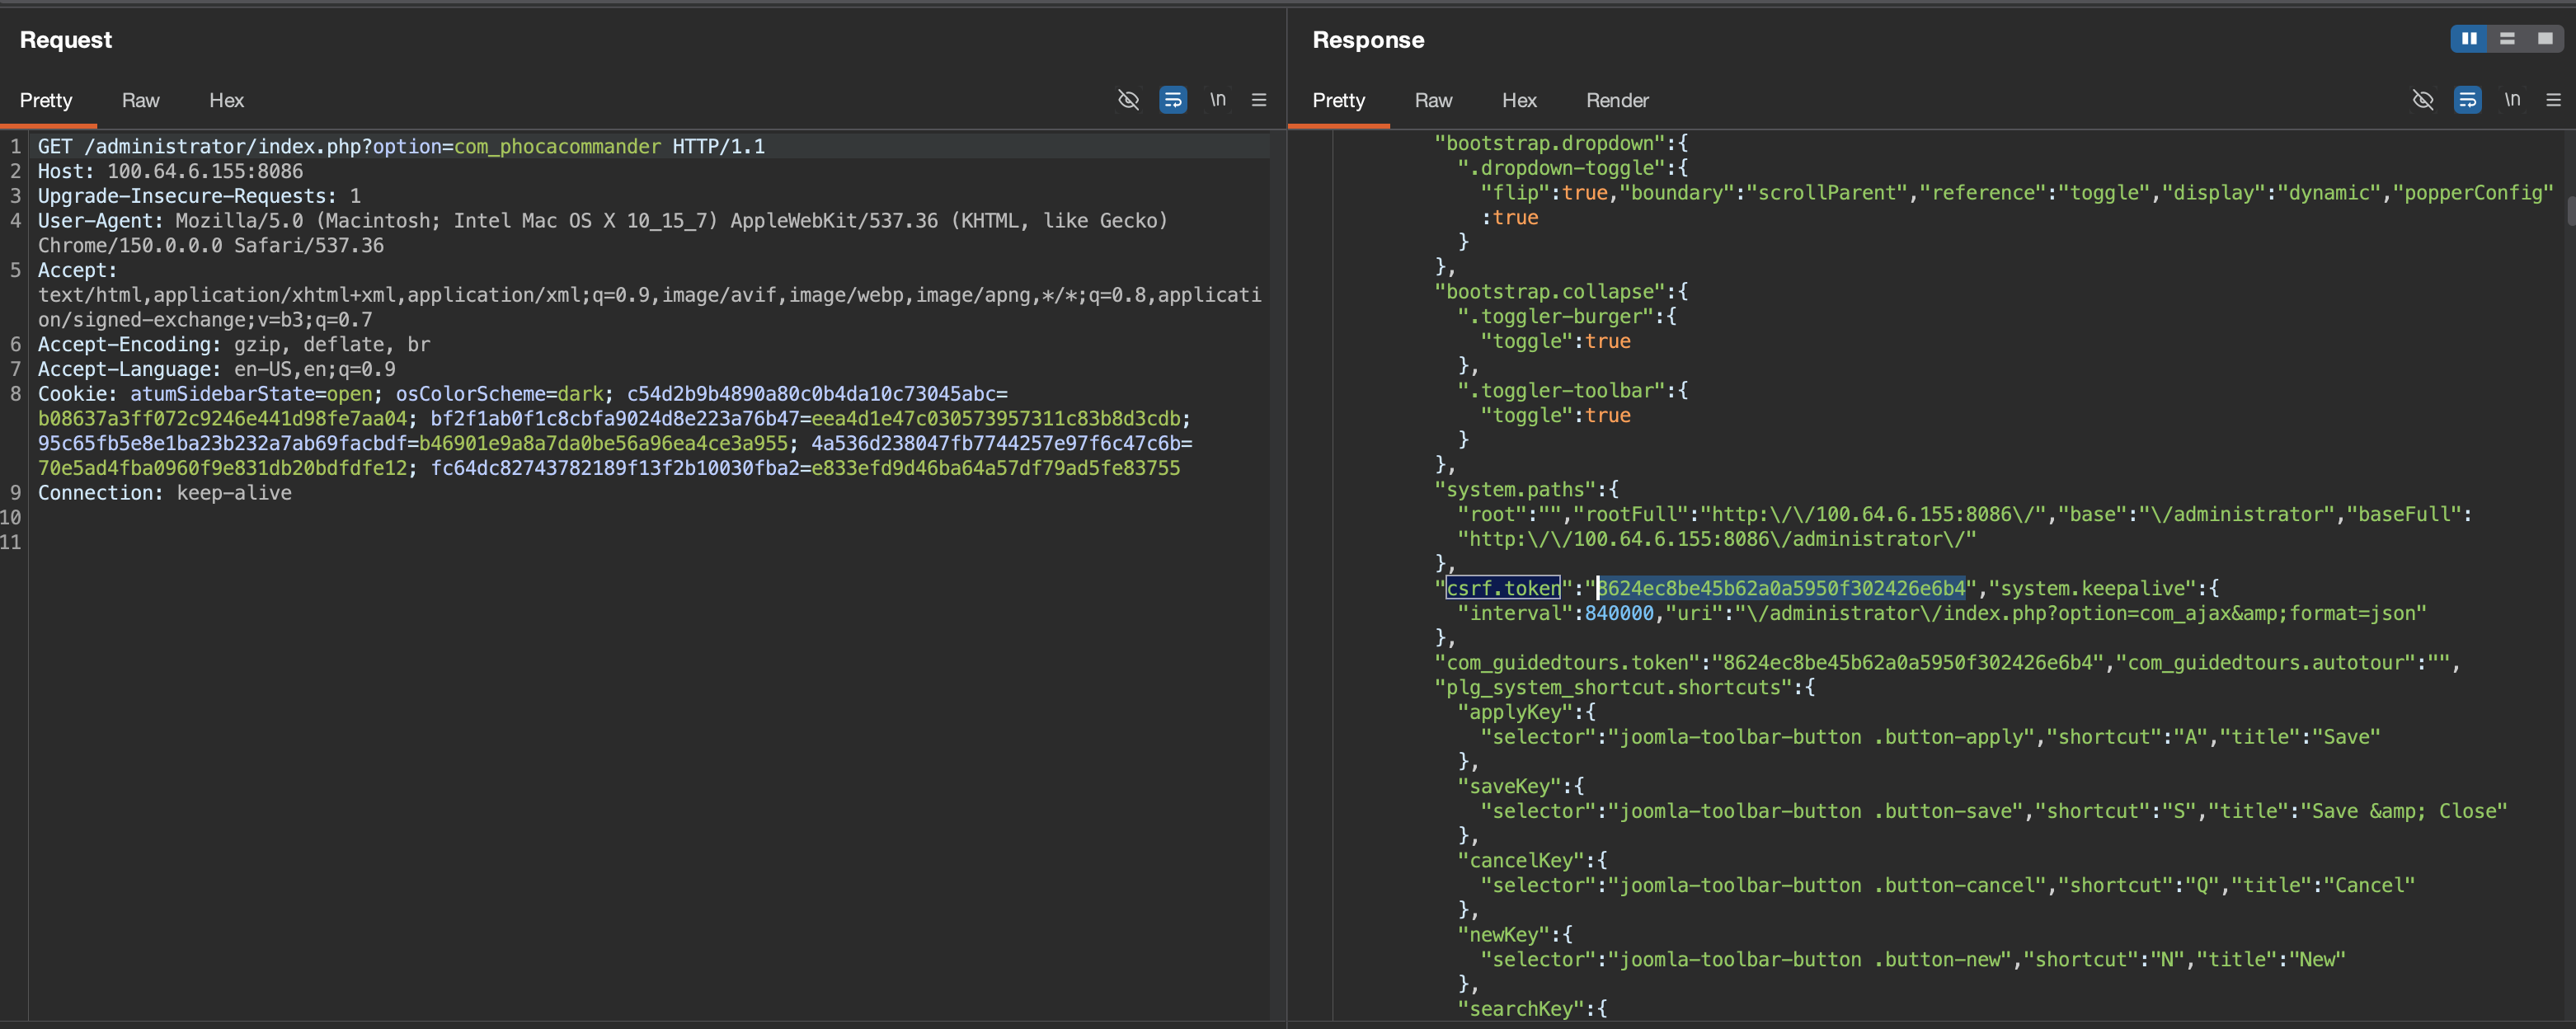
The Joomla extension PhocaCommander is vulnerable to Path Traversal in delete, copy, move actions - CVSS 6.4

方便实用的CVE-2026-39363利用工具

Proof-of-Concept exploit for CVE-2026-15409 (SonicWall SMA 1000 RCE) via Erlang distribution over WebSocket. Achieves unauthenticated remote code…

CVE-2026-60004 — Gitea/Forgejo Diffpatch Git Hook RCE. Bare clone → post-index-change hook injection. CVSS 9.8 | CWE-94 | Gitea < 1.27.1

Demonstrates a critical GraphQL batching alias-confusion SQL injection (CVE-2026-5432) with a vulnerable Node.js server and Python exploit for…