
php_filter_chain_oracle_poc
 4xura/php_filter_chain_oracle_poc
PoC scripts to exploit LFR (Local File Read) via PHP filters chain oracle (php://filter), especially for CTF purposes or the exploit of…
ctfexploitationinformation-gathering+3
2
4xura/php_filter_chain_oracle_pocPoC scripts to exploit LFR (Local File Read) via PHP filters chain oracle (php://filter), especially for CTF purposes or the exploit of…
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 diego-treitos/linux-smart-enumeration
Linux enumeration tool for pentesting and CTFs with verbosity levels
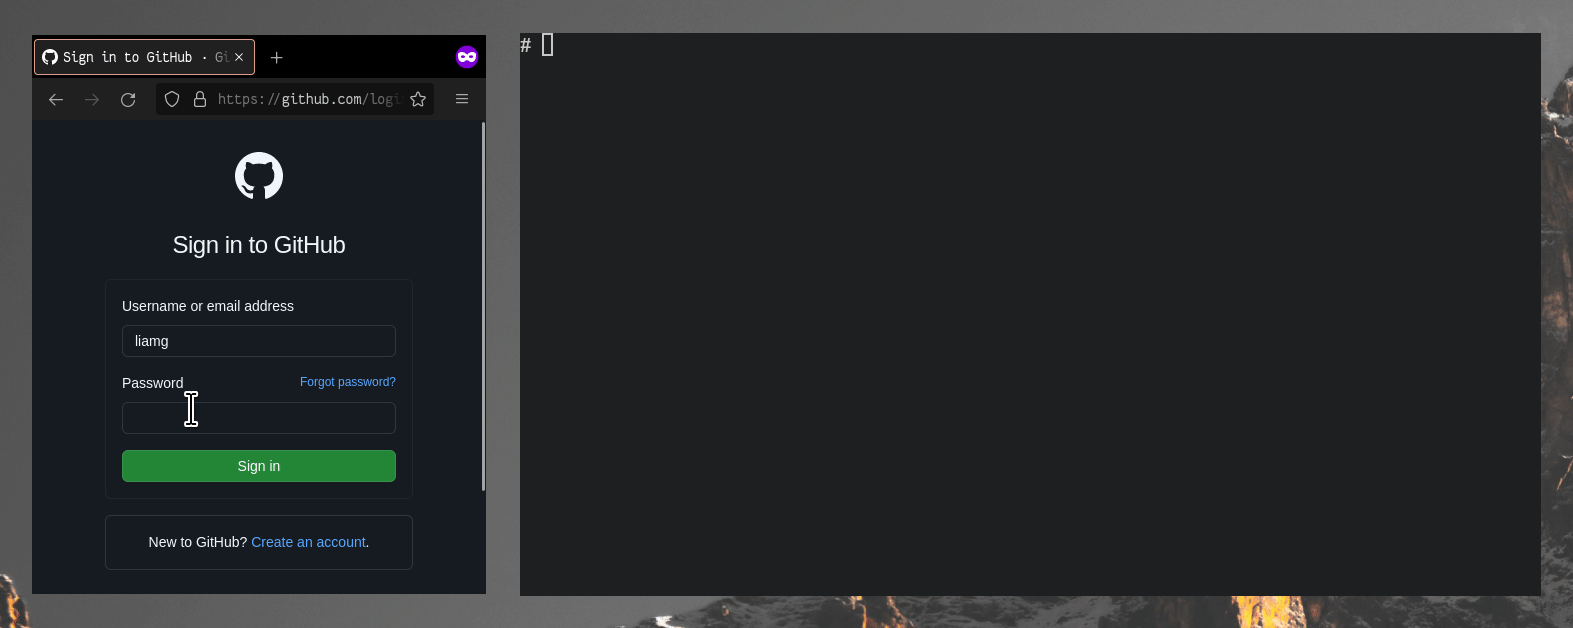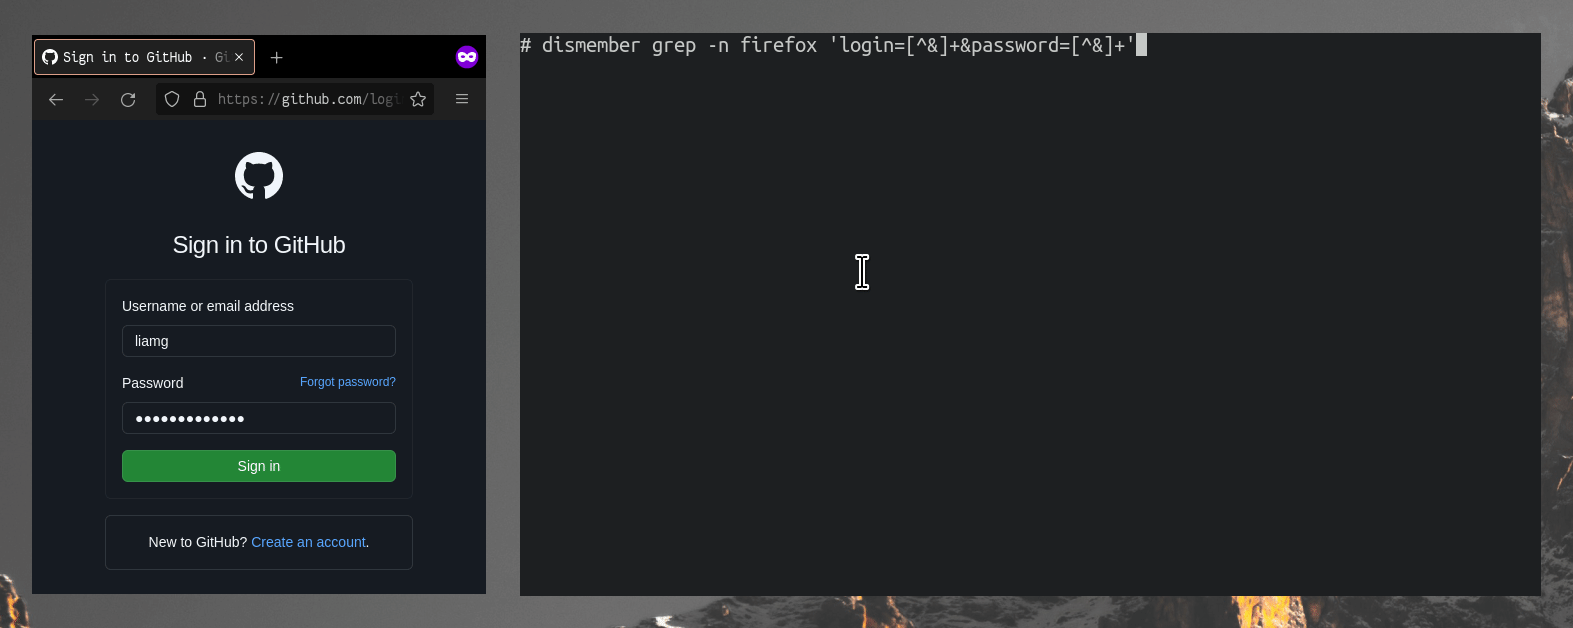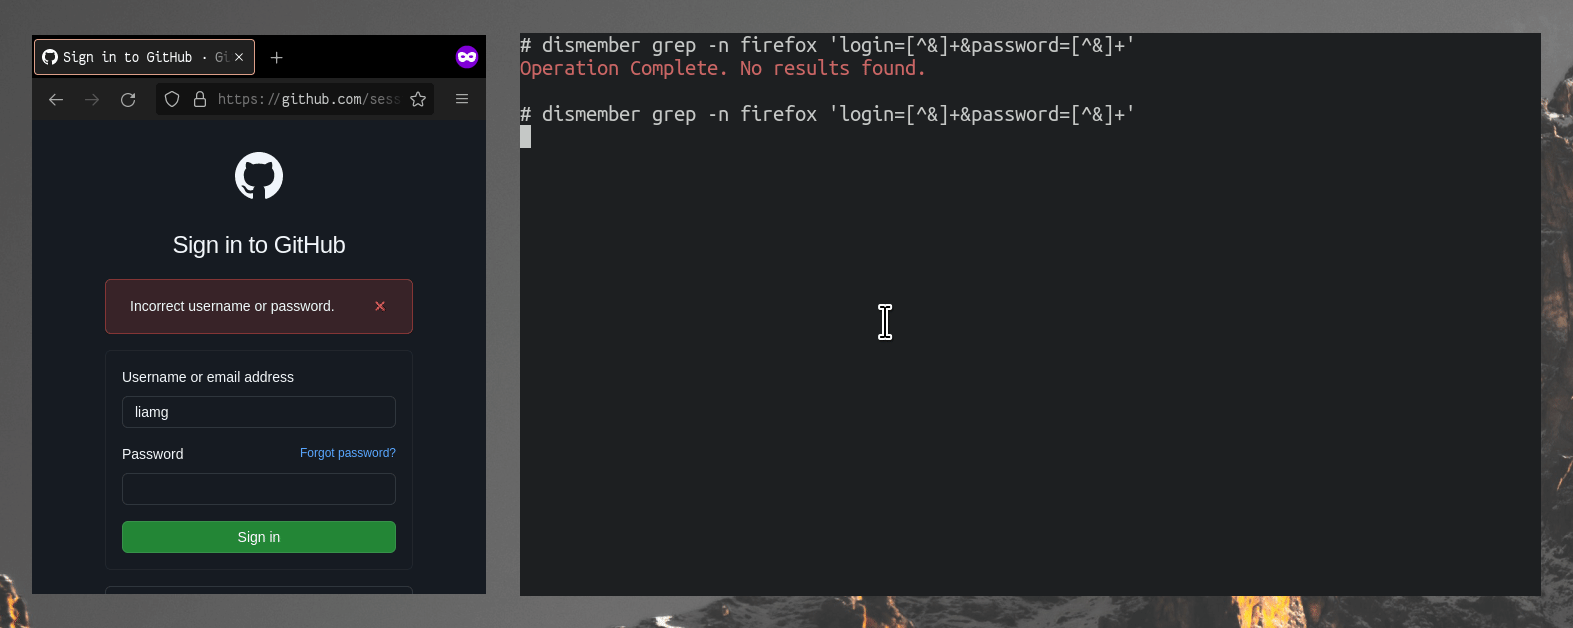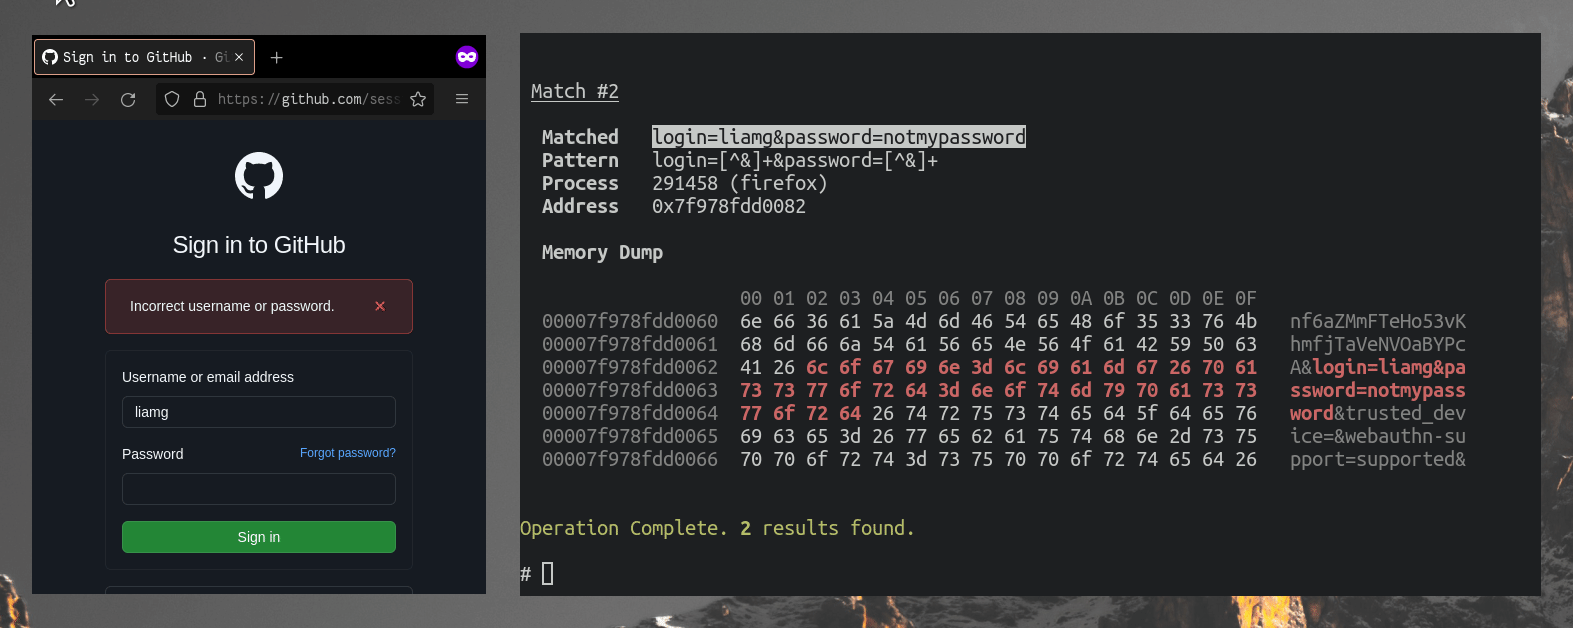 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
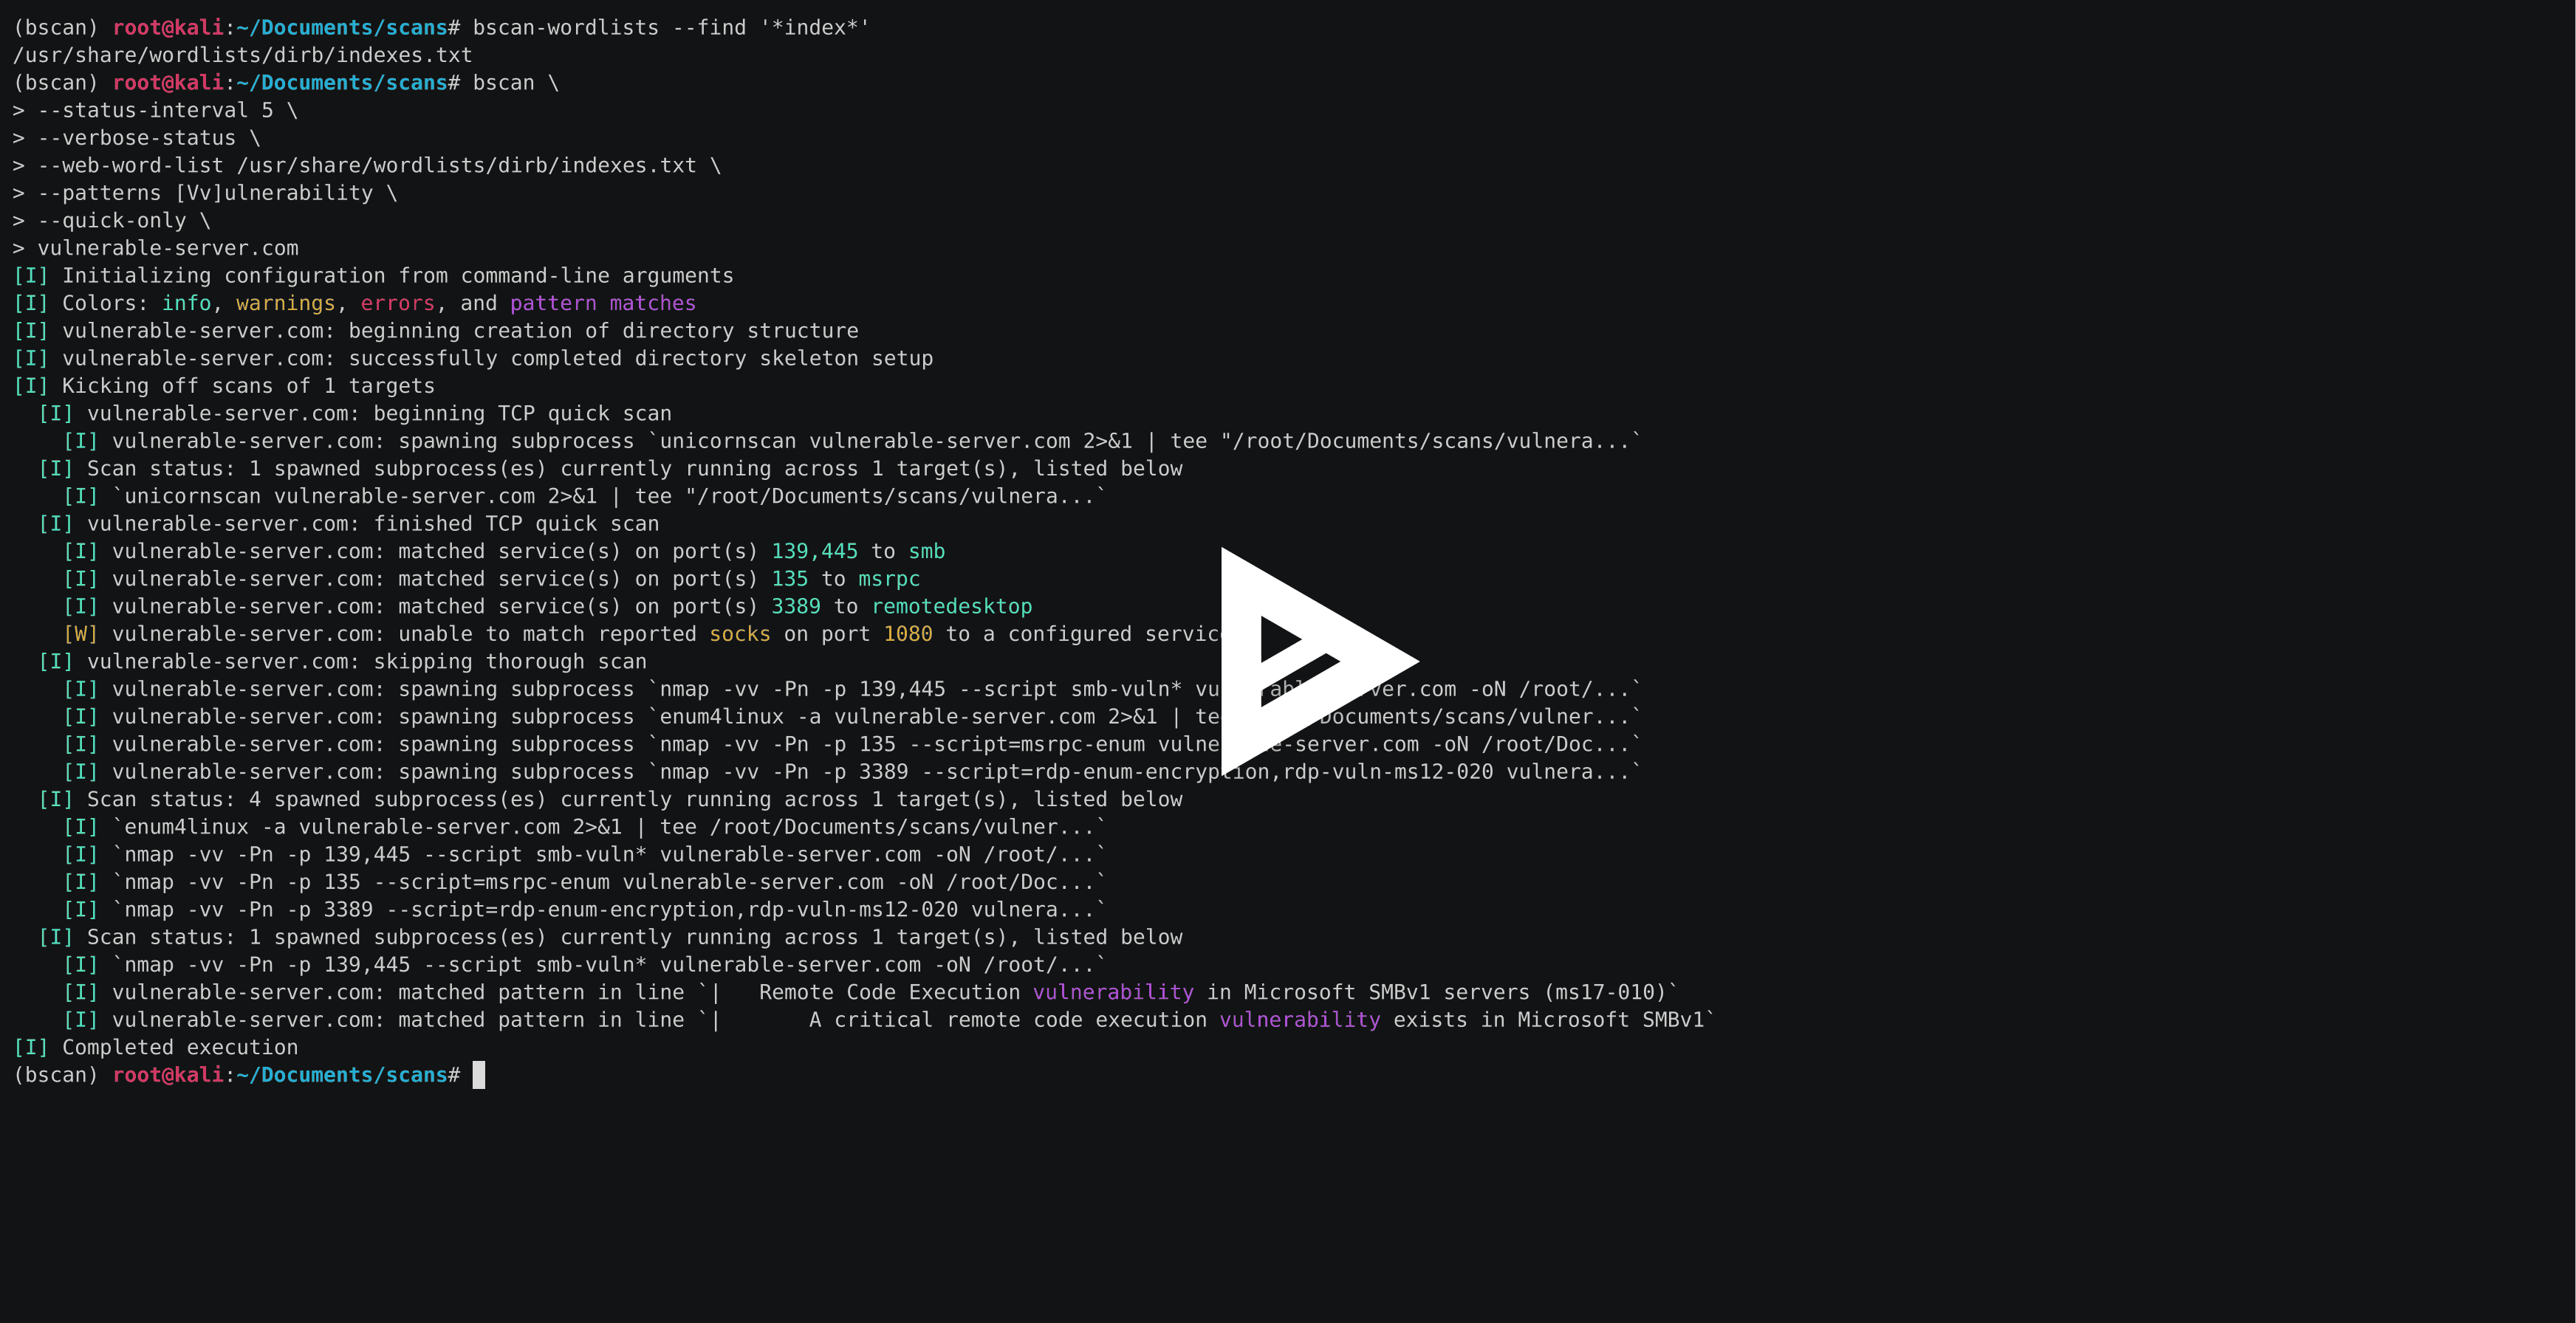
 gr1mmie/autoenum
Automatic Service Enumeration Script
 p1ckzi/cve-2012-5519
cups-root-file-read.sh | CVE-2012-5519
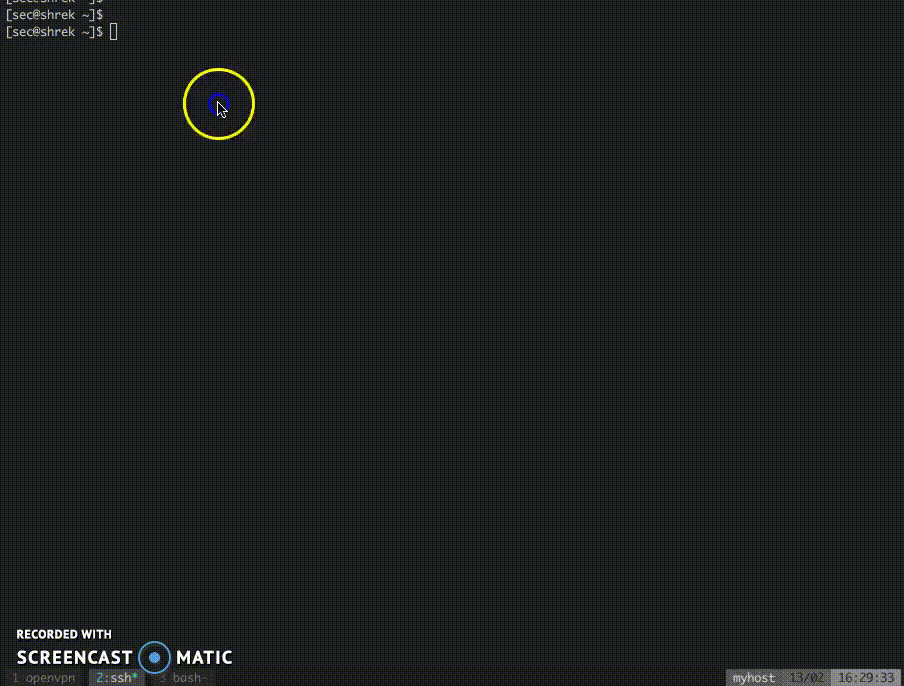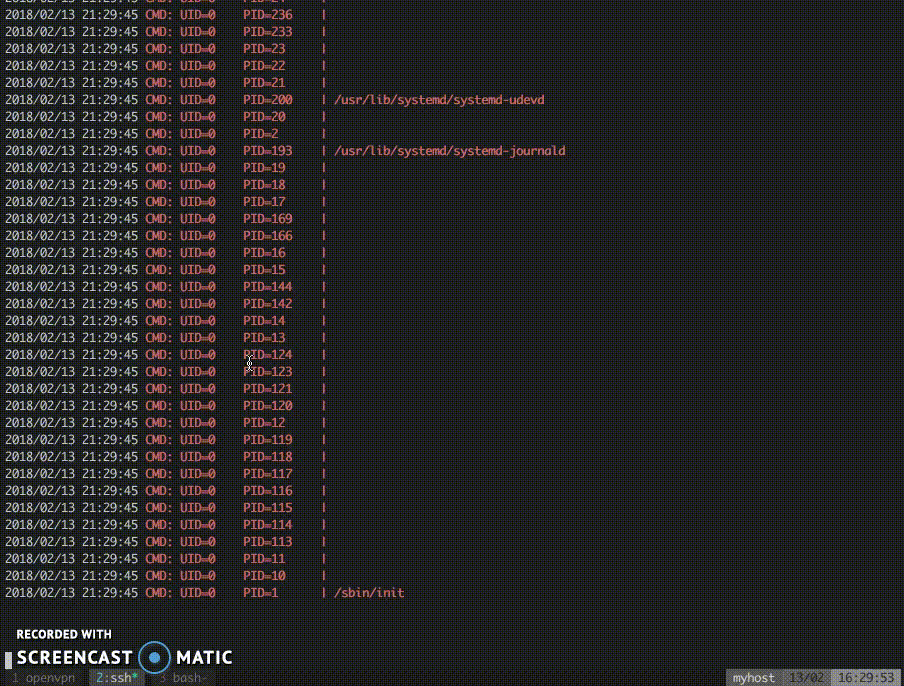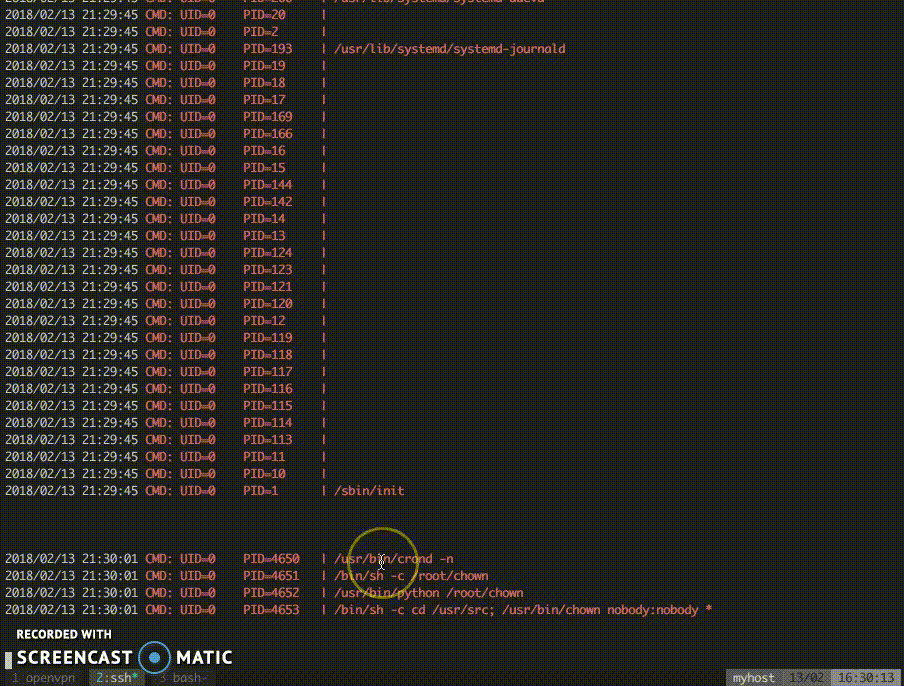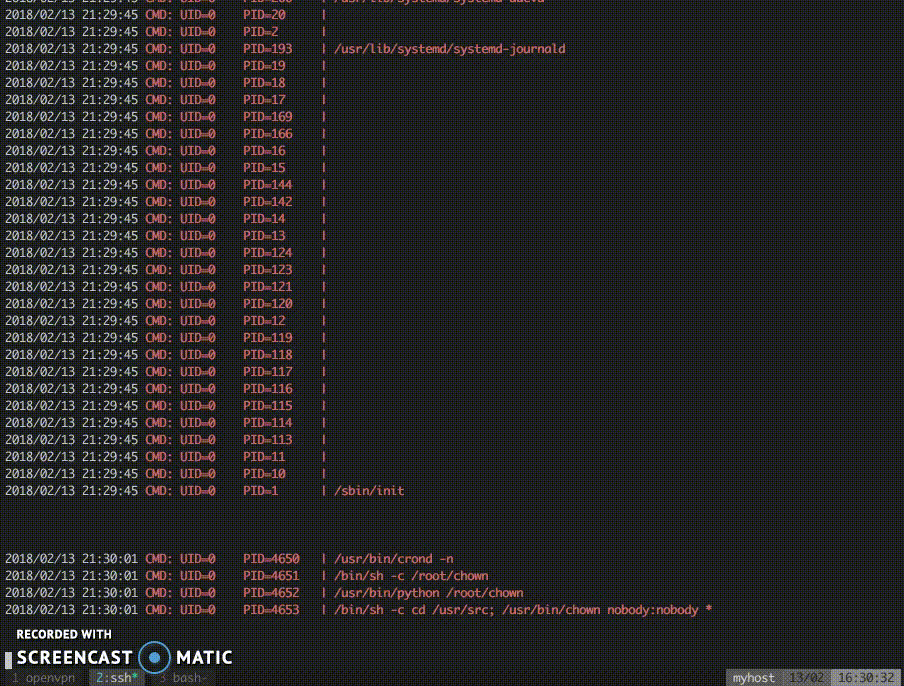 dominicbreuker/pspy
Monitor linux processes without root permissions
 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
 devploit/debughunter
Chrome extension that passively finds debug parameters, sensitive headers and exposed paths (.env, .git, actuator) while you browse. Built for bug…
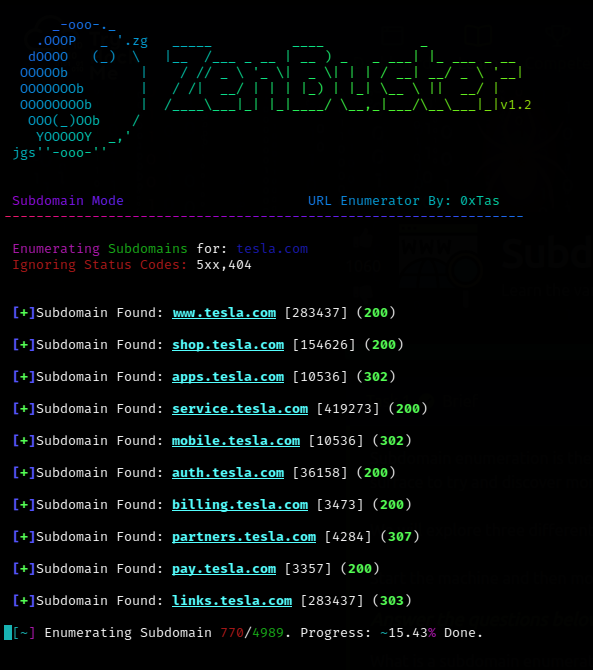 0xtas/zenbuster
Multi-threaded URL enumeration/content-discovery tool in Python.
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
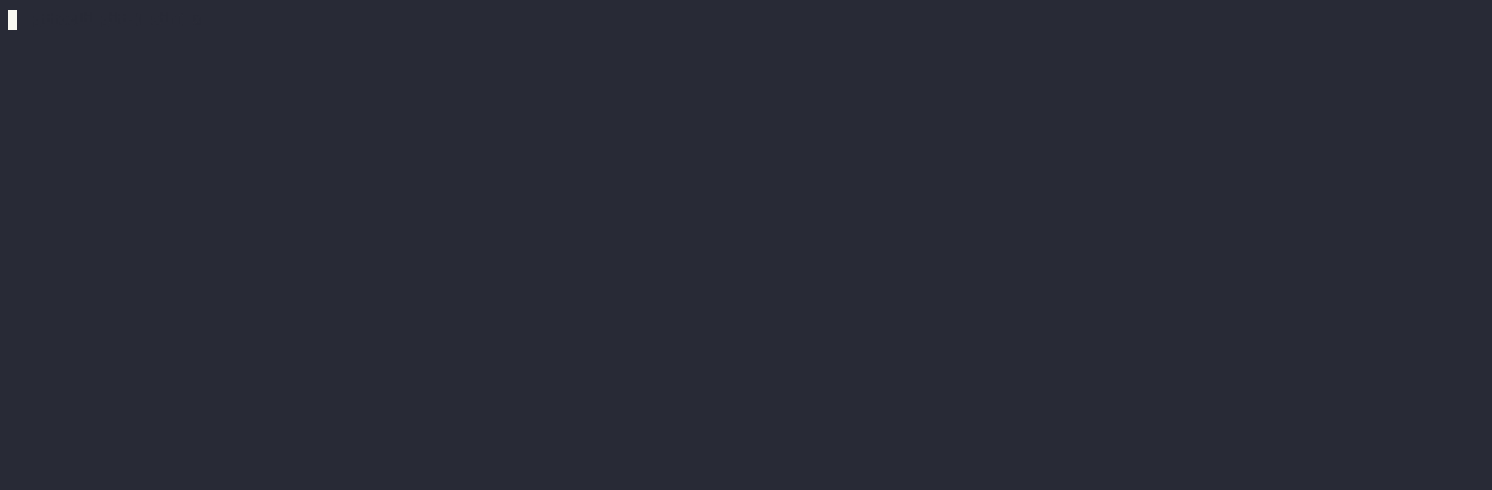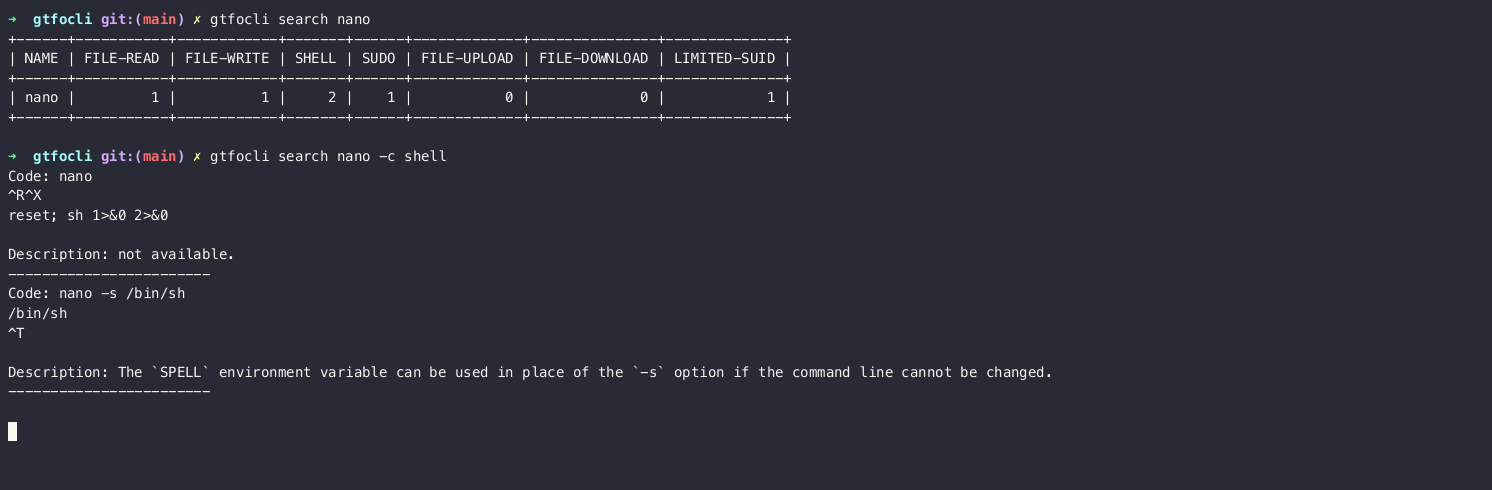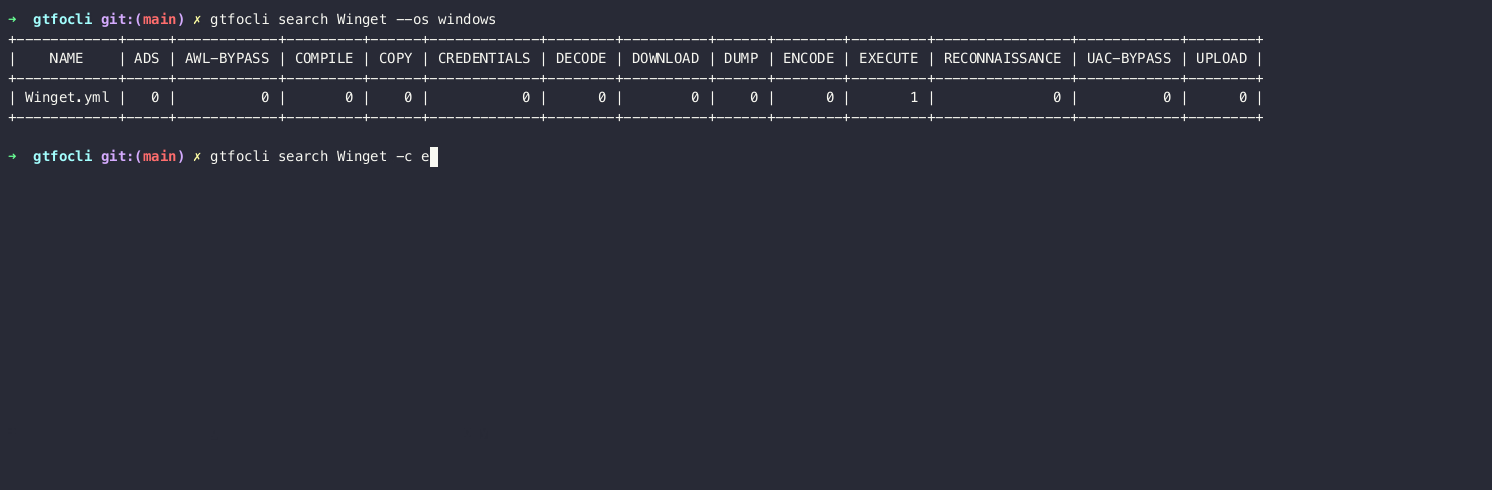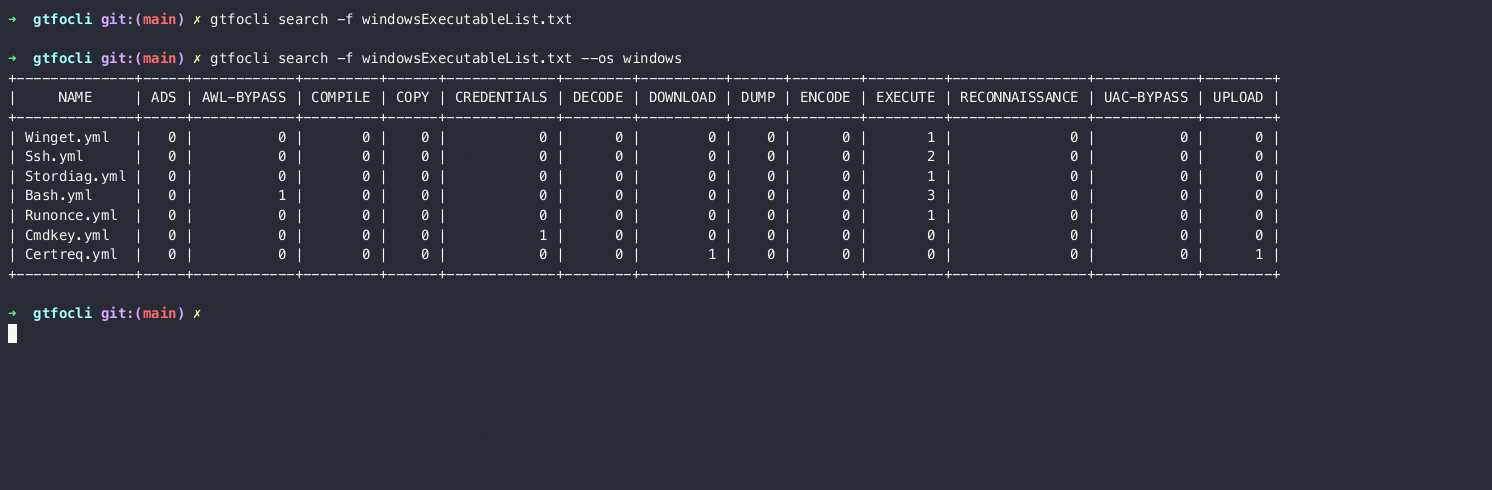 cmd-tools/gtfocli
GTFO Command Line Interface for easy binaries search commands that can be used to bypass local security restrictions in misconfigured systems.
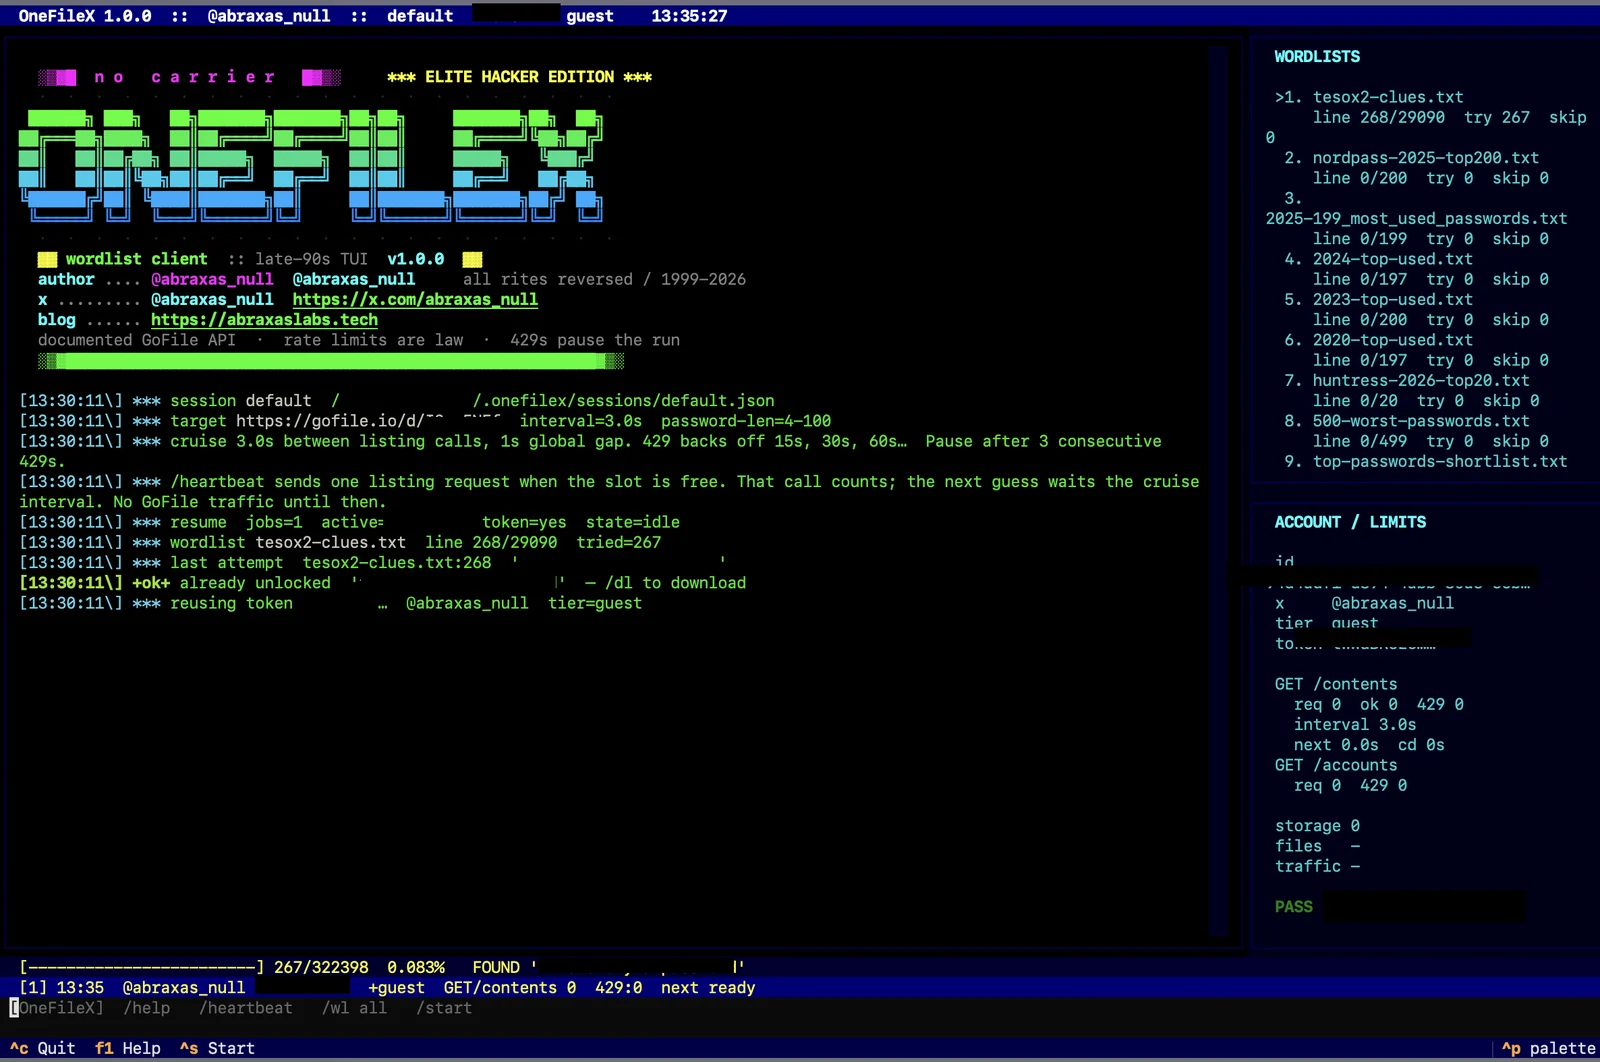 abraxas/gofilex
Wordlist Bruteforcer for GoFile (gofile.io) Download Passwords
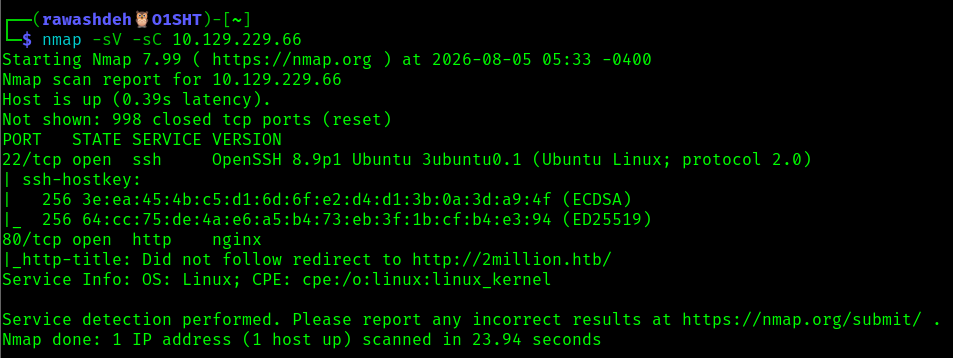 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 bitburner/ivre-wizard
An interactive wizard front end for IVRE to make creating scans to the database easier.