

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/cmd-tools/gtfocli
Privilege EscalationInformation GatheringCTFPenetration Testing
GitHubcmd-tools/gtfocli

gtfocli

GTFO Command Line Interface for easy binaries search commands that can be used to bypass local security restrictions in misconfigured systems.

View Repository
181371 month agoNot yet reviewed
Share

GTFOcli

GTFOcli it's a Command Line Interface for easy binaries search commands that can be used to bypass local security restrictions in misconfigured systems.
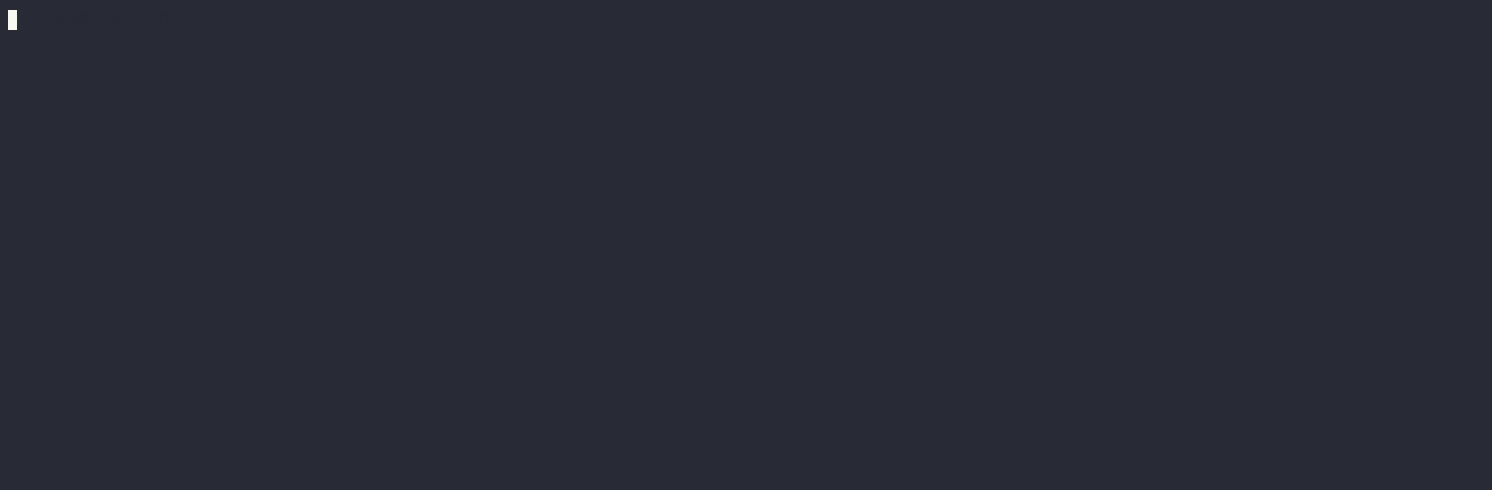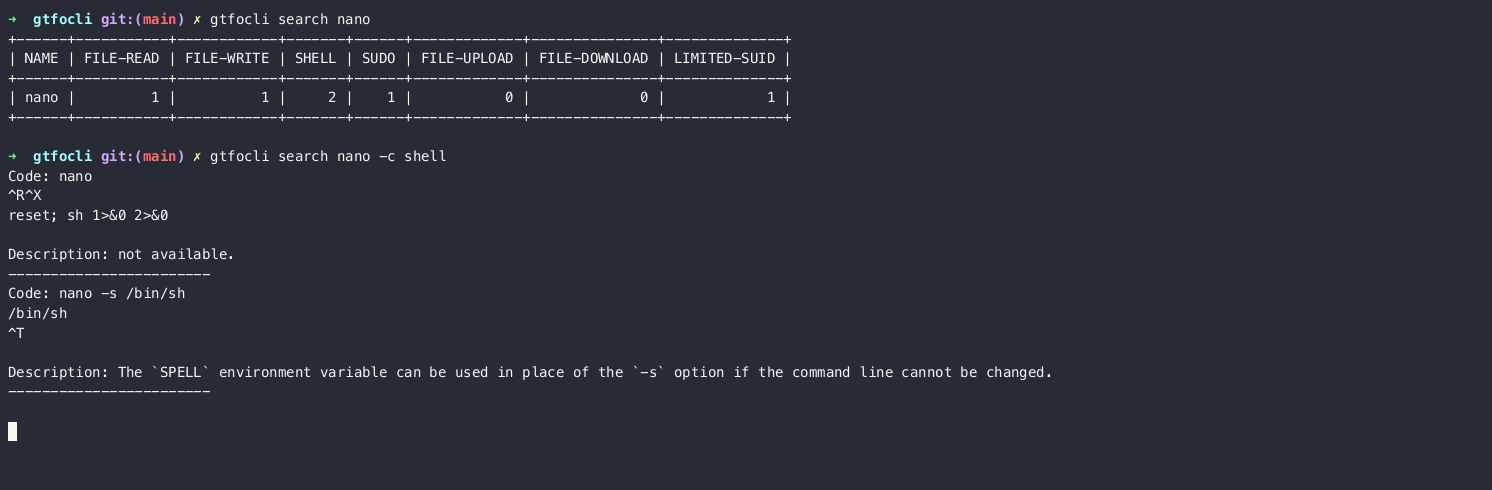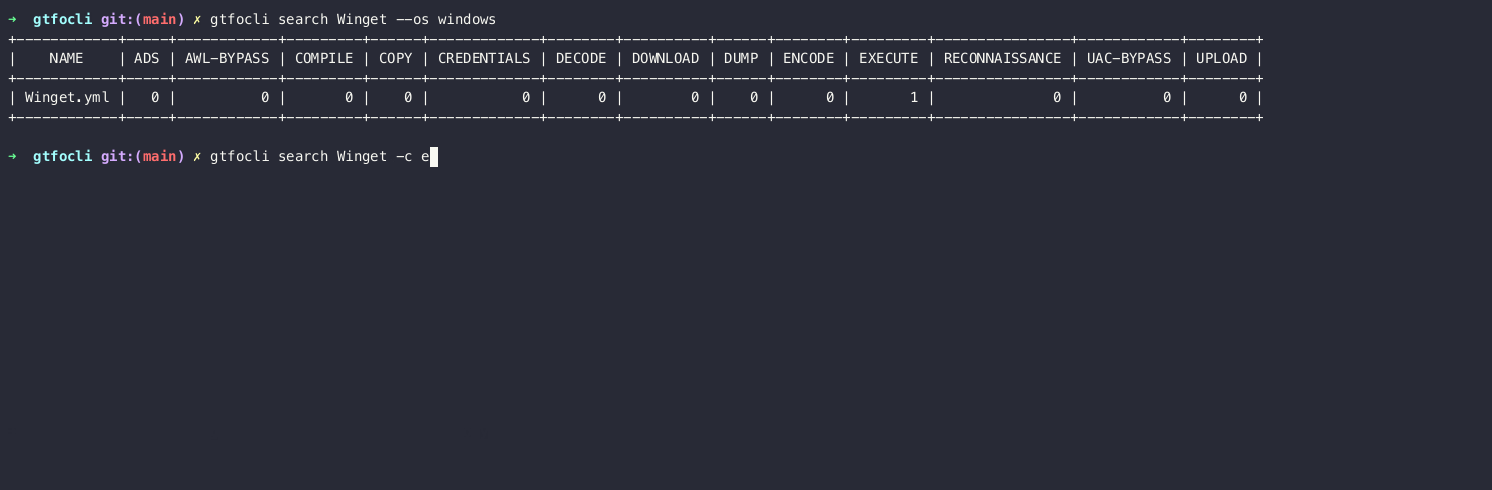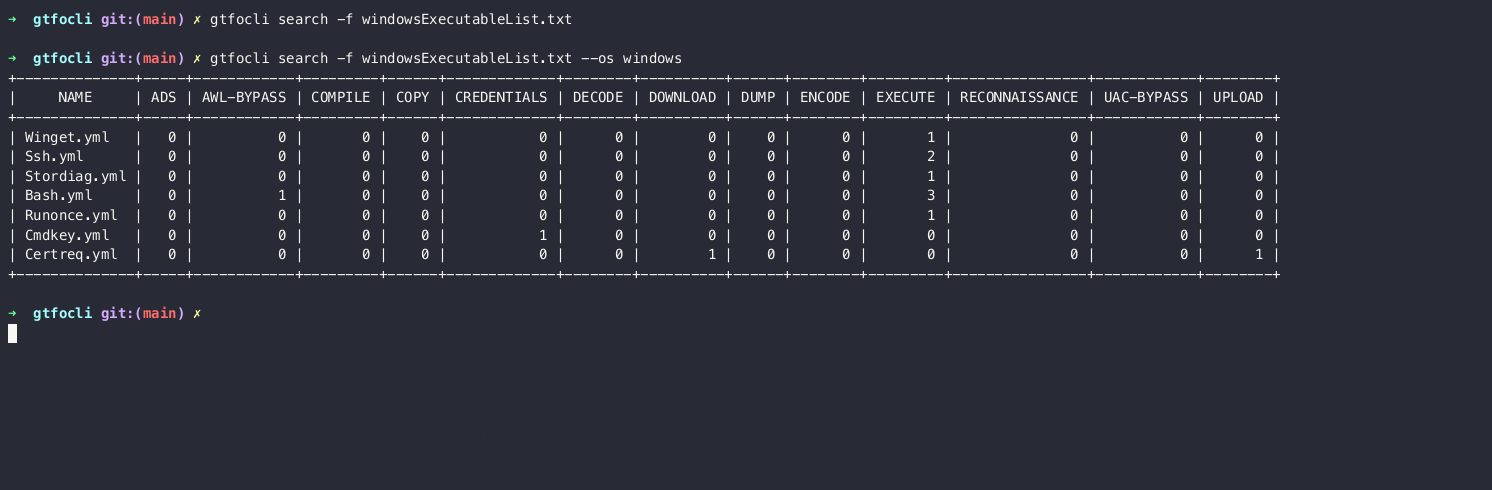
Table of Contents

  • Table of Contents
  • Installation
  • Usage
    • Search for Unix binaries
    • Search for Windows binaries
    • Search using dockerized solution
    • CTF
  • Credits
  • Contributing

Installation

Using go:

go install github.com/cmd-tools/gtfocli@latest

Using homebrew:

brew tap cmd-tools/homebrew-tap
brew install gtfocli

Using docker:

docker pull cmdtoolsowner/gtfocli

Usage

Search for unix binaries

Search for binary tar:

gtfocli search tar

Search for binary tar from stdin:

echo "tar" | gtfocli search

Search for binaries located into file;

cat myBinaryList.txt
/bin/bash
/bin/sh
tar
arp
/bin/tail

gtfocli search -f myBinaryList.txt

Search for windows binaries

Search for binary Winget.exe:

gtfocli search Winget --os windows

Search for binary Winget from stdin:

echo "Winget" | gtfocli search --os windows

Search for binaries located into file:

cat windowsExecutableList.txt
Winget
c:\\Users\\Desktop\\Ssh
Stordiag
Bash
c:\\Users\\Runonce.exe
Cmdkey
c:\dir\subDir\Users\Certreq.exe

gtfocli search -f windowsExecutableList.txt --os windows

Search for binary Winget and print output in yaml format (see -h for available formats):

gtfocli search Winget -o yaml --os windows

Search using dockerized solution

Examples:

Search for binary Winget and print output in yaml format:

docker run -i cmdtoolsowner/gtfocli search Winget -o yaml --os windows

Search for binary tar and print output in json format:

echo 'tar' | docker run -i cmdtoolsowner/gtfocli search -o json

Search for binaries located into file mounted as volume in the container:

cat myBinaryList.txt
/bin/bash
/bin/sh
tar
arp
/bin/tail

docker run -i -v $(pwd):/tmp cmdtoolsowner/gtfocli search -f /tmp/myBinaryList.txt

CTF

An example of common use case for gtfocli is together with find:

find / -type f \( -perm 04000 -o -perm -u=s \) -exec gtfocli search {} \; 2>/dev/null

or

find / -type f \( -perm 04000 -o -perm -u=s \) 2>/dev/null | gtfocli search

Credits

Thanks to GTFOBins and LOLBAS, without these projects gtfocli would never have come to light.

Contributing

You want to contribute to this project? Wow, thanks! So please just fork it and send a pull request.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    806
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    523
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    441
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    270
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →




