

CVE-2026-85243
 oscerd/cve-2026-85243
Runnable Spring Boot and Quarkus proof-of-concept for CVE-2026-85243, demonstrating the Apache Camel camel-crypto-pgp integrity-verification…
cryptographydefensive-toolseducation+4
oscerd/cve-2026-85243Runnable Spring Boot and Quarkus proof-of-concept for CVE-2026-85243, demonstrating the Apache Camel camel-crypto-pgp integrity-verification…
 testssl/testssl.sh
Testing TLS/SSL encryption anywhere on any port
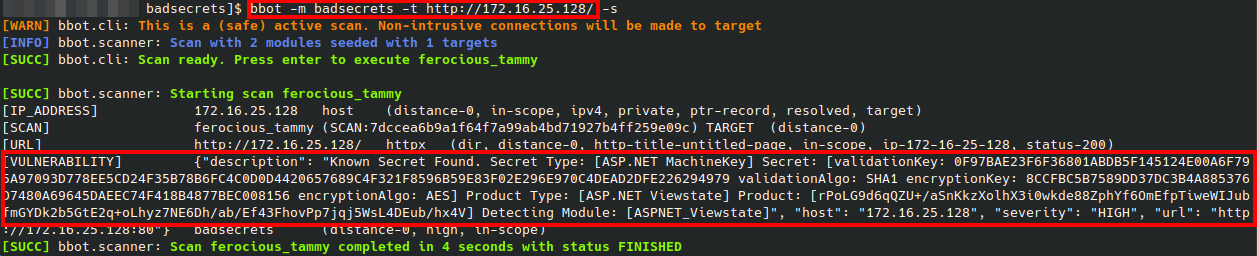 blacklanternsecurity/badsecrets
A library for detecting known secrets across many web frameworks
 coroner/cryptolyzer
Multi-protocol cryptographic analyzer auditing TLS, SSL, SSH, IKE, DNSSEC, and HTTP security headers. Detects 400+ cipher suites, generates JA3/HASSH…
 owasp/o-saft
O-Saft - OWASP SSL advanced forensic tool
 strozfriedberg/ssh-weak-dh
Audits SSH servers for weak Diffie-Hellman key exchange groups by testing multiple client configurations, identifying Logjam-vulnerable endpoints…
 badchemical/iot-vulnerability-research-public
Independent IoT security research, vulnerability disclosures, and PoCs focusing on firmware analysis, hardware interfaces, and cryptographic flaws.
 tls-attacker/tls-scanner
Automated TLS server and client configuration scanner for pentesters and researchers. Evaluates cipher suites, protocol versions, and security…
 rbsec/sslscan
Fast SSL/TLS scanner that discovers supported cipher suites, protocols, and vulnerabilities (Heartbleed, POODLE, CRIME) with certificate chain…
 aramosf/cve-2026-61500
Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.
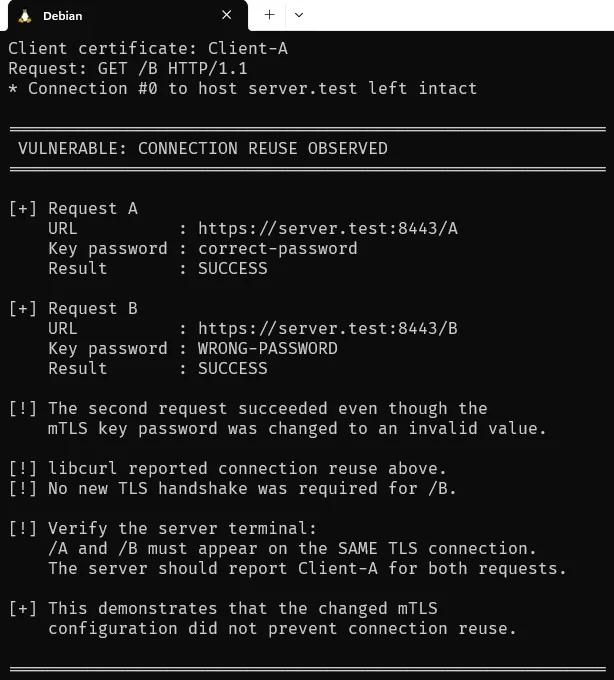 nimaarek/cve-2026-8932-poc
Proof-of-concept reproducing CVE-2026-8932, an incomplete mTLS configuration matching flaw in libcurl connection reuse, with a local lab server and C…
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 l1lf1ng3r/heartbleed-vulnerability-exploitation
hands on investigation of the heartbleed vulnerability (CVE-2014-0160).
 goldendivider/gpgsm-cve-2026-57062-cms-gcm-short-tag
Proof-of-concept demonstrating a CMS AES-GCM short-tag authentication bypass in GnuPG's gpgsm (CVE-2026-57062). Forges a message that decrypts on…
 tony102741/cve-2026-15469
Advisory and technical analysis of CVE-2026-15469, a hard-coded RSA-512 mesh group private key in TP-Link Deco routers, including root cause, impact,…
 mattgsys/cve-2026-19586
Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
 hunt-benito/the-same-key-opens-every-box-cve-2026-71960-hard-coded-jwt-secret-in-cudy-wr3000-mesh-mqtt
PoC toolkit that unpacks router firmware, decrypts device secrets, forges JWT tokens, and exploits CVE-2026-71960/71961 to take over Cudy WR3000 mesh…
 blacklanternsecurity/dp_cryptomg
Another tool for exploiting CVE-2017-9248, a cryptographic weakness in Telerik UI for ASP.NET AJAX dialog handler.