Web-Cache-Vulnerability-Scanner

Go-based CLI scanner for web cache poisoning and deception. Supports 10 poisoning techniques, multiple deception methods, built-in crawler, JSON…

Go-based CLI scanner for web cache poisoning and deception. Supports 10 poisoning techniques, multiple deception methods, built-in crawler, JSON…

The Prime Cross Site Request Forgery (CSRF) Audit and Exploitation Toolkit.

htcap is a web application scanner able to crawl single page application (SPA) recursively by intercepting ajax calls and DOM changes.

Web Application Vulnerability Scanner.

This is a CVE-2025-29927 Scanner.

Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…

Proof-of-concept exploit demonstrating SSRF vulnerabilities in Firecrawl web scraper (CVE-2024-56800, CVE-2025-57818) with self-hosted setup and…

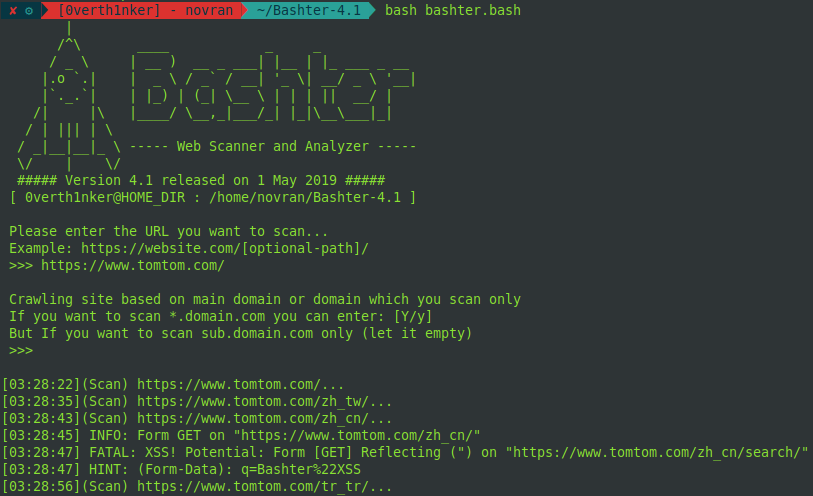
Web Vulnerability Scanner using Shell Script

Gryffin is a large scale web security scanning platform.

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…

GUI based offensive penetration testing tool (Open Source)

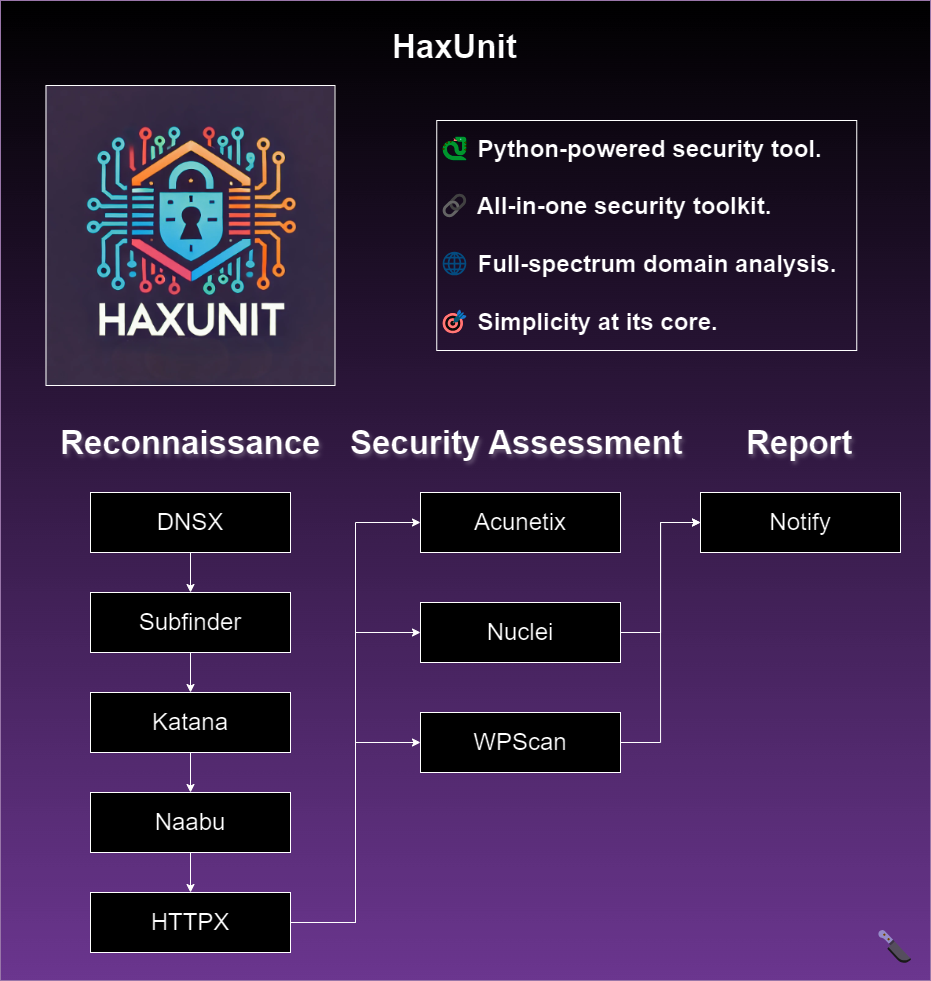
Automated web domain reconnaissance and security assessment tool integrating subdomain enumeration, port scanning, vulnerability scanning, and…

A modular distributed penetration testing tool.

Curated collection of validated Joomla exploit artifacts with Docker lab environments. Includes RCE, SQLi, XSS, and privilege escalation scripts…

Vajra is a highly customizable target and scope based automated web hacking framework to automate boring recon tasks and same scans for multiple…

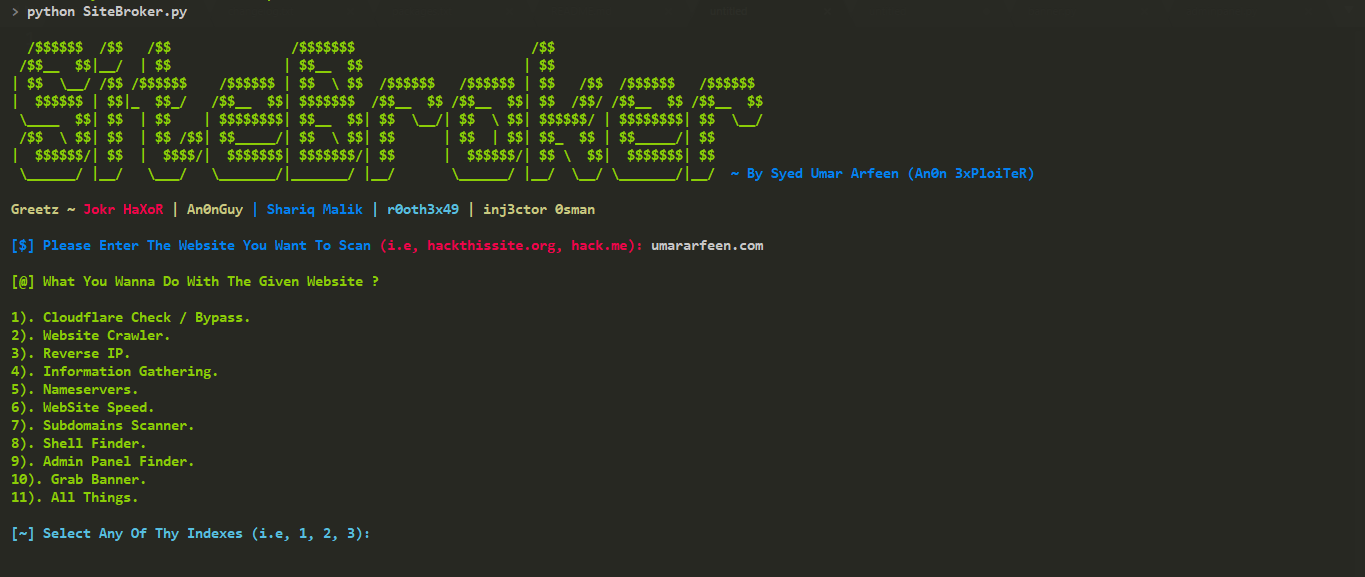
A cross-platform python based utility for information gathering and penetration testing automation!

Automatic SQL injection and database takeover tool