
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
webvulscan — Web Application Vulnerability Scanner. | Kitploit

Tools/GitHubGitHub/dermotblair/webvulscan
Vulnerability ScannersWeb Vulnerability ScannersWeb SecurityPenetration TestingCrawler
GitHubdermotblair/webvulscan

webvulscan

Web Application Vulnerability Scanner.

View Repository
151687611 years agoReviewed by Kitploit
Website
Share

WebVulScan

Synopsis

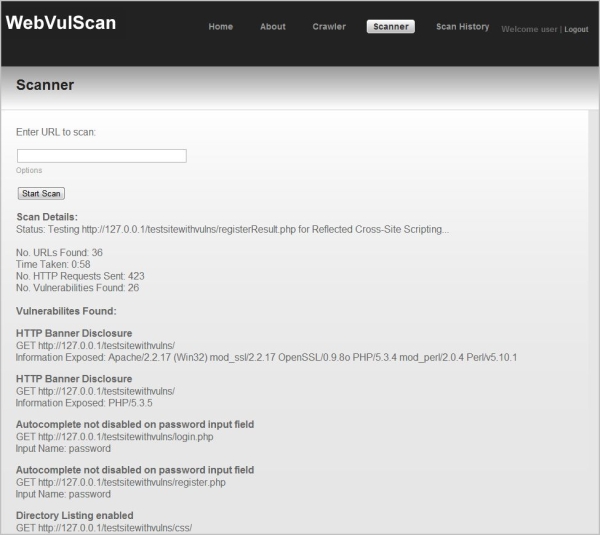
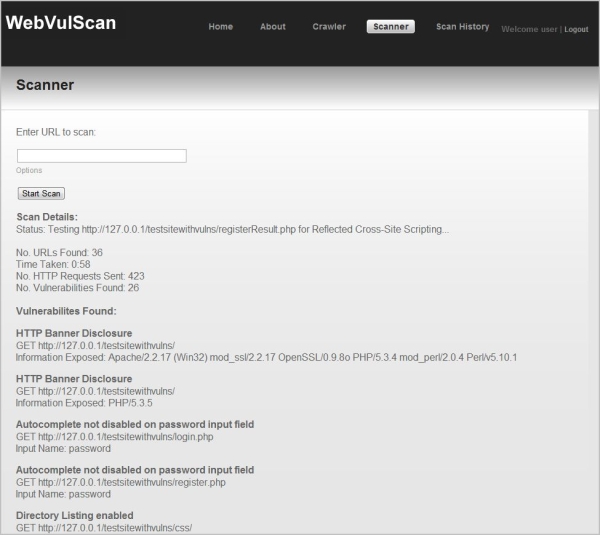
WebVulScan is a web application vulnerability scanner. It is a web application itself written in PHP and can be used to test remote, or local, web applications for security vulnerabilities. As a scan is running, details of the scan are dynamically updated to the user. These details include the status of the scan, the number of URLs found on the web application, the number of vulnerabilities found and details of the vulnerabilities found.

After a scan is complete, a detailed PDF report is emailed to the user. The report includes descriptions of the vulnerabilities found, recommendations and details of where and how each vulnerability was exploited.
alt tag

The vulnerabilities tested by WebVulScan are:

  • Reflected Cross-Site Scripting
  • Stored Cross-Site Scripting
  • Standard SQL Injection
  • Broken Authentication using SQL Injection
  • Autocomplete Enabled on Password Fields
  • Potentially Insecure Direct Object References
  • Directory Listing Enabled
  • HTTP Banner Disclosure
  • SSL Certificate not Trusted
  • Unvalidated Redirects

Features:

  • Crawler: Crawls a website to identify and display all URLs belonging to the website.
  • Scanner: Crawls a website and scans all URLs found for vulnerabilities.
  • Scan History: Allows a user to view or download PDF reports of previous scans that they performed.
  • Register: Allows a user to register with the web application.
  • Login: Allows a user to login to the web application.
  • Options: Allows a user to select which vulnerabilities they wish to test for (all are enabled by default).
  • PDF Generation: Dynamically generates a detailed PDF report.
  • Report Delivery: The PDF report is emailed to the user as an attachment.

Installation

See ReadMe file in txt and docx format for installation instructions.

Discussion

As this project was exported from Google Code, previously found problems and solutions are available at:

  • https://groups.google.com/forum/#!forum/webvulscan
  • https://code.google.com/p/webvulscan/issues/list

For any other issues or feedback, please contact [email protected]

License

GNU GPL v3

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    851
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    538
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    297
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →






