LFITester
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
crawlerexploitationfuzzing+7
112
kostas-pa/lfitesterPython3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 ambitsecurity/jshound
Find every API request a web app makes, from the JavaScript it ships: method, URL, body, headers and GraphQL operations. One command.
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
 si9int/cc.py
Extracting URLs of a specific target based on the results of "commoncrawl.org"
 rverton/webanalyze
Port of Wappalyzer (uncovers technologies used on websites) to automate mass scanning.
 qeeqbox/social-analyzer
API, CLI, and Web App for analyzing and finding a person's profile in 1000 social media \ websites
 urbanadventurer/whatweb
Next generation web scanner
 thewhiteh4t/finalrecon
Automated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…
 soxoj/maigret
🕵️♂️ Collect a dossier on a person by username from 6K websites
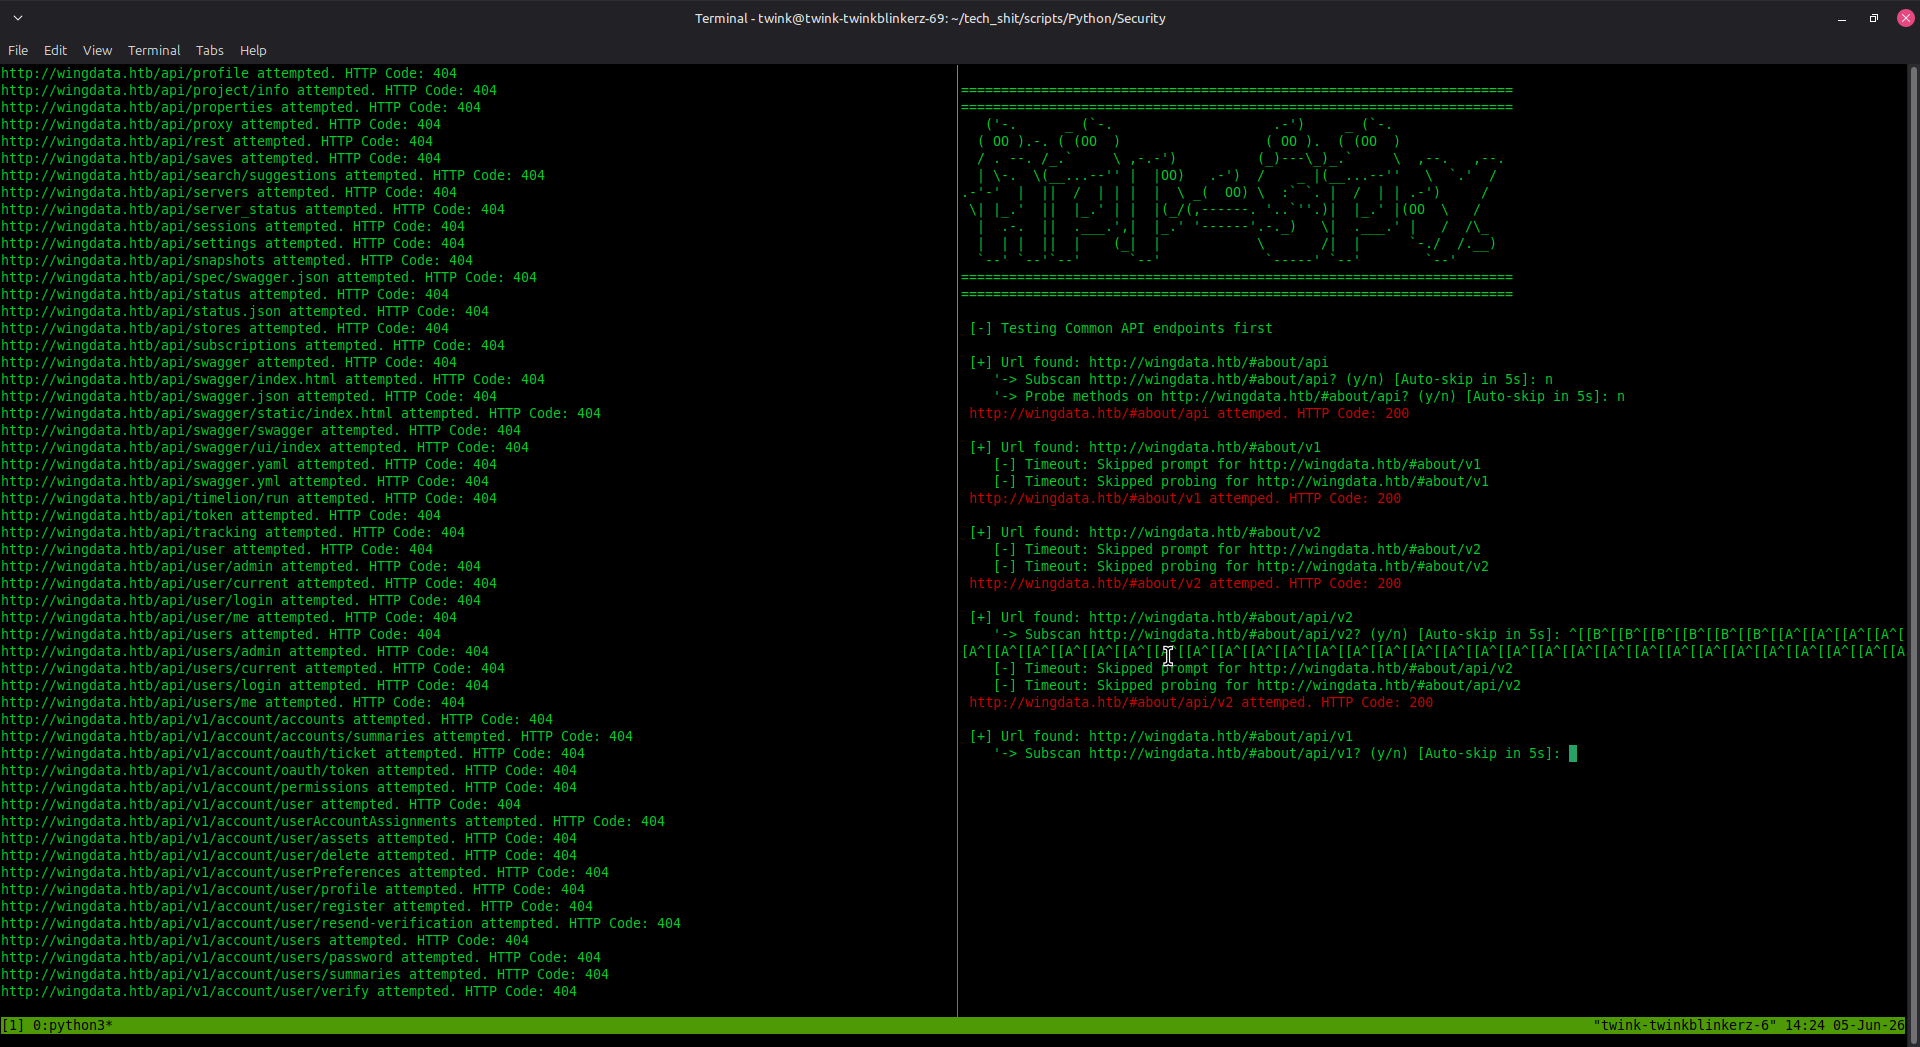 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
 bhavsec/autopentest-ai
Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.
 spider12223/penscope
Passive recon & attack surface mapper — zero requests sent
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 talyx66/webfang
WEBFANG, is my first CLI, a modular OSINT & Reconnaissance toolkit curated for Ethical Hackers and Red-Teamers. Sink fangs into web targets using a…

 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…